

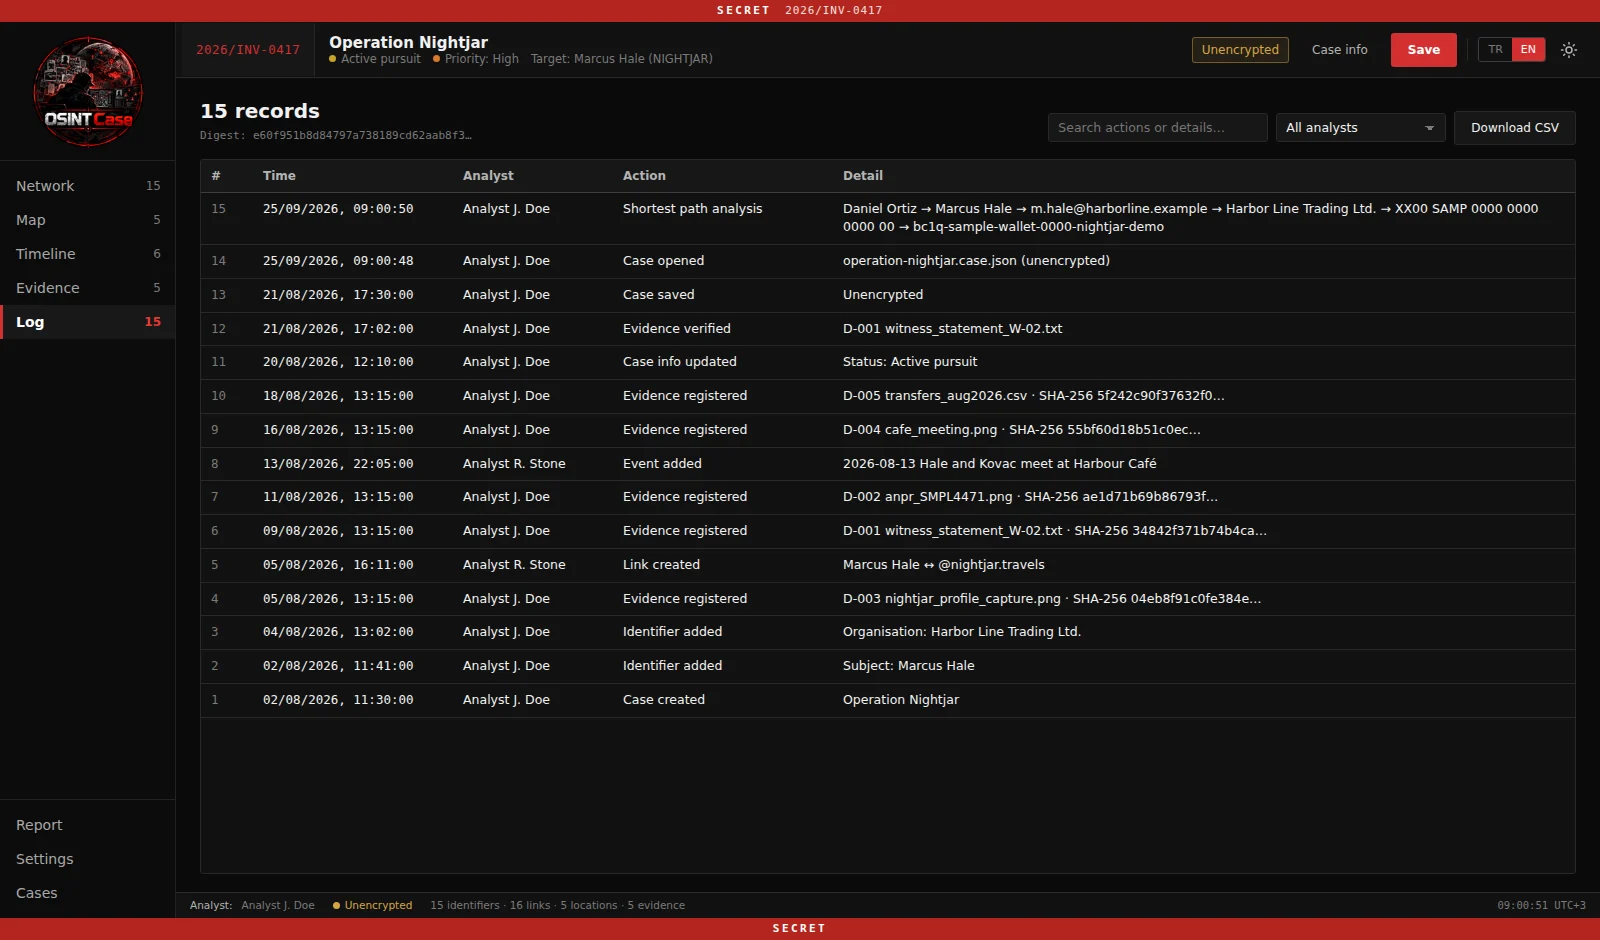
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
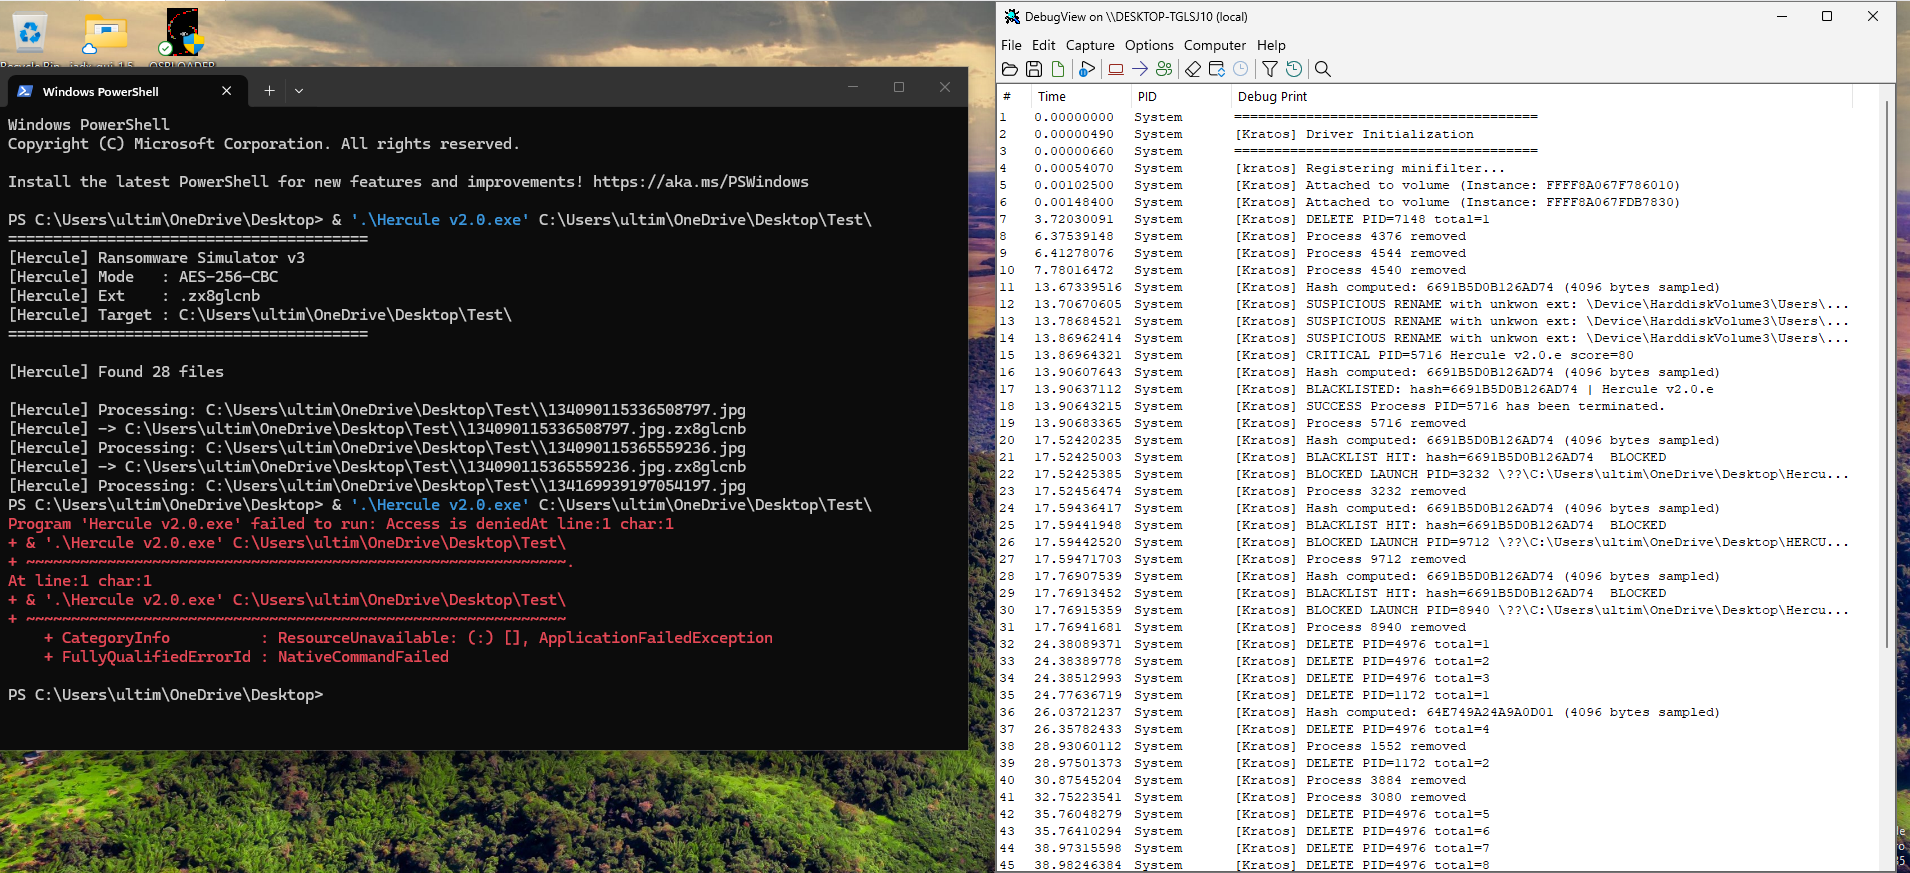 mukendi/kratosminifilter
Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize
 0xv1n/macnoise
Extensible MacOS system telemetry generator.
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
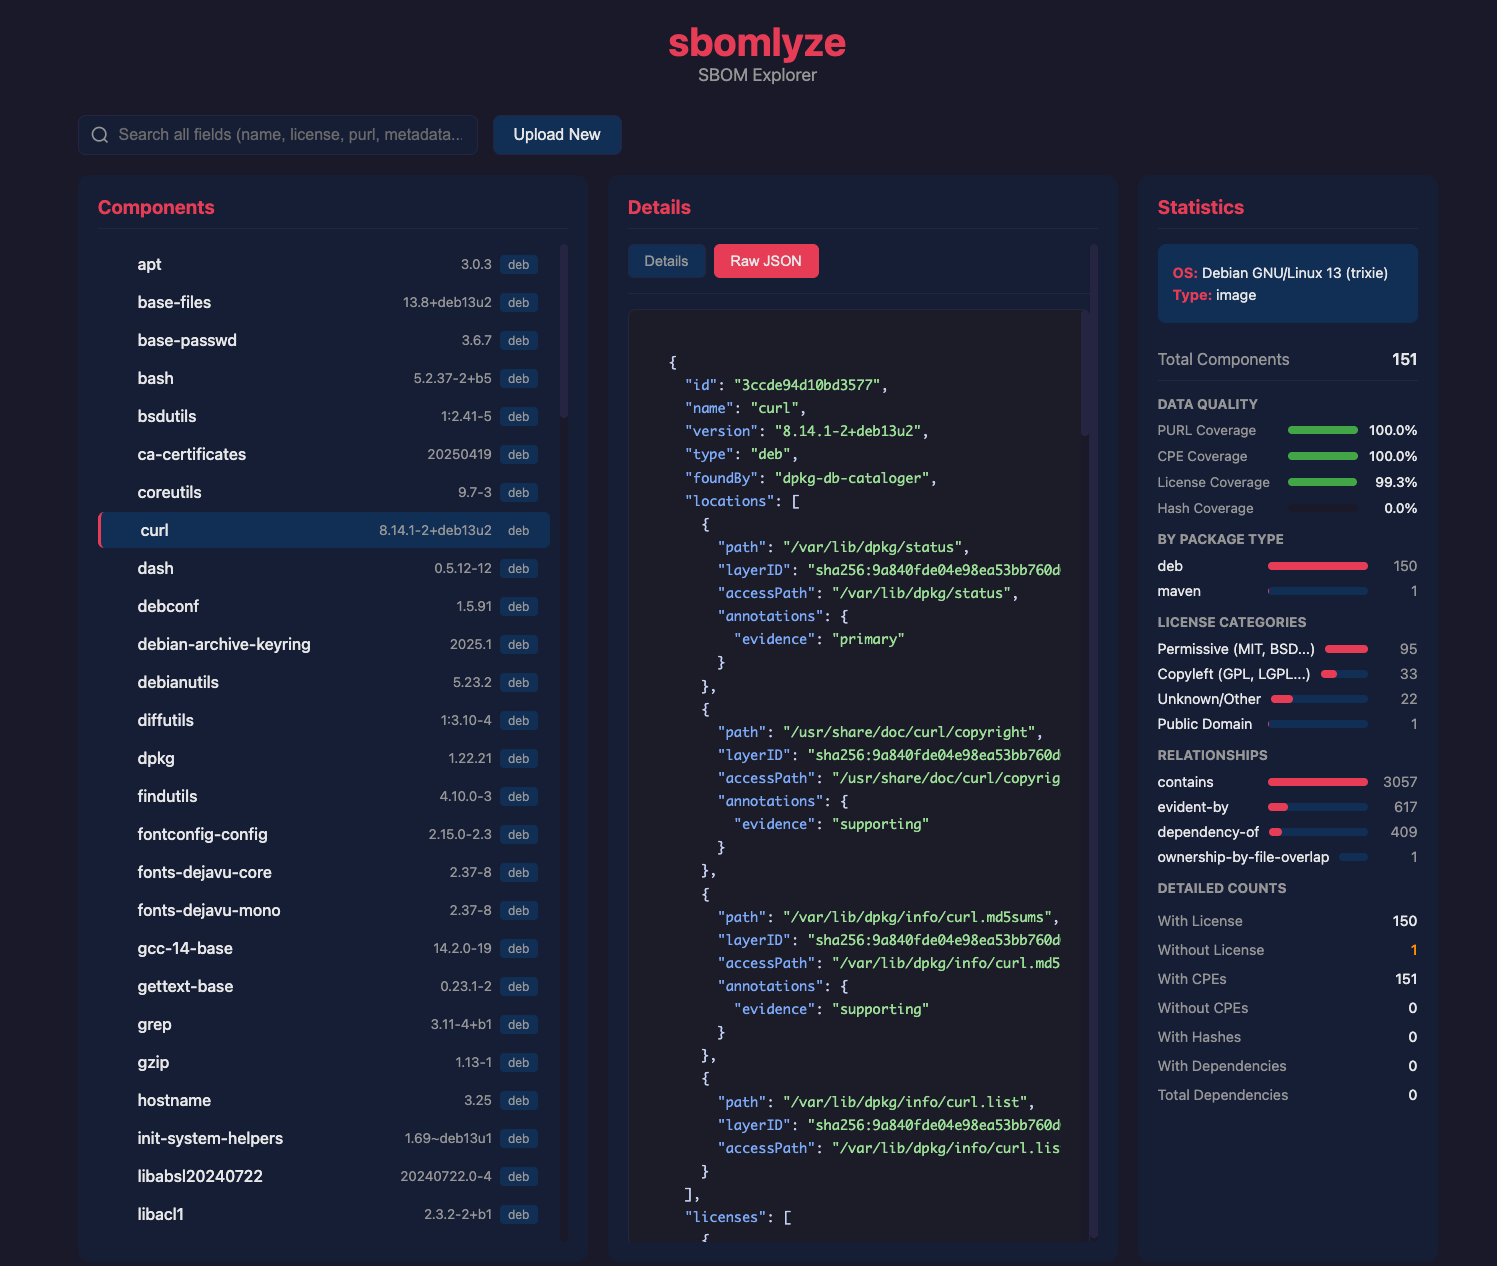 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 target/strelka
Real-time, container-based file scanning at enterprise scale
 kagancapar/cve-2026-54984
CVE-2026-54984 / ZDI-26-543: Windows ICC file parsing out-of-bounds write (CWE-122, CVSS 7.8)
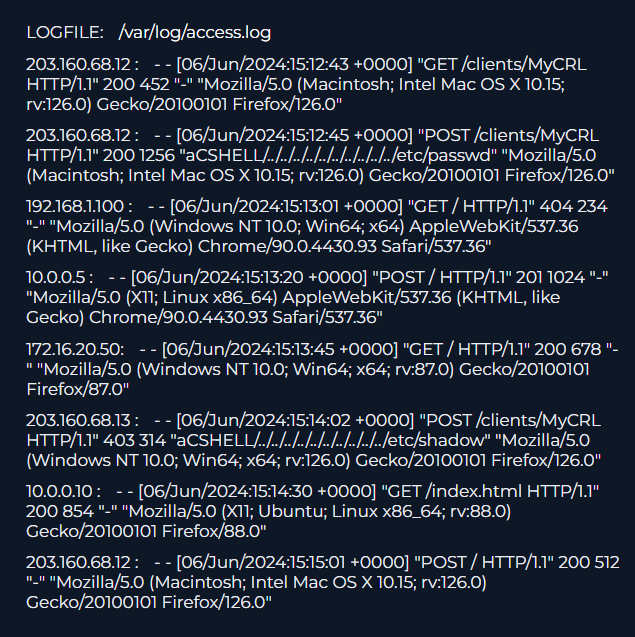 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 corelight/extendintel
This package extends the Intel package to log more fields
 threatlabz/tools
Tools developed by the Zscaler ThreatLabz Threat Intelligence team
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…