
RedTeamSimmer
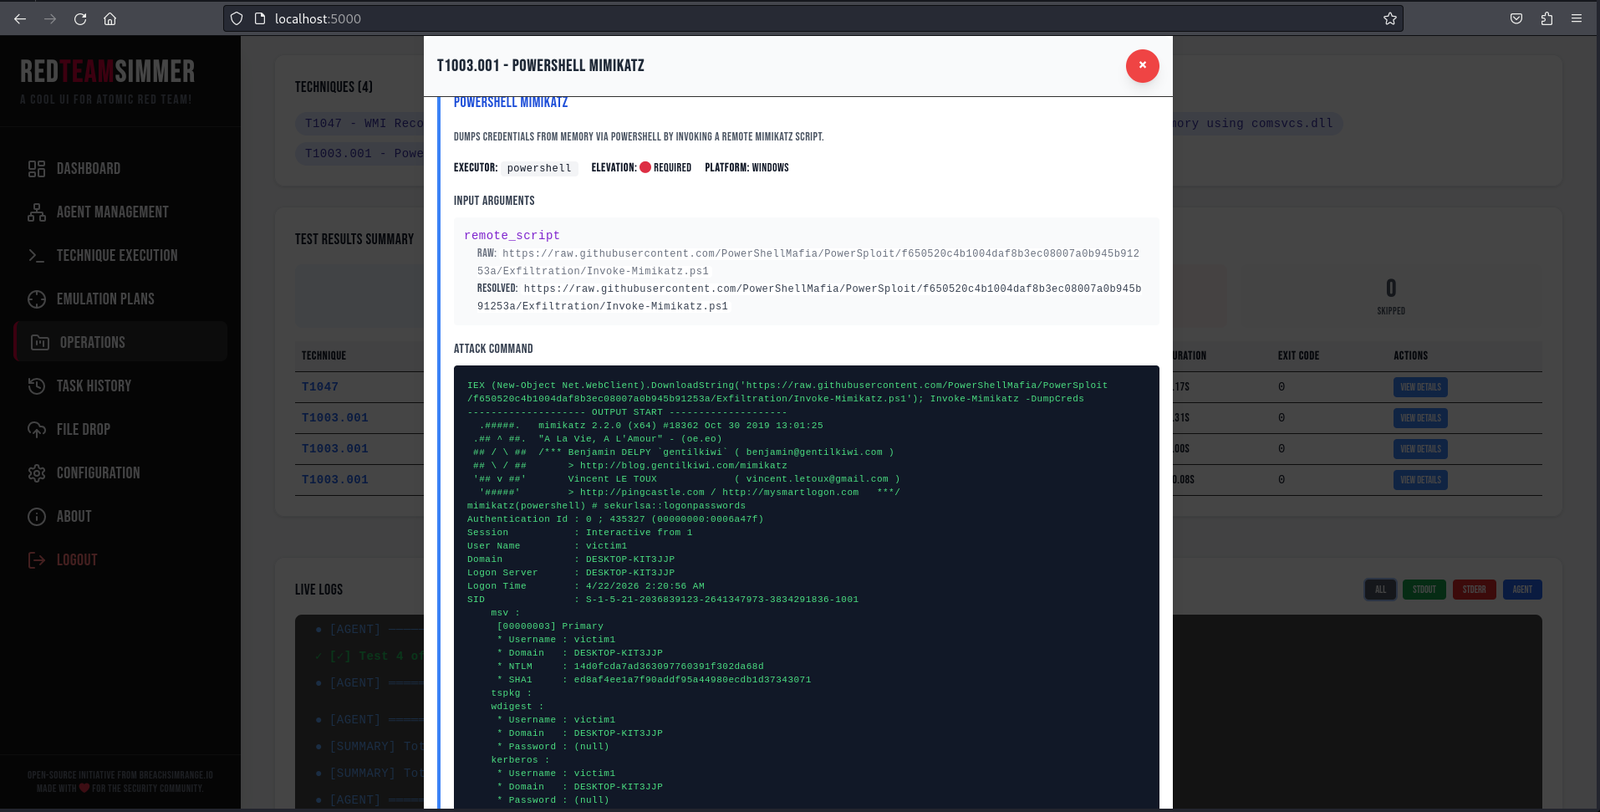
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

Strelka Web UI for File Submission and Analysis

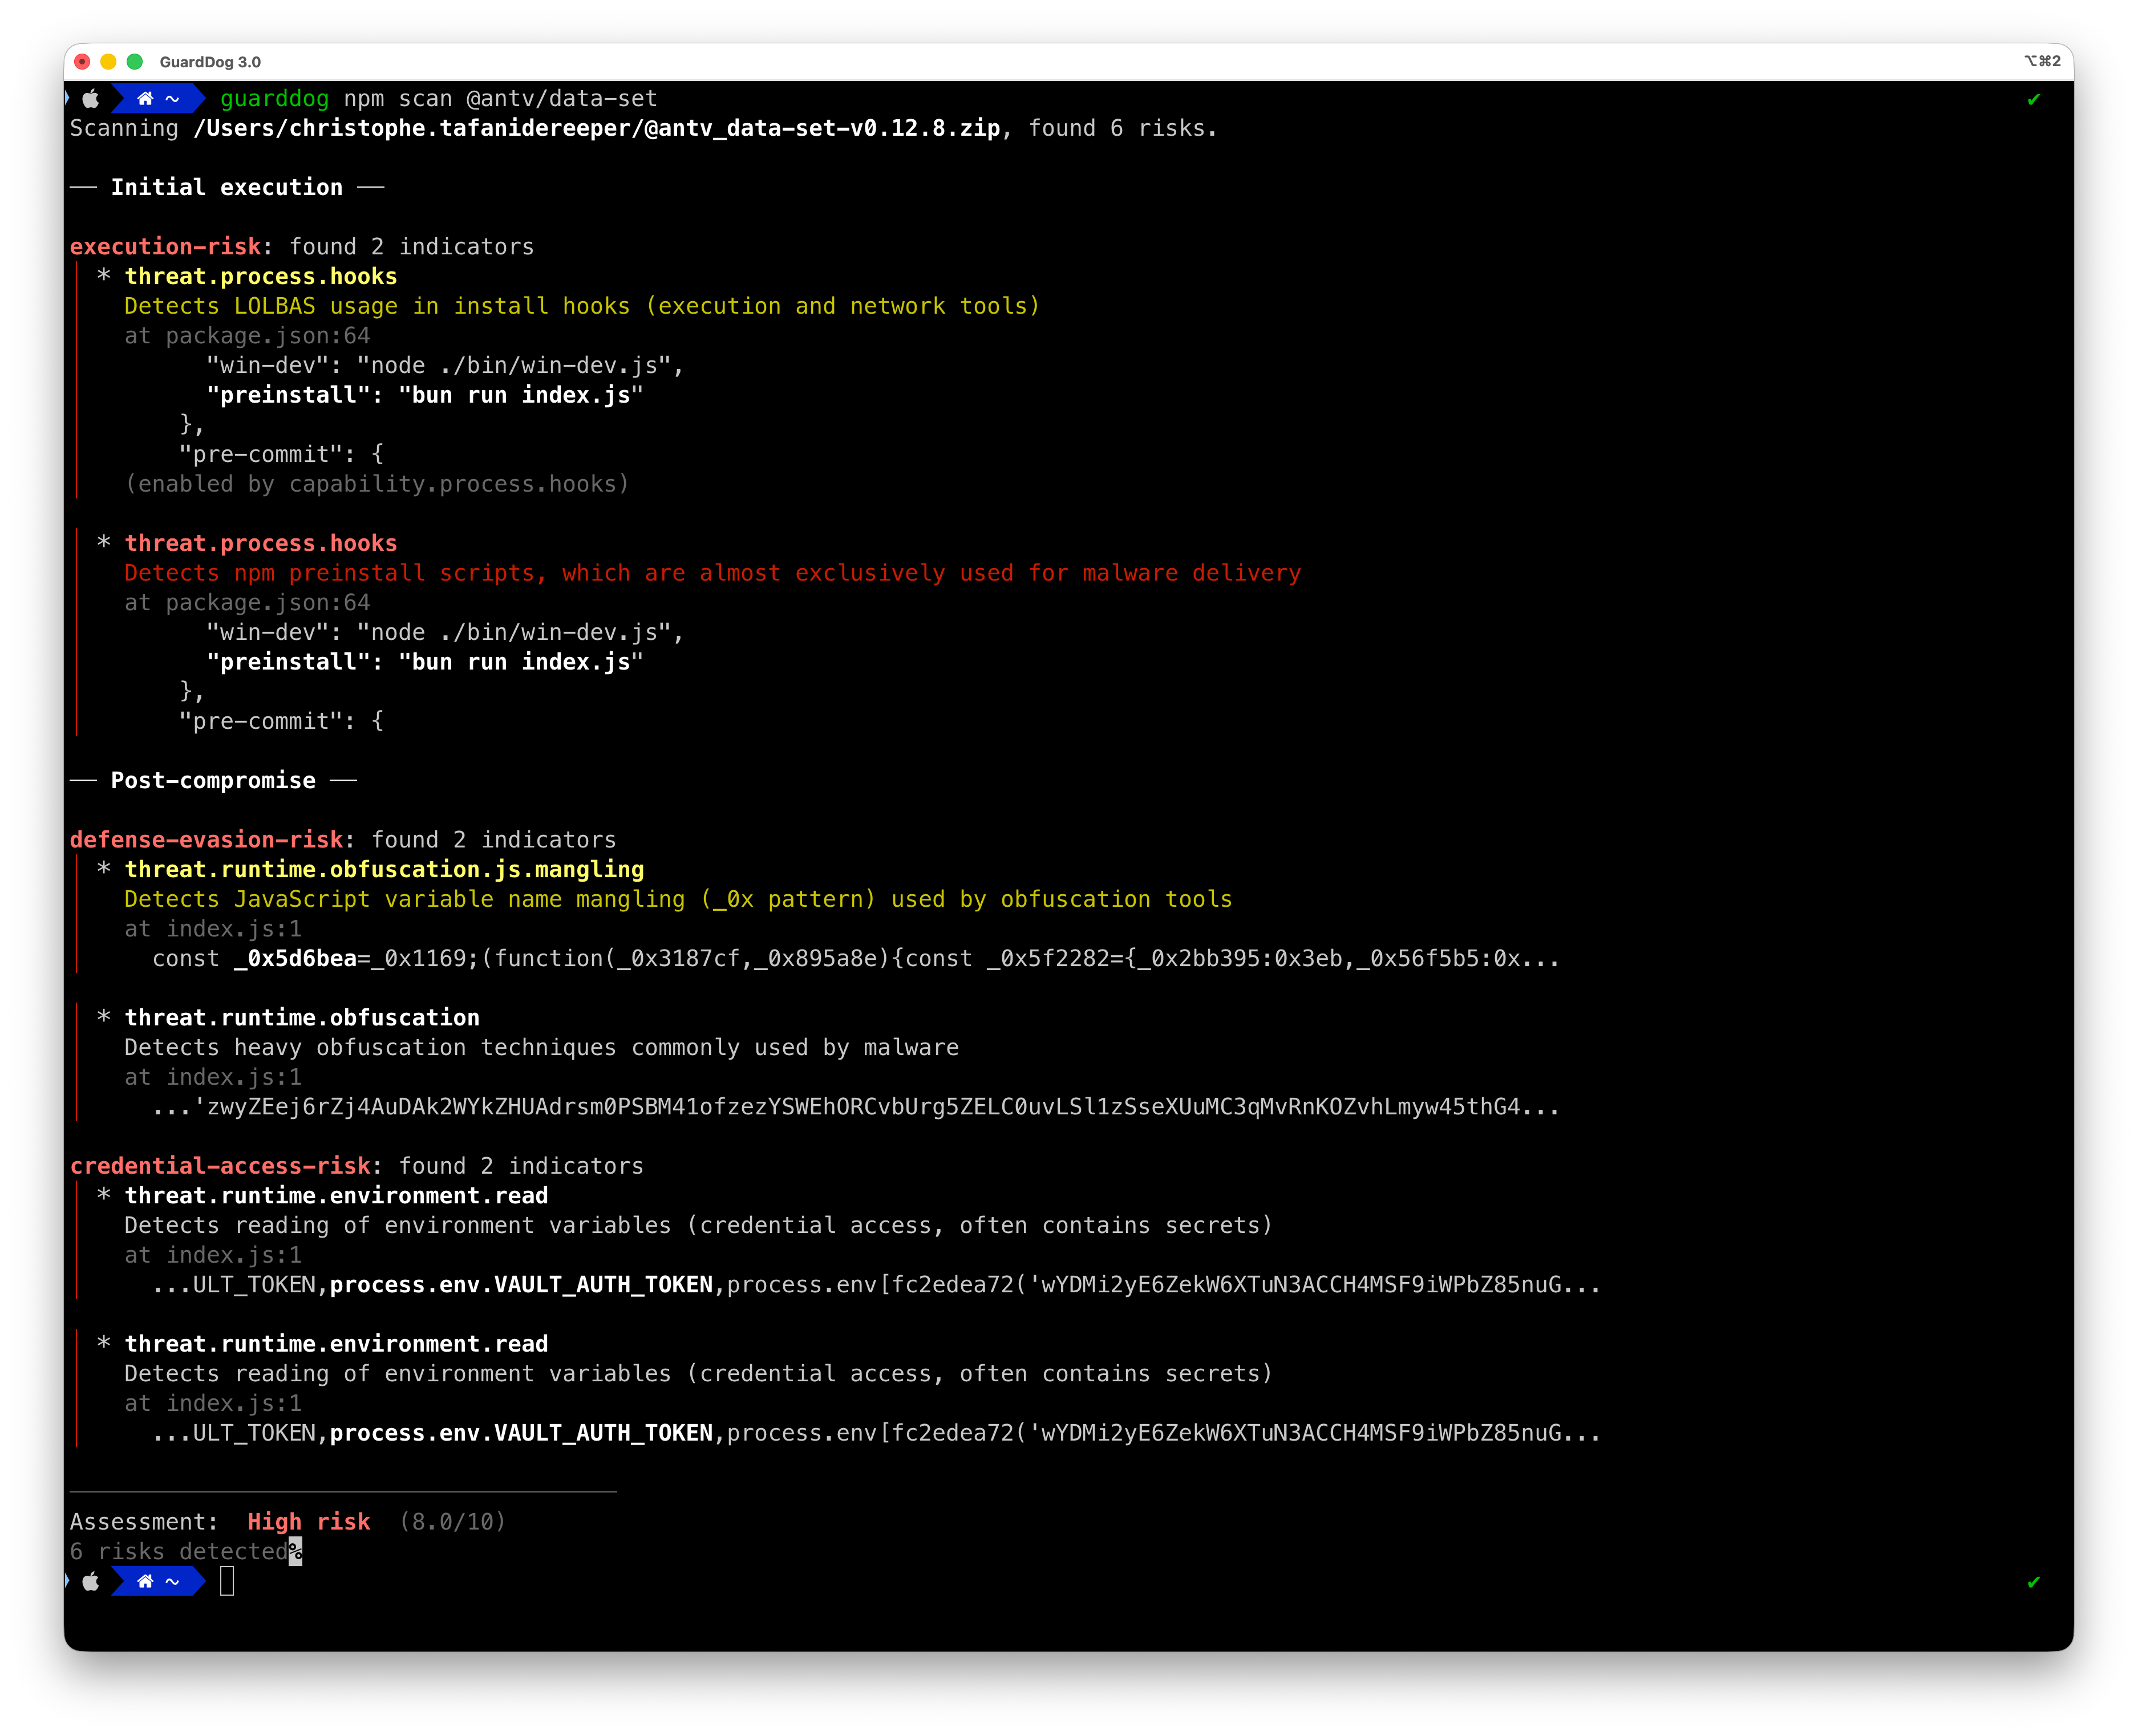
🐍 🔍 GuardDog is a CLI tool to Identify malicious PyPI and npm packages

Python-based scanner for CVE-2025-55182 indicators of compromise. Checks filesystem paths, processes, systemd services, cron persistence, and…

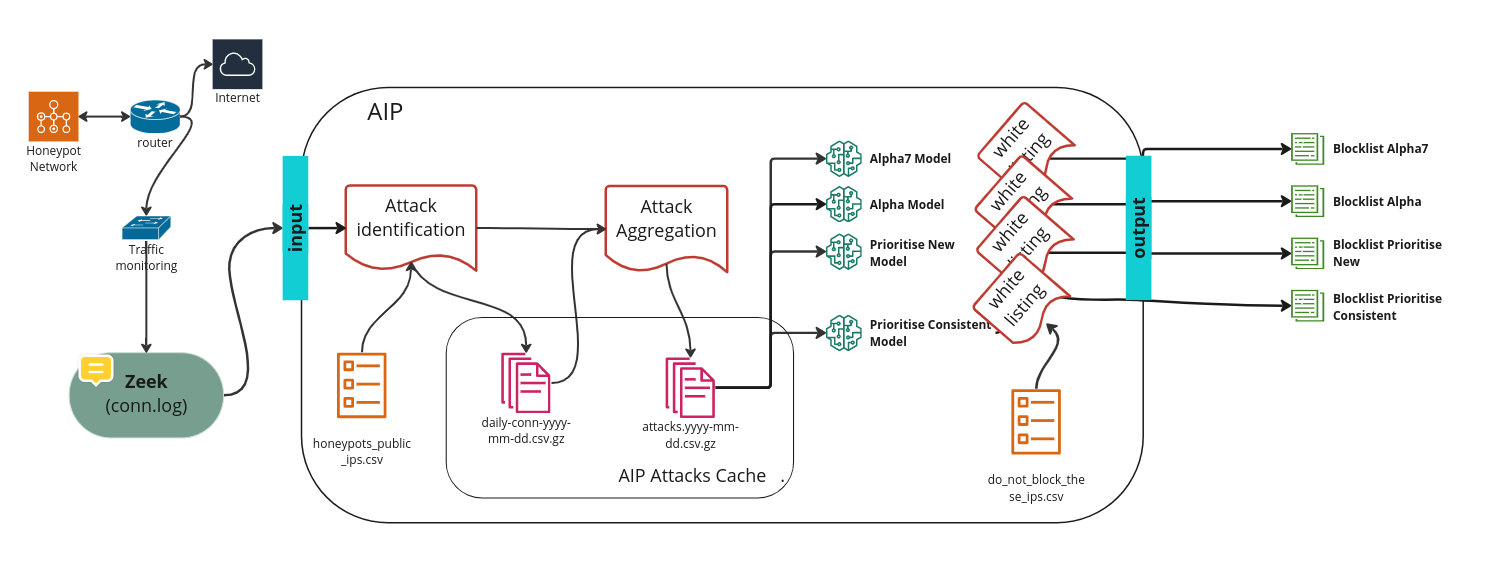
Generates efficient IPv4 blocklists from Zeek network flows using multiple prioritization models (new, consistent, random forest) to identify…

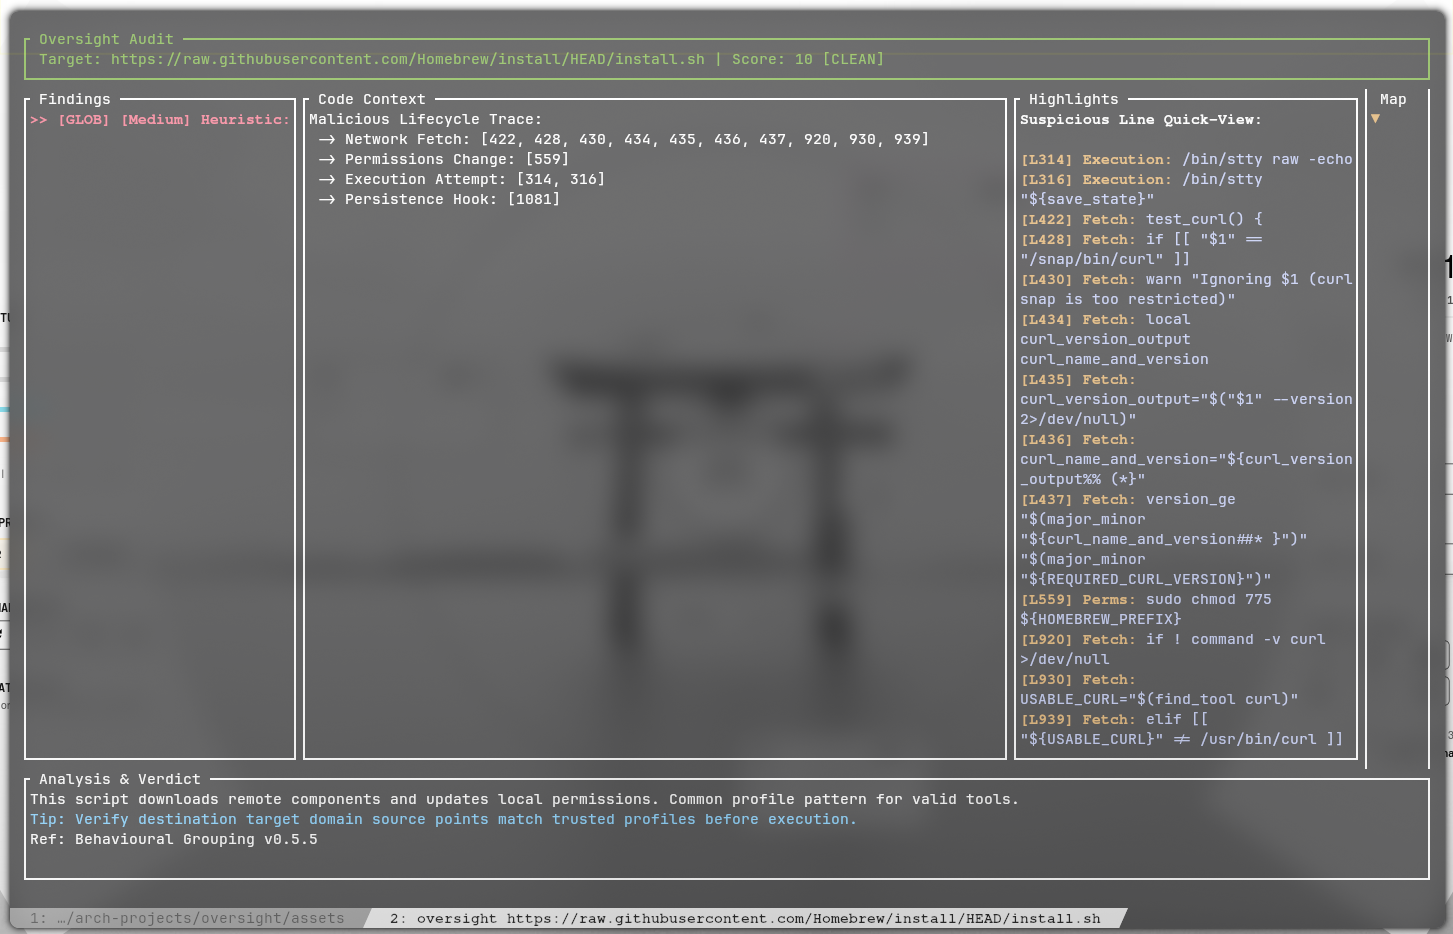
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…

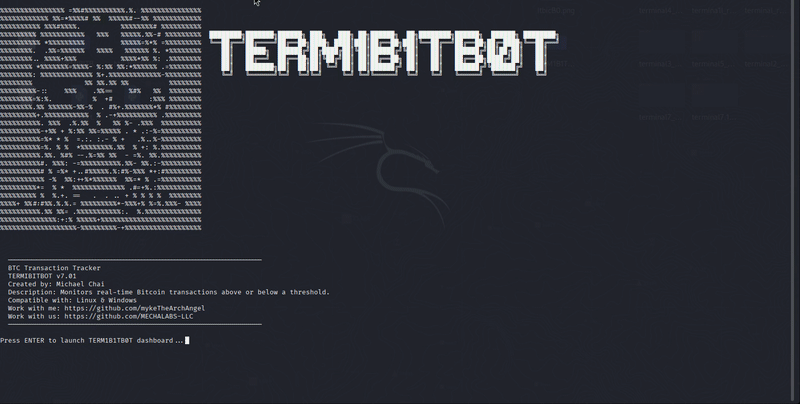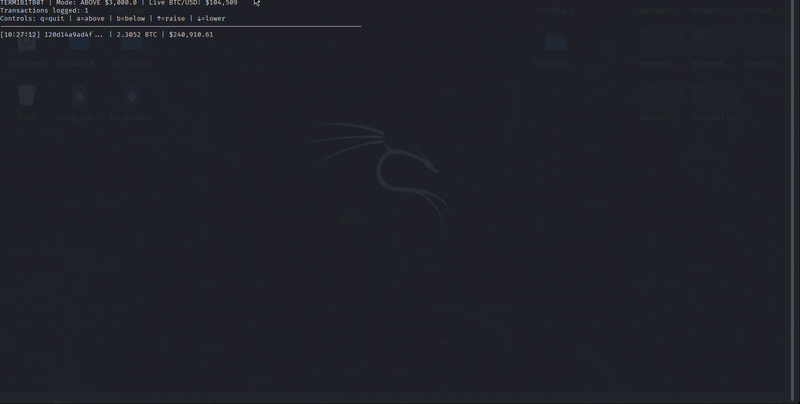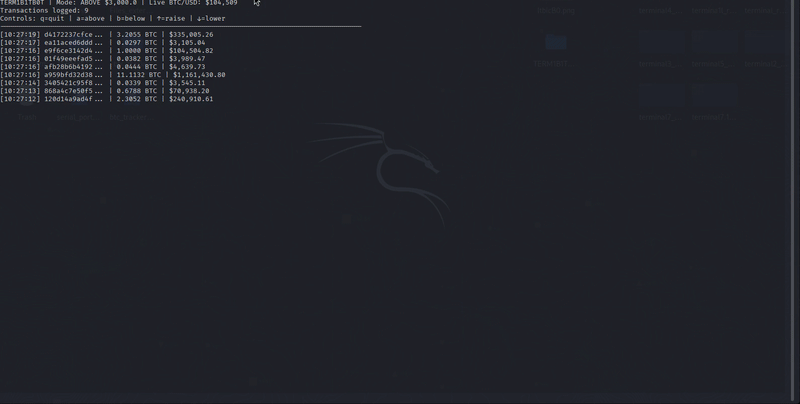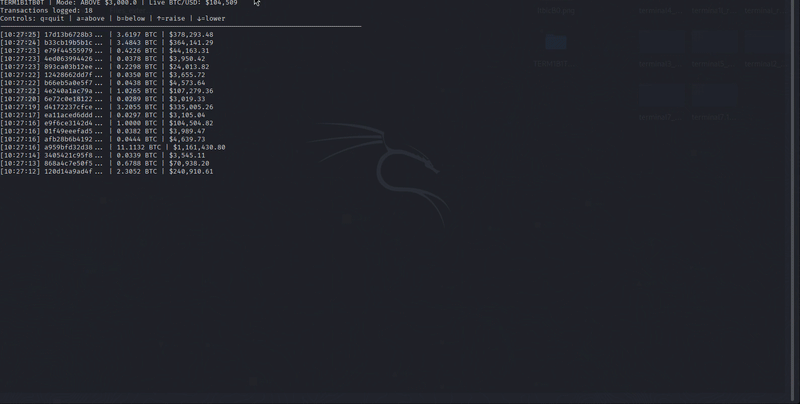
A terminal based tool that monitors real-time Bitcoin transactions above or below a specified threshold.

MAPS cloud scanner and response parser for Microsoft Defender research.

iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.

Investigate malicious Windows logon by visualizing and analyzing Windows event log

A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.

FATT /fingerprintAllTheThings - a pyshark based script for extracting network metadata and fingerprints from pcap files and live network traffic

PatrowlHears - Vulnerability Intelligence Center / Exploits

Python tool that queries the VirusTotal API to check file hashes against 70+ antivirus engines, schedules recurring scans, and exports detection…

ThePhish: an automated phishing email analysis tool