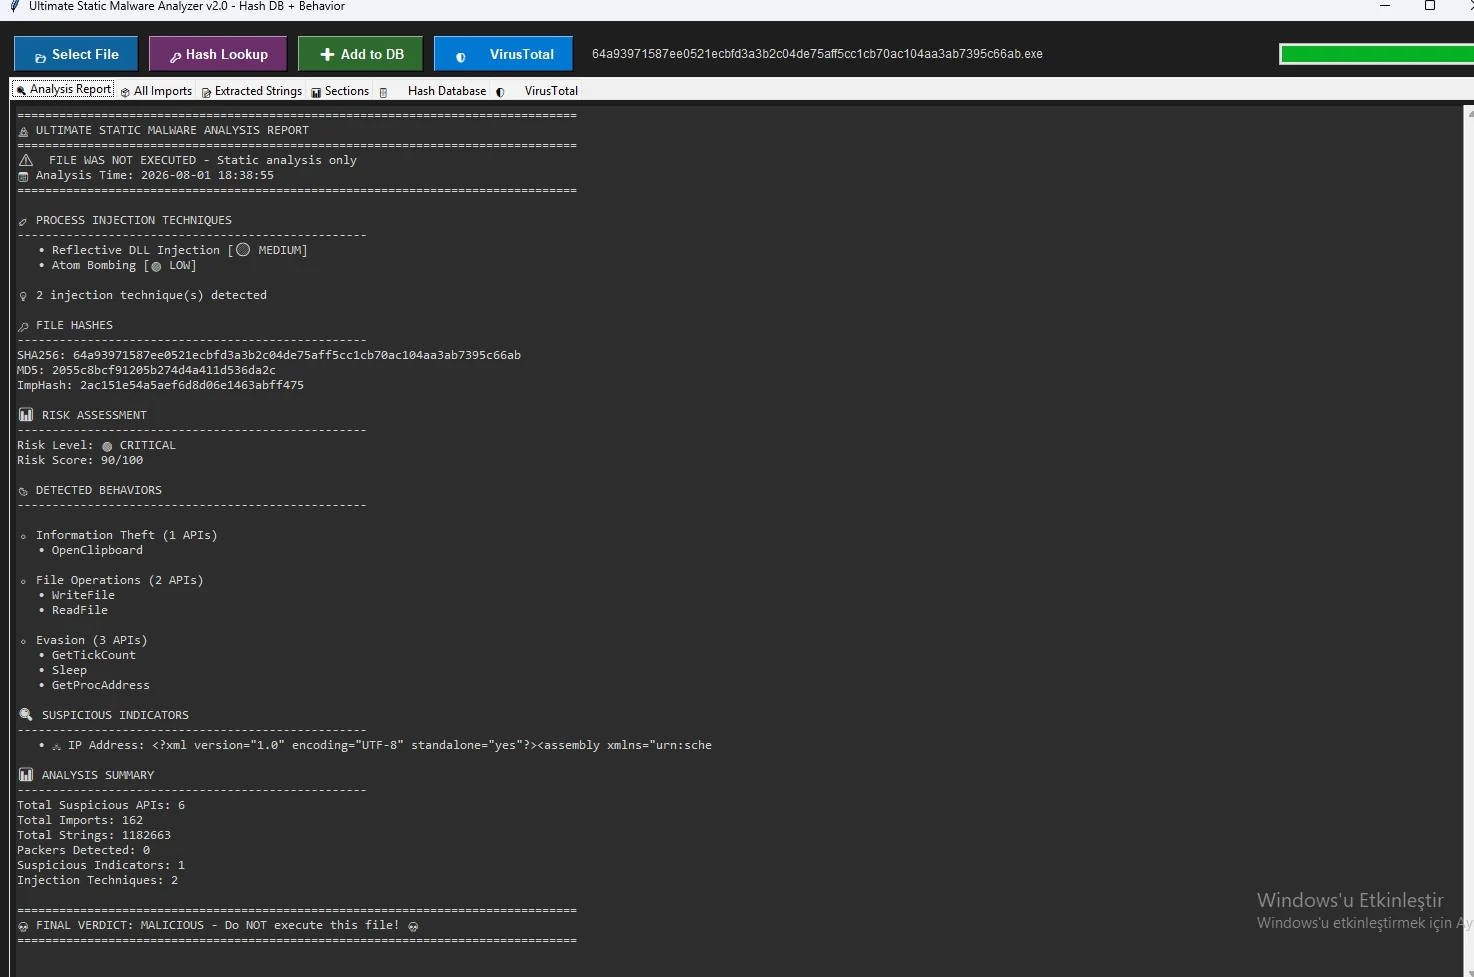
MalwareForge---Advanced-Static-Malware-Analyzer

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Trust & Safety tools for working together to fight digital harms.

Open YARA scan- and search engine

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.

Yara Rules for Modern Malware

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…

Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…

A high interaction SSH honeypot

Check if a IP is from tor or is a malicious proxy

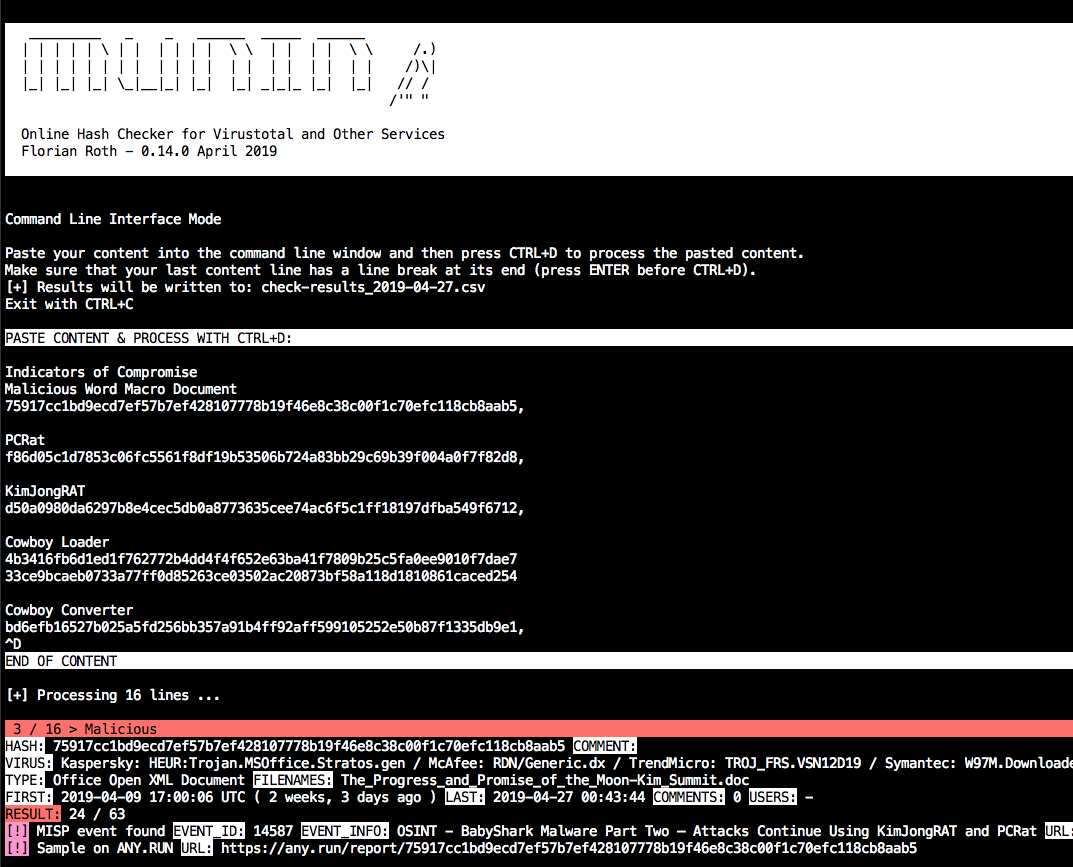
Online hash checker for Virustotal and other services

Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

A modular Python application to pull intelligence about malicious files

The SOC Analysts all-in-one CLI tool to automate and speed up workflow.

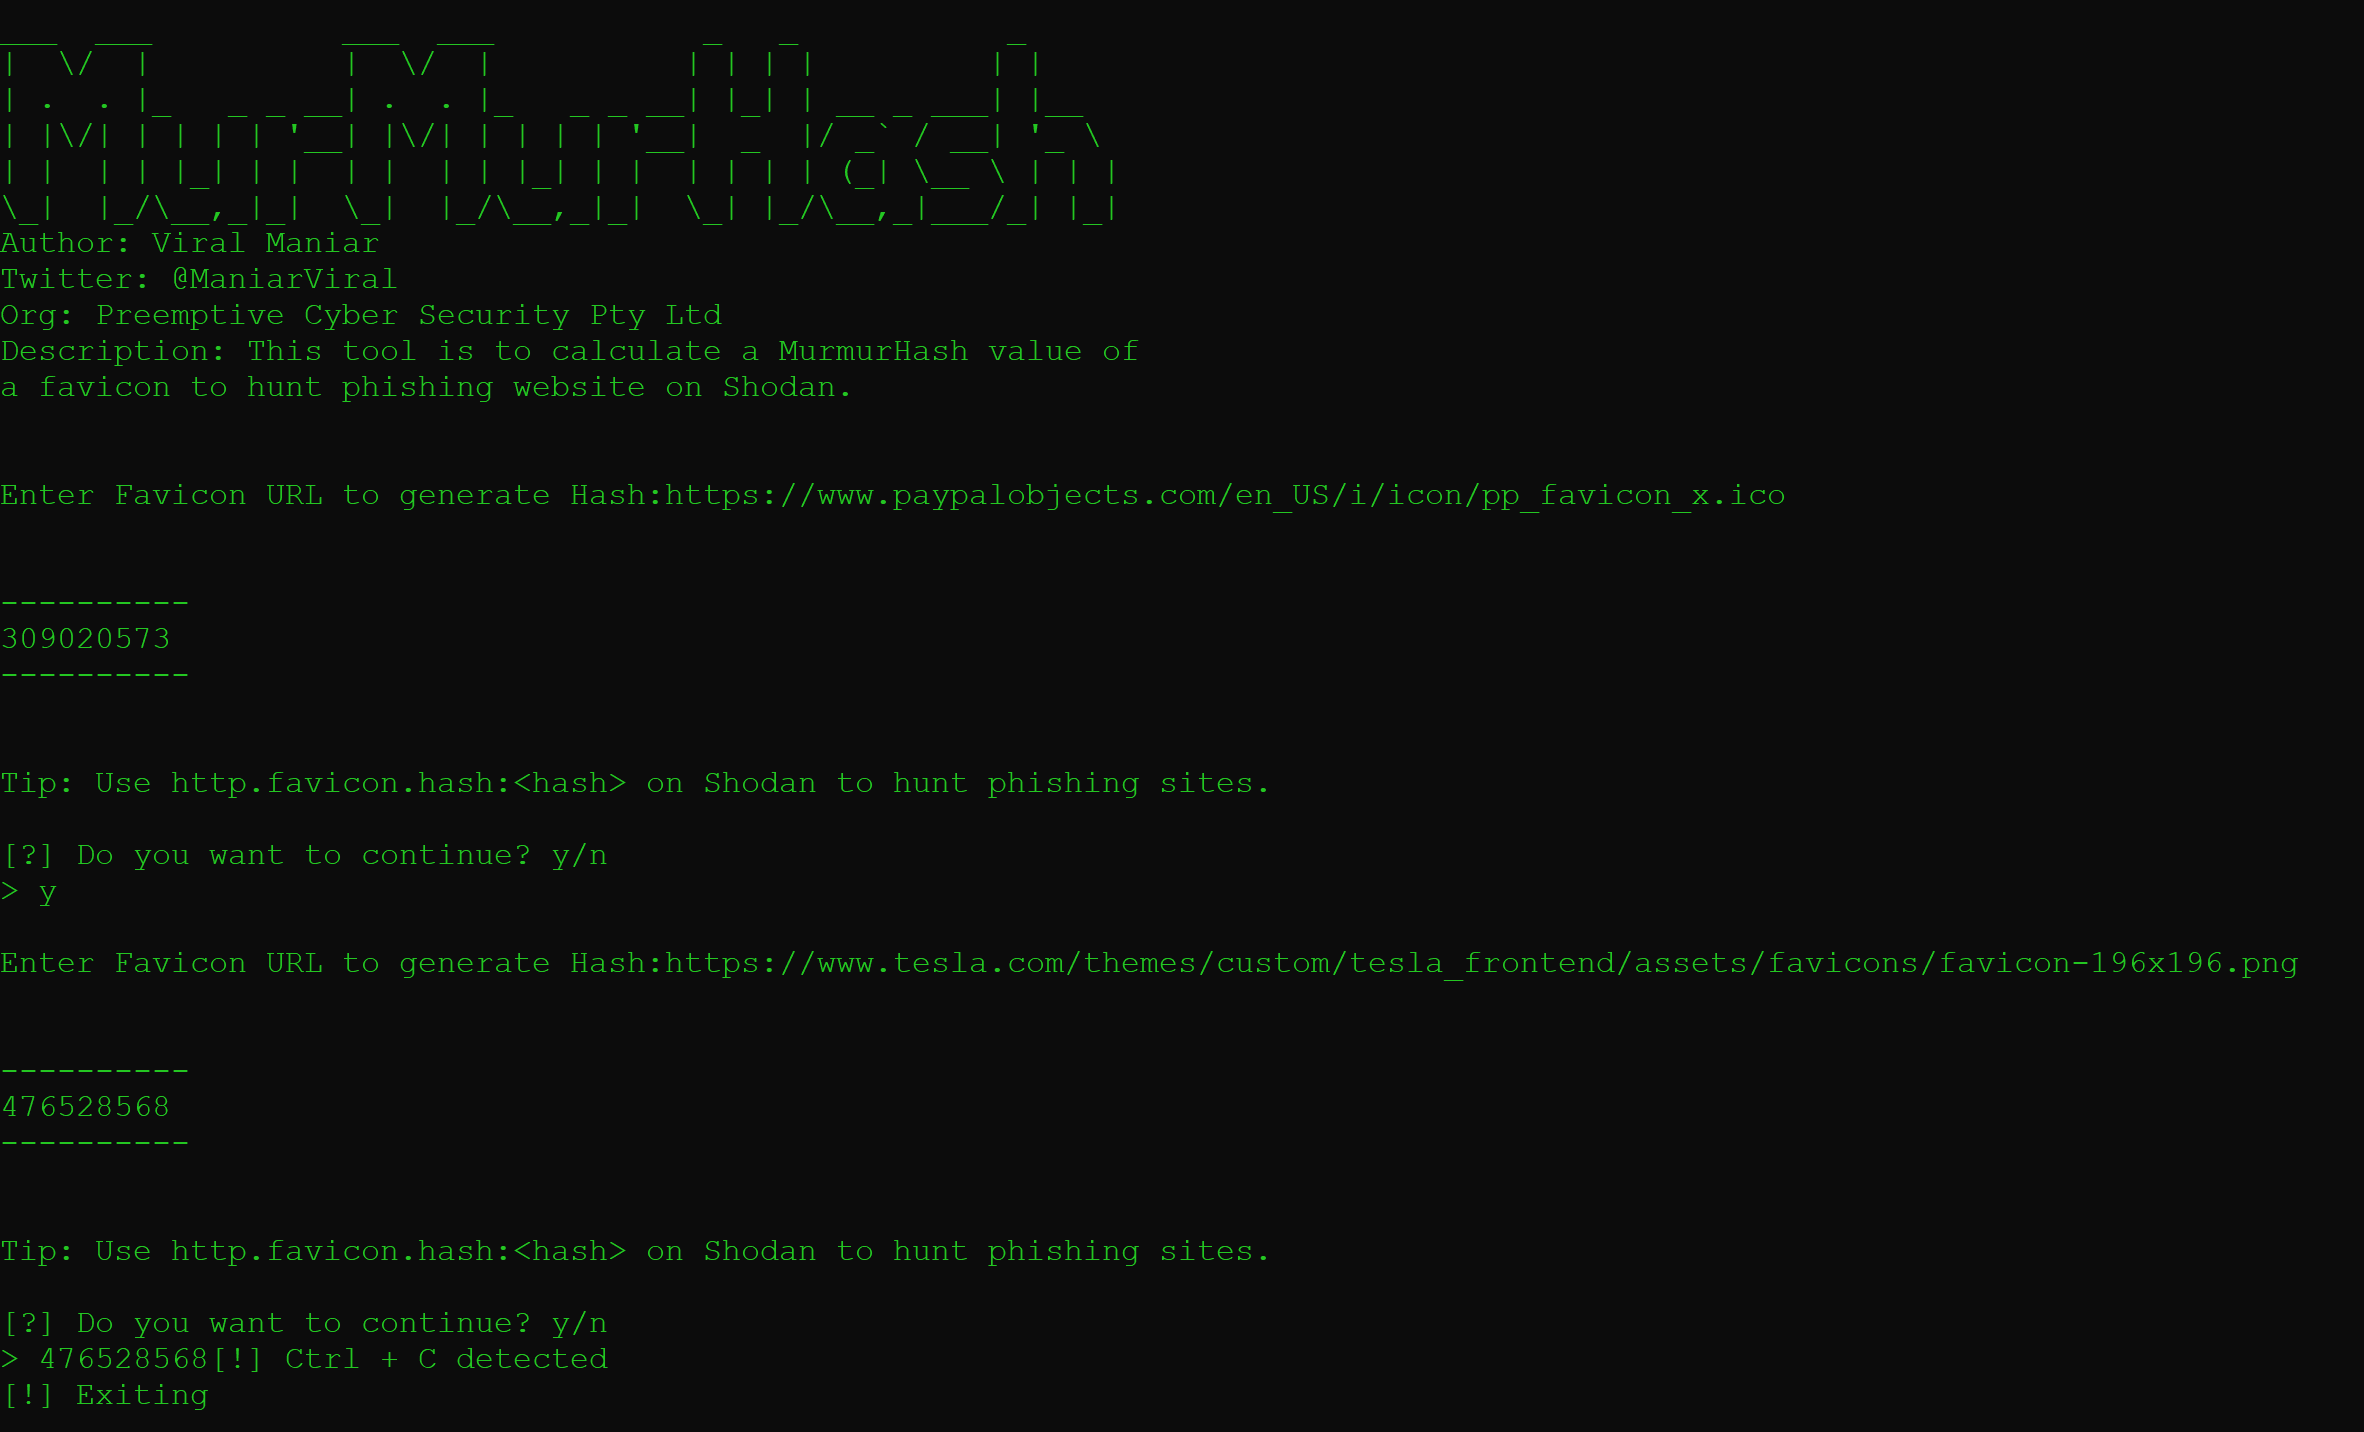
This little tool is to calculate a MurmurHash value of a favicon to hunt phishing websites on the Shodan platform.