SOC335---CVE-2024-49138-Exploitation-Detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

Automated AI powered Facebook intelligence tool for target profiling, network analysis and threat reporting. Runs entirely on-device via Ollama.…

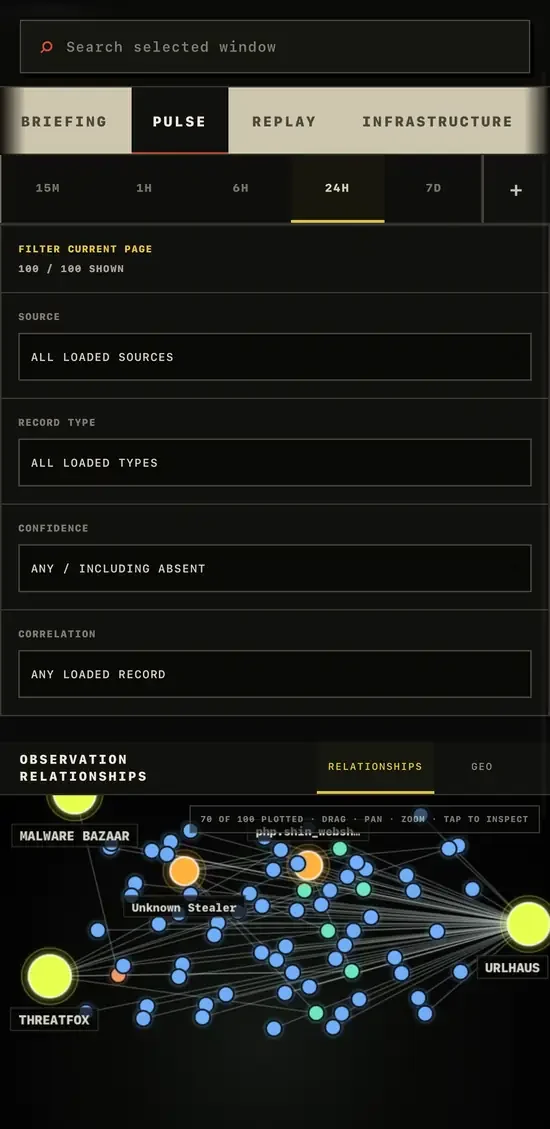
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.

Open Vulnerability Intelligence platform, aggregated intel in one dashboard, with correlation and IOC lookups, completely self hosted. All resources…

Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.

Analysis of malware and Cyber Threat Intel of APT and cybercriminals groups

🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…

A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.


This package extends the Intel package to log more fields

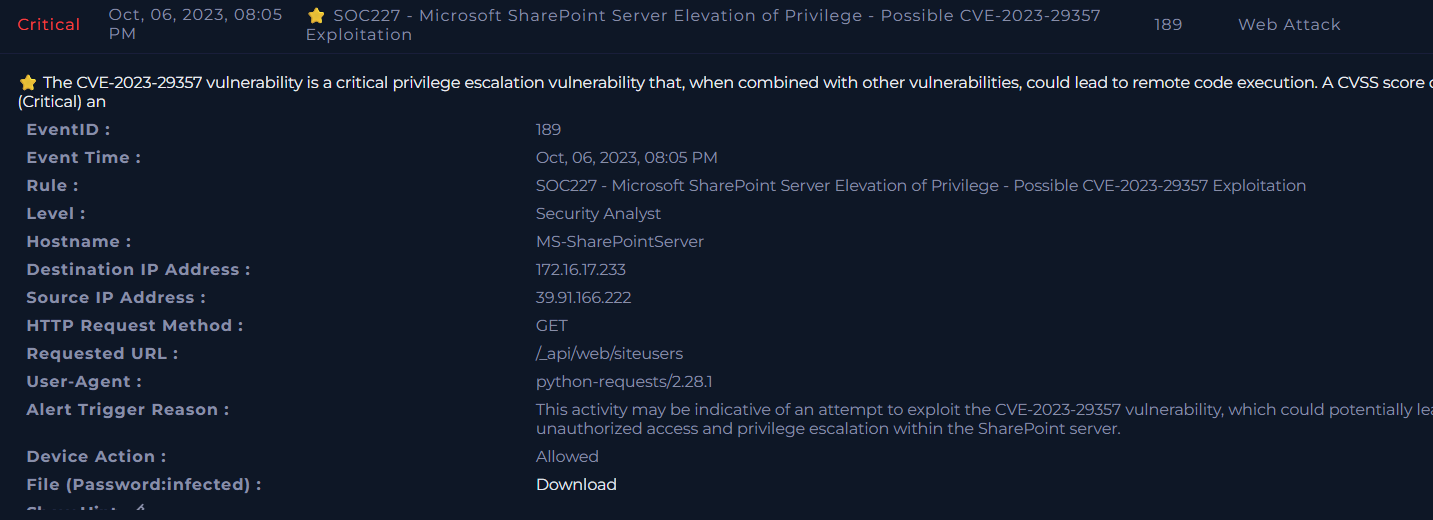
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29375) using SIEM logs,…

Proofpoint - Emerging Threats - Threat Research tools + publicly shared intel and documentation

My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…

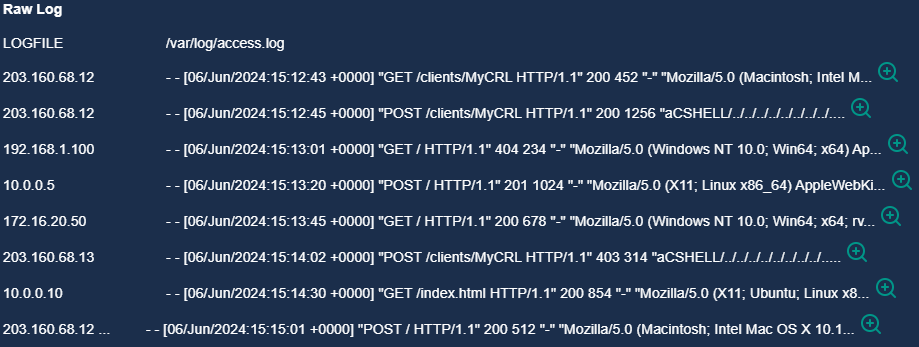
Walkthrough of detecting, investigating, and responding to a CVE-2024-24919 path traversal attack, including log analysis, threat intel checks, and…

This repository contains Yara rule and the method that a security investigator may want to use for CVE-2022-26134 threat hunting on their Linux…