

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
5 days ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
defensive-toolsdigital-forensicsincident-response+2
3033 years ago
rspamd preview

rspamd

GitHubrspamd/rspamd

Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.

defensive-toolsemail-securityphishing+1
2.5k1 day ago
DShield-SIEM preview

DShield-SIEM

GitHubbruneaug/dshield-siem

DShield Sensor Log Collection with ELK

defensive-toolsincident-responseintrusion-detection+4
501 month ago
icannTLD preview

icannTLD

GitHubcorelight/icanntld

Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…


dns-analysisinformation-gatheringintrusion-detection+3
81 year ago
Securekit preview

Securekit

GitLabroxanne_ardary/securekit

Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
ai-securityapi-securitycloud-security+5
2 months ago
Log4Pot preview

Log4Pot

GitHubthomaspatzke/log4pot

A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
intrusion-detectionlog-analysispayload-generation+2
941 year ago
CVE-2025-32433-Detection preview

CVE-2025-32433-Detection

GitHubte0rwx/cve-2025-32433-detection

Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…

incident-responseintrusion-detectionmalware-analysis+2
2 months ago
DesckVB-RAT preview

DesckVB-RAT

GitHubshadowopcode/desckvb-rat

Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain

command-and-controldigital-forensicseducation+8
97 months ago
My-Sigma-Rule-Collection preview

My-Sigma-Rule-Collection

GitHub17patmaks/my-sigma-rule-collection

Sigma Rule for CVE-2025-49666
curated-resourceseducationintrusion-detection+3
6 months ago
agent-scanning preview

agent-scanning

GitHubvigil-xy/agent-scanning

Unified dashboard to monitor, govern, and audit AI agents in real-time. Enforce budgets, detect policy violations, and export compliance reports for…
ai-securityapi-securitycloud-security+2
66 months ago
agentwatch preview

agentwatch

GitHubfarjadahmed/agentwatch

Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
forensicsincident-responselog-analysis+2
126 months ago
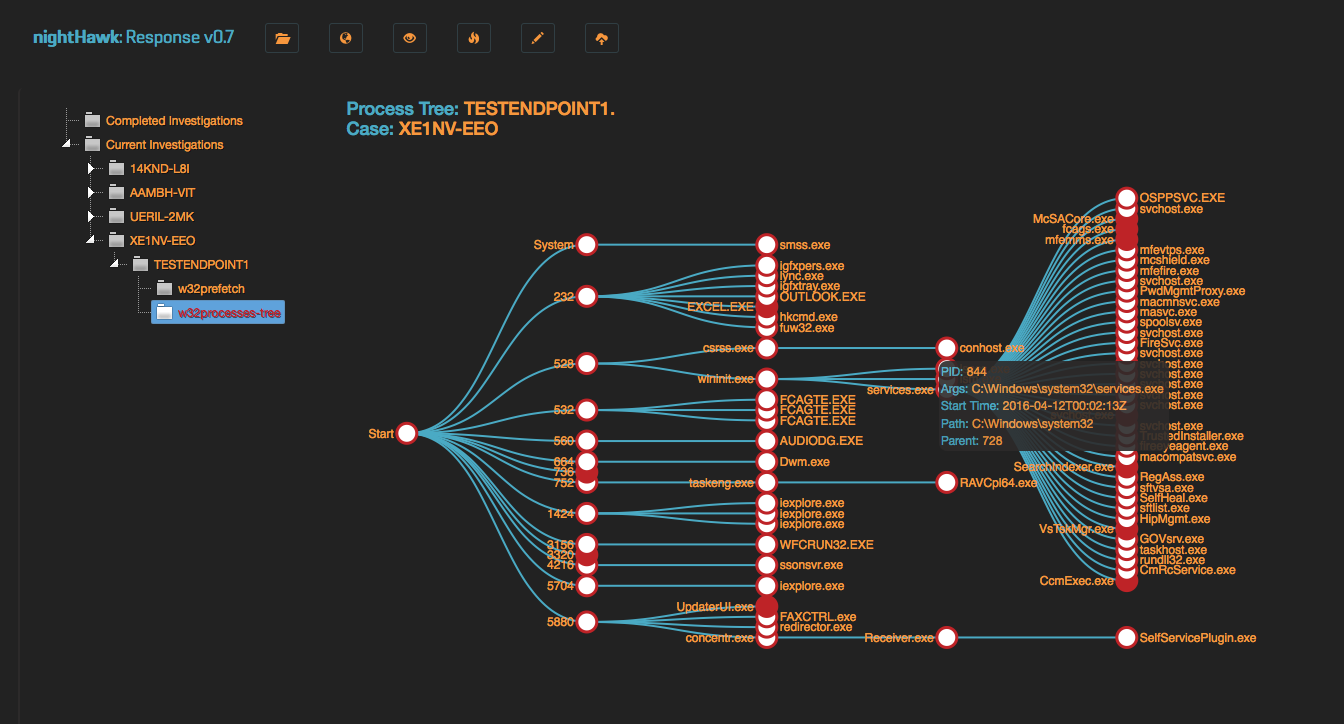
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework
digital-forensicsdisk-forensicsforensics+7
6076 years ago
grafeo preview

grafeo

GitHubmnemonic-no/grafeo

Open platform for modelling, collection and exchange of knowledge
data-exfiltrationinformation-gatheringthreat-intelligence+1
1661 year ago
CloudGrappler preview

CloudGrappler

GitHubpermiso-io-tools/cloudgrappler

Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.

cloud-securitydefensive-toolsincident-response+2
26710 months ago
PurpleKeep preview

PurpleKeep

GitHubretrospected/purplekeep

Providing Azure pipelines to create an infrastructure and run Atomic tests.

cloud-securityeducationincident-response+4
533 years ago
opencve preview

opencve

GitHubopencve/opencve

Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
incident-responseioc-managementthreat-intelligence+2
2.8k10 days ago
melody preview
Archived

melody

GitHubma111e/melody

Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.

information-gatheringintrusion-detectionnetwork-security+5
1391 year ago