Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
MalwareForge---Advanced-Static-Malware-Analyzer preview

MalwareForge---Advanced-Static-Malware-Analyzer

GitHubkaandemir993/malwareforge---advanced-static-malware-analyzer

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

binary-analysishash-analysismalware-analysis+2
41 month ago
purple-team-exercise-framework preview

purple-team-exercise-framework

GitHubscythe-io/purple-team-exercise-framework

Purple Team Exercise Framework

adversarial-attackai-securitycloud-security+5
8205 months ago
uefi_bootkit_softlanding preview

uefi_bootkit_softlanding

GitHubares-sys/uefi_bootkit_softlanding

First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…

defensive-toolsdigital-forensicsfirmware-analysis+5
1 month ago
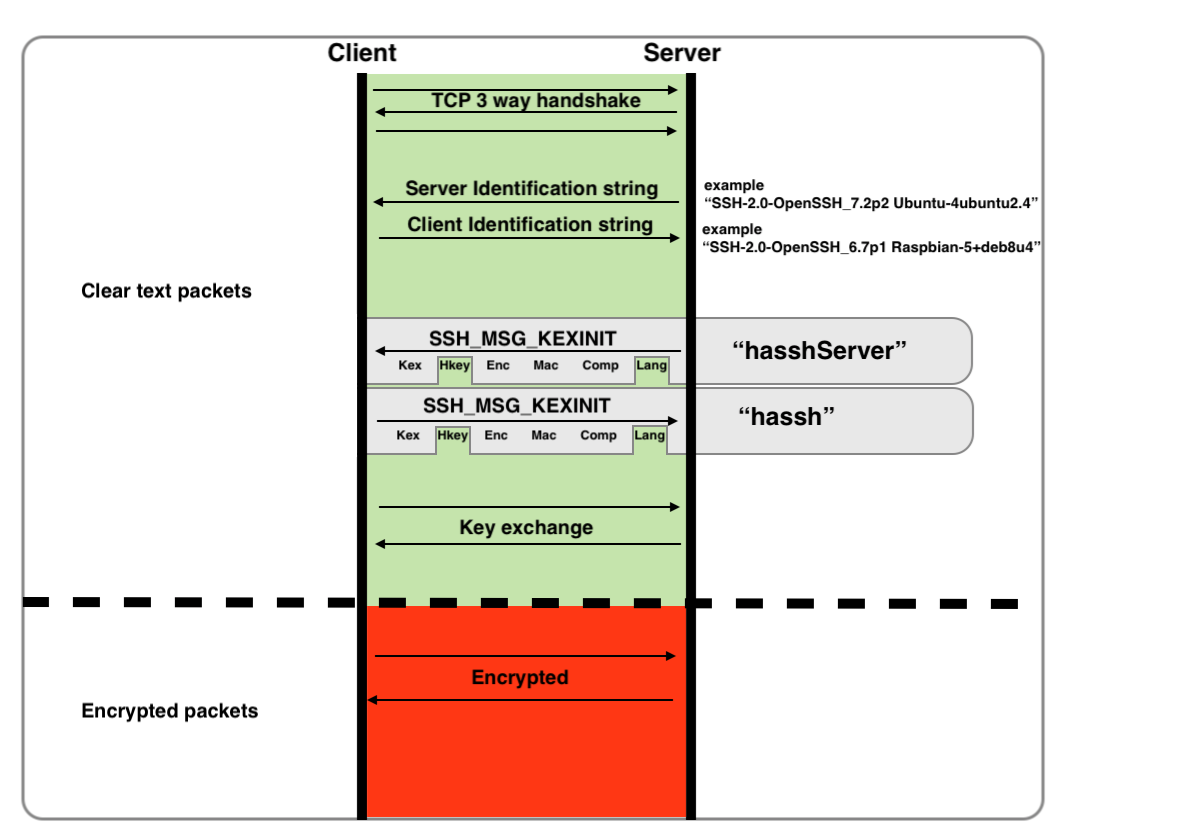
hassh preview

hassh

GitHubcorelight/hassh

Fingerprint SSH clients and servers.

anomaly-detectionforensicsintrusion-detection+4
122 years ago
pingback preview

pingback

GitHubcorelight/pingback

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.

command-and-controlintrusion-detectionmalware-analysis+2
1111 months ago
follina-msdt-threat-investigation preview

follina-msdt-threat-investigation

GitHubzavikhttak/follina-msdt-threat-investigation

🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…

digital-forensicseducationincident-response+4
2 months ago
loki-parse preview

loki-parse

GitHubr3mrum/loki-parse

A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…

data-exfiltrationdigital-forensicsforensics+5
139 years ago
CVE-2021-31166-detection-rules preview

CVE-2021-31166-detection-rules

GitHubmvlnetdev/cve-2021-31166-detection-rules

Different rules to detect if CVE-2021-31166 is being exploited

exploitationintrusion-detectionnetwork-security+3
34 years ago
fortileak-01-2025-Be preview

fortileak-01-2025-Be

GitHubniklasmato/fortileak-01-2025-be

This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…

incident-responseinformation-gatheringioc-management+3
1 year ago
InfoSec-Black-Friday preview

InfoSec-Black-Friday

GitHub0x90n/infosec-black-friday

All the deals for InfoSec related software/tools this Black Friday

cloud-securitycurated-resourceseducation+9
4.4k9 months ago
log4shell_ioc_ips preview

log4shell_ioc_ips

GitHubhackinghippo/log4shell_ioc_ips

log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)

incident-responseinformation-gatheringioc-management+3
374 years ago
CVE-2020-5902-F5BigIP preview

CVE-2020-5902-F5BigIP

GitHubcorelight/cve-2020-5902-f5bigip

A network detection package for CVE-2020-5902, a CVE10.0 vulnerability affecting F5 Networks, Inc BIG-IP devices.

exploitationincident-responseintrusion-detection+3
45 years ago
cve-2026-5950-bind9-resolver-dos preview

cve-2026-5950-bind9-resolver-dos

GitHubbillybaraja/cve-2026-5950-bind9-resolver-dos

Defensive research notes for CVE-2026-5950, a BIND 9 resolver DoS vulnerability credited to Billy Baraja (BielraX).

defensive-toolsdns-analysiseducation+3
13 months ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…

android-securitydynamic-analysis-sandboxingforensics+8
1836 minutes ago
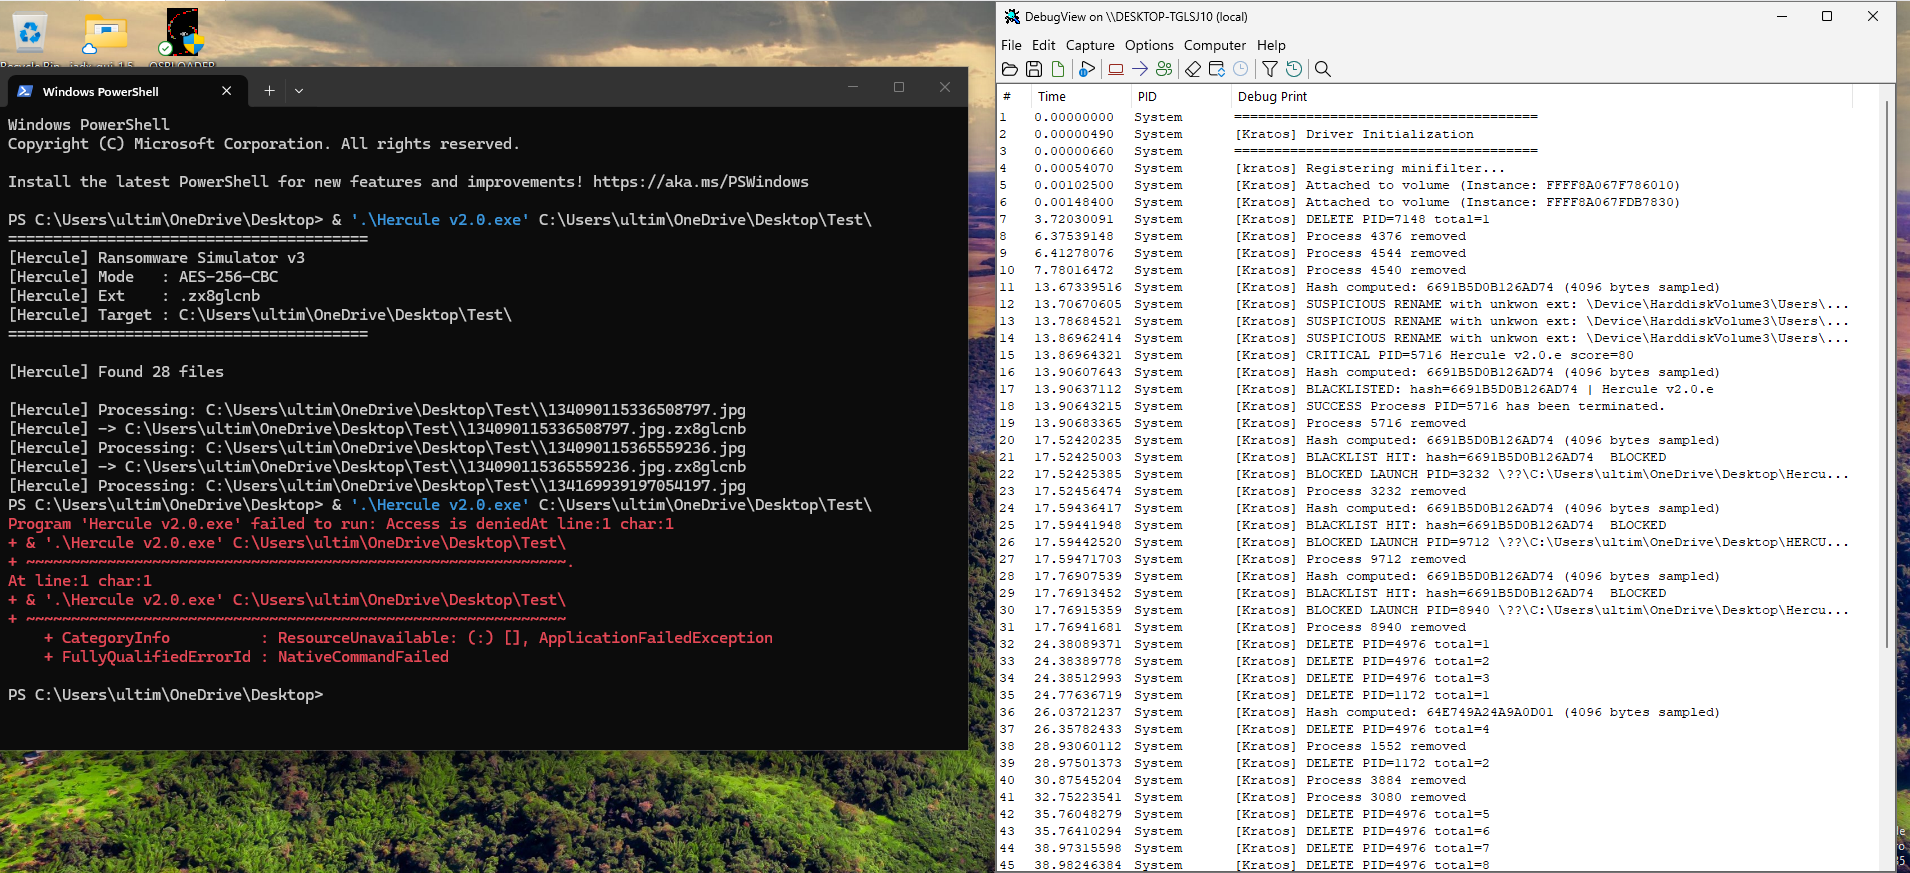
kratosminifilter preview

kratosminifilter

GitHubmukendi/kratosminifilter

Kratos is a high-performance Windows File System Minifilter driver designed to detect, block, and permanently immunize

anomaly-detectiondefensive-toolsincident-response+2
47 days ago
sigma-ai preview

sigma-ai

GitHubagentshield-ai/sigma-ai

Sigma detection rules for AI agent security monitoring

ai-securityanomaly-detectiondata-exfiltration+8
151 month ago
mcp-security-checklist preview

mcp-security-checklist

GitHubhelixar-ai/mcp-security-checklist

MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…

ai-securityapi-securityauthentication-authorization+5
226 months ago
Minesweeper preview

Minesweeper

GitHubcodingo/minesweeper

A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).

cryptographythreat-intelligencevulnerability-scanners+1
2037 years ago
Previous12Next