
spamassassin
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
defensive-toolsemail-securitymachine-learning+1
345
apache/spamassassinOpen-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
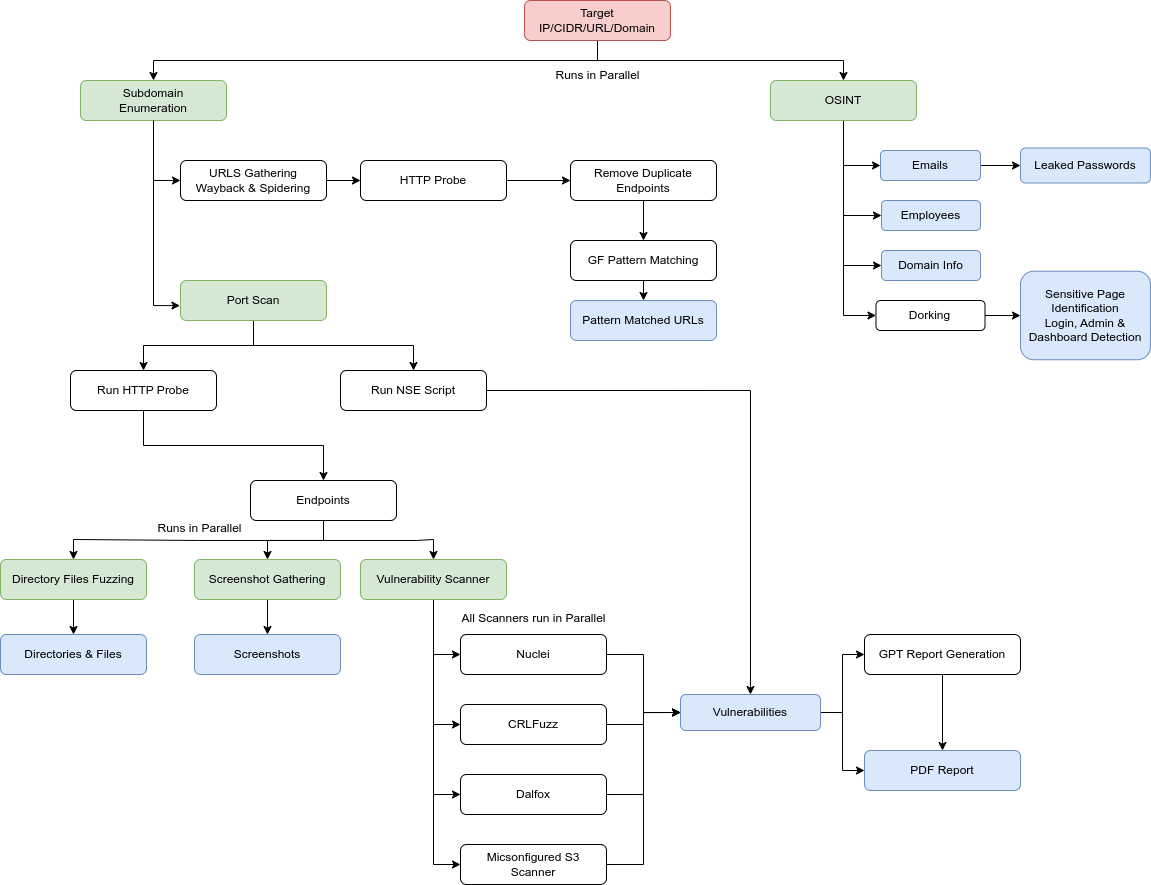 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 xaitax/sploitscan
Aggregates CVE details, exploit databases, and EPSS scores with AI risk assessment and vulnerability scanner import for prioritized patching.
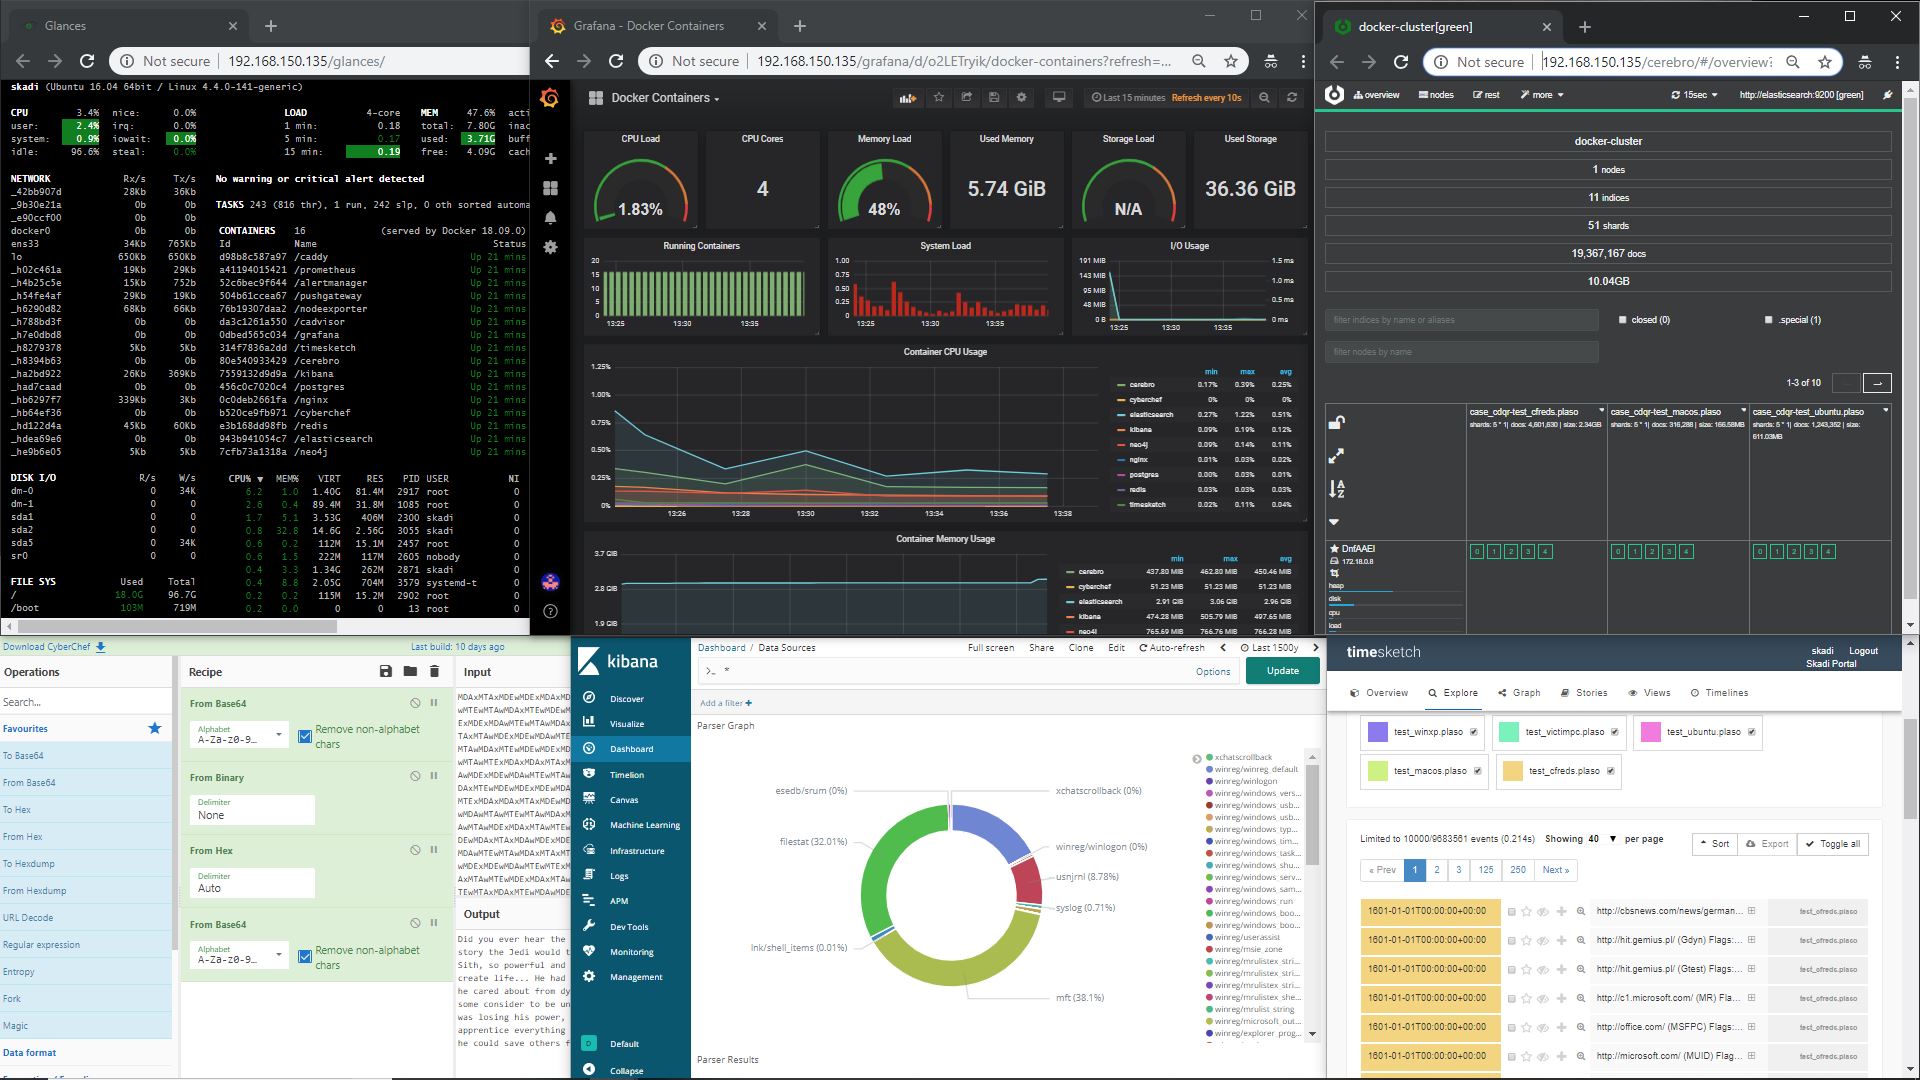 orlikoski/skadi
Collect, Process, and Hunt with host based data from MacOS, Windows, and Linux
 chiasmod0n/chiasmodon
Chiasmodon is an OSINT tool designed to assist in the process of gathering information about a target domain. Its primary functionality revolves…
 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
 ebwi11/agentsmith-hids
By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.
 scoubi/bloodsocer
Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…
 ranguli/ioccheck
A tool for simplifying the process of researching IOCs.
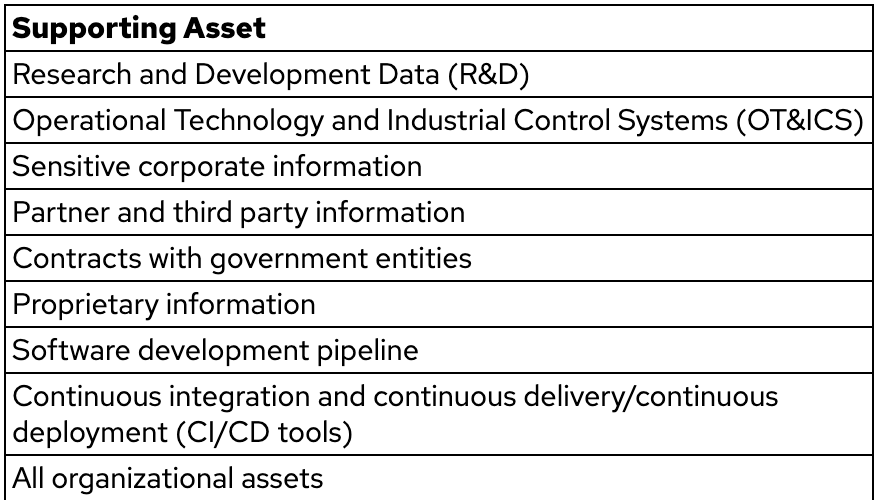 redhat-infosec/priority-intelligence-requirements-dev
This guide describes a process for developing Cyber Threat Intelligence Priority Intelligence Requirements
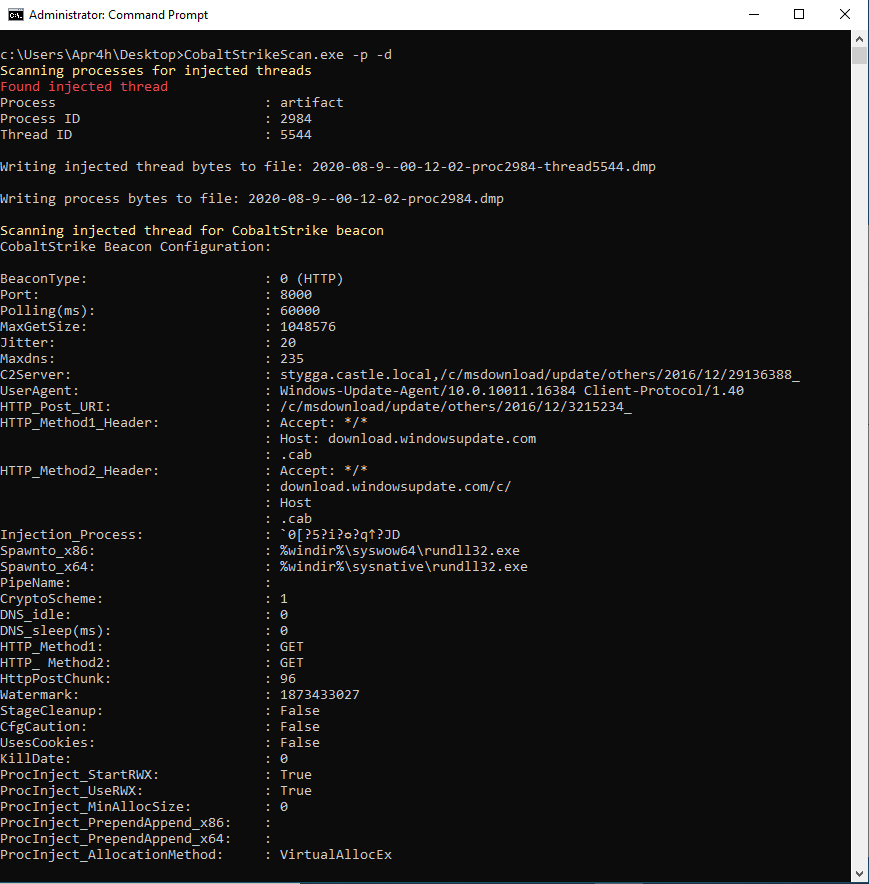 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 ernestak/sigma-rule-for-cve-2022-30190
Sigma rule for detecting exploitation of CVE-2022-30190 (Follina) via Windows process creation events, enabling SOC teams to identify malicious…
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.