Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…

Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…

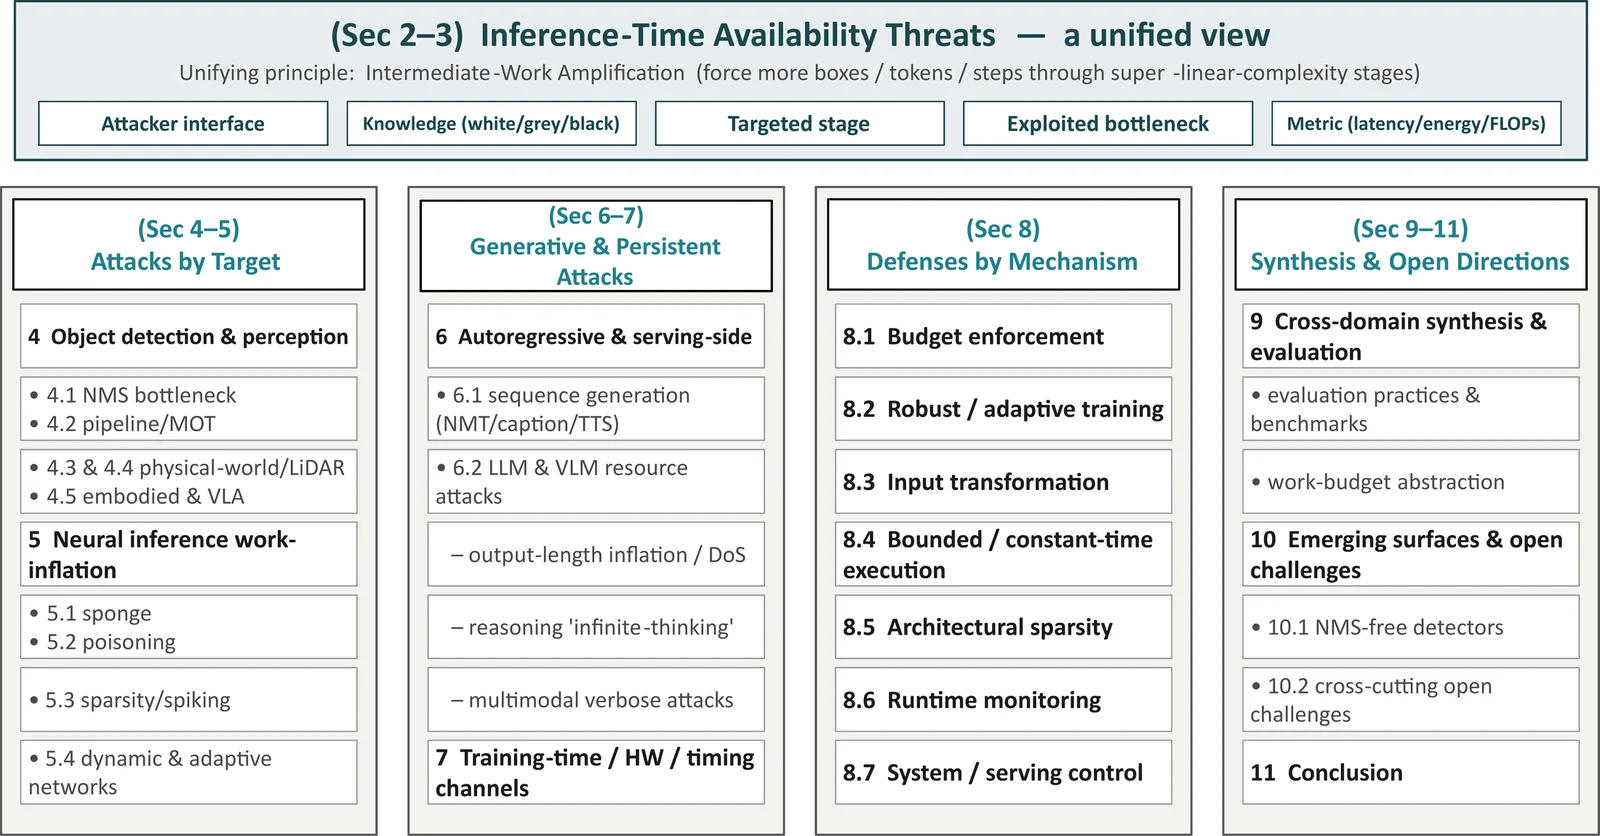
Curated index of deep learning latency, energy-latency & timing (availability) attacks and defenses — companion to the ACM Computing Surveys…

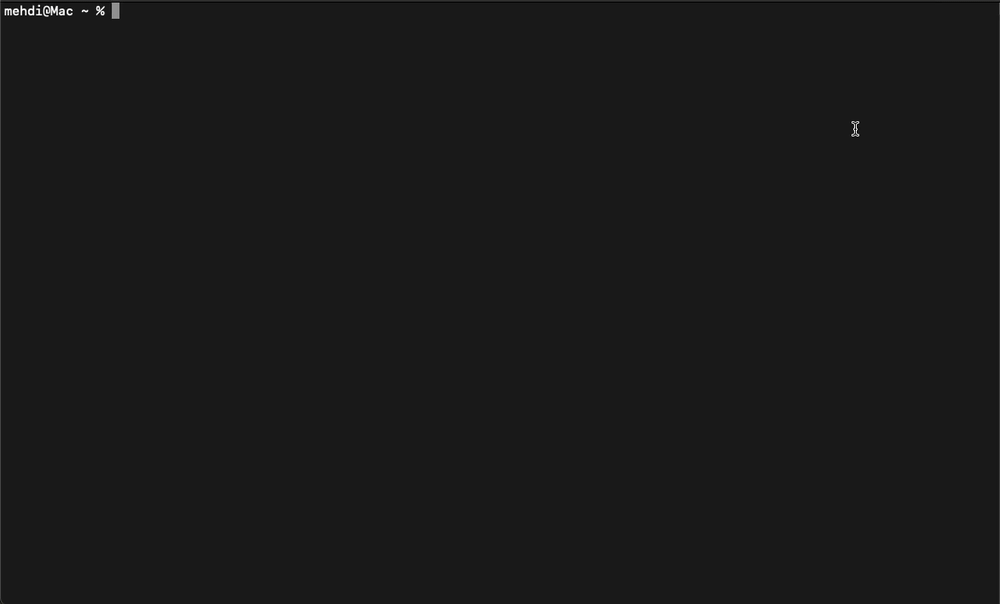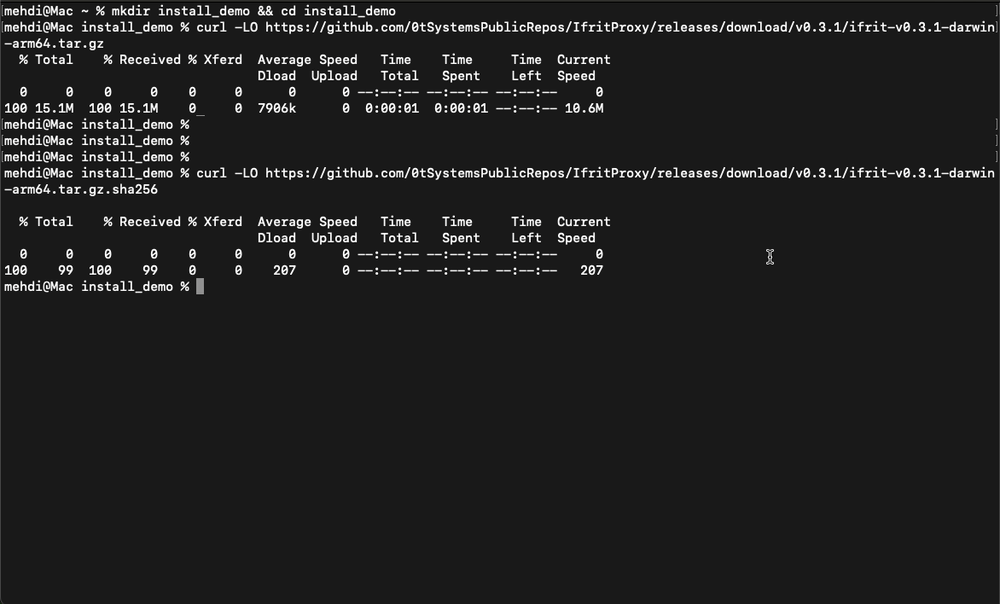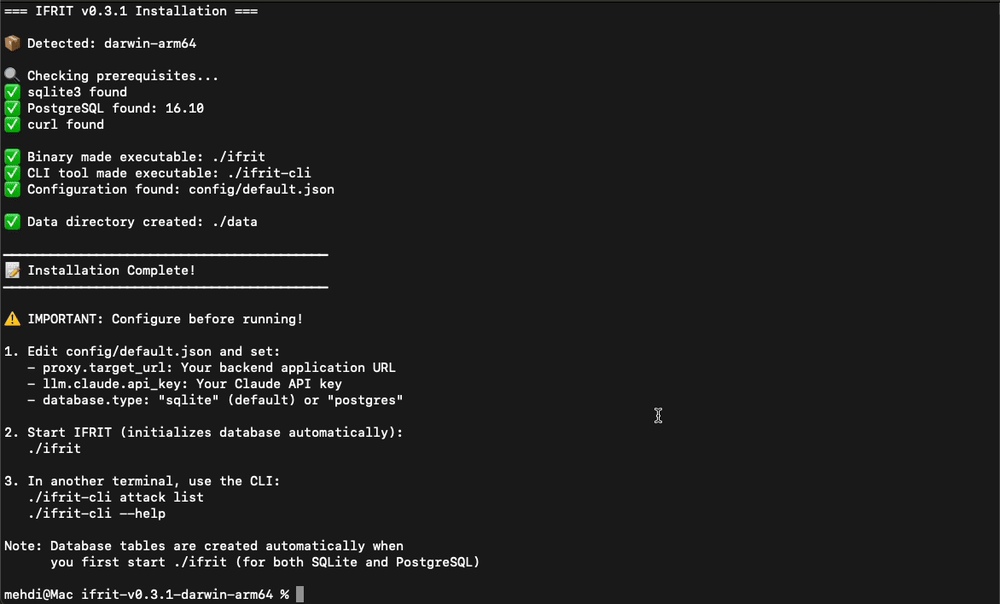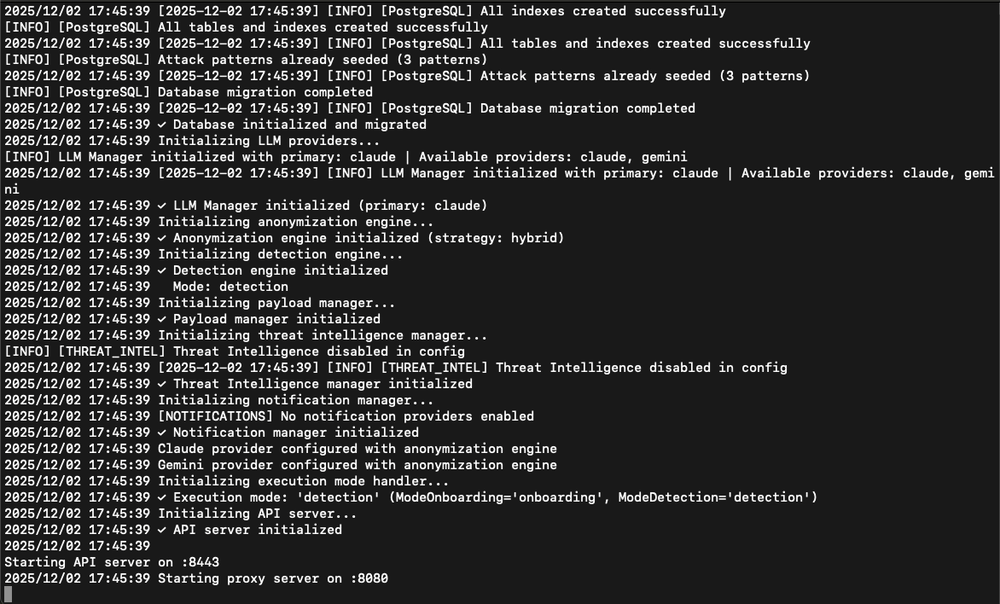
IFRIT is an AI-powered reverse proxy that intercepts incoming requests in real time, classifying each one as legitimate or malicious. Legitimate…

AI / LLM Red Team Field Manual & Consultant’s Handbook

:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud

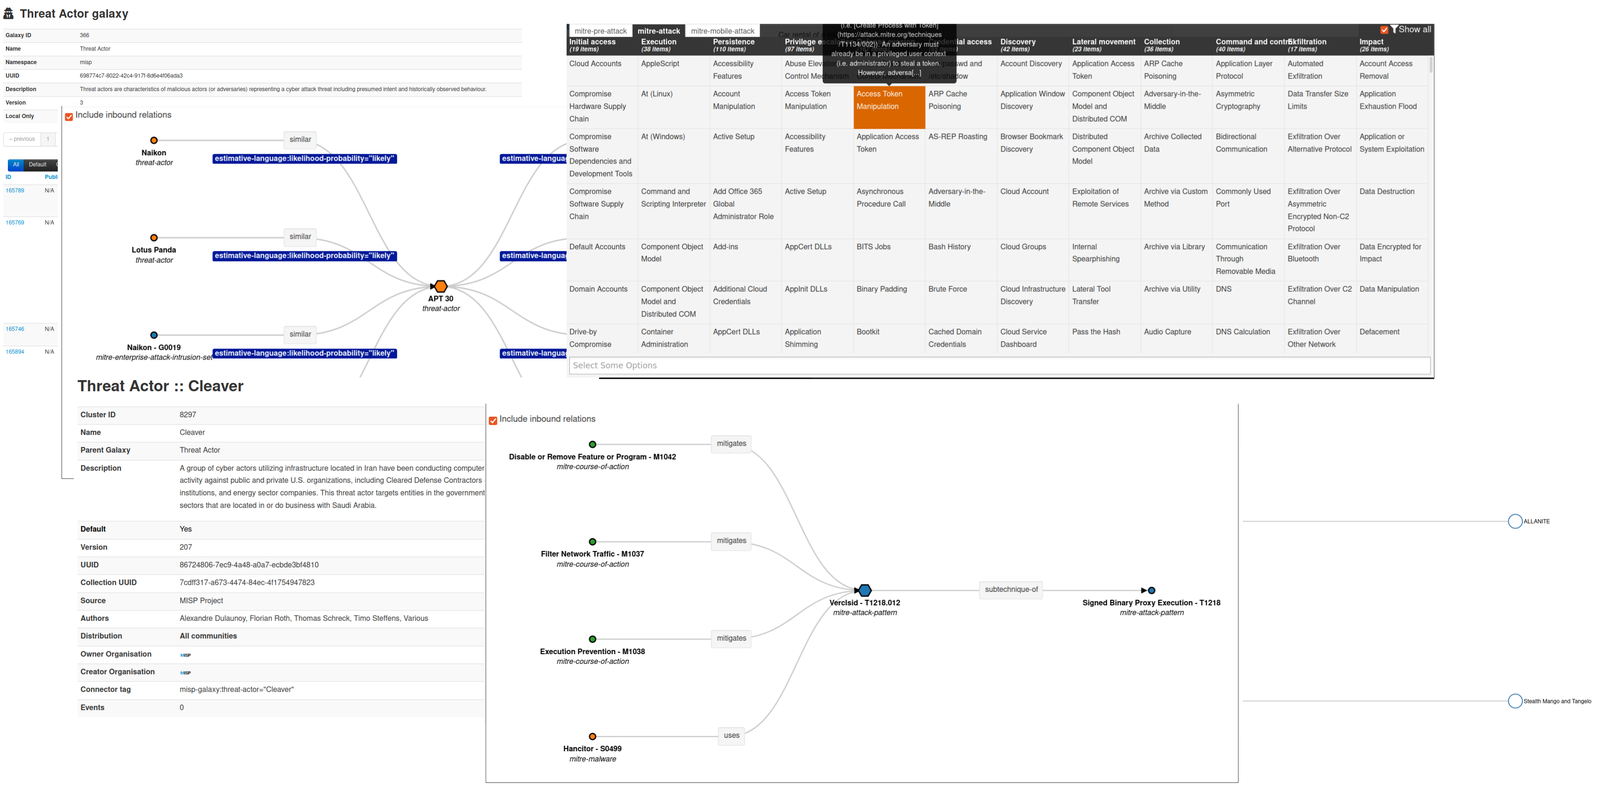
Clusters and elements to attach to MISP events or attributes (like threat actors)

Purple Team Exercise Framework

Proof-of-concept and technical analysis of CVE-2025-0411, a 7-Zip Mark-of-the-Web bypass vulnerability exploited in SmokeLoader campaigns, with…

Data from a BRAWL Automated Adversary Emulation Exercise

Improve your security and privacy by blocking ads, tracking and malware domains.

Open-source AI security platform providing perimeter defense for LLMs and AI agents through swarm analysis, policy enforcement, adversarial testing,…

Purpleteam scripts simulation & Detection - trigger events for SOC detections