

EntraTrace
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
authenticationcloud-securitydefensive-tools+5
122
bert-janp/entratraceDefensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
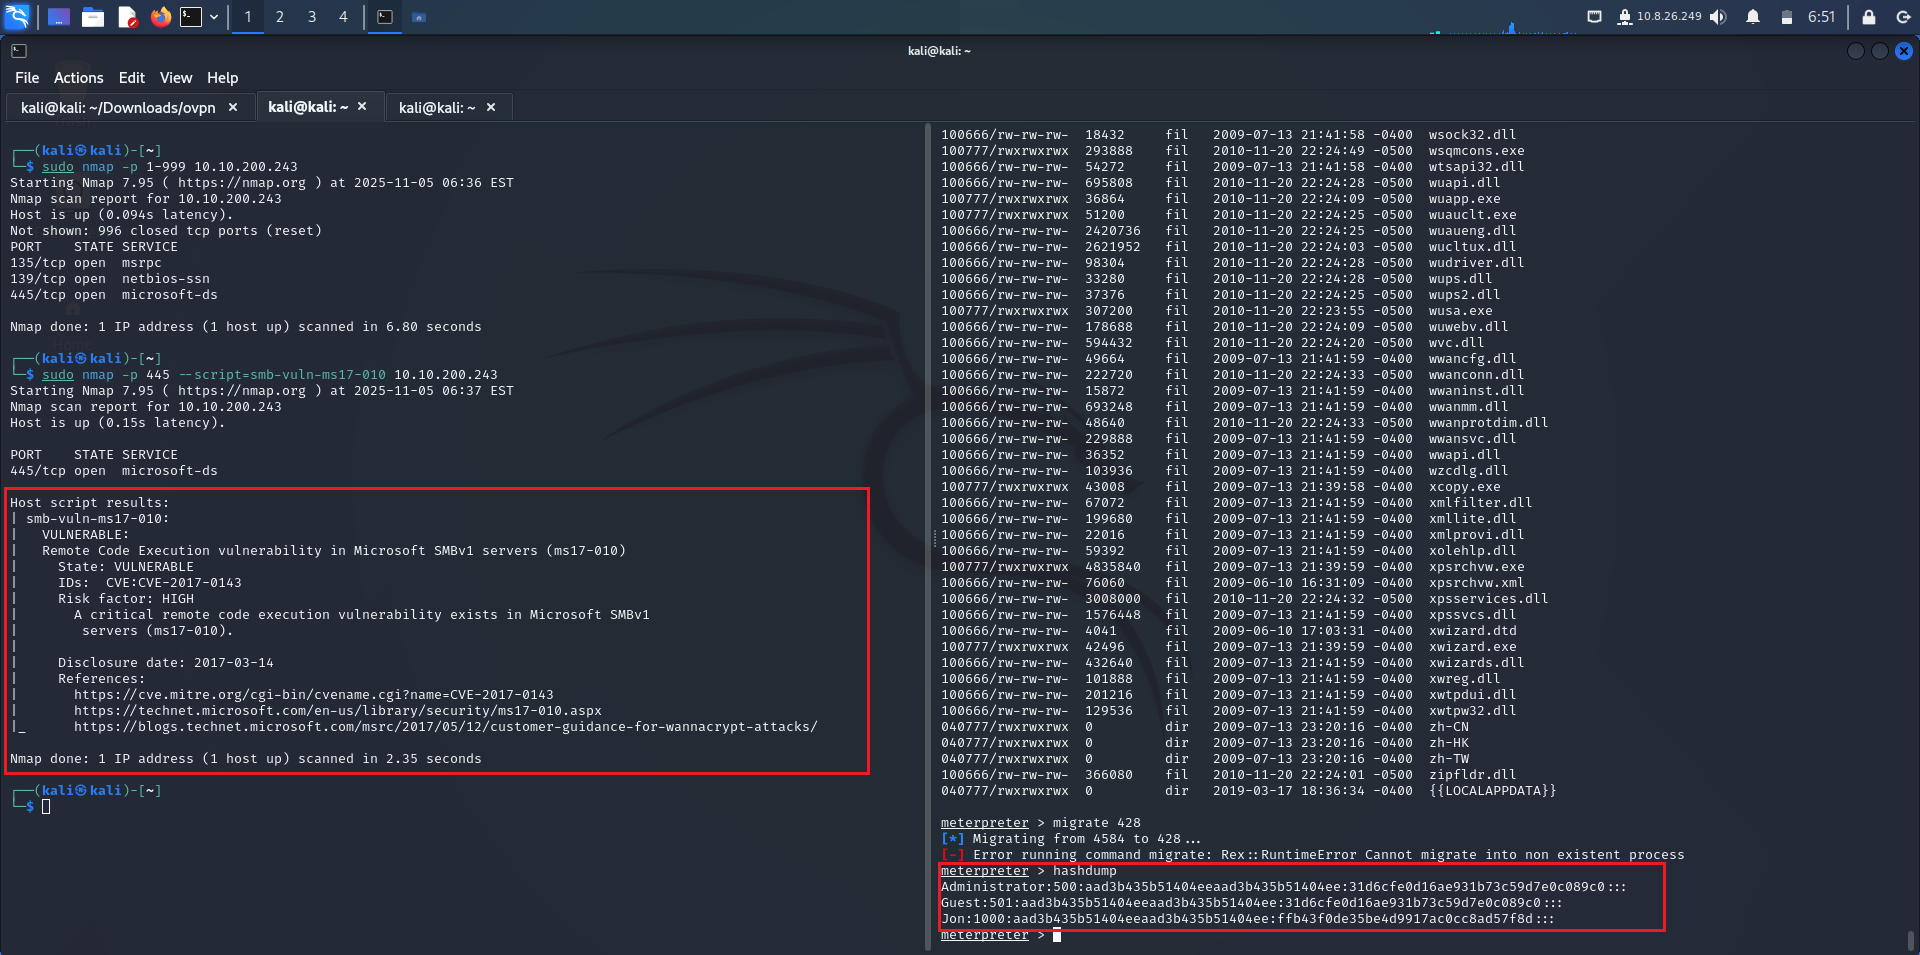 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 chpratik/cve-2026-50522
Deserialization of untrusted data in Microsoft Office SharePoint allows an unauthorized attacker to execute code over a network.
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
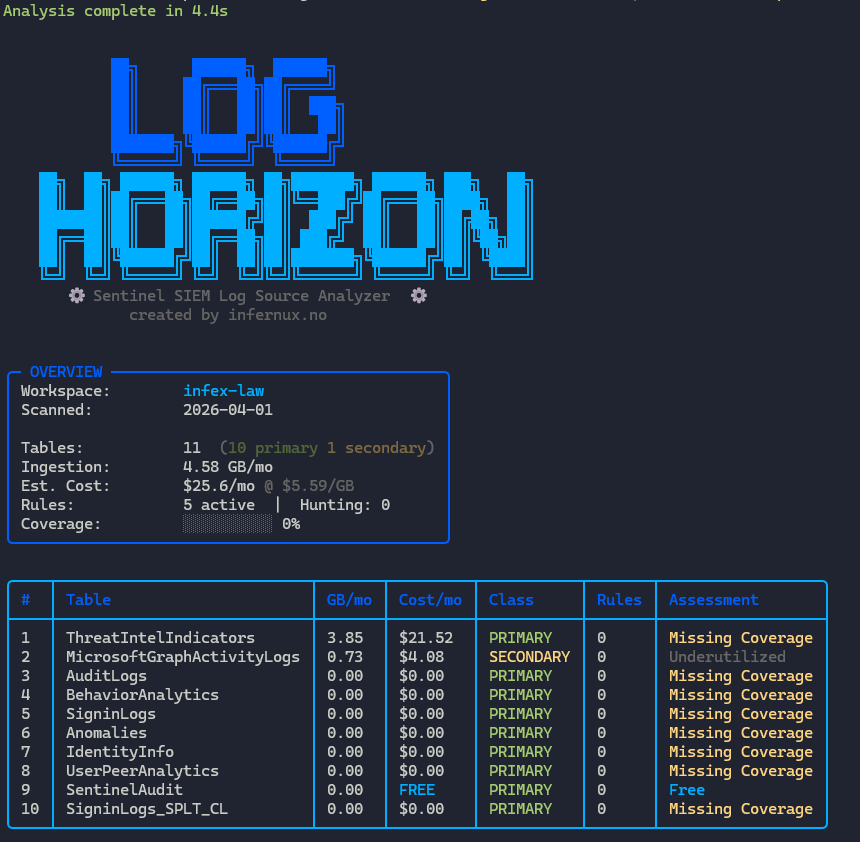 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
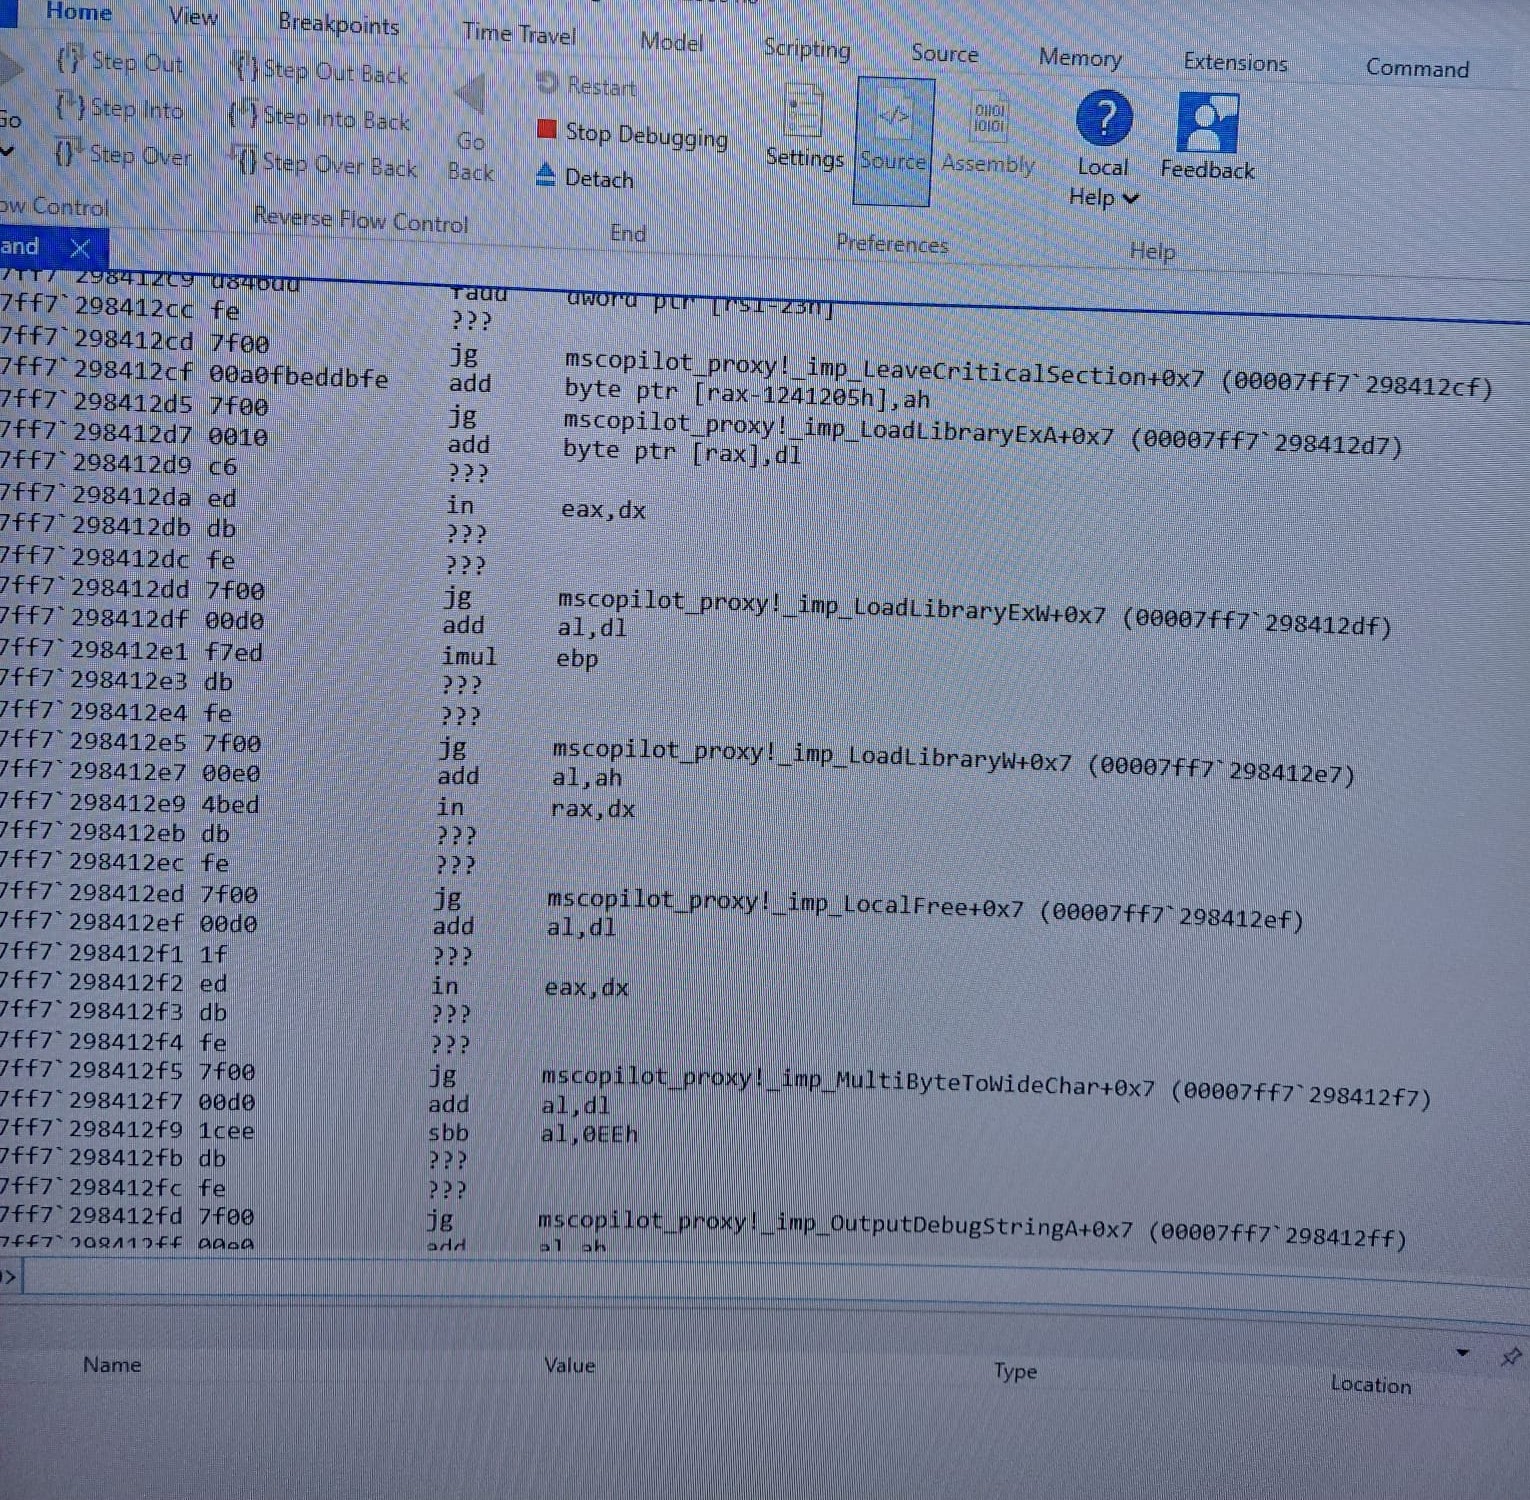 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 tadash10/detailed-analysis-and-mitigation-strategies-for-cve-2024-38124-and-cve-2024-43468
In-depth analysis and mitigation strategies for CVE-2024-38124 (Windows Netlogon) and CVE-2024-43468 (Microsoft Configuration Manager), including…
 cyprianatsyor/letsdefend-cve-2022-41082-exploitation-attempt
Detailed incident report and educational analysis of CVE-2022-41082 (ProxyNotShell) exploitation attempt on Microsoft Exchange Server, including…
 jangeisbauer/gundog
gundog - guided hunting in Microsoft Defender
 corelight/sigred
Zeek package for detecting CVE-2020-1350 (SIGRed) Windows DNS server exploit attempts via large DNS SIG/KEY response analysis with configurable…