
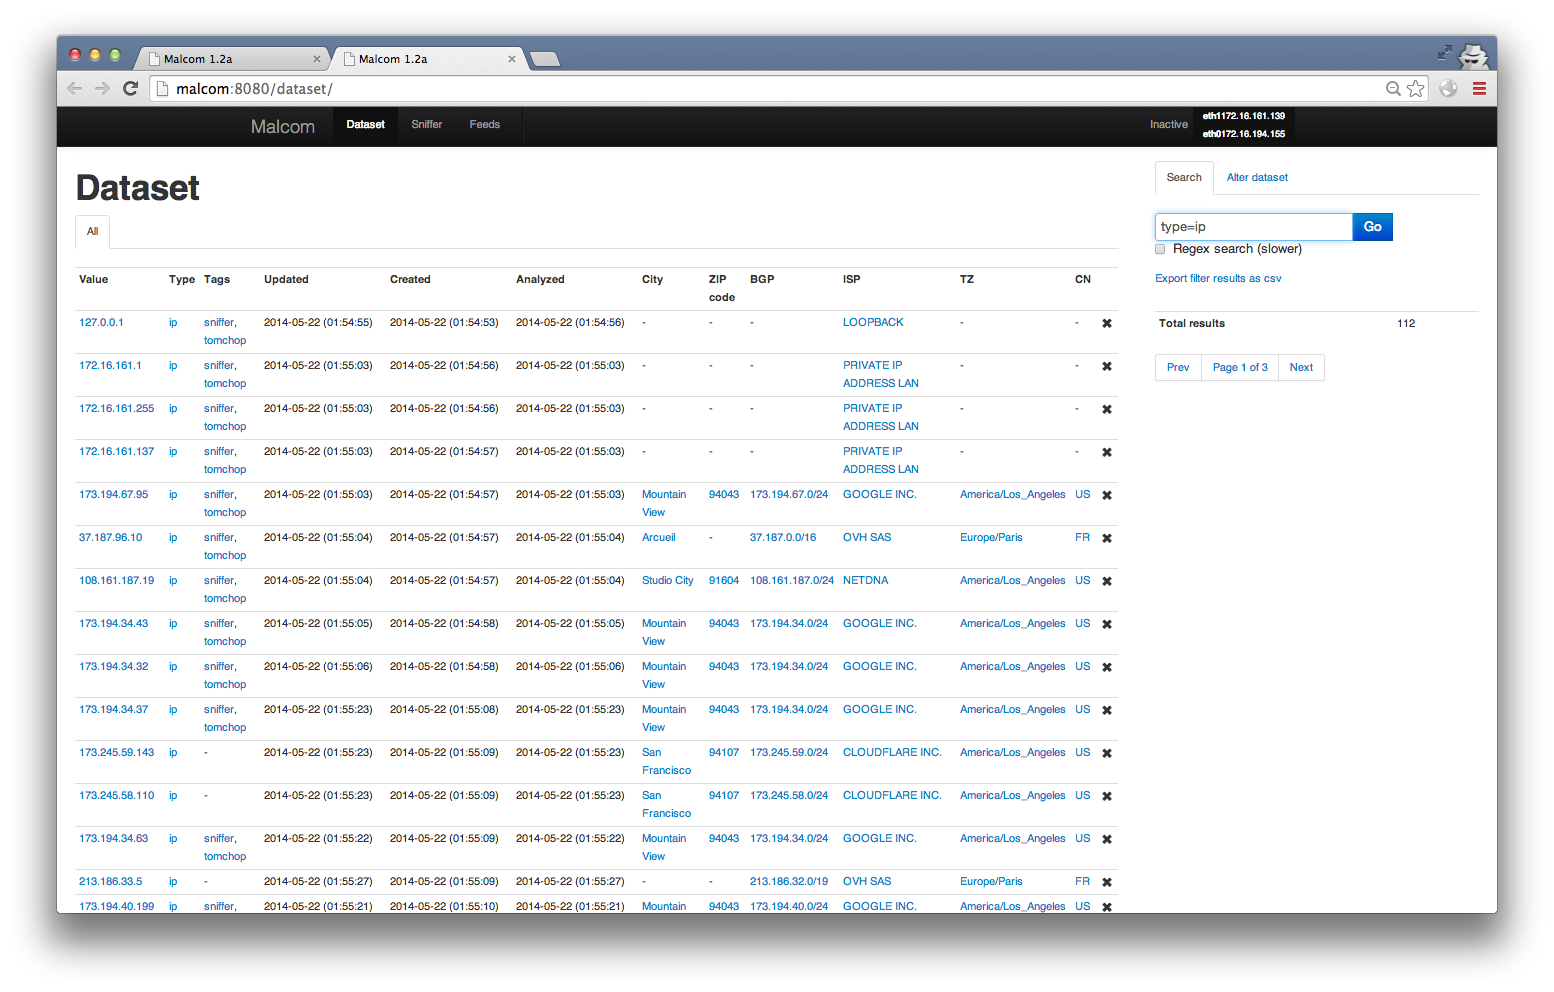
malcom
 tomchop/malcom
Malcom - Malware Communications Analyzer
malware-analysisnetwork-forensicsthreat-intelligence
tomchop/malcomMalcom - Malware Communications Analyzer
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
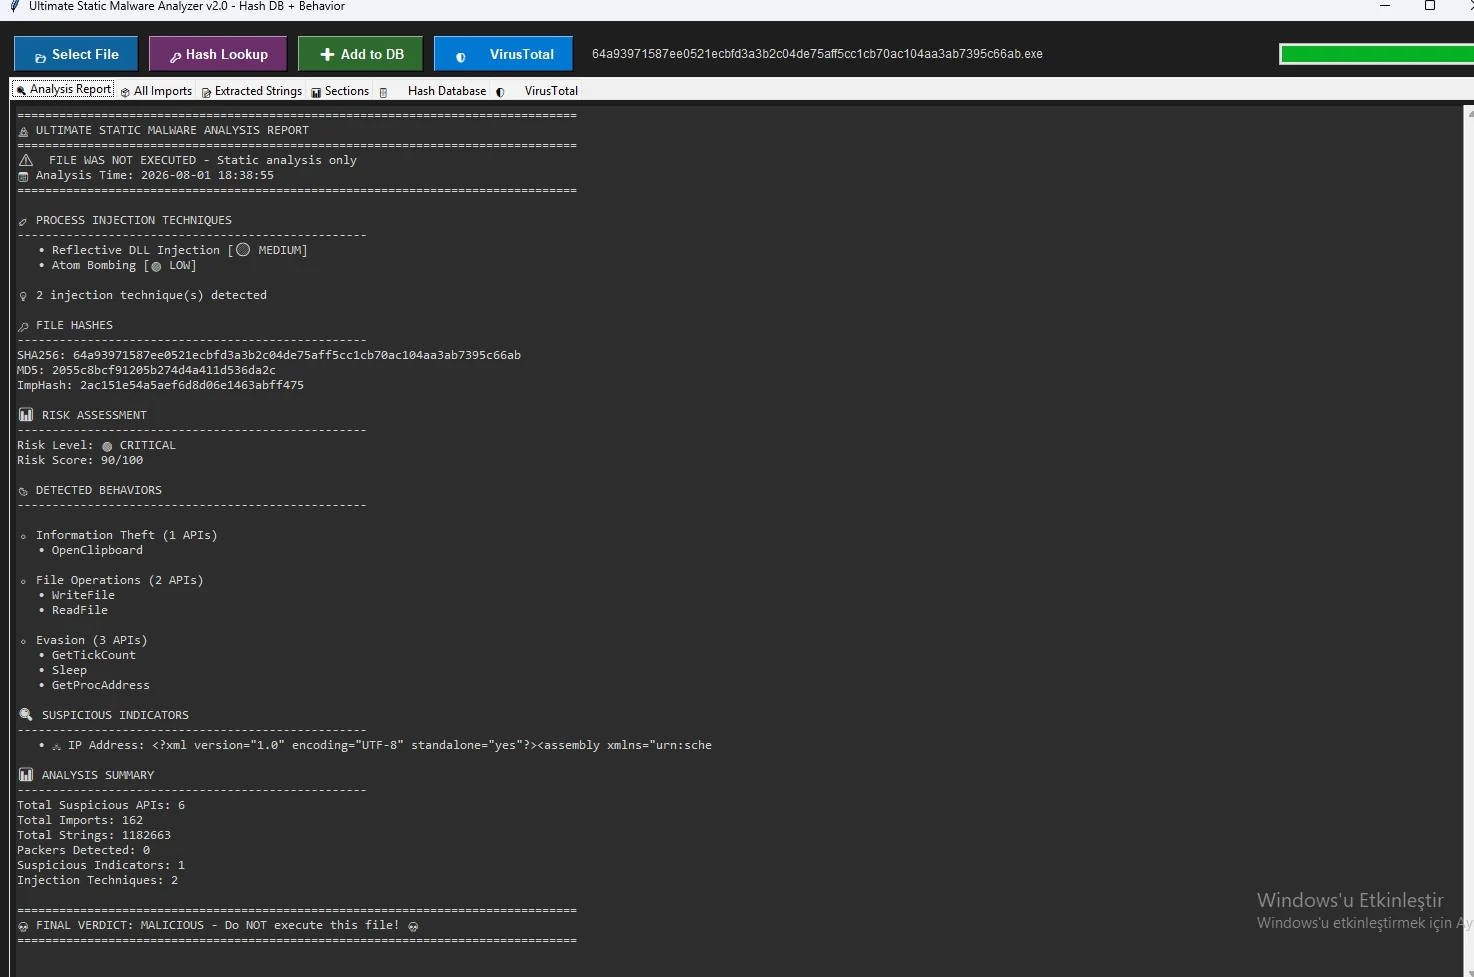 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 rjbhide/wireshark-forensics-plugin
Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…

 lethal-forensics/memprocfs-analyzer
Automates Windows memory forensics and DFIR workflows with MemProcFS: YARA/ClamAV scanning, process anomaly detection, and artifact/log extraction.
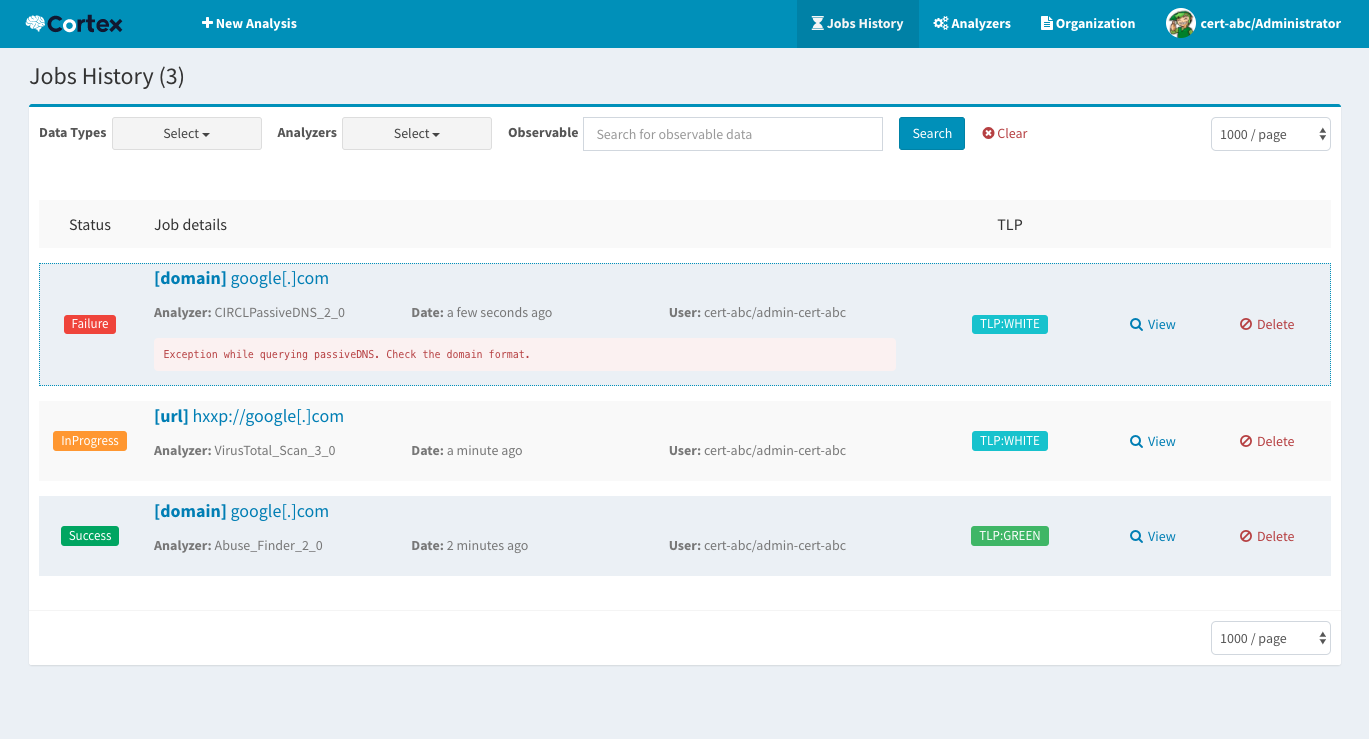 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 mhaggis/package-inferno
A Public Package Scanner for The Community