ciso-assistant-community

GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…

GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…

Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…

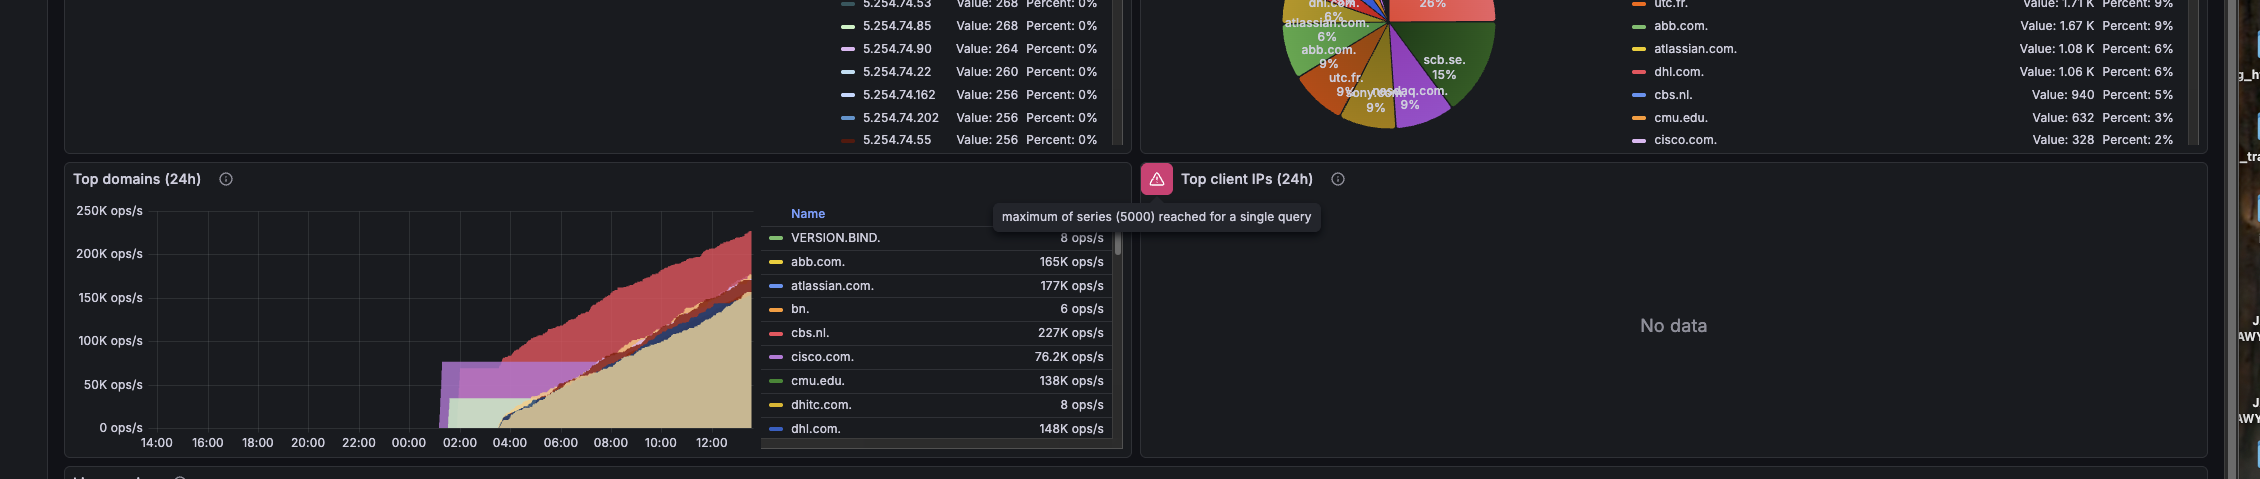
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…

Security sensor for realtime threat detection and protection

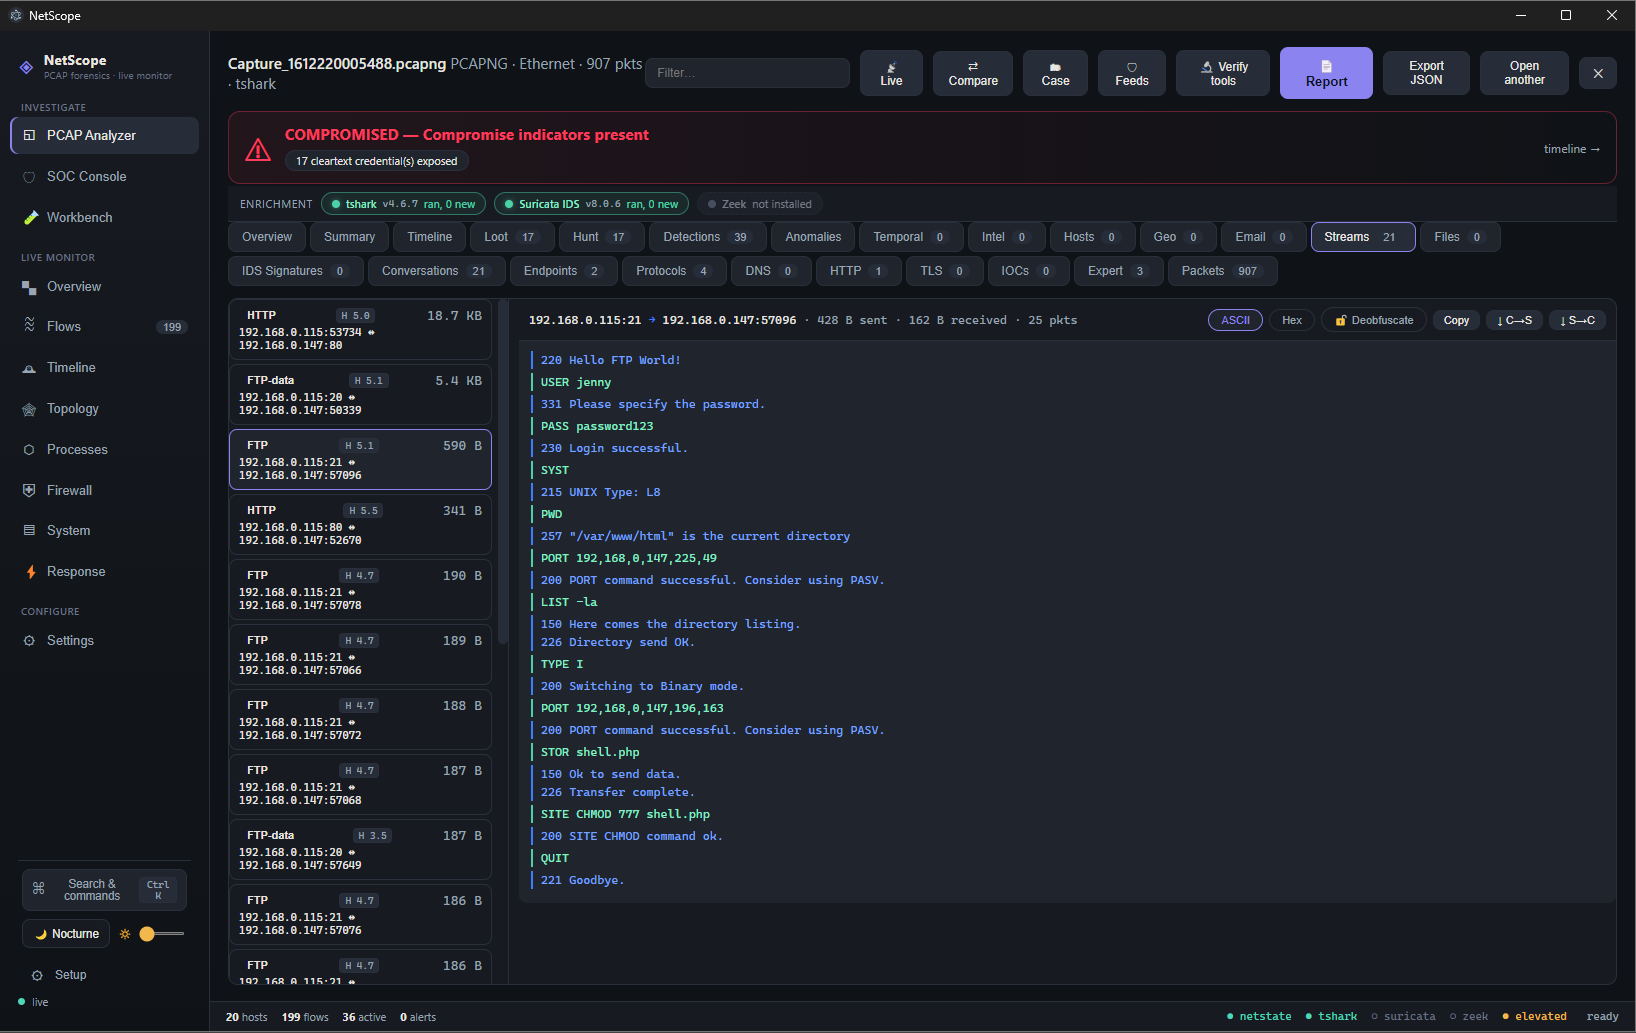
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…

ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.

Detect Tactics, Techniques & Combat Threats

Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation

Threat Pursuit Virtual Machine (VM): A fully customizable, open-sourced Windows-based distribution focused on threat intelligence analysis and…

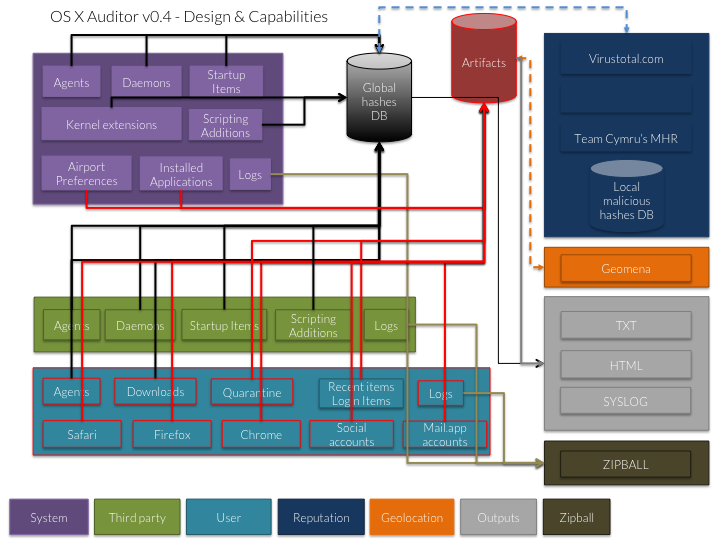
OS X Auditor is a free Mac OS X computer forensics tool

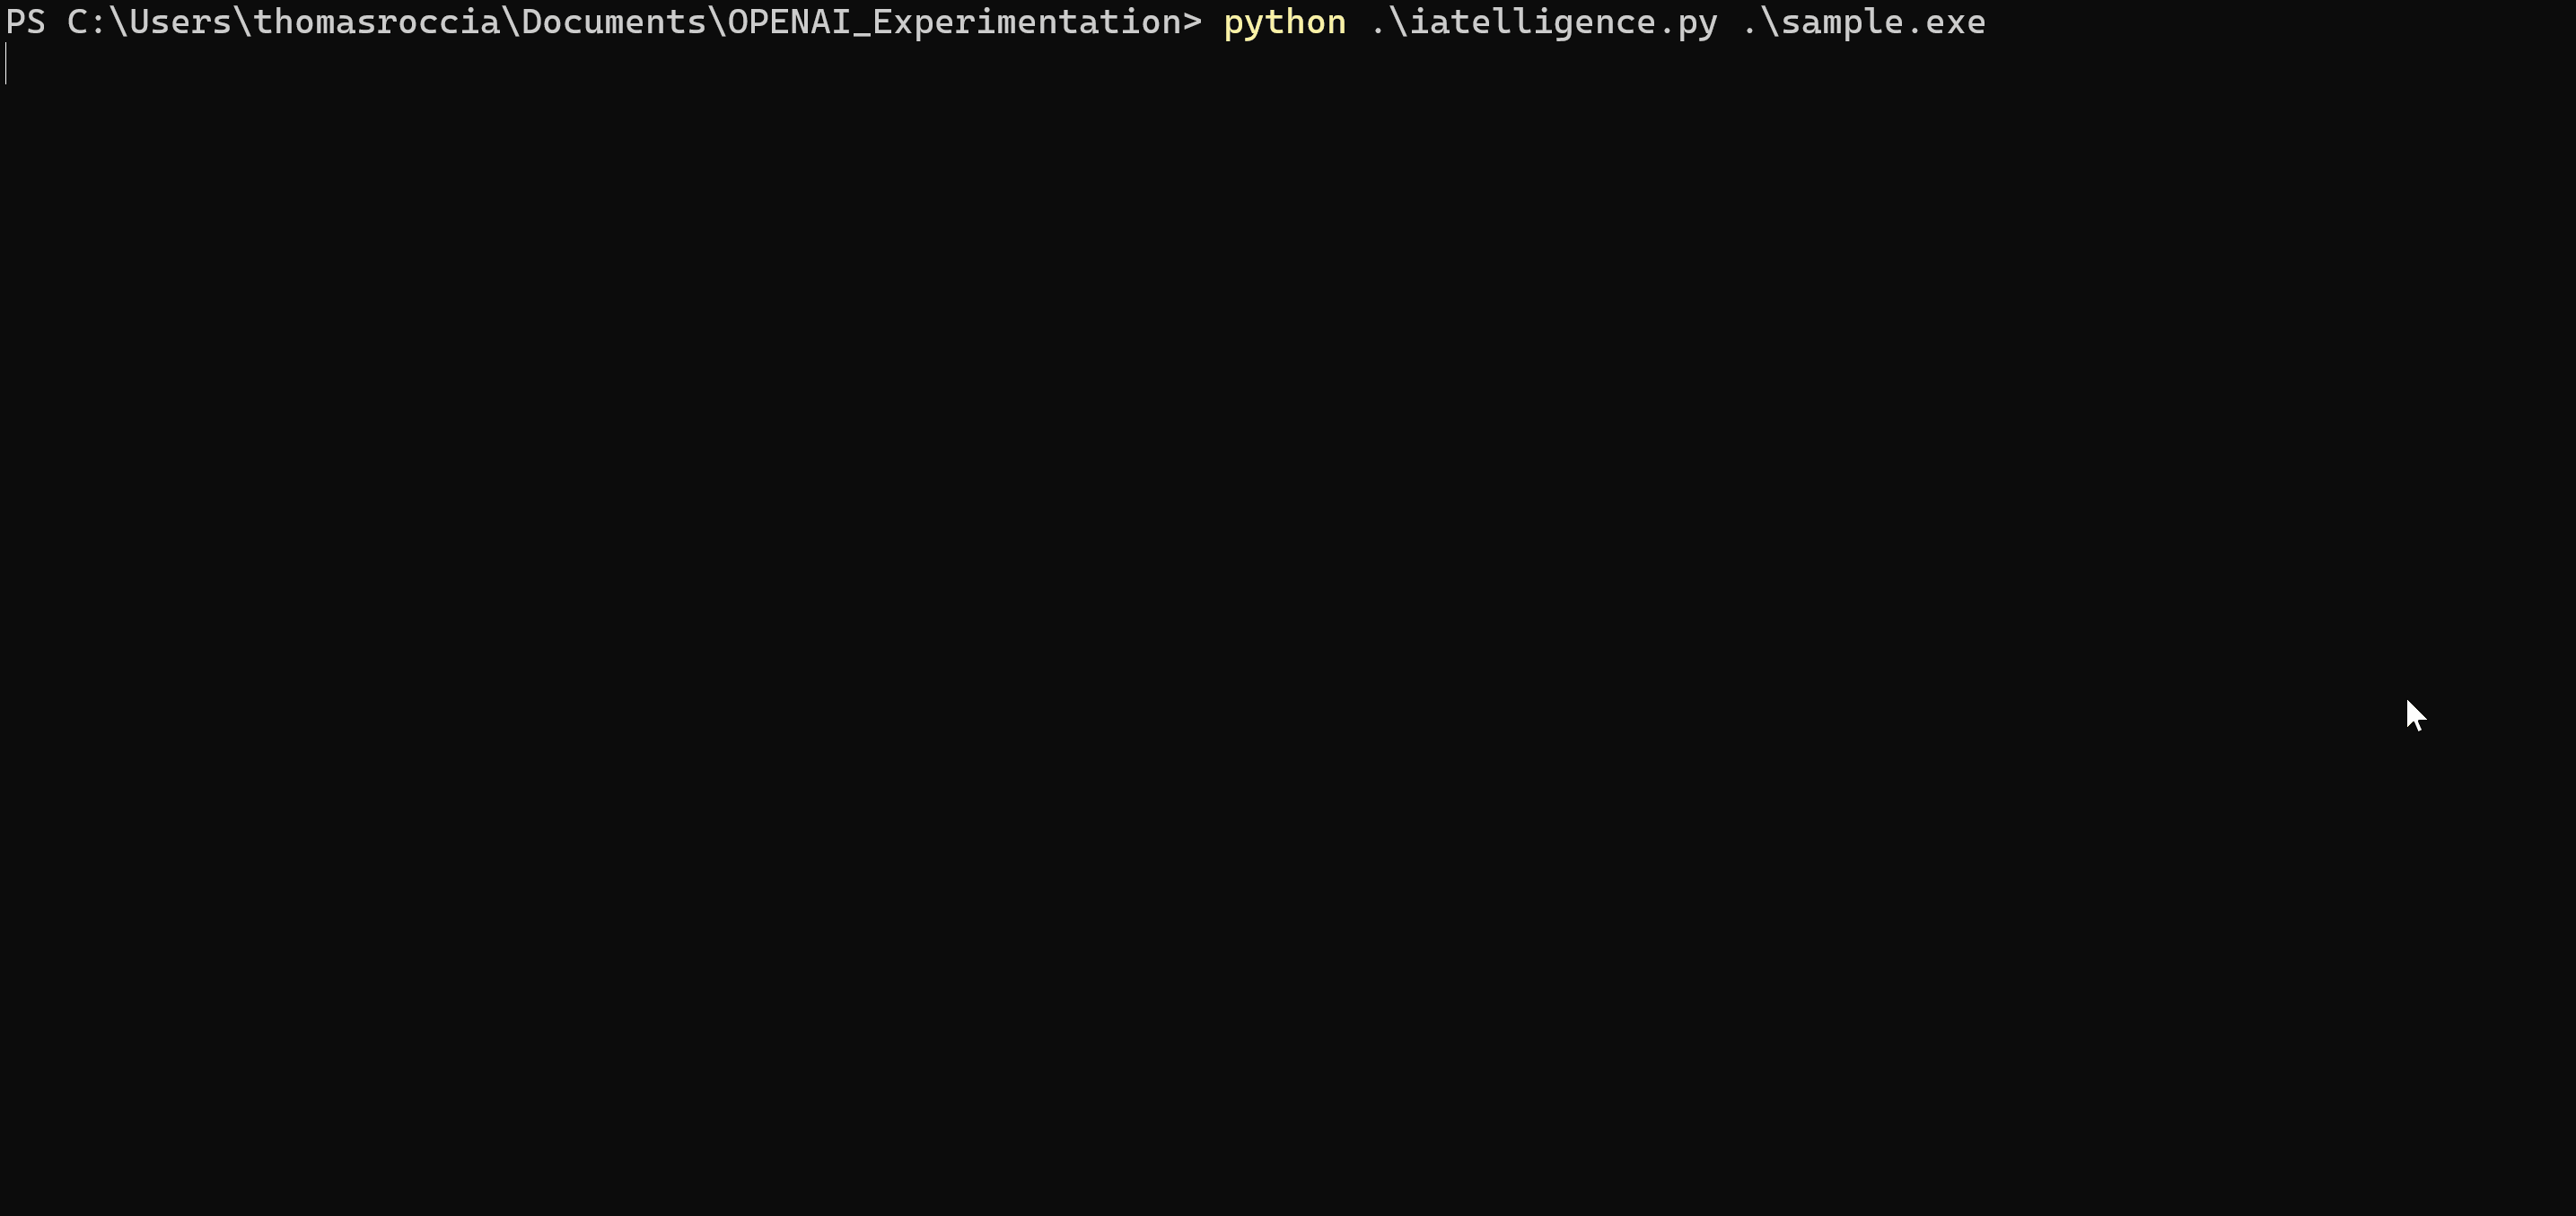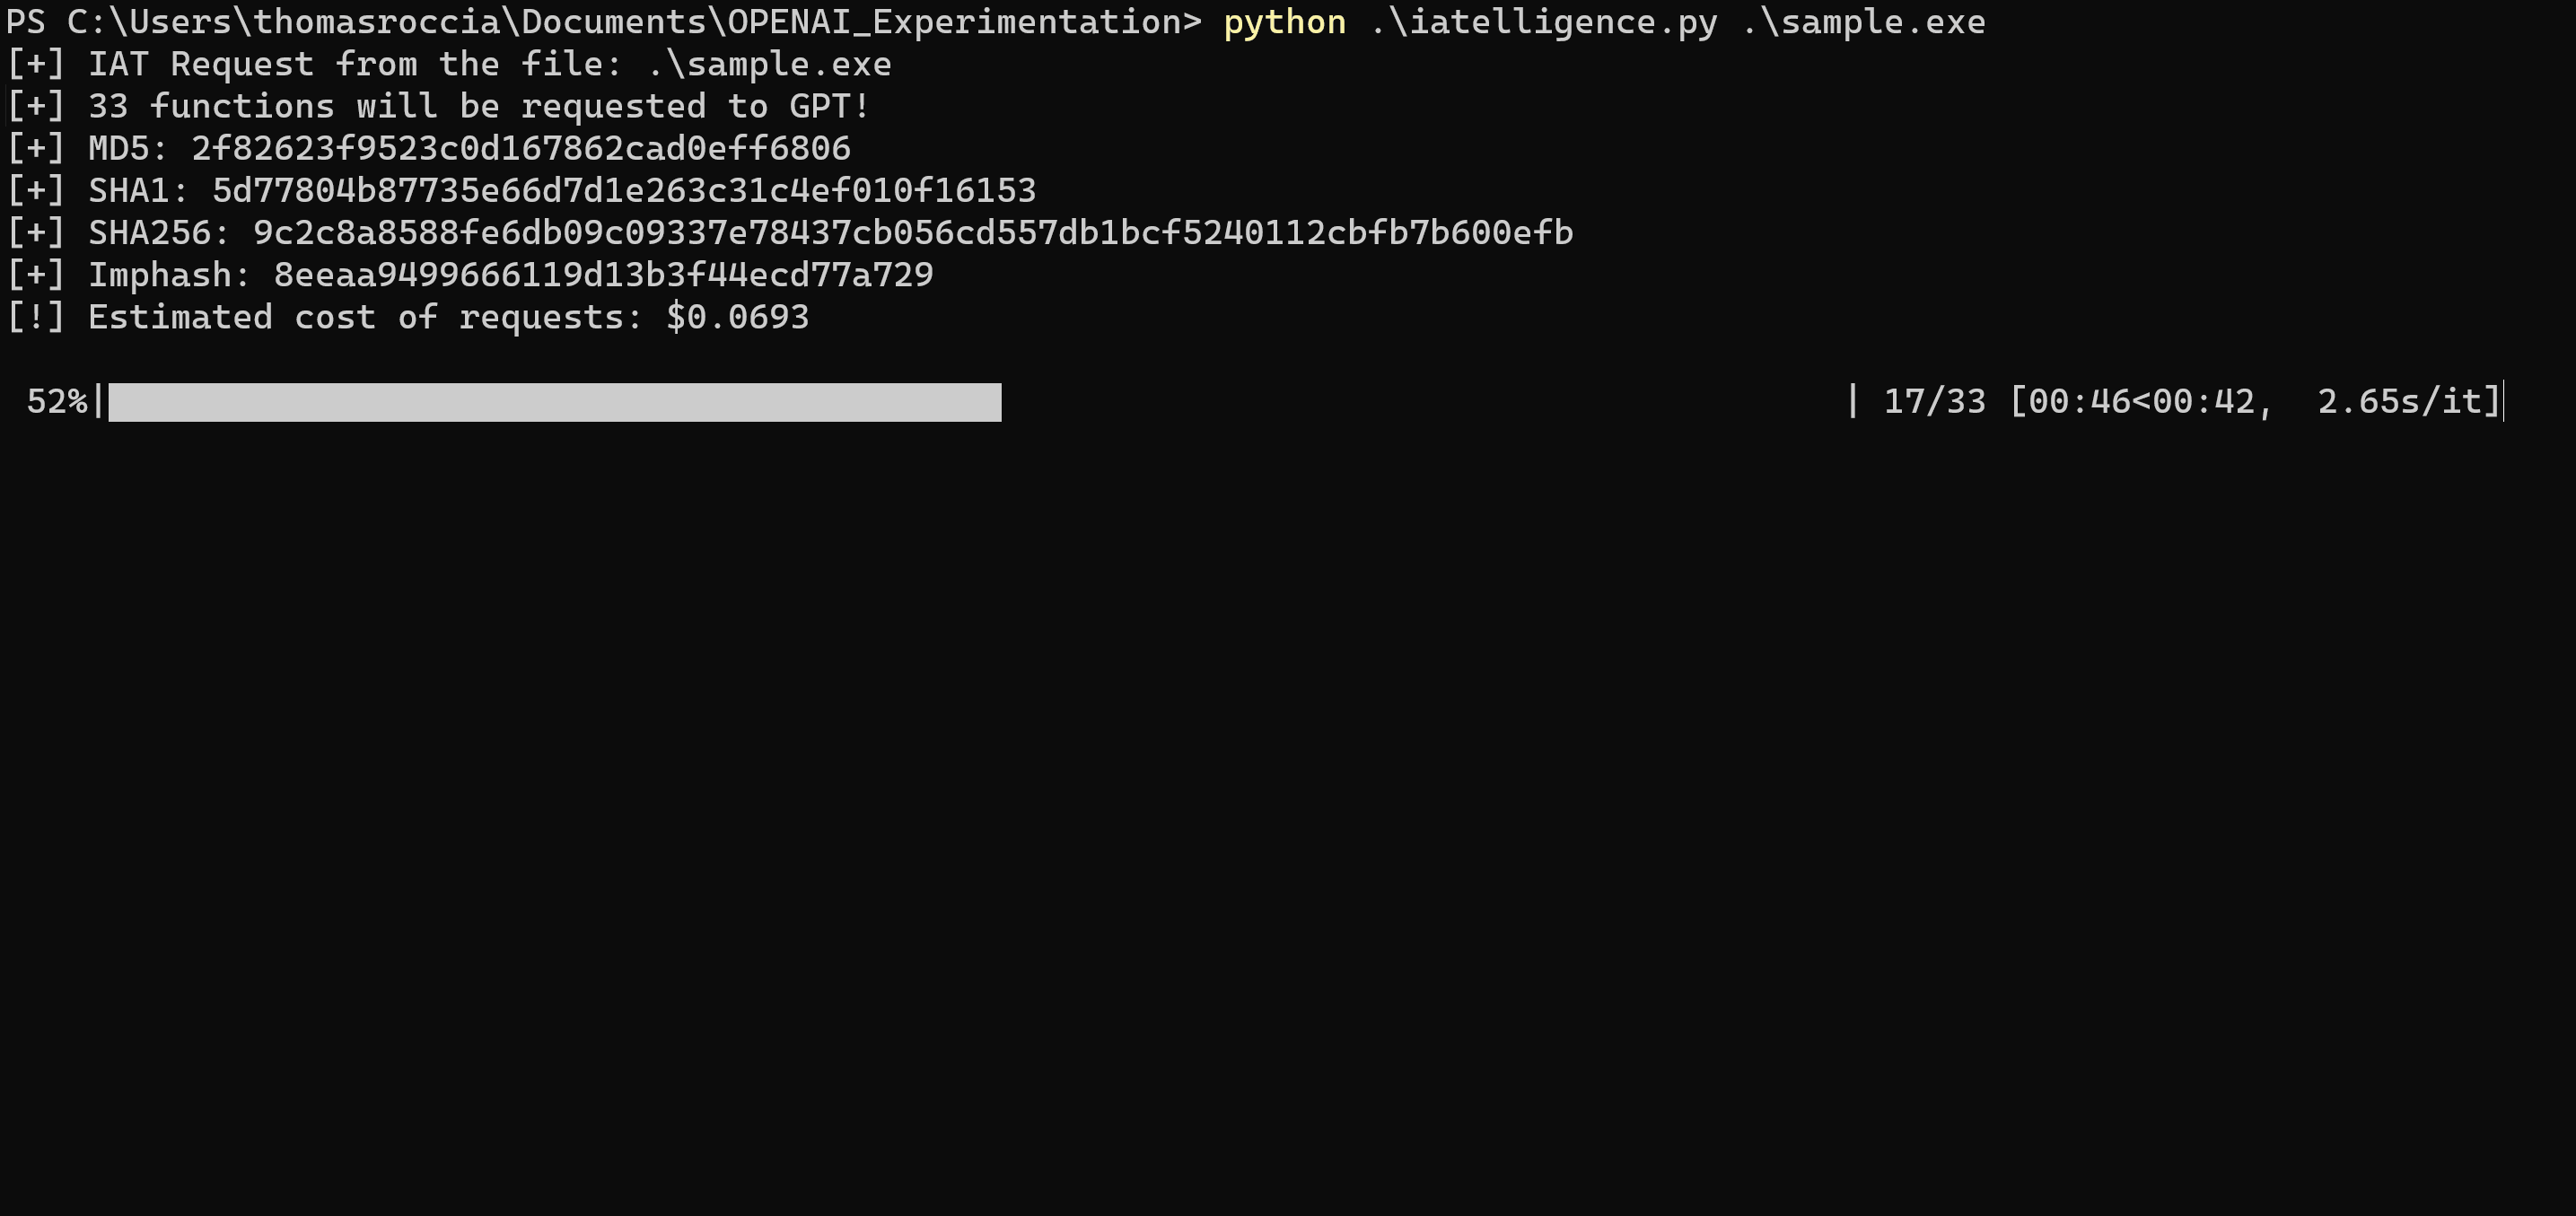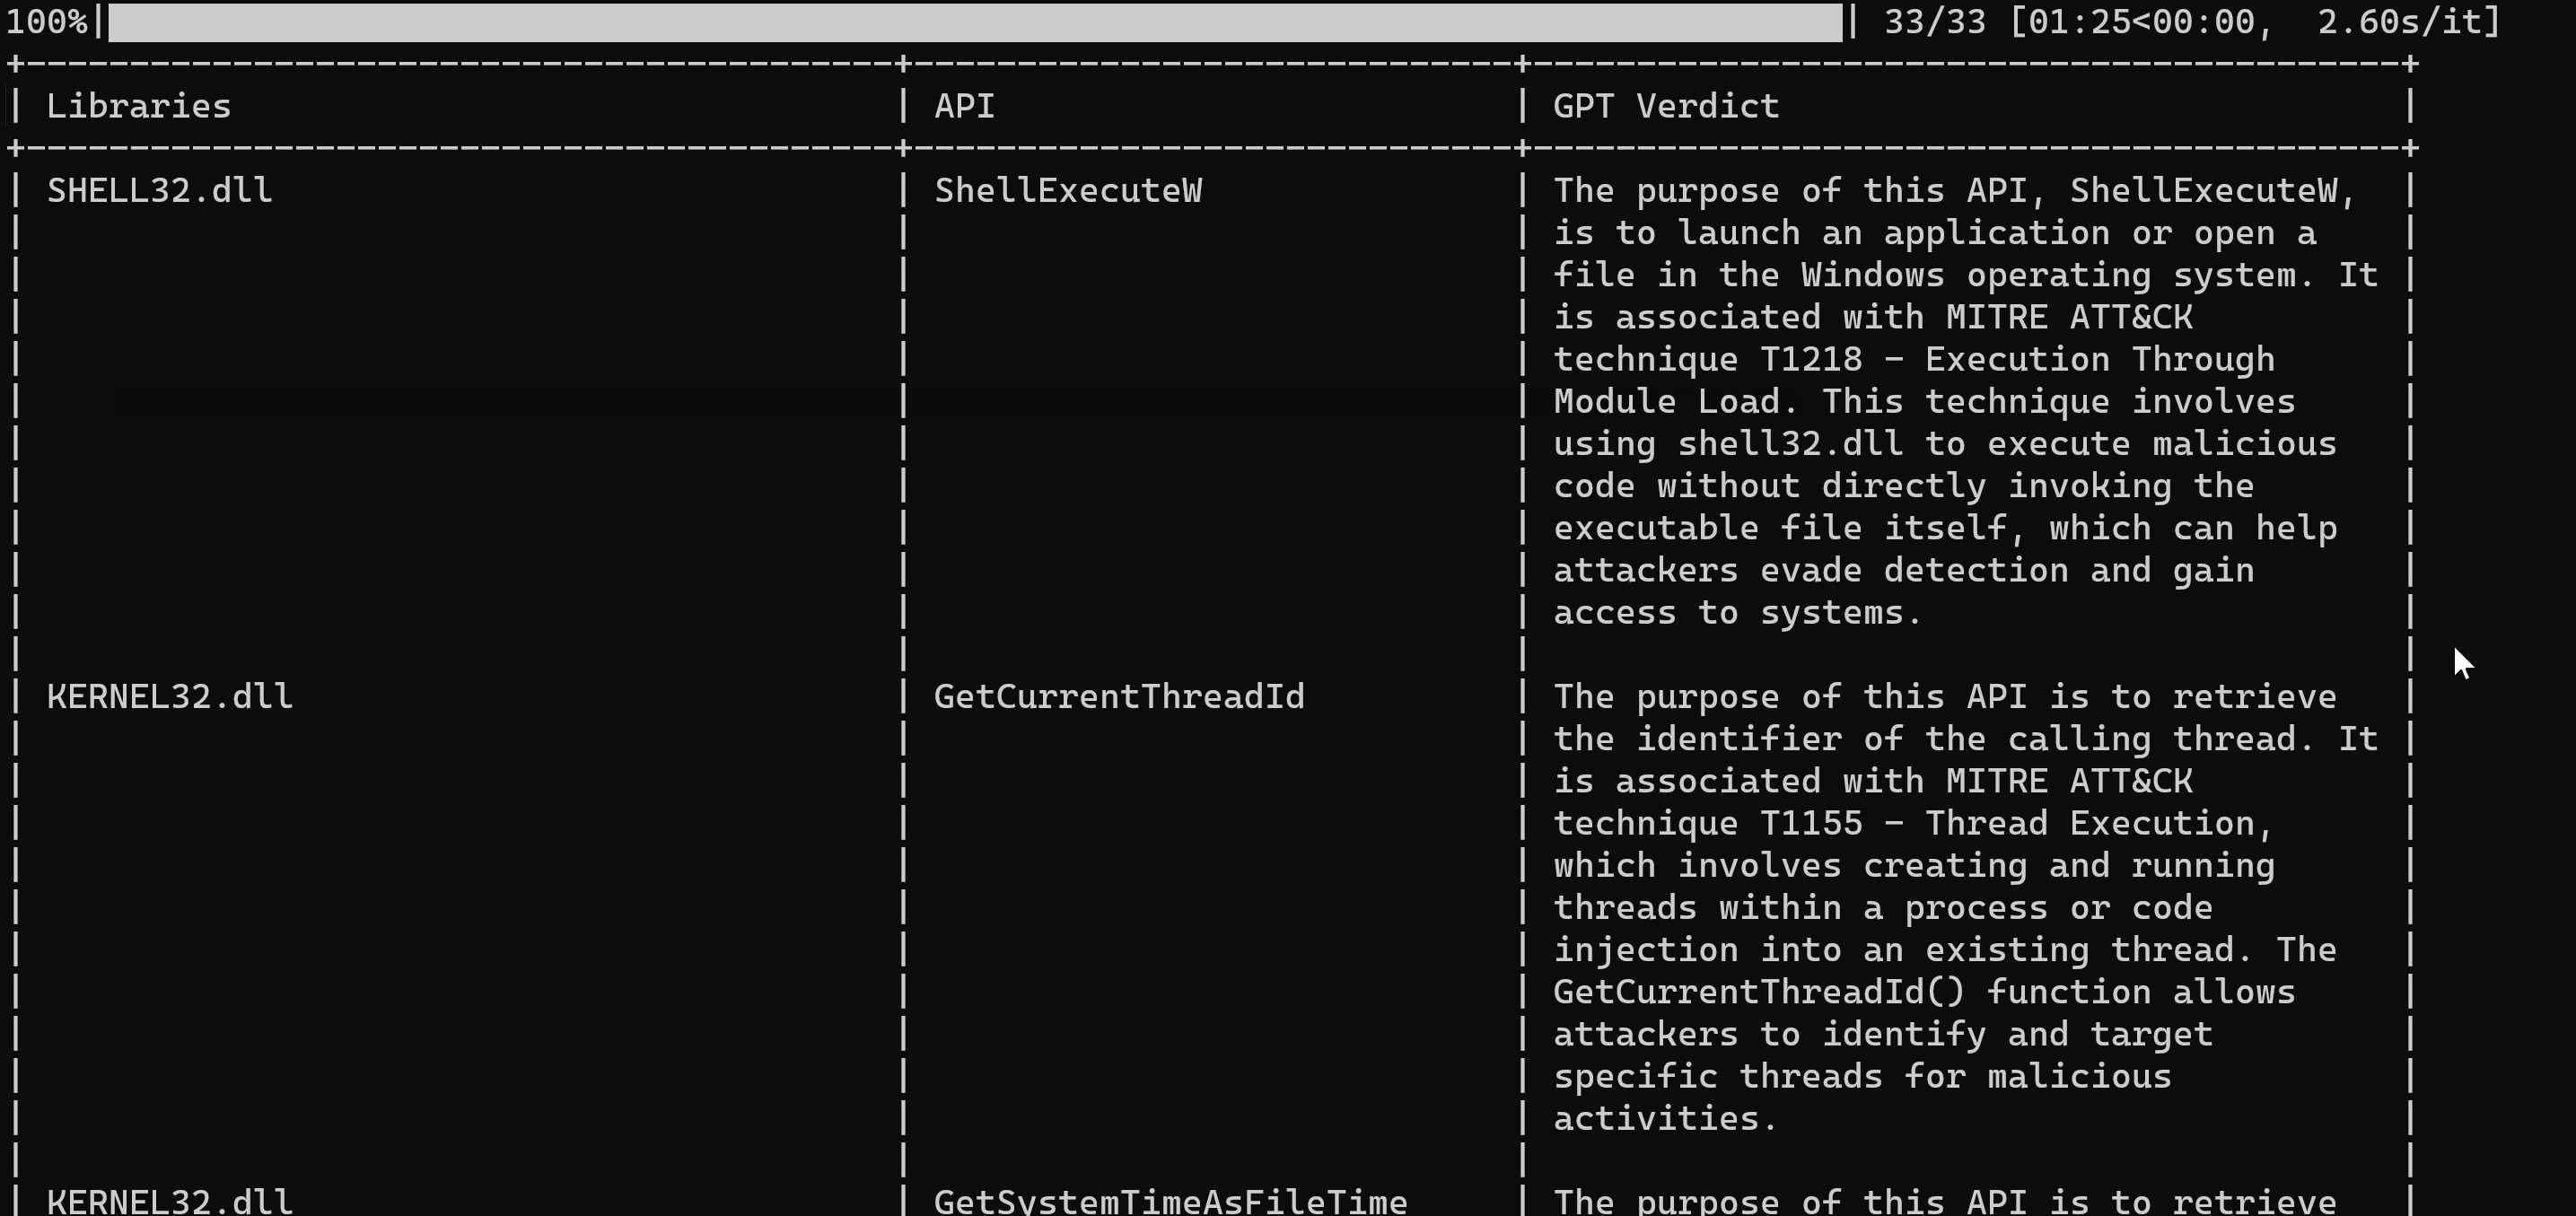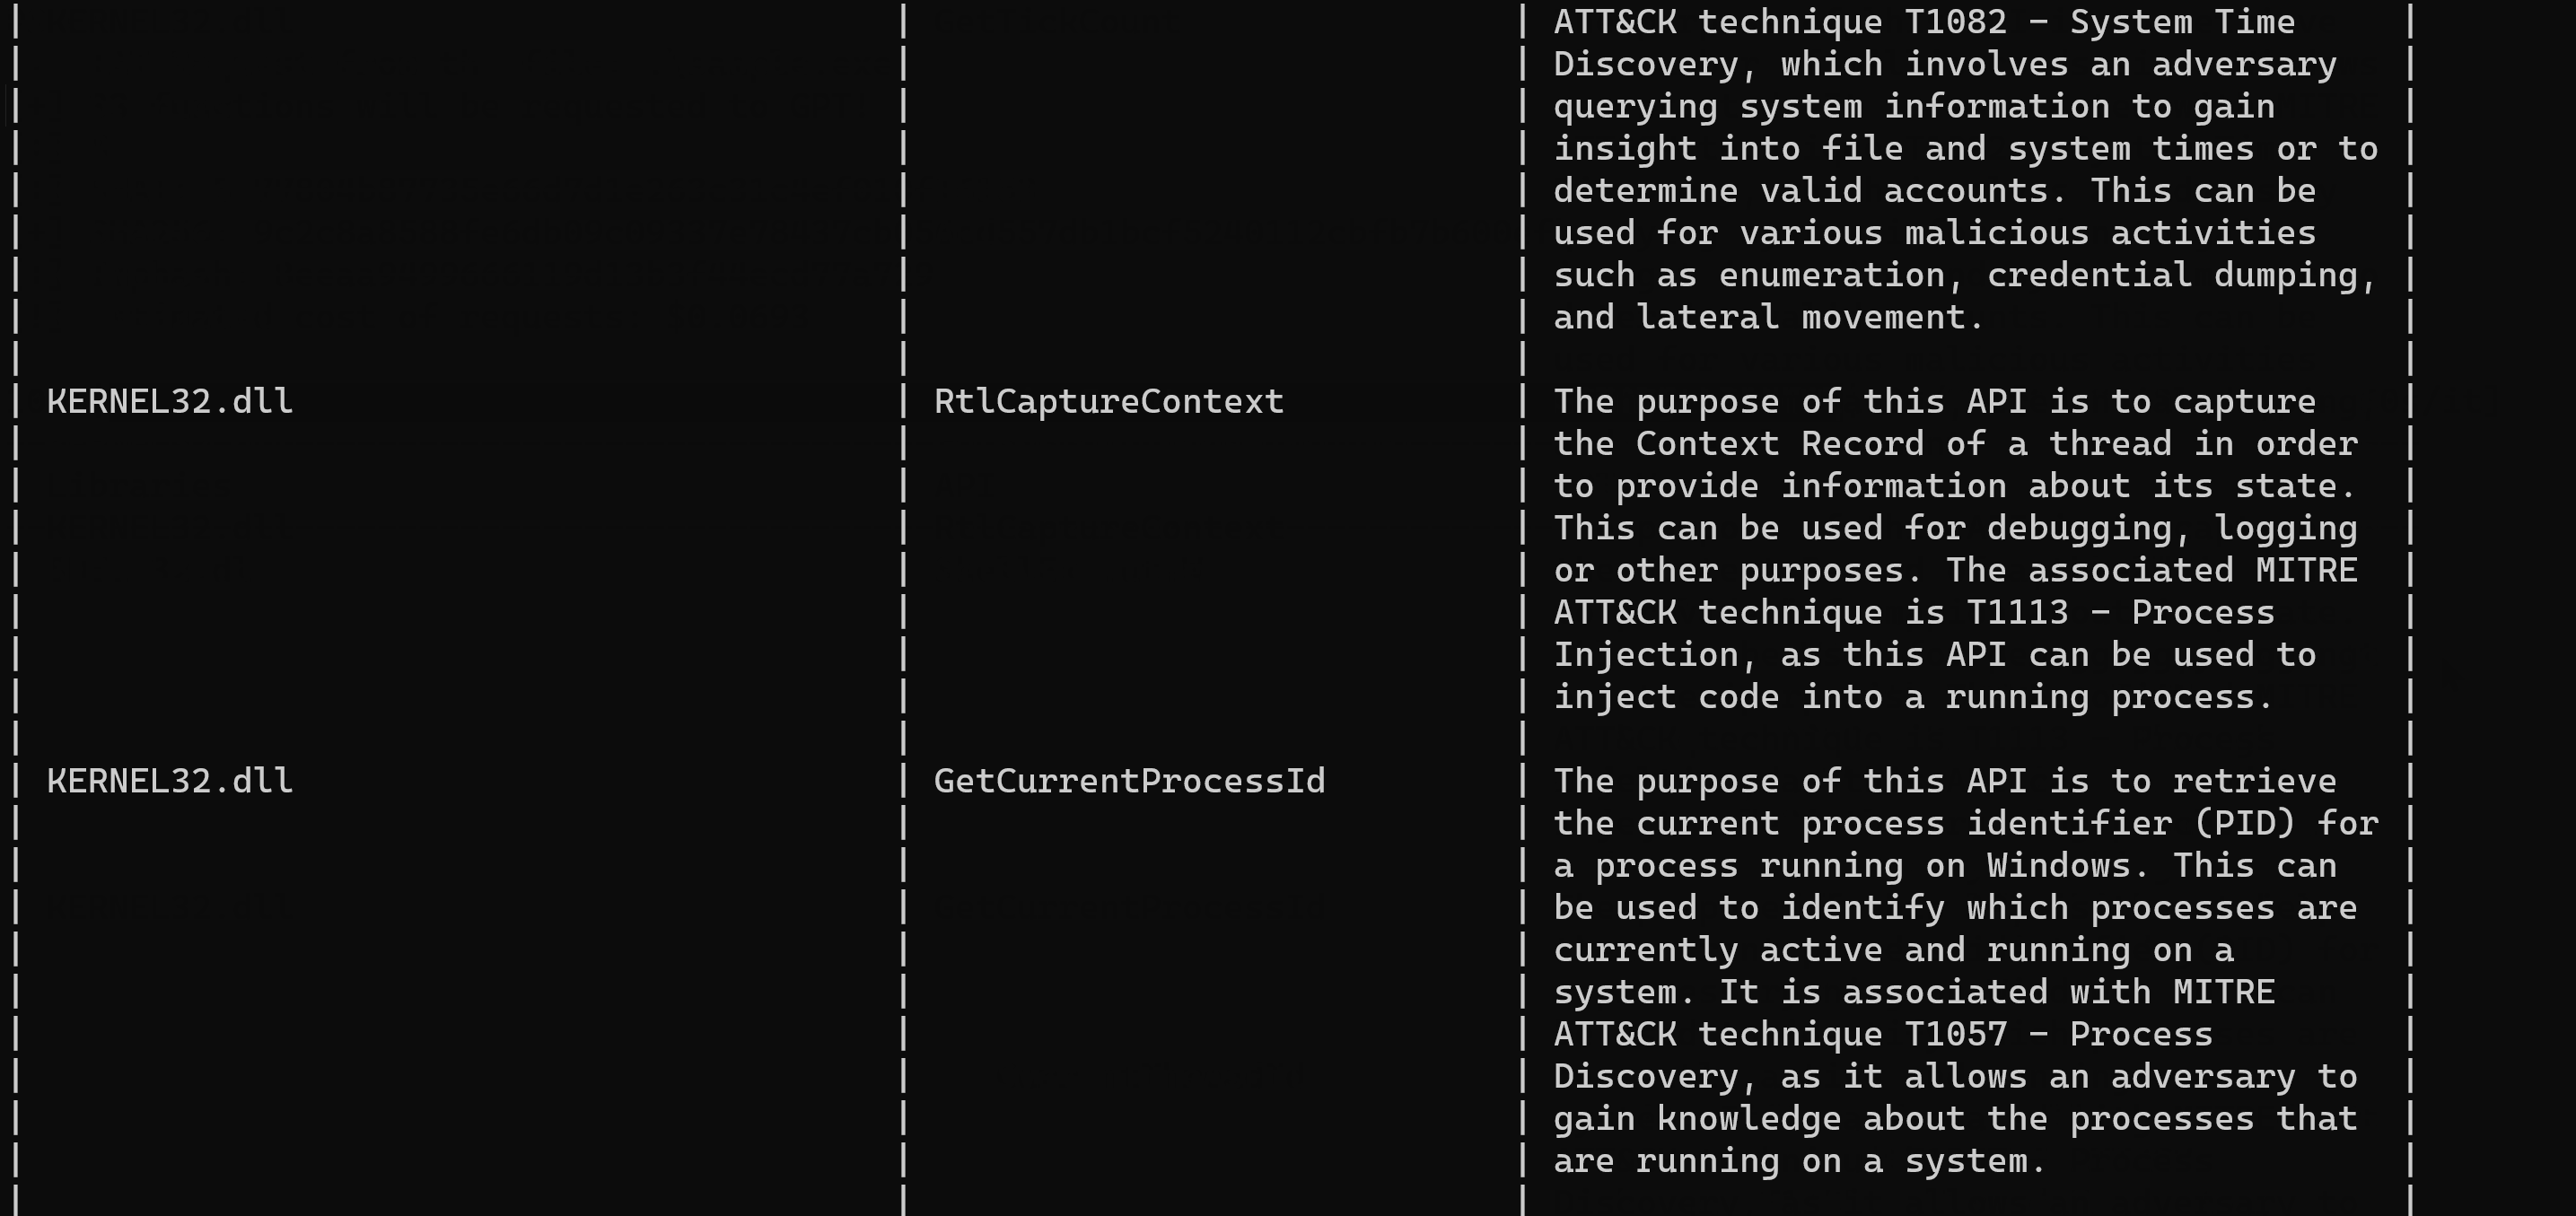
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…

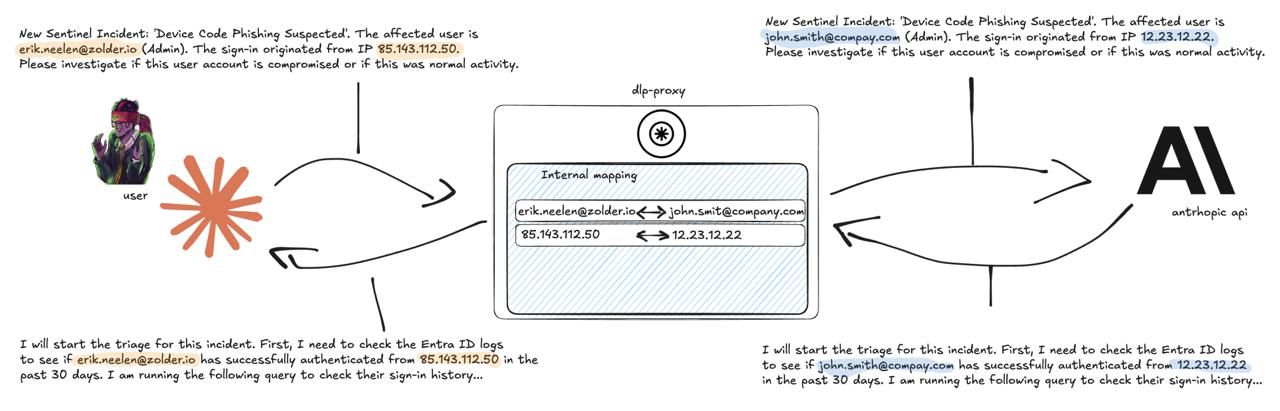
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…


CLI tool for open source and threat intelligence

A collection of online trackers, advertising networks, telemetry collectors and general 'we like to watch' lists for you to use to get better control…

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…