
tirith
 sheeki03/tirith
Terminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
curated-resourcesdata-exfiltrationdevsecops+8
2.7k
sheeki03/tirithTerminal security for developers and AI agents. Intercepts homograph URLs, pipe-to-shell, ANSI injection, obfuscated payloads, data exfiltration, and…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
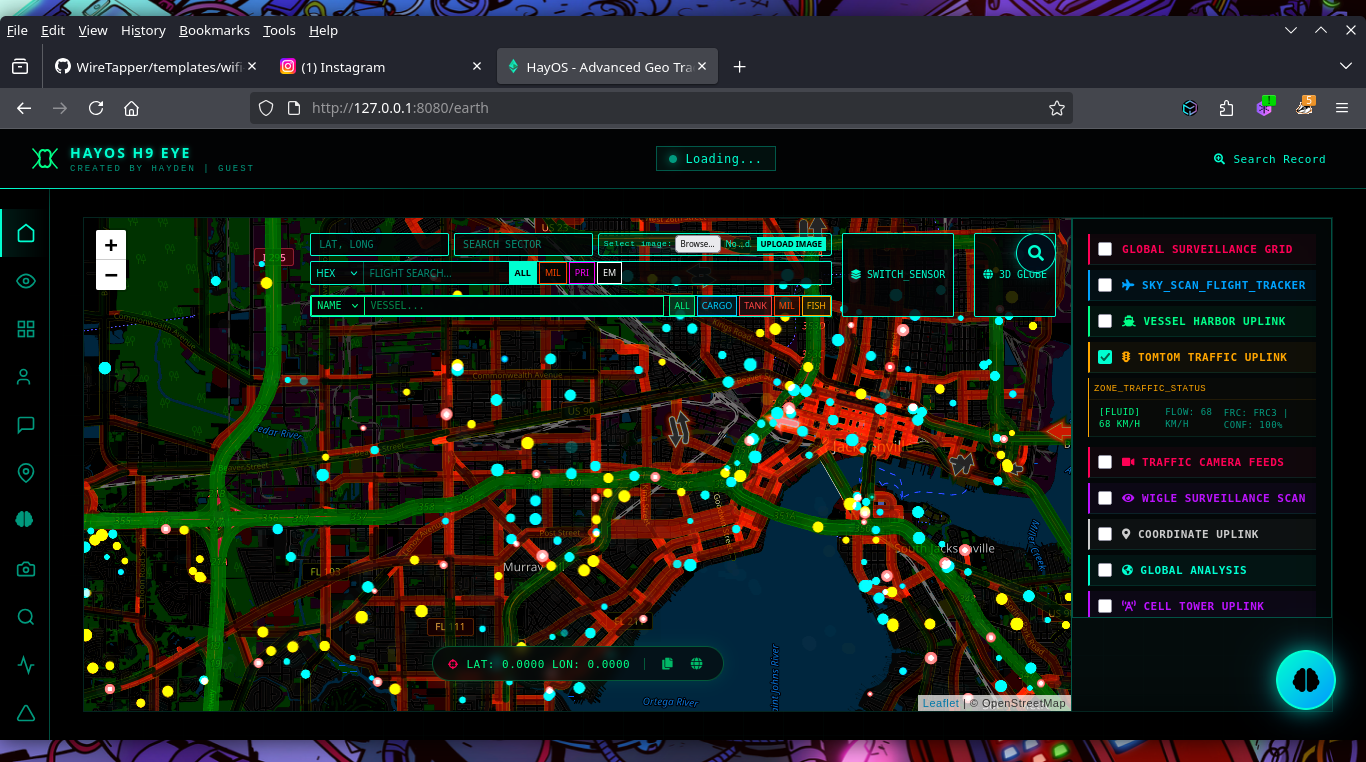 h9zdev/geosentinel
Real-time geospatial OSINT platform aggregating flight, vessel, and satellite data with dark web search, social media dorking, and AI-powered…
 badchars/darknet-mcp-server
66-tool MCP server for dark web intelligence — breach data, ransomware tracking, Tor .onion access, malware analysis, blockchain intel, exploit…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
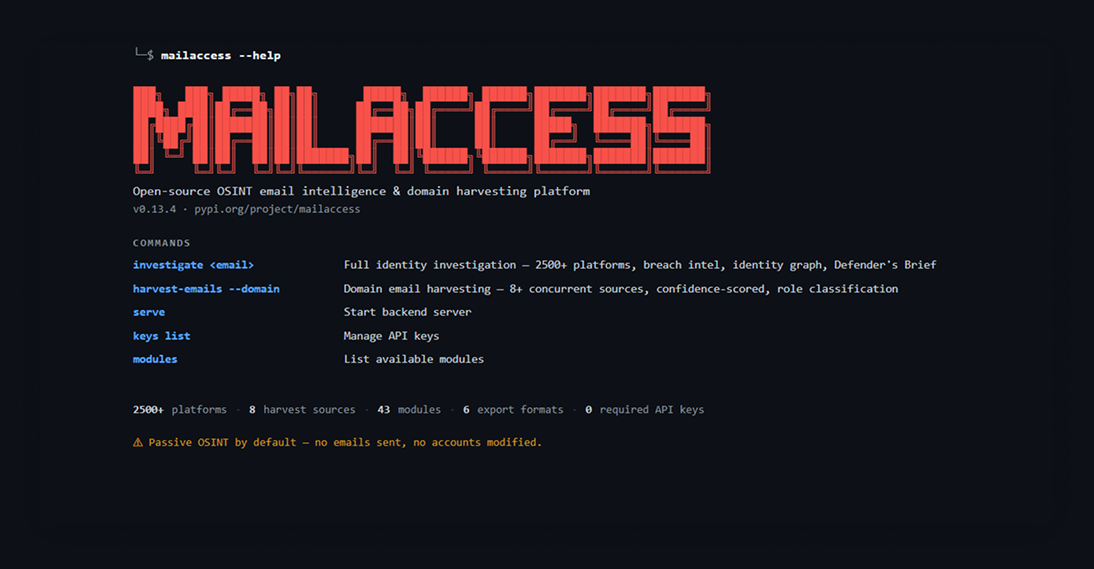 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
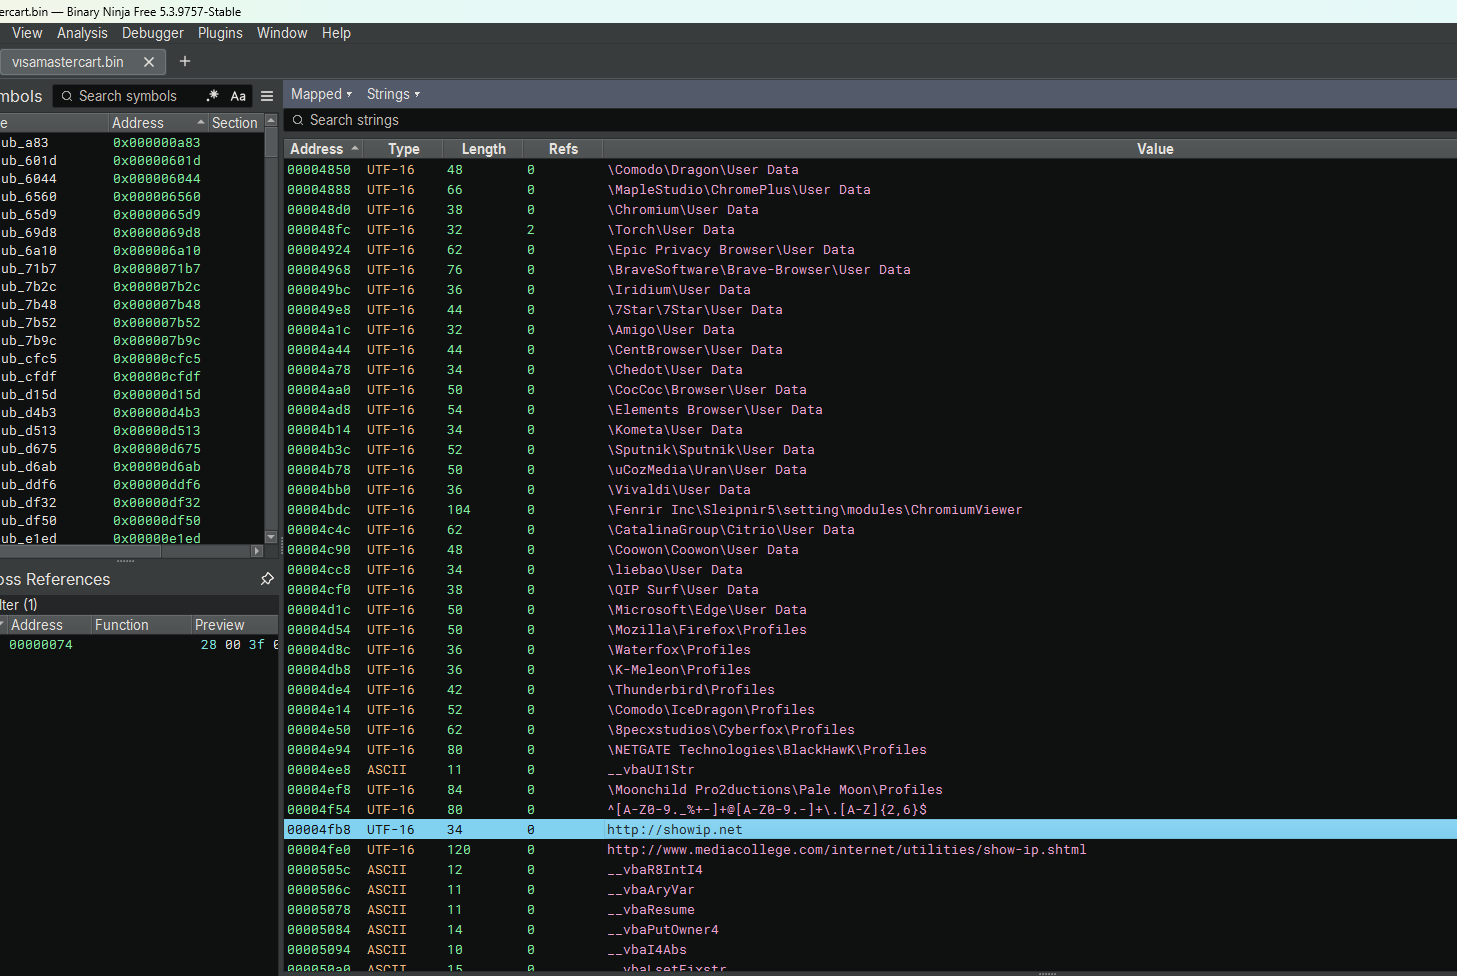 kaandemir993/darktortilla-rat-telegram-exfiltration-payload-extraction-analysis
Reverse engineering analysis of DarkTortilla RAT, a sophisticated malware that steals credit card data, decrypts browser passwords, and exfiltrates…
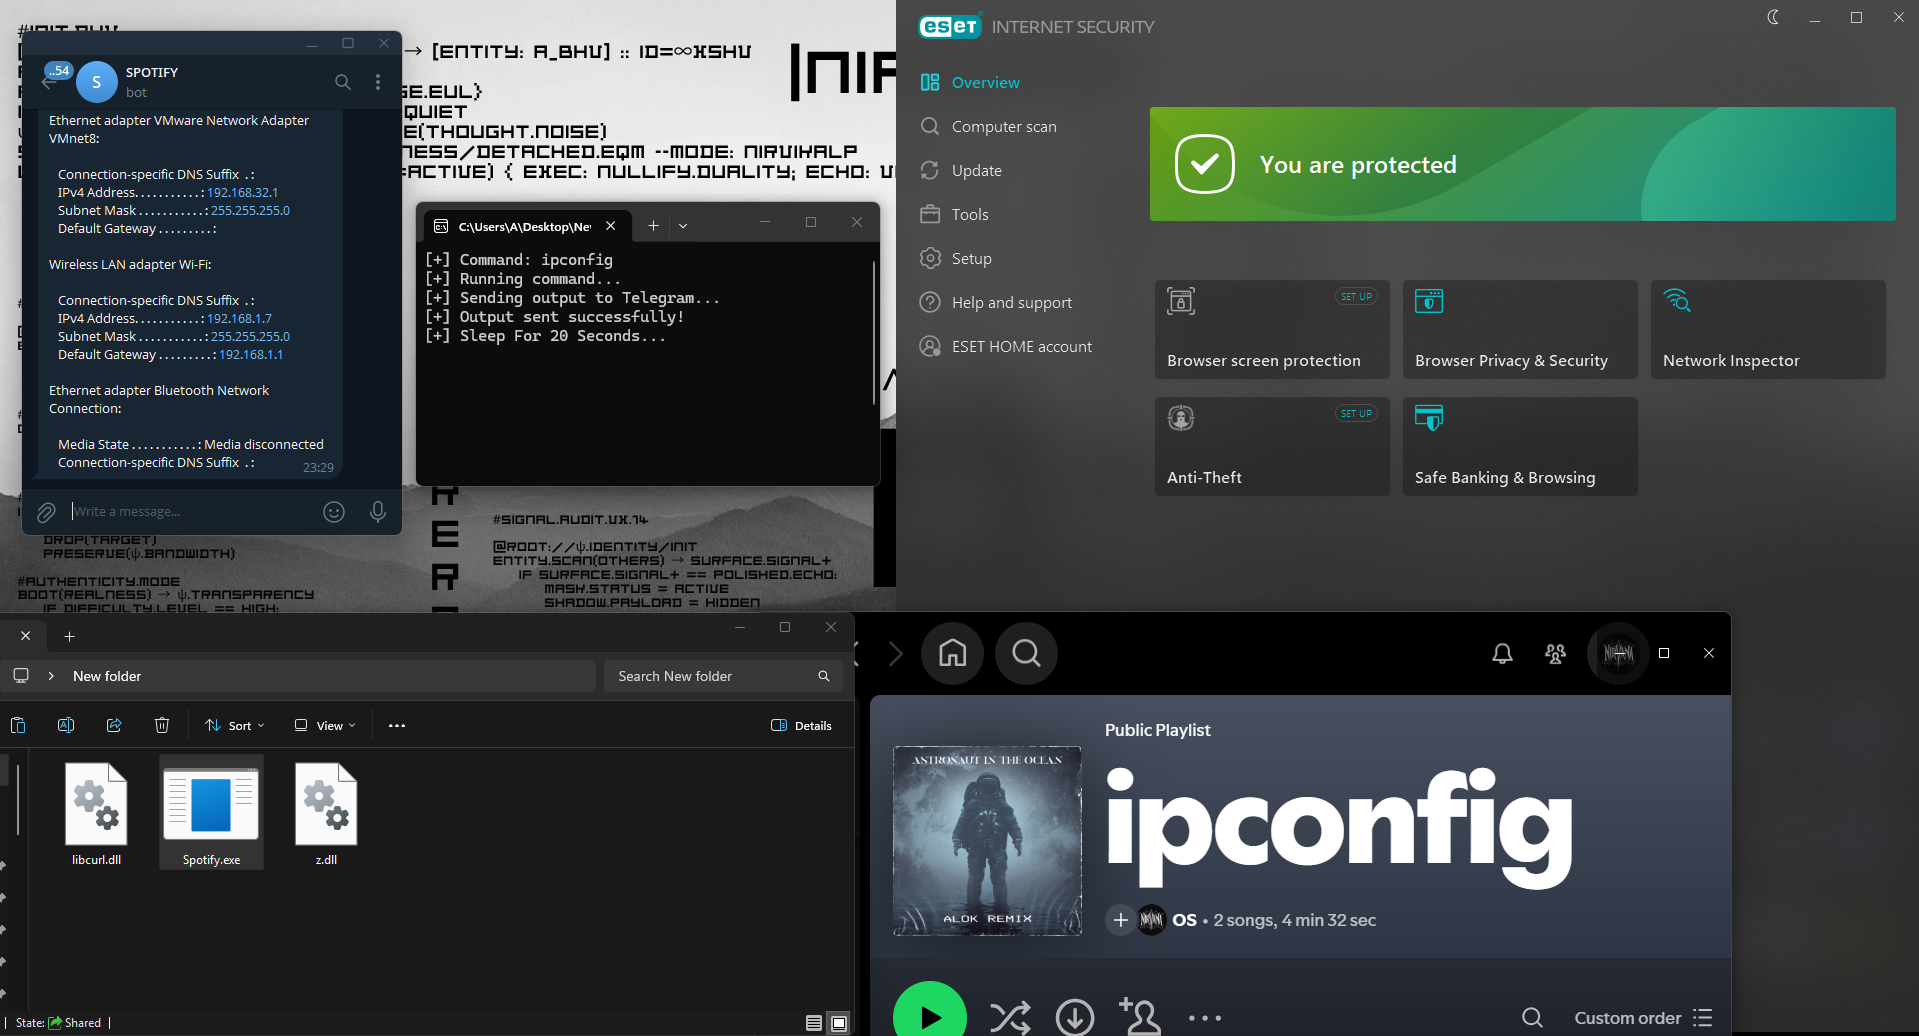 nirvanaon/spotifyc2
Windows-based C2 research tool that uses Spotify playlists as a command channel and Telegram for output delivery, demonstrating cloud-assisted…
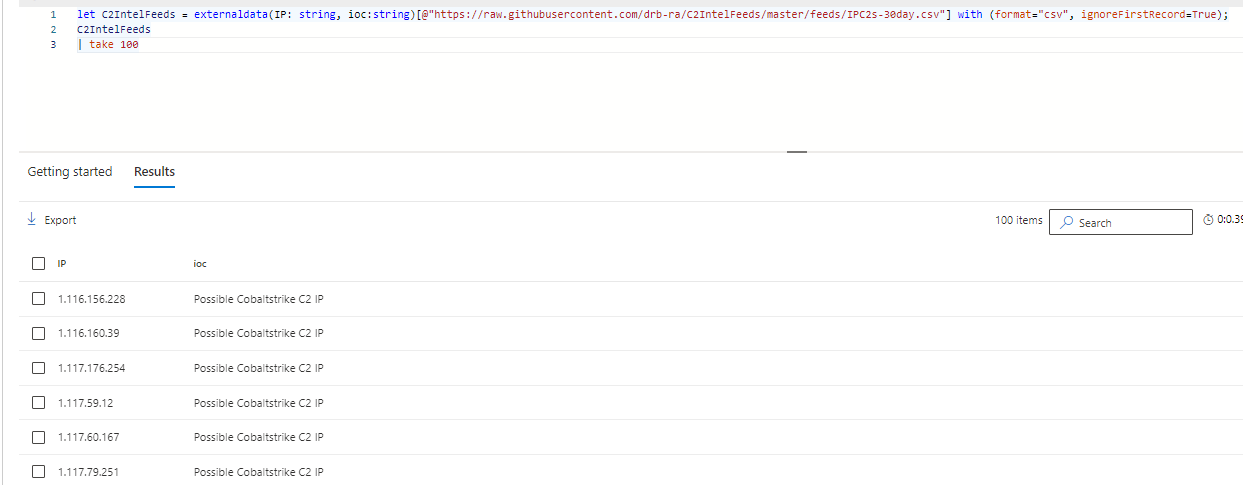 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 kennbroorg/iky
OSINT Project. Collect information from a mail. Gather. Profile. Timeline.
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 ethan-andrews/exploitarium-detections
KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
 luckypipewrench/pipelock
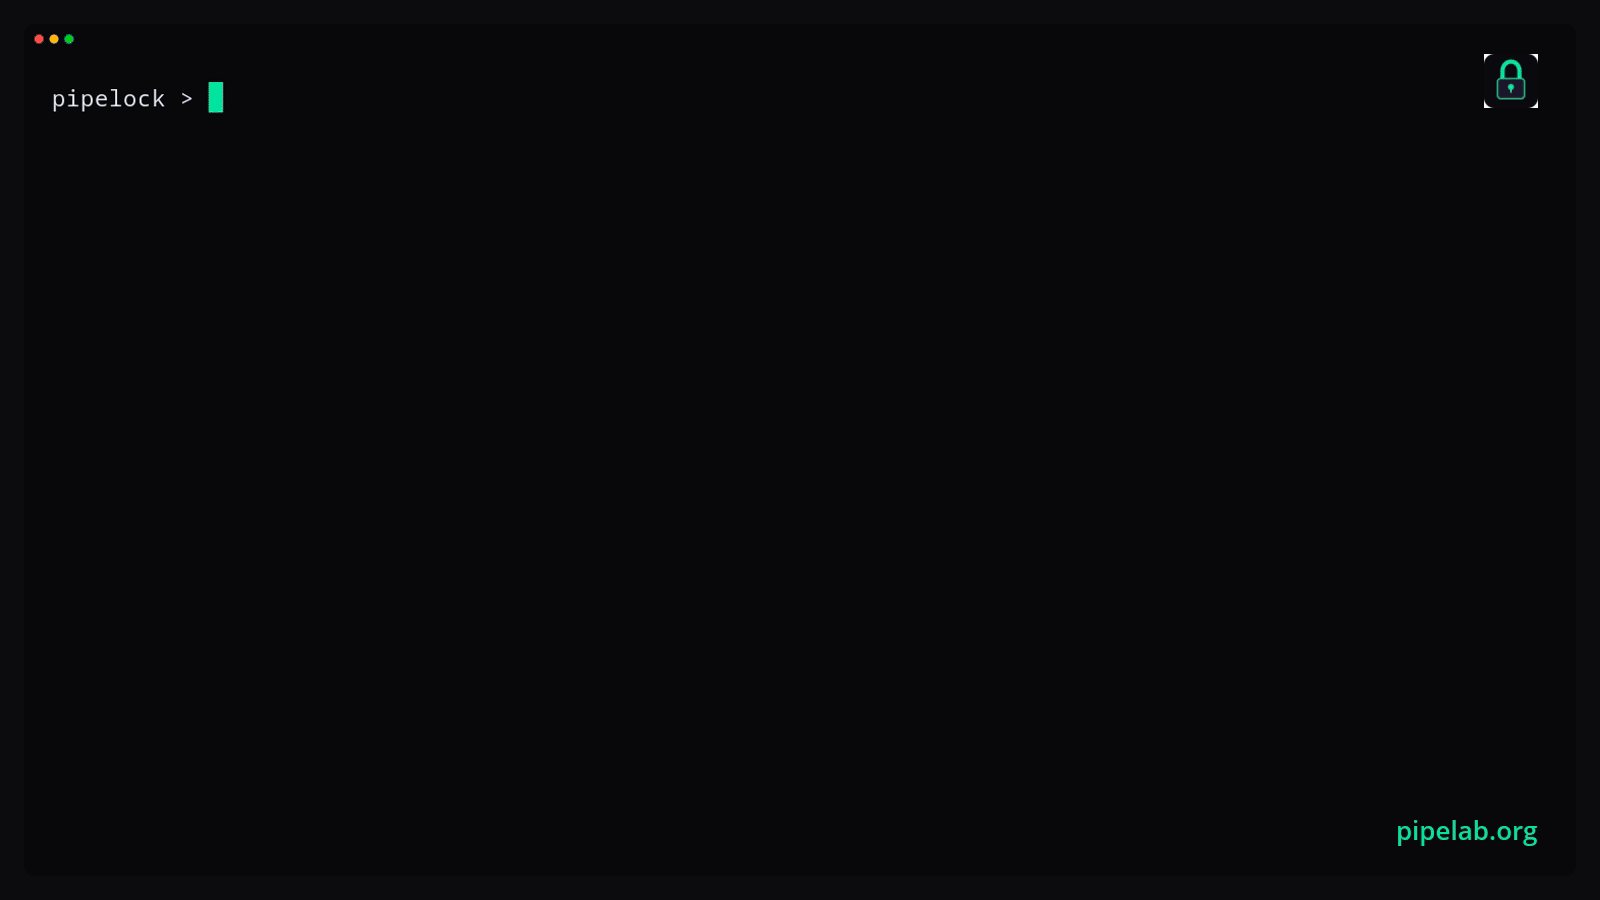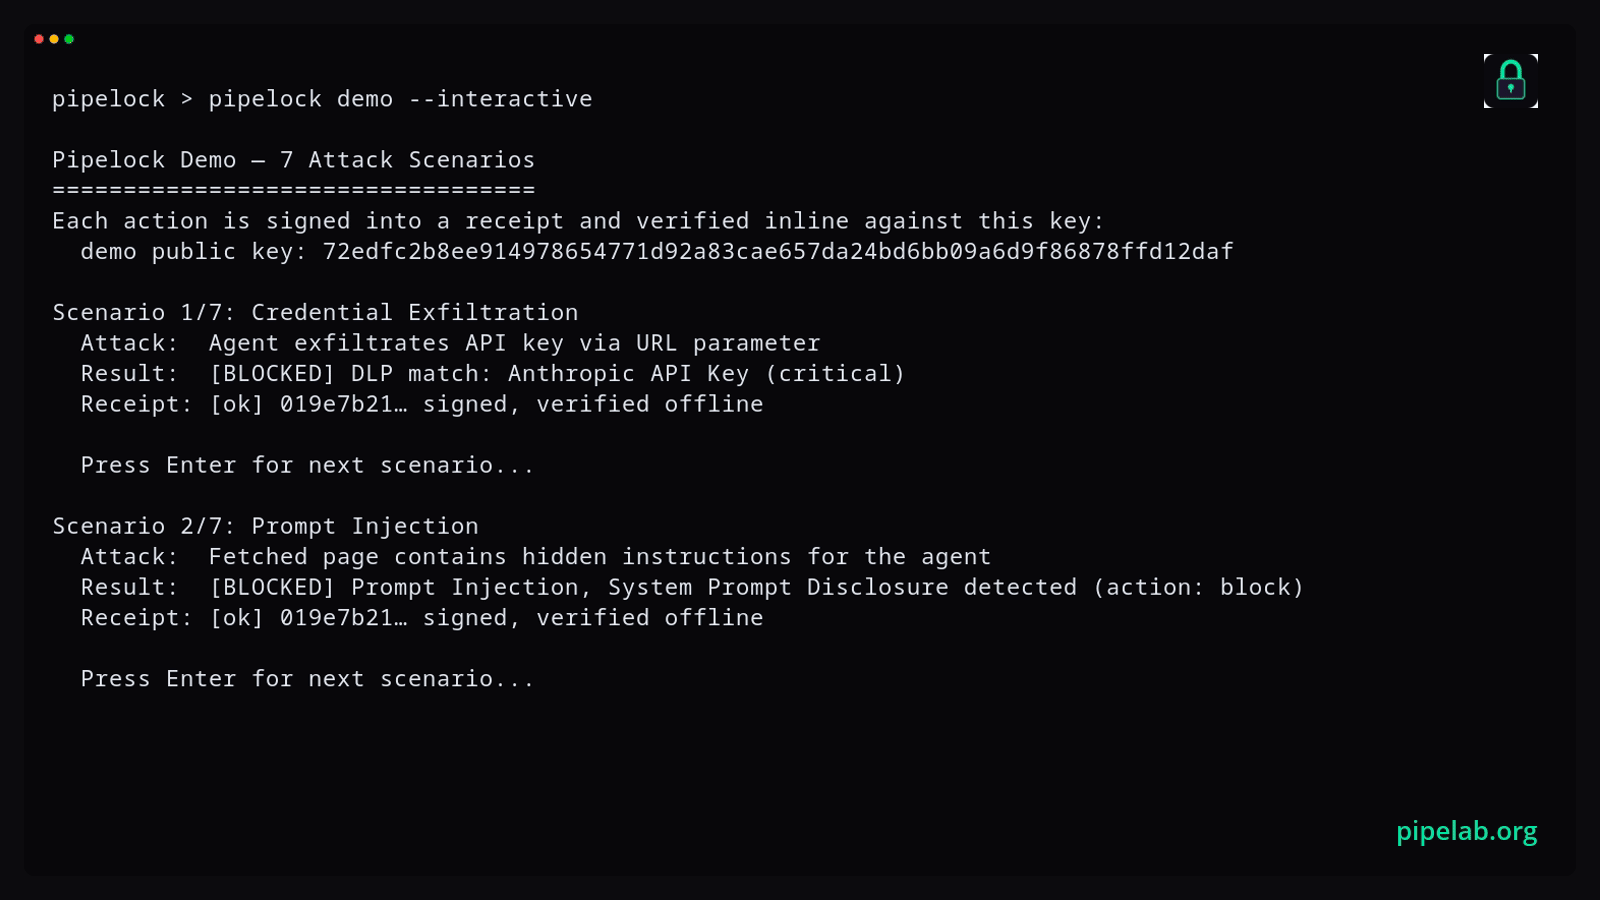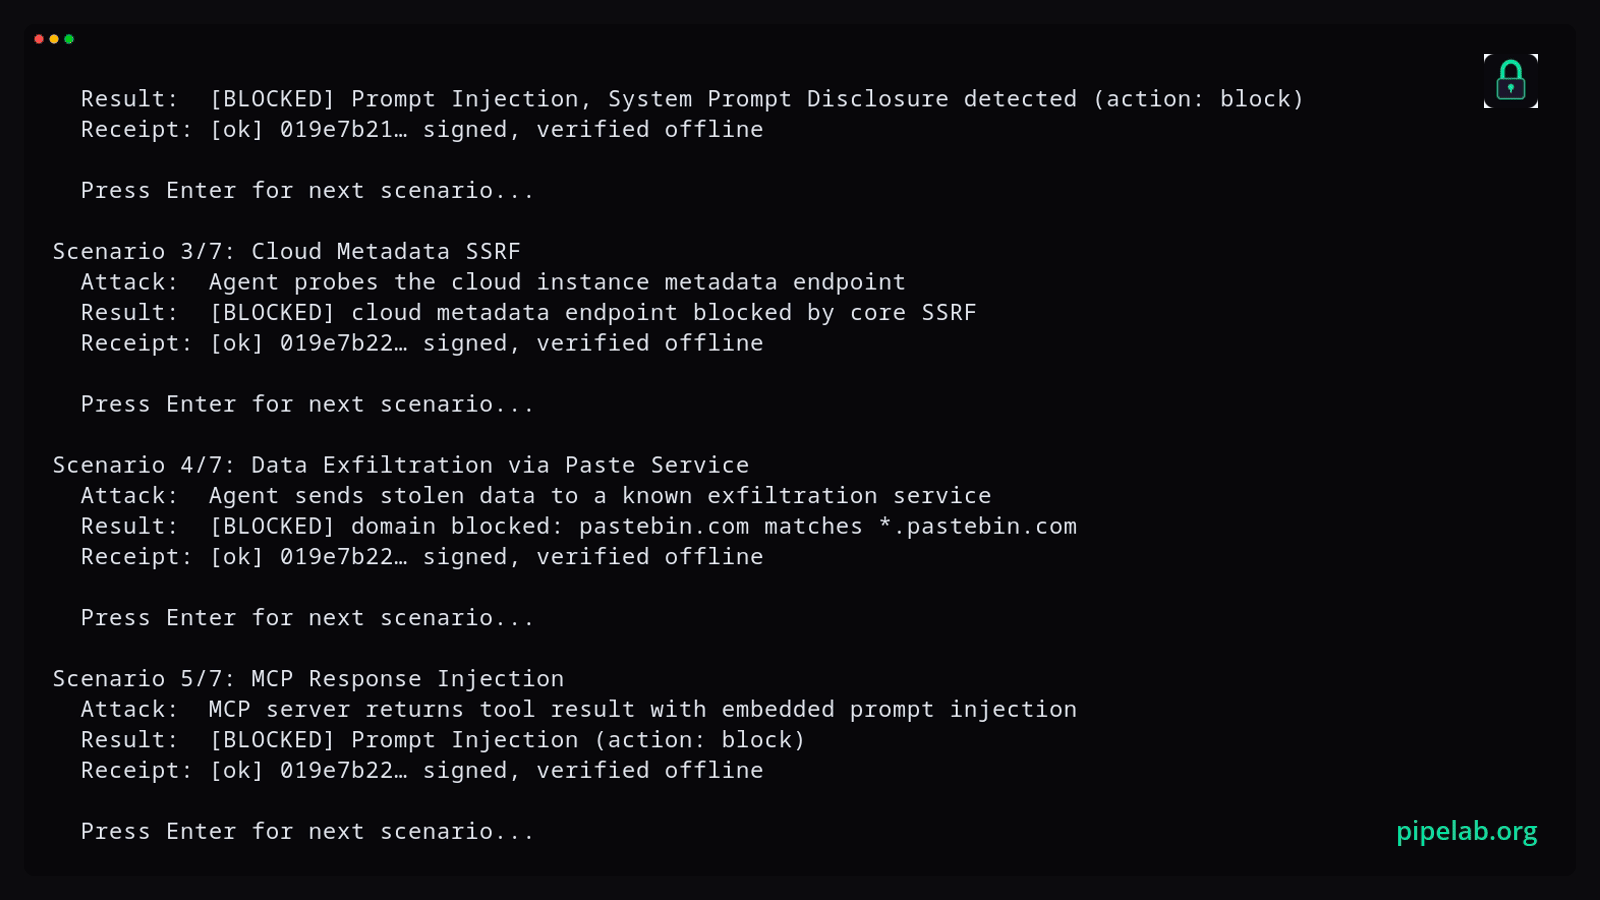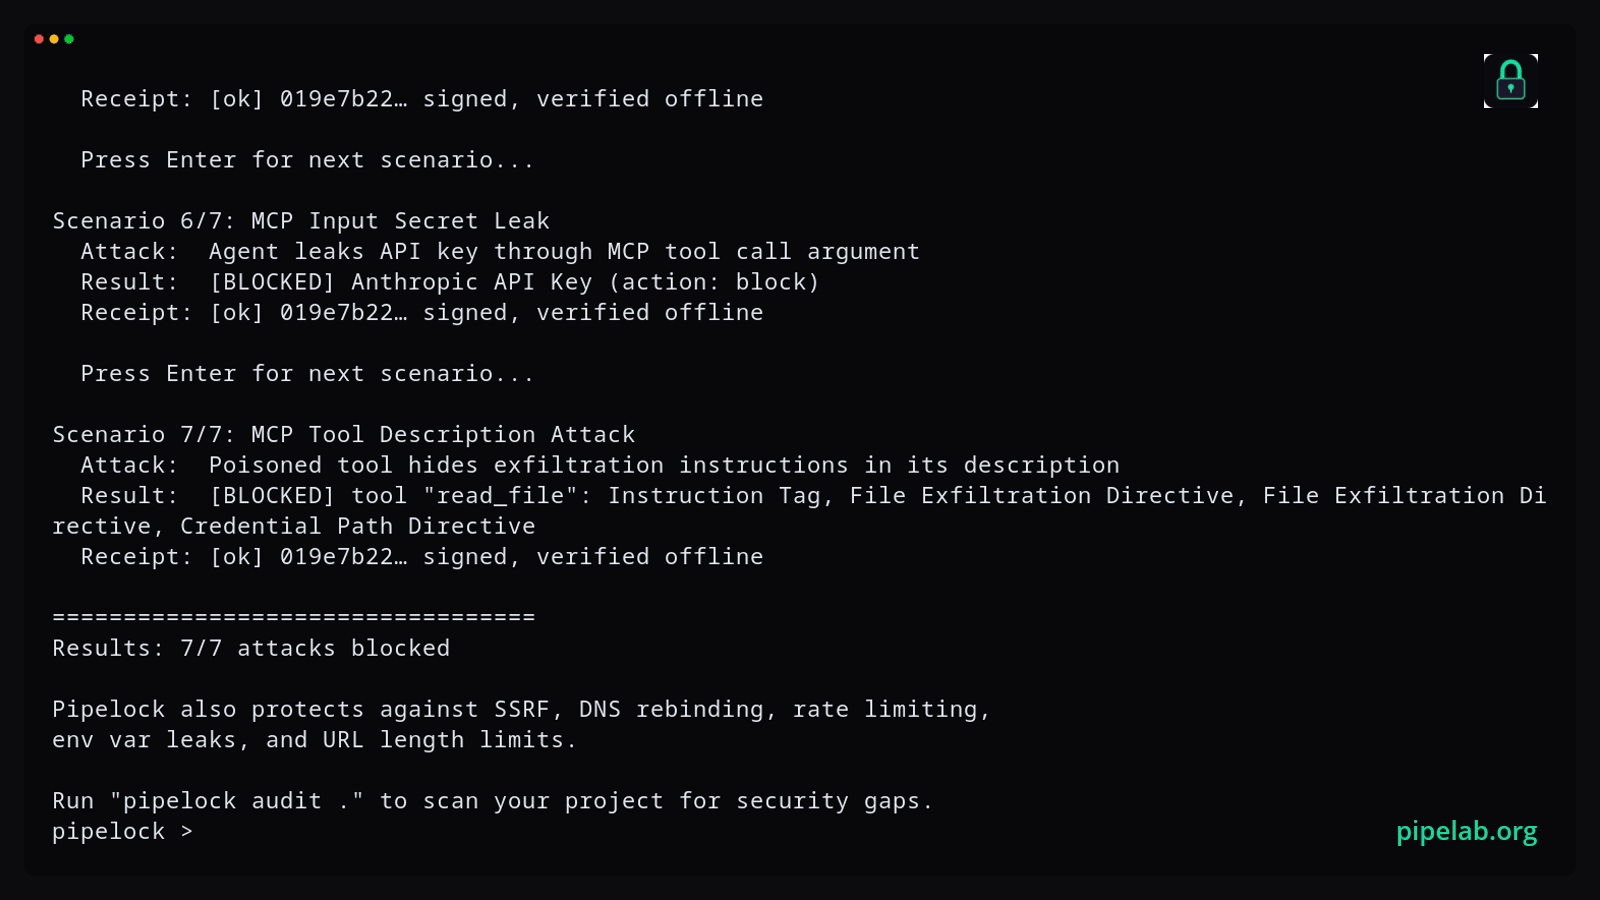
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 drunkf0x/adspider
Monitor changes in Active Directory with replication metadata
 sh3llyr/statistrings
YARA Rule Strings Statistics Calculator and Malware Research Helper
 browserbox/browserbox
💚🇺🇸🗽Secure remote browsing anywhere, any way you like it.
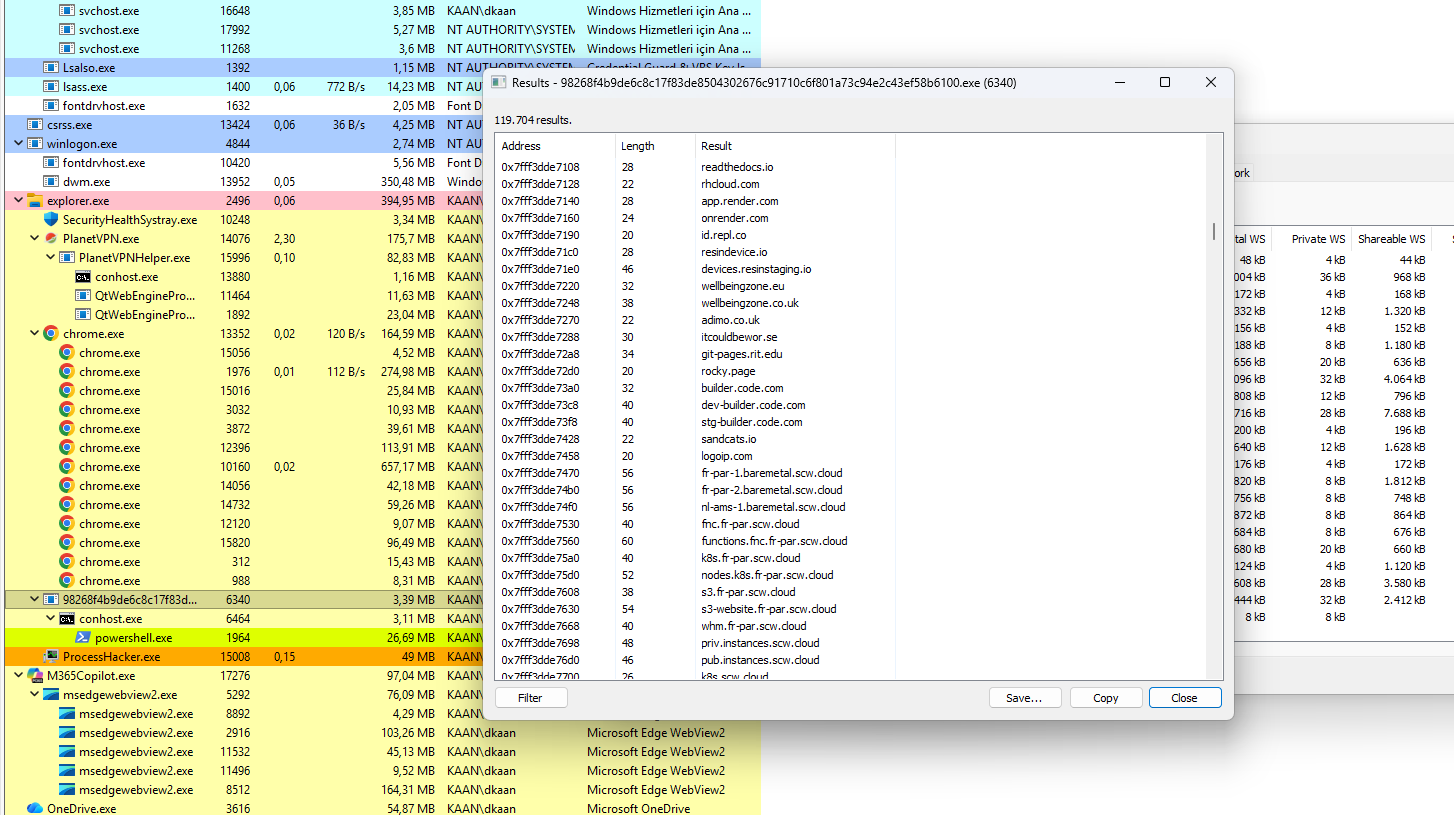 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.