

chainsaw
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k
withsecureopensource/chainsawRapidly Search and Hunt through Windows Forensic Artefacts
 permiso-io-tools/cloudgrappler
Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
 rspamd/rspamd
Spam filtering and email processing framework with regex rules, statistical analysis, custom Lua plugins, and external blocklists for MTA integration.
 vigil-xy/agent-scanning
Unified dashboard to monitor, govern, and audit AI agents in real-time. Enforce budgets, detect policy violations, and export compliance reports for…
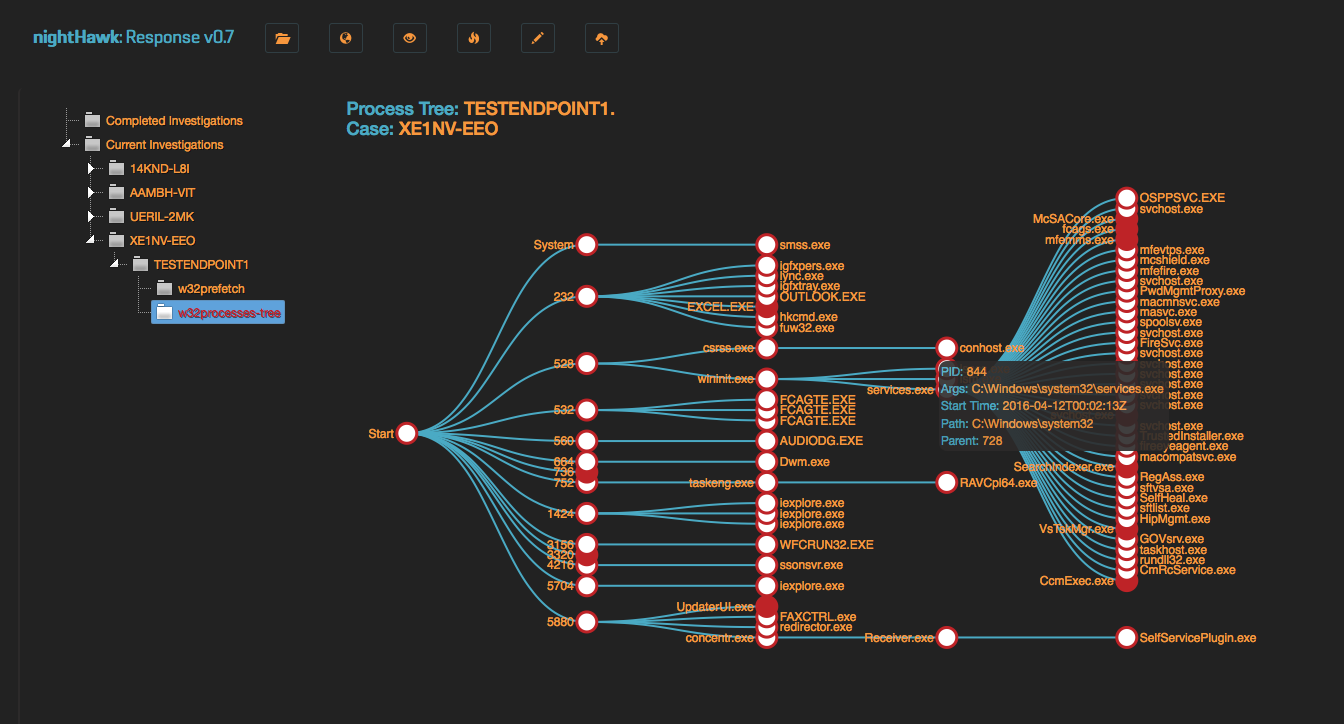 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 shadowopcode/desckvb-rat
Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).

 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 mnemonic-no/grafeo
Open platform for modelling, collection and exchange of knowledge
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 retrospected/purplekeep
Providing Azure pipelines to create an infrastructure and run Atomic tests.
 17patmaks/my-sigma-rule-collection
Sigma Rule for CVE-2025-49666