

auditd-attack
 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
configuration-auditingdefensive-toolsintrusion-detection+2
8227 years ago
bfuzzy/auditd-attackA Linux Auditd rule set mapped to MITRE's Attack Framework
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 blevene/bandjacks
Cyber Threat Defense World Modeling

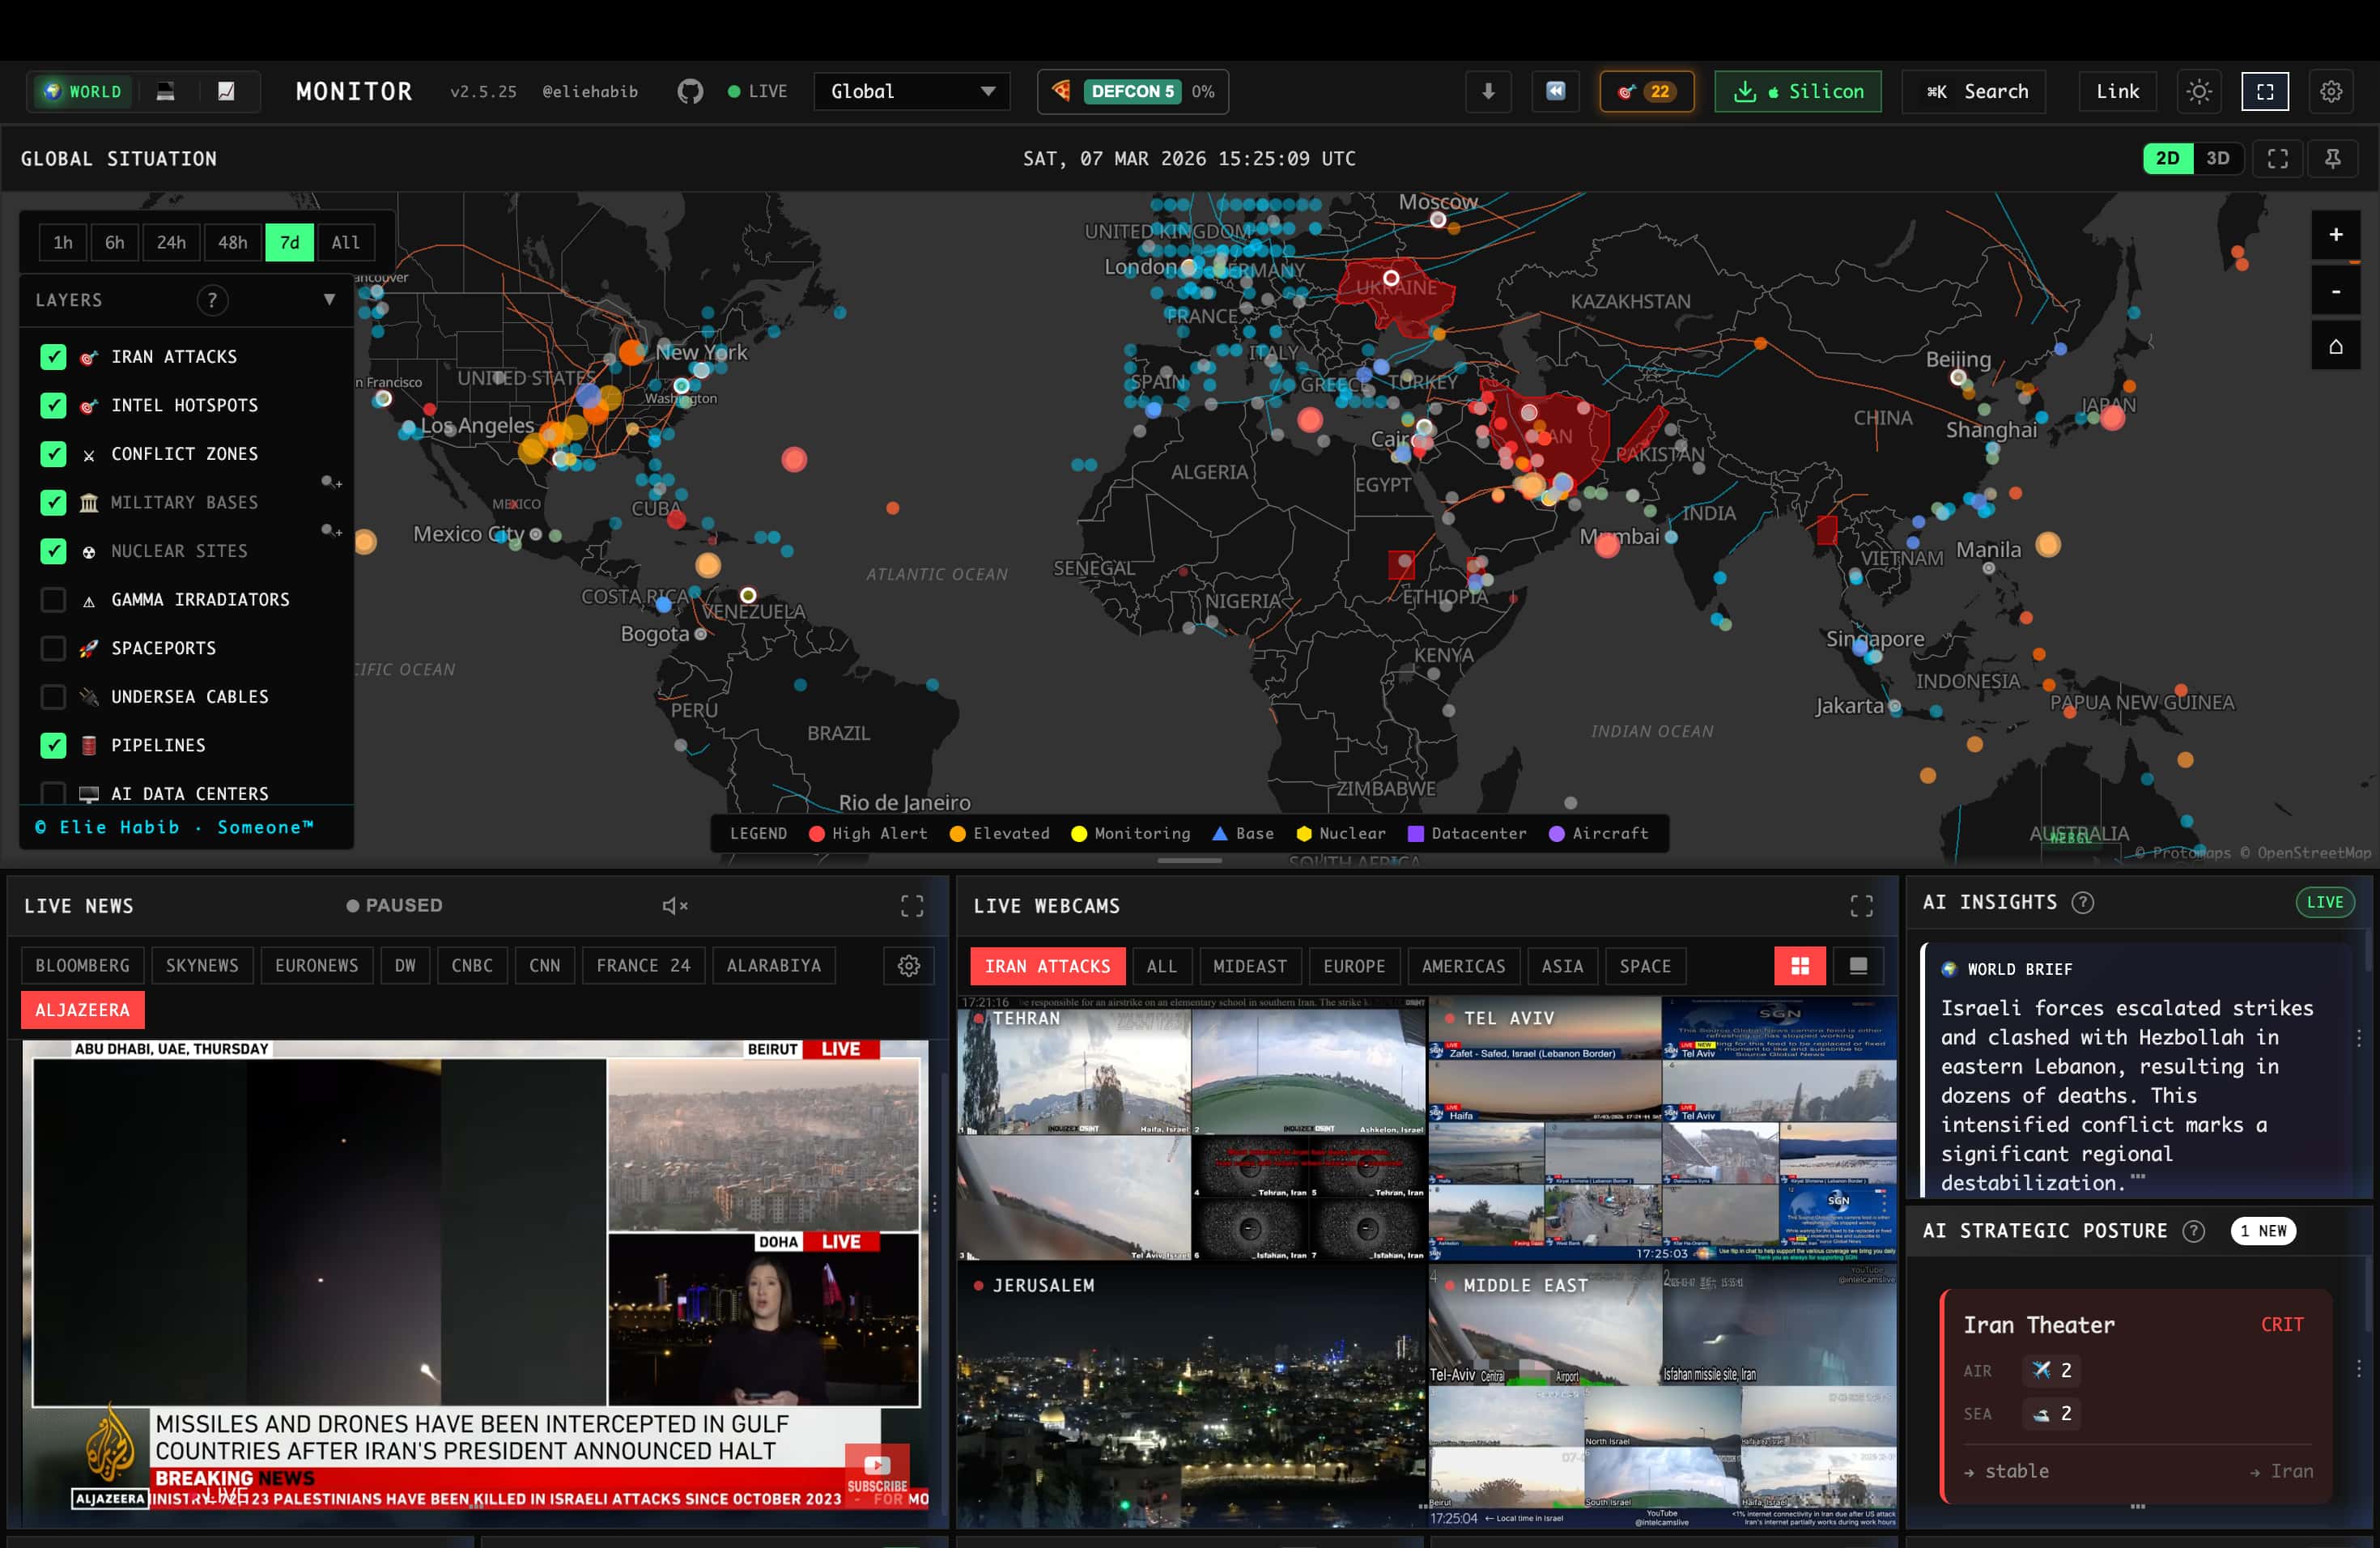 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
 payloadsecurity/sandbox_scryer
Parses public sandbox detonation reports to produce threat hunting intelligence, organizes findings via MITRE ATT&CK, assembles IOCs, and generates…
 reloading01/certstream-server-rust
High-performance Certificate Transparency (CT) monitoring tool written in Rust. Real-time stream of newly issued SSL/TLS certificates from CT logs.…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 vulncheck-oss/cli
VulnCheck's official command line tool
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 fastfire/deepdarkcti
Collection of Cyber Threat Intelligence sources from the deep and dark web
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
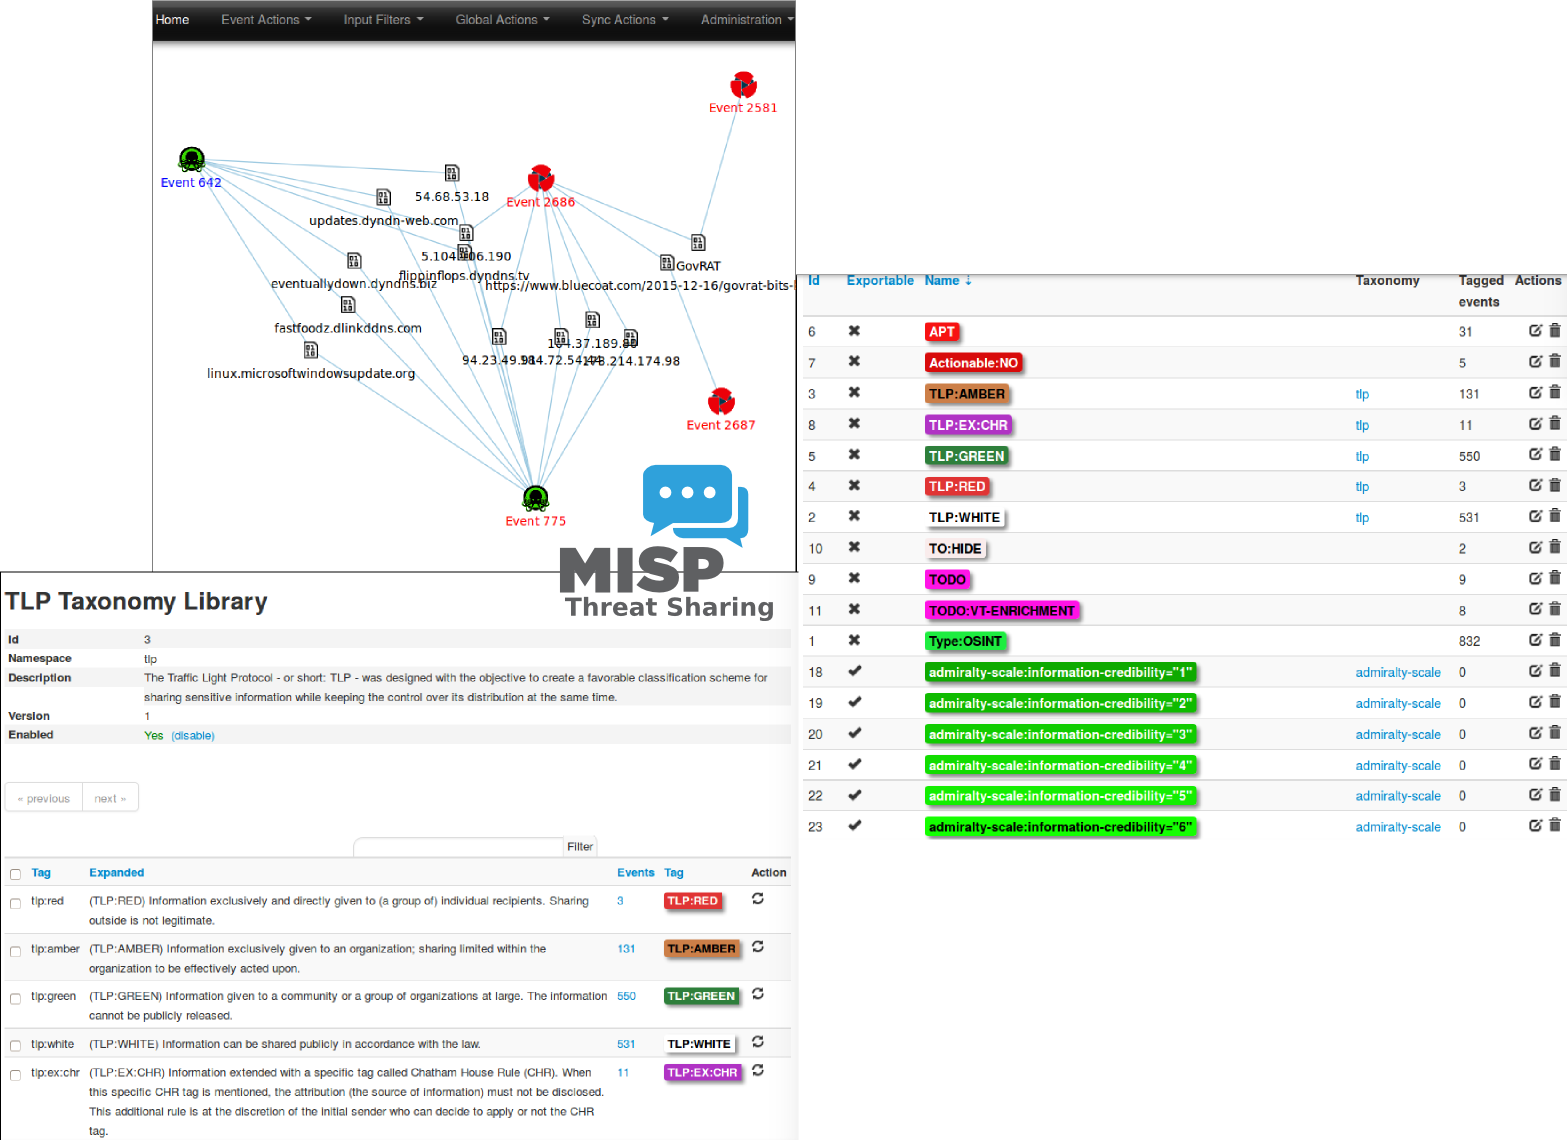 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform