
 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 katrielmoses/voidaccess
Self-hosted dark web OSINT platform. Automated threat intelligence from query to graph in 13 steps. Free alternative to Recorded Future, DarkOwl, and…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
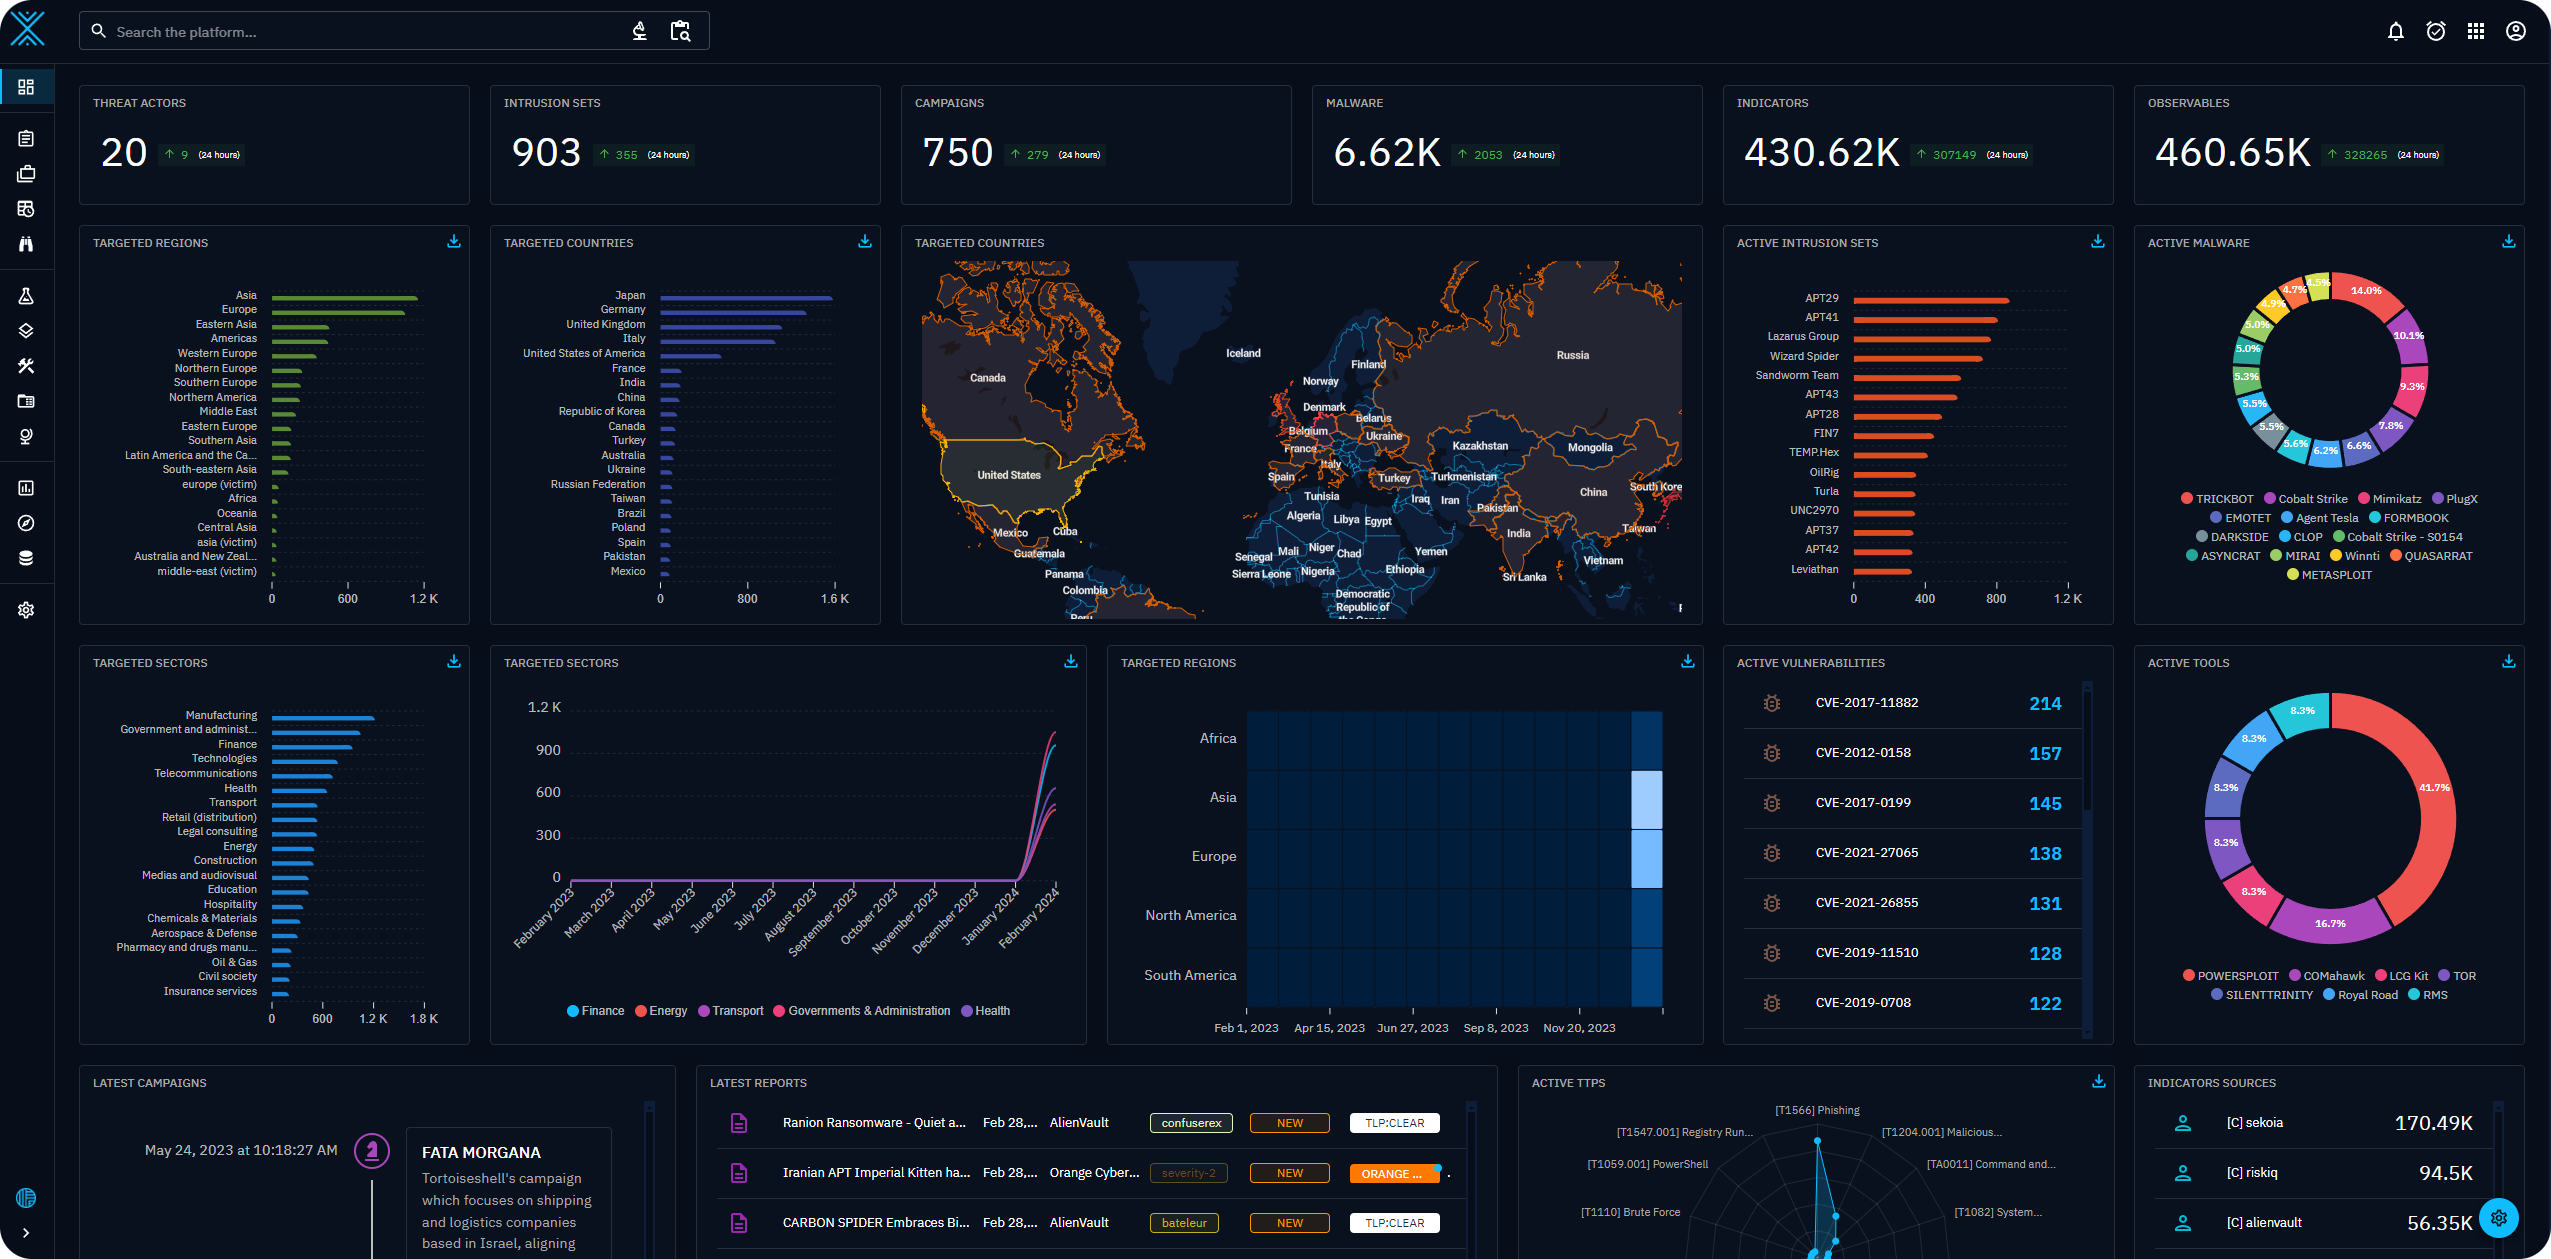 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
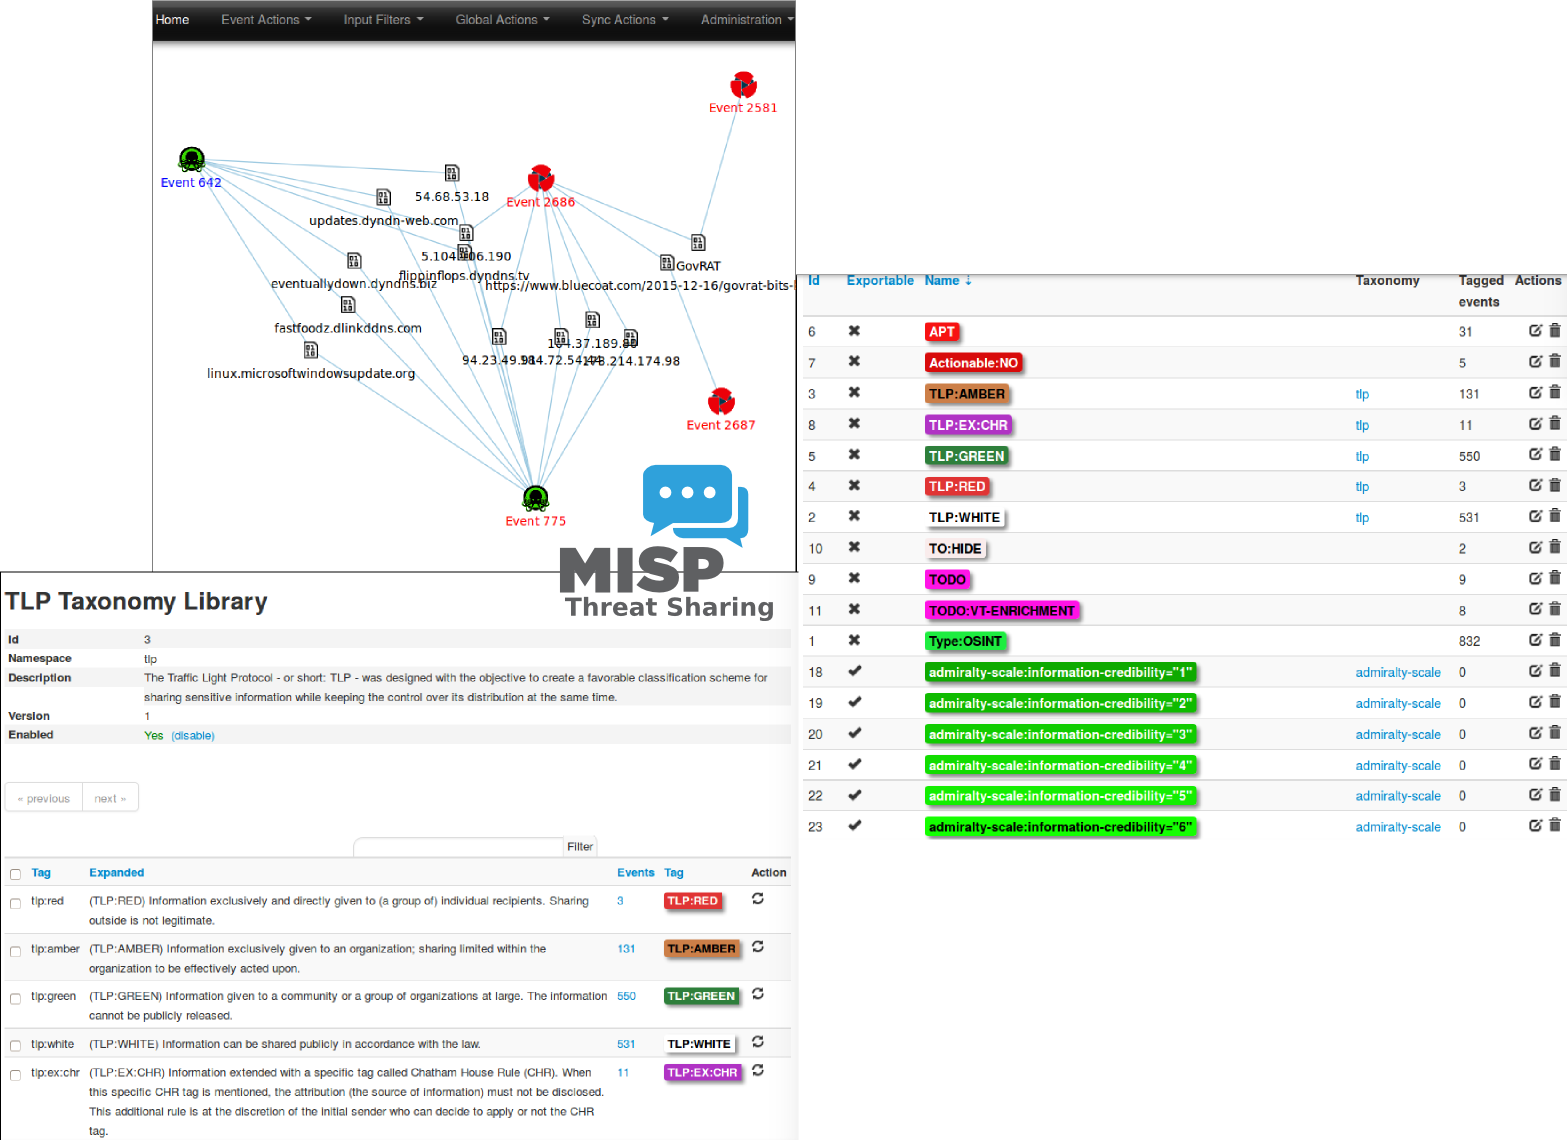 misp/misp
MISP (core software) - Open Source Threat Intelligence and Sharing Platform
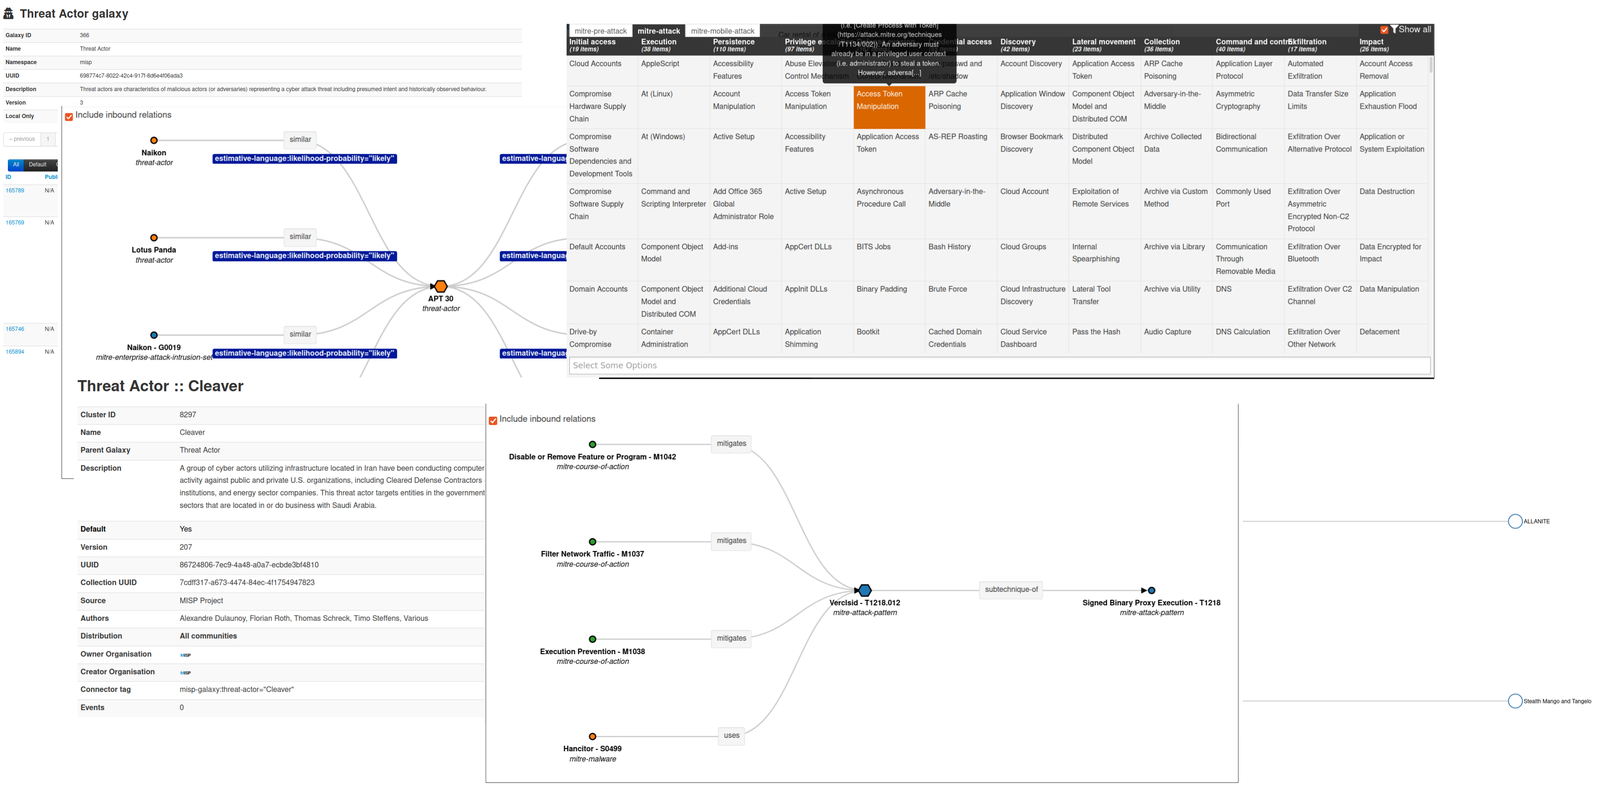 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)