

connectors
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
defensive-toolsincident-responseinformation-gathering+5
591
opencti-platform/connectorsCollection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
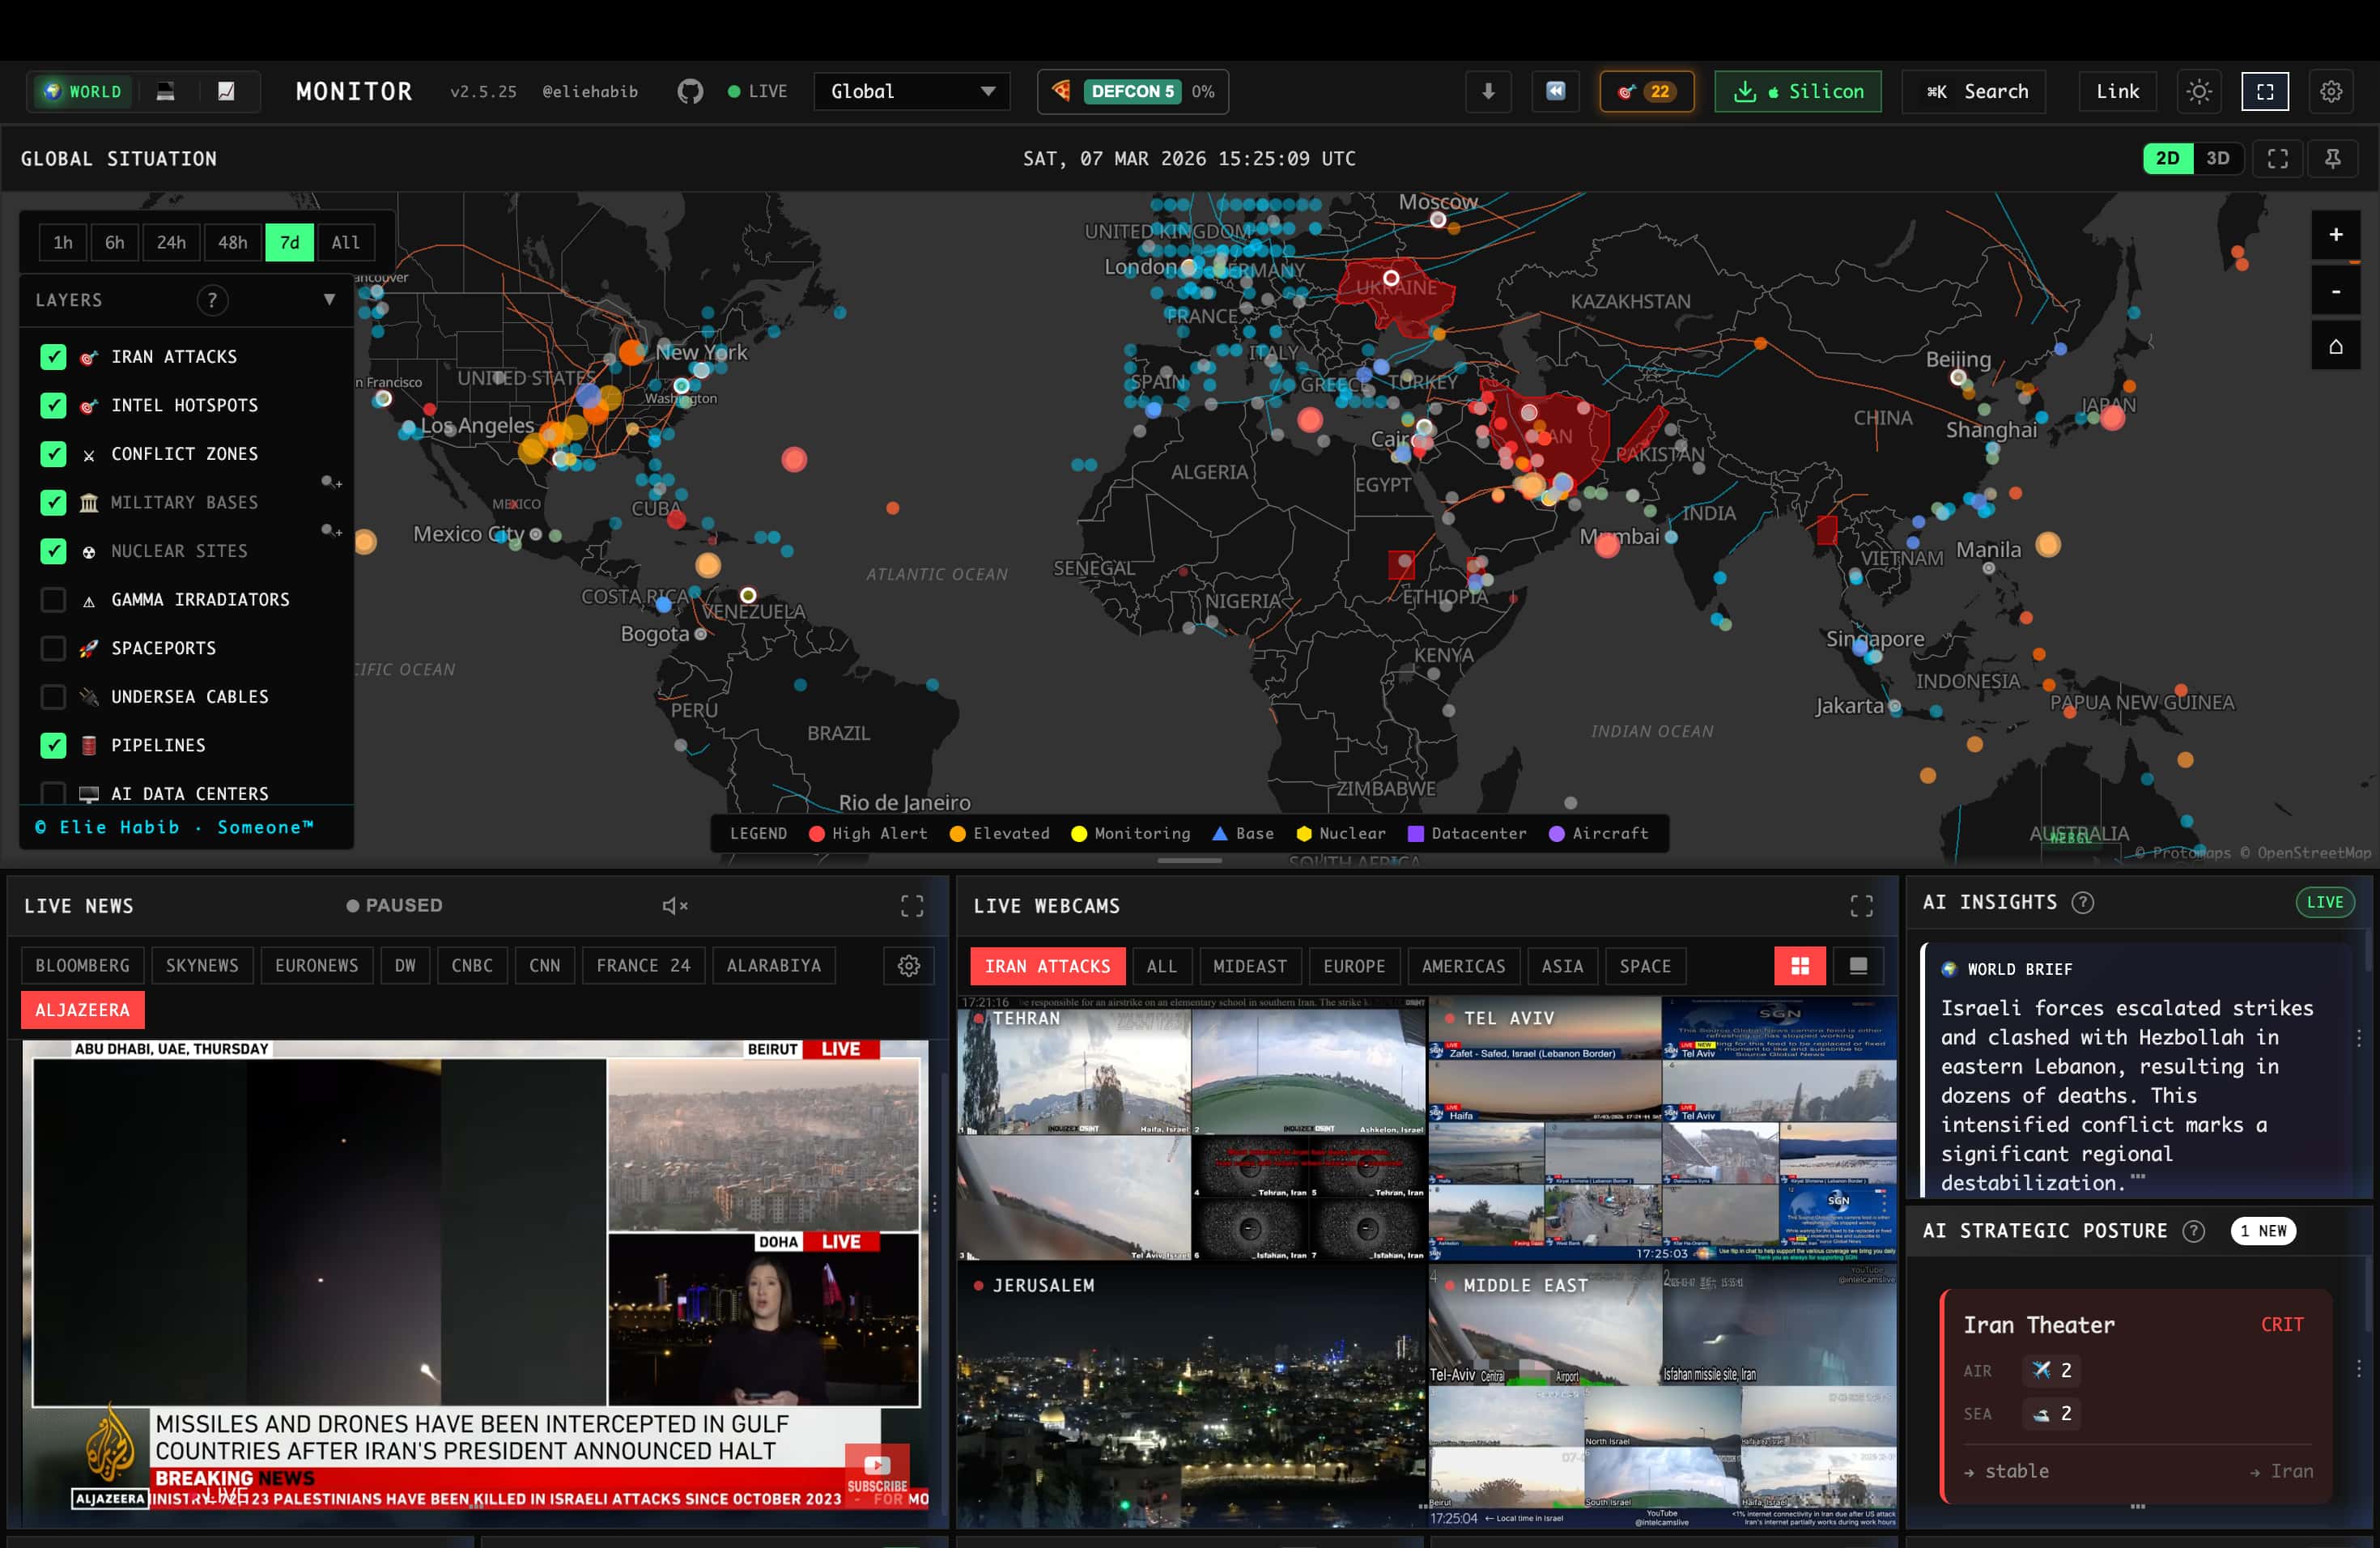 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
 fastfire/deepdarkcti
Collection of Cyber Threat Intelligence sources from the deep and dark web
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…