
ThreatIntelligenceDiscordBot
 vxunderground/threatintelligencediscordbot
Gets updates from various clearnet domains and ransomware threat actor domains
information-gatheringosintthreat-feeds-aggregators+1
433
vxunderground/threatintelligencediscordbotGets updates from various clearnet domains and ransomware threat actor domains
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 shirkdog/pulledpork
Pulled Pork for Snort and Suricata rule management (from Google code)
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 vulncheck-oss/cli
VulnCheck's official command line tool
 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 threatlabz/iocs
This repository is for Indicators of Compromise (IOCs) from Zscaler ThreatLabz public reports
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
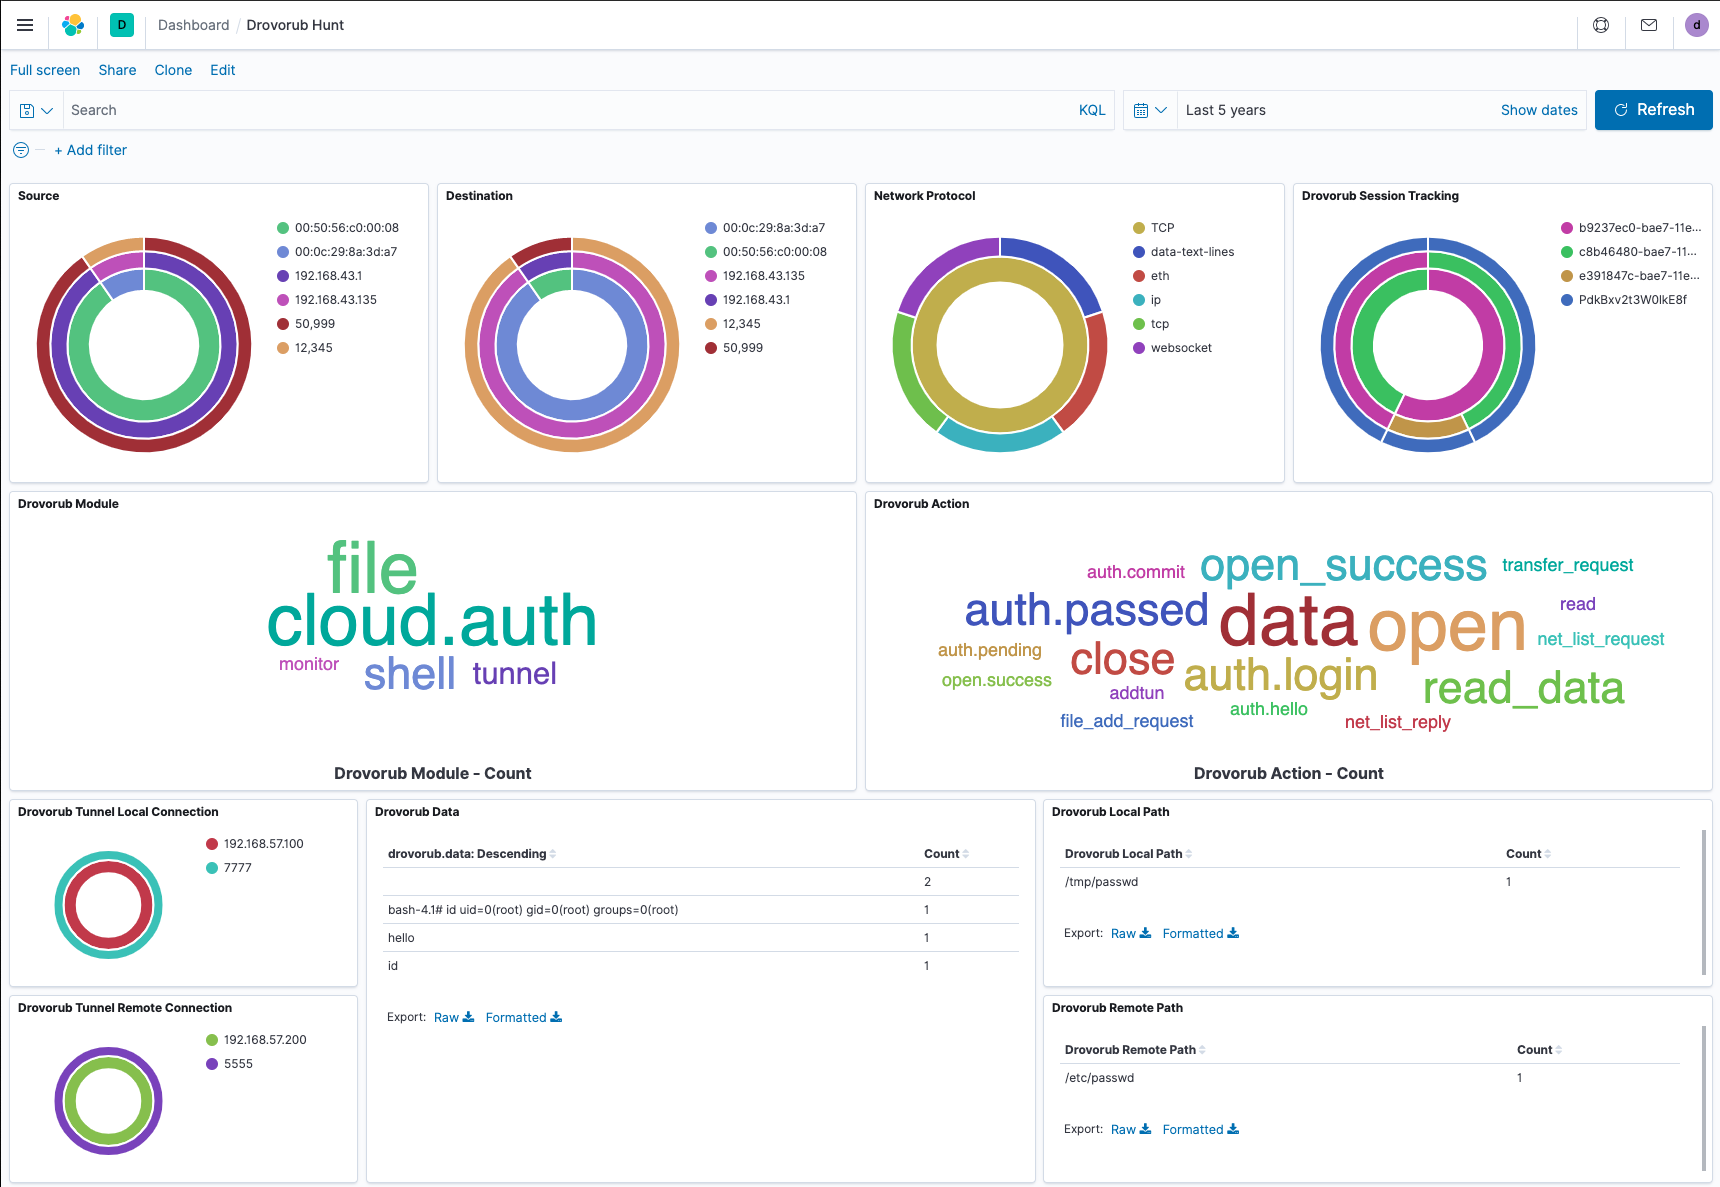 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 cybershujin/prompt-injection-in-the-wild
Tracker of publicly reported prompt-injection techniques, broken down by delivery method, encoding, and propagation behavior, with confirmed models,…
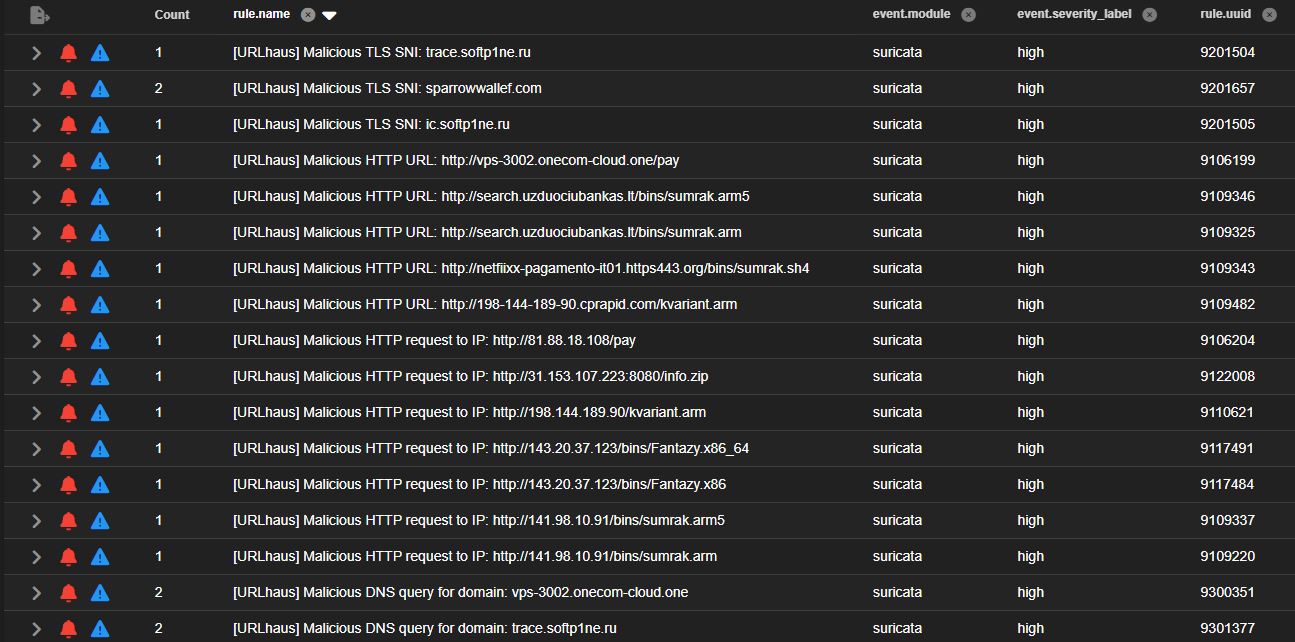 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 the-art-of-hacking/h4cker
Curated collection of cybersecurity resources, labs, and training materials covering ethical hacking, penetration testing, exploit development,…