

threat-intel
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
defensive-toolsintrusion-detectionioc-management+4
37510 days ago
volexity/threat-intelSignatures and IoCs from public Volexity blog posts.
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 emergingthreats/threatresearch
Proofpoint - Emerging Threats - Threat Research tools + publicly shared intel and documentation
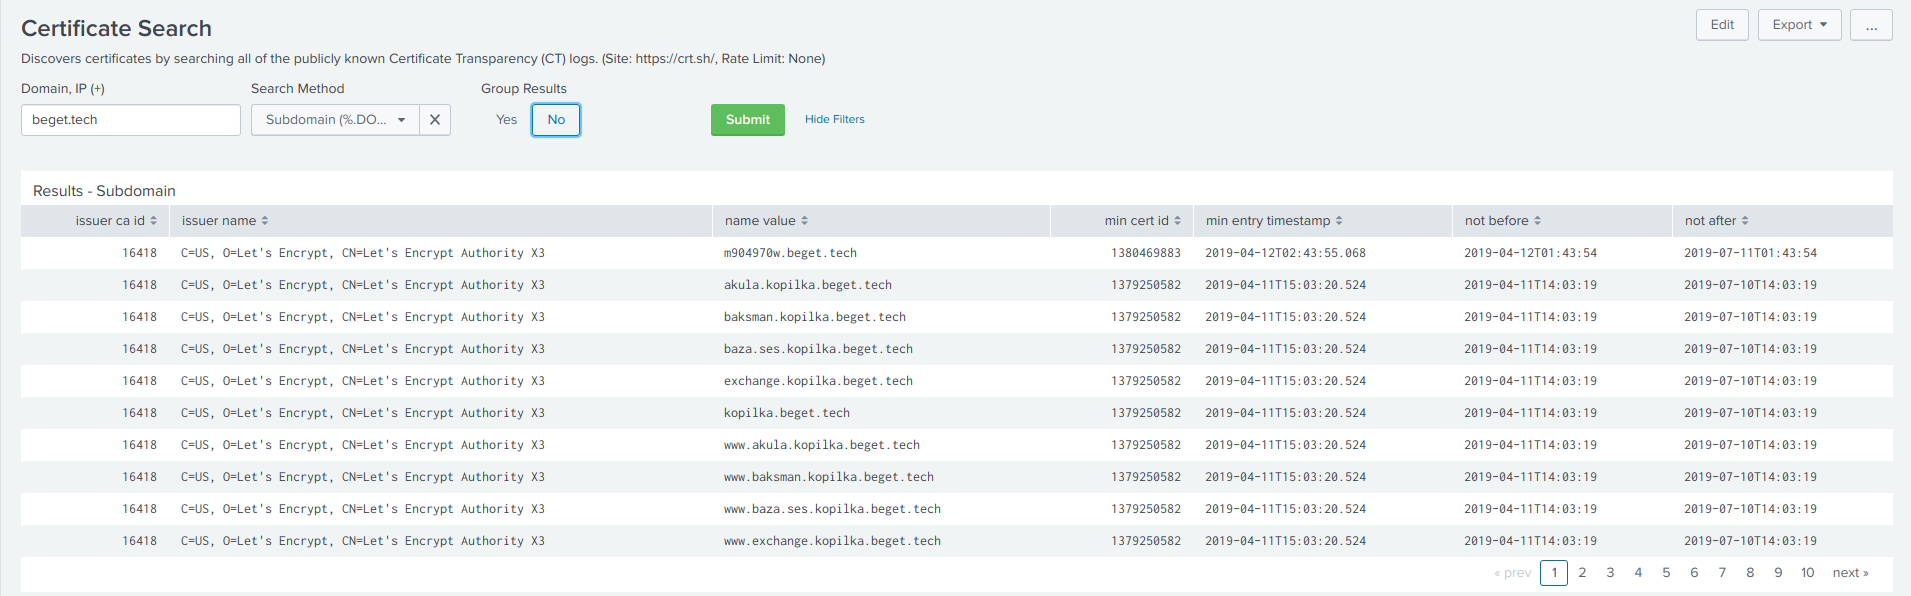 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
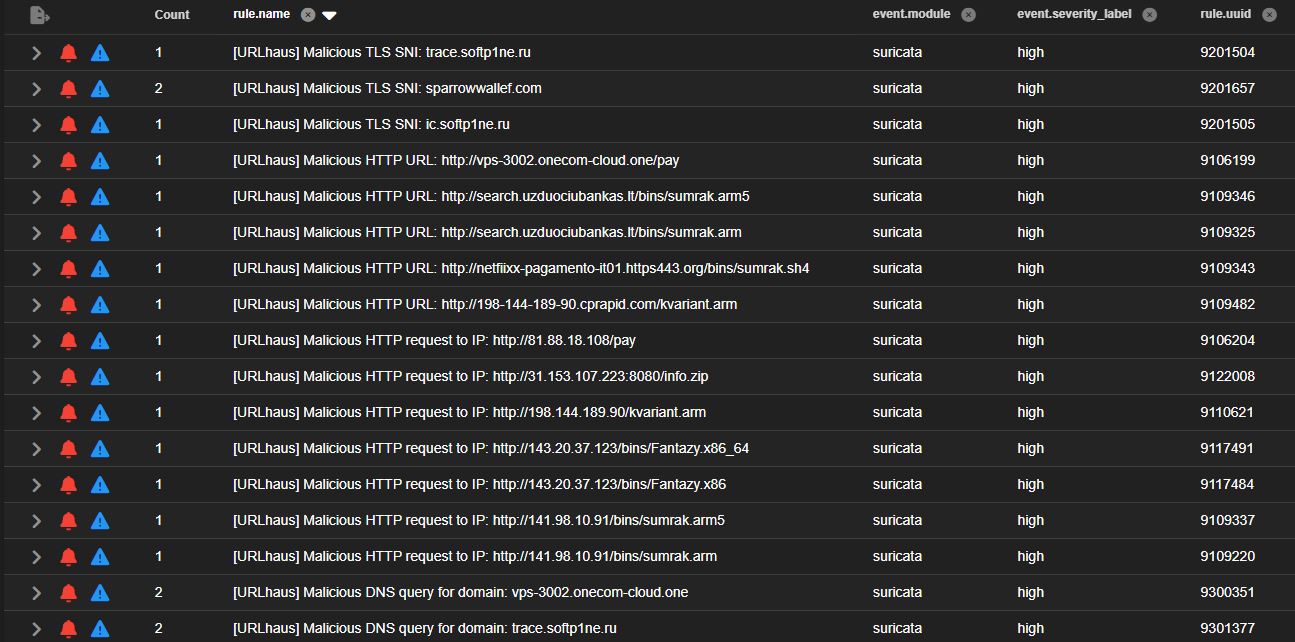 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 rollwagen/abusech
CLI client for abuse.ch
 renat0z3r0/notepadpp-supply-chain-iocs
IoCs and detection rules for the Notepad++ supply chain attack (CVE-2025-15556) — Lotus Blossom APT, June–December 2025. Includes Falcon LogScale…
 watchguard-threat-lab/log4shell-iocs
A collection of IOCs for CVE-2021-44228 also known as Log4Shell
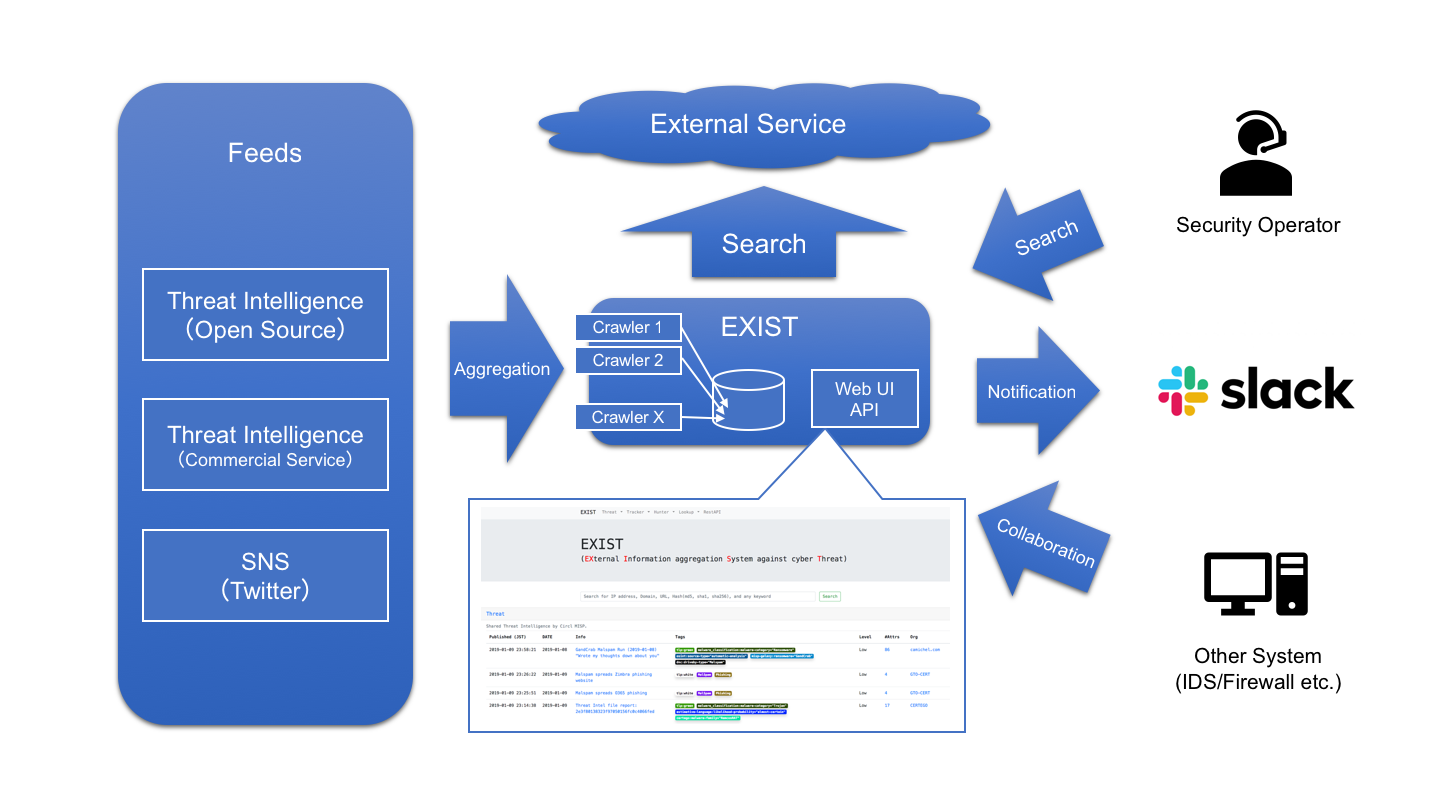 nict-csl/exist
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

 securewithumer/exploit-index
Zero-API aggregator indexing 150k+ CVE exploits and PoCs from Exploit-DB, Nuclei, Metasploit, and CISA KEV, with EPSS/CVSS risk scoring for threat…
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits