
ThreatKB
 inquest/threatkb
Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
information-gatheringioc-managementmalware-analysis+2
104
inquest/threatkbKnowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 xghst0/reconkg
Vulnerability triage with provenance. Resolves CVEs from locally built corpora (NVD/KEV/EPSS, ExploitDB, nmap script.db) and emits verification…
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 xakepnz/enterpriseattack
A lightweight Python module to interact with the [MITRE ATT&CK®](https://attack.mitre.org/) Enterprise dataset. Built for speed with minimal…
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
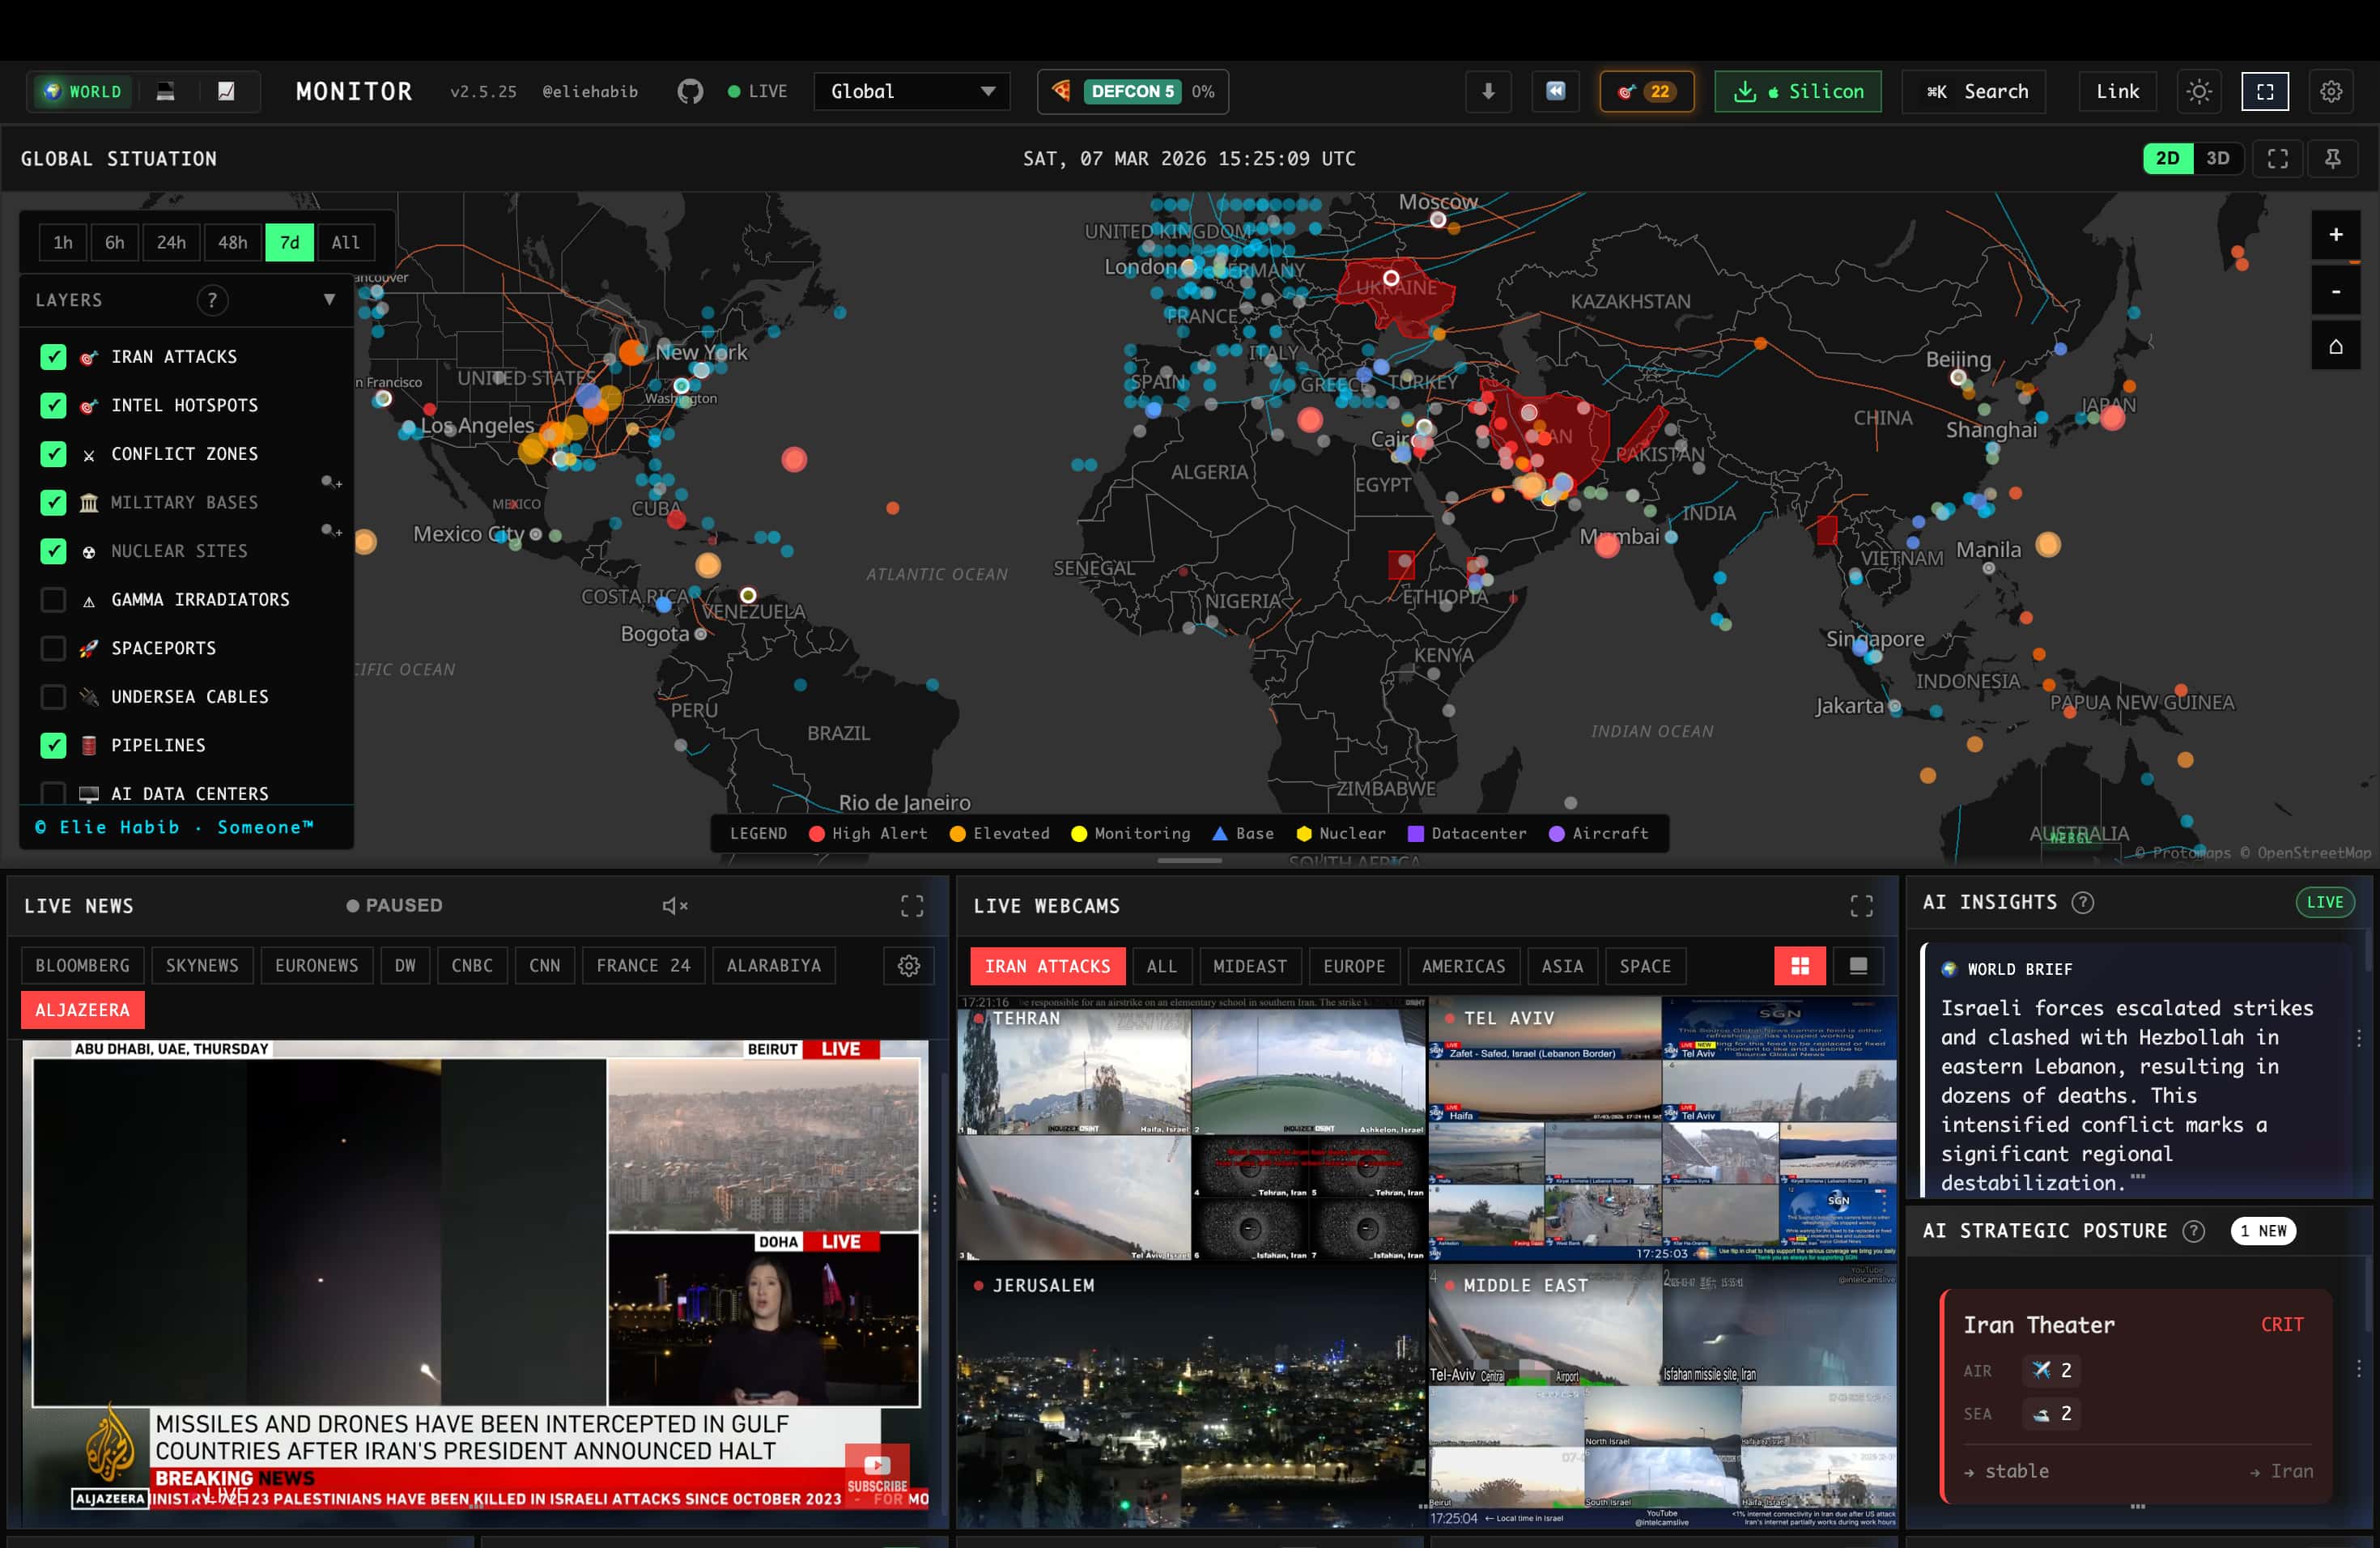 koala73/worldmonitor
Real-time global intelligence dashboard. AI-powered news aggregation, geopolitical monitoring, and infrastructure tracking in a unified situational…
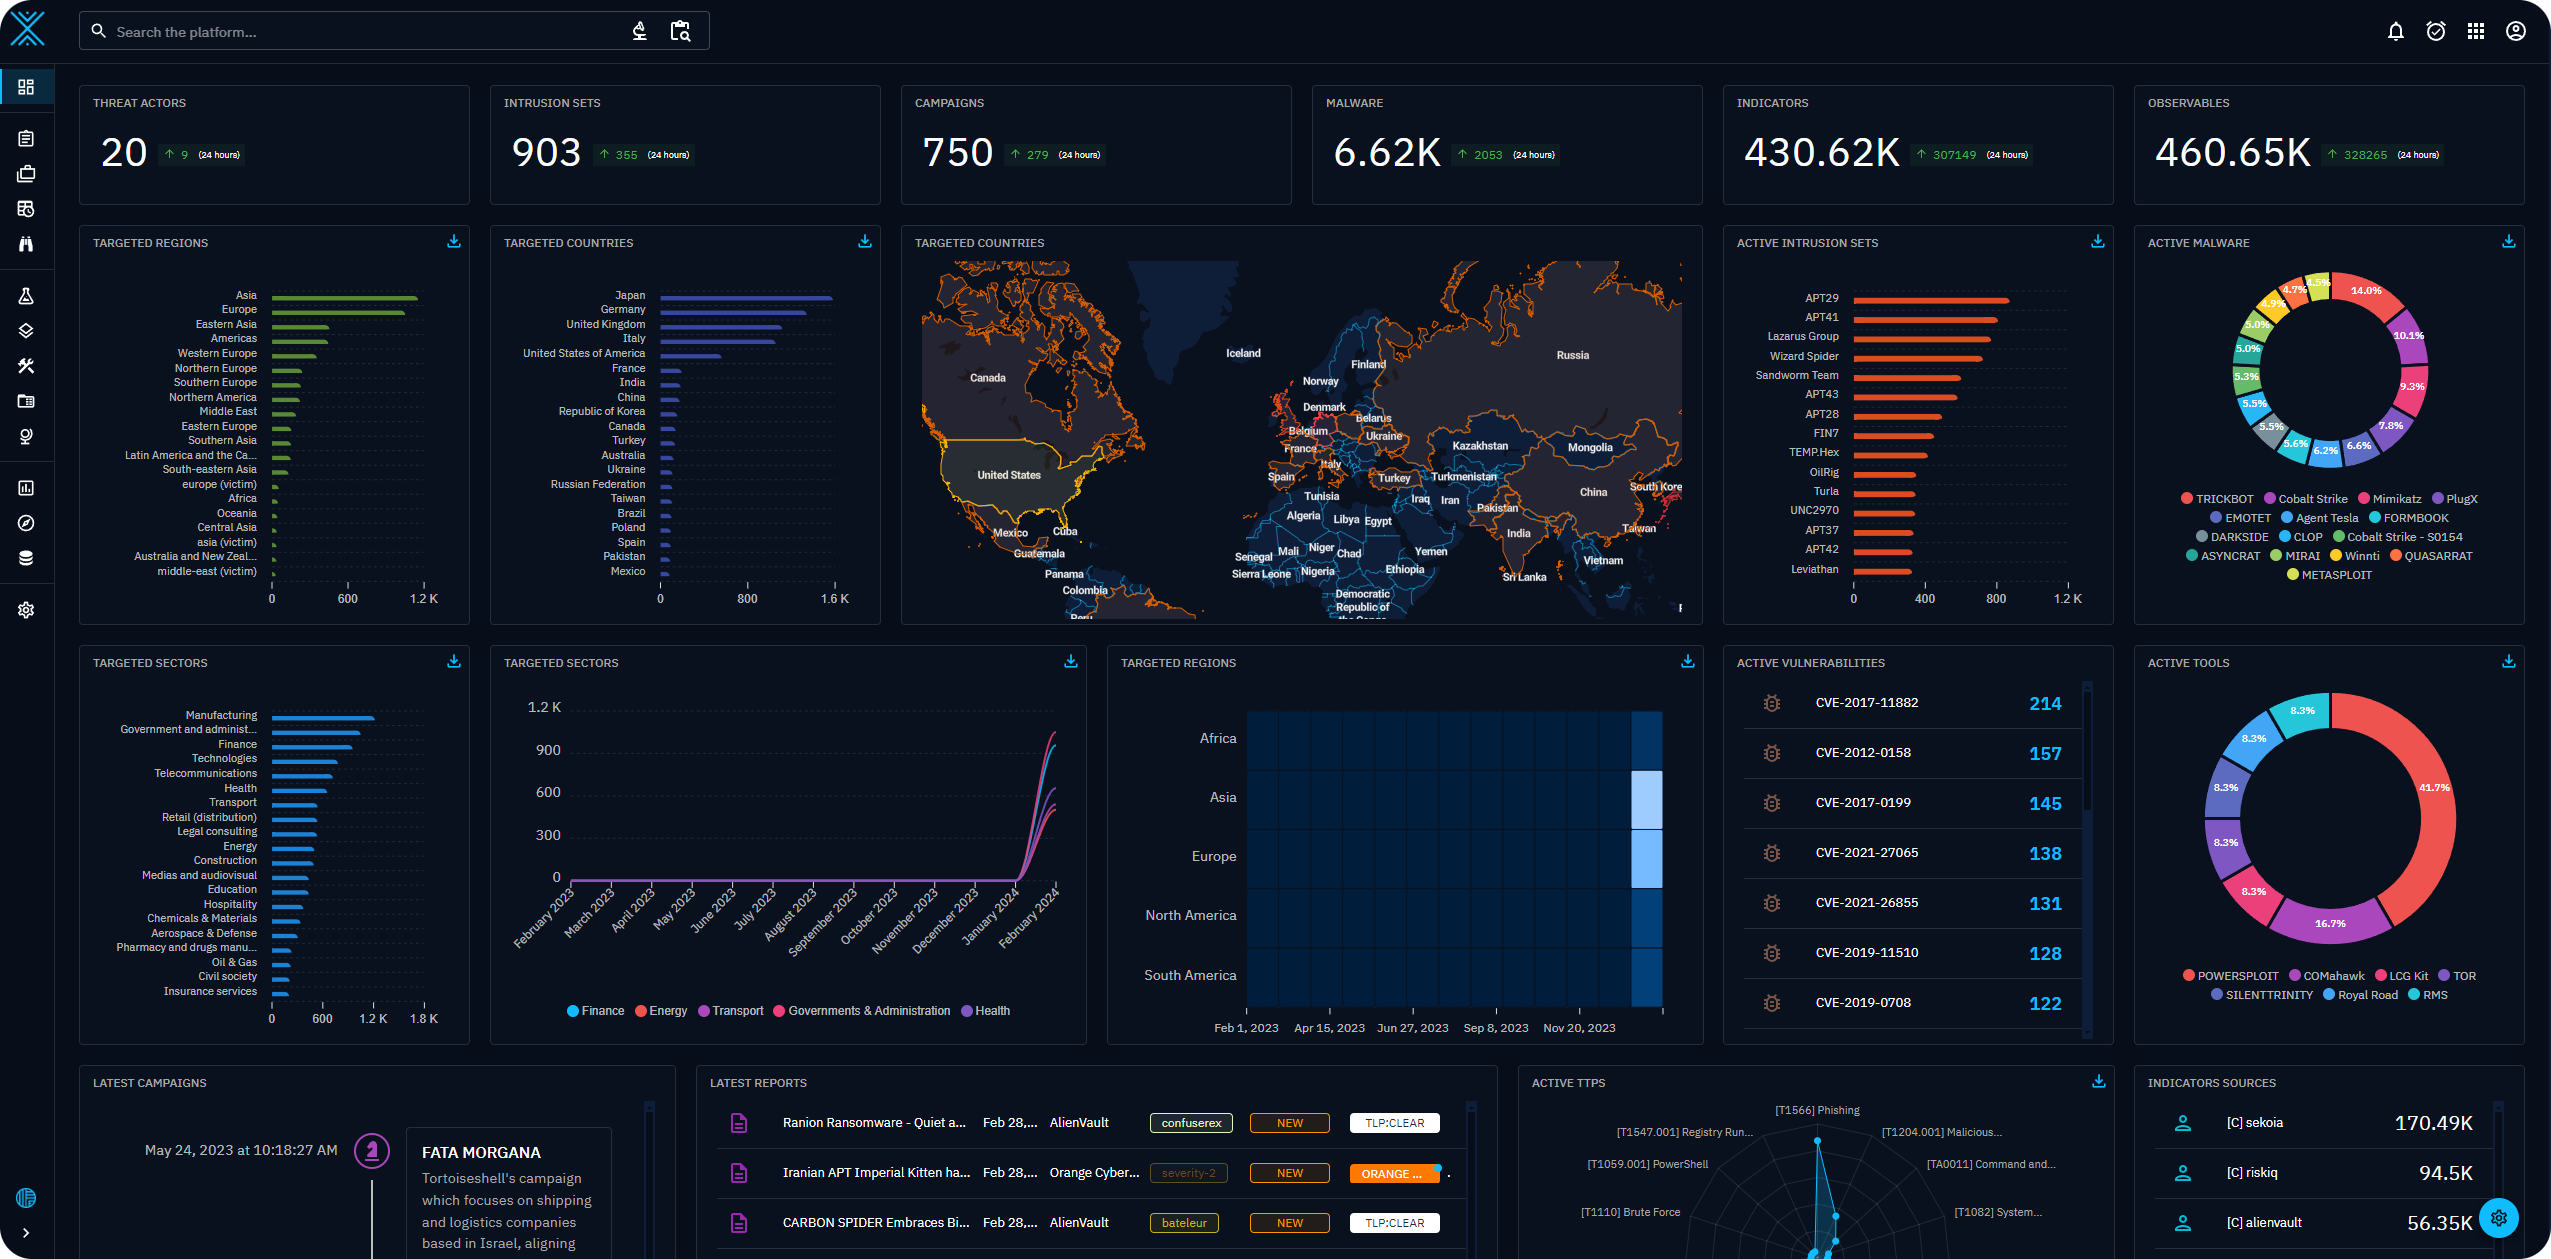 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 ransomlook/ransomlook
Yet another Ransomware gang tracker
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…