
Exploit-Index
 securewithumer/exploit-index
The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat…
curated-resourcesexploitationinformation-gathering+8
64
securewithumer/exploit-indexThe Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat…
 rootless-ghost/vulnforge
Vulnerability & exploit intelligence — ExploitDB, NVD, Metasploit search with CVE→ATT&CK mapping and LogNorm/HuntForge integration | Part of Nebula…
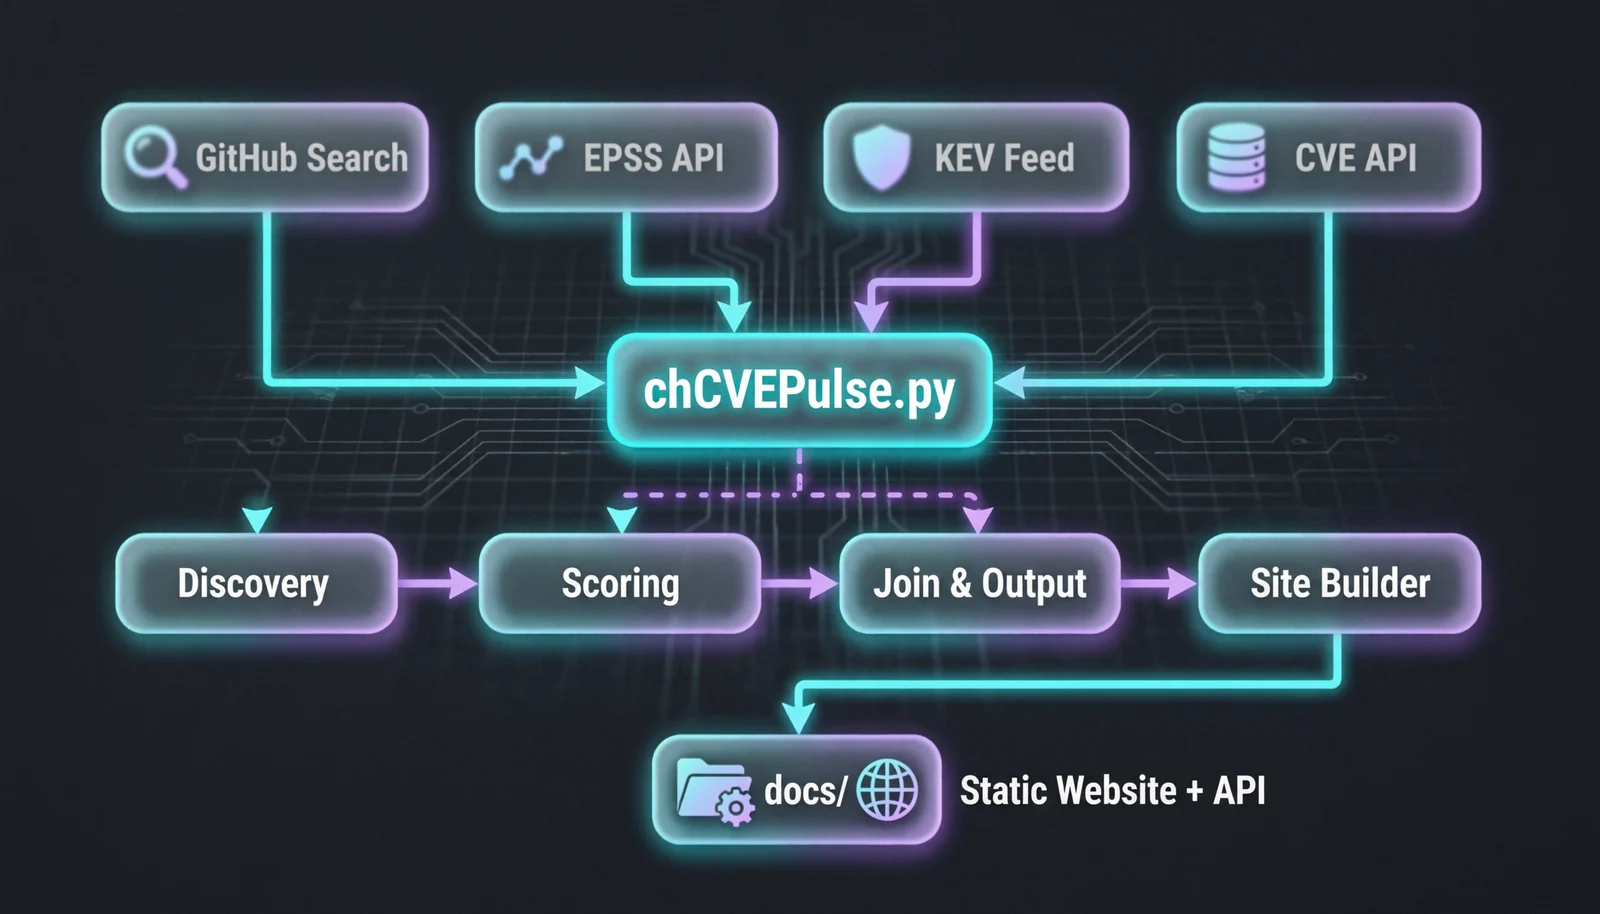 ch4120n/ch4120n-cve-pulse
Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
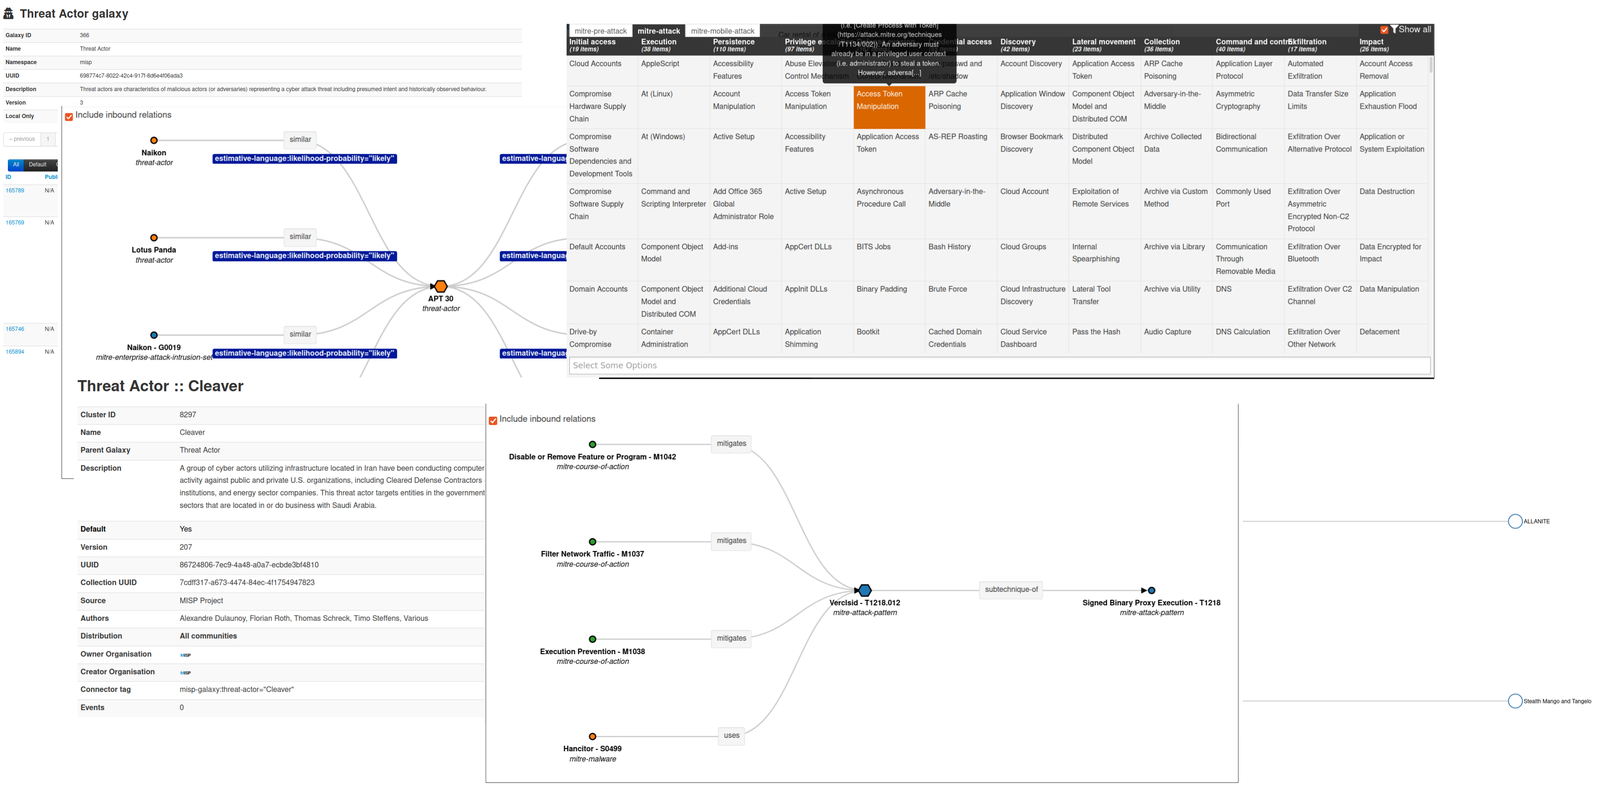 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
 bushidouk/abused-legitimate-services
Cloud, CDN, and marketing services leveraged by cybercriminals and APT groups
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 bushidouk/ransomware-tool-matrix
A resource containing all the tools each ransomware gangs uses

 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
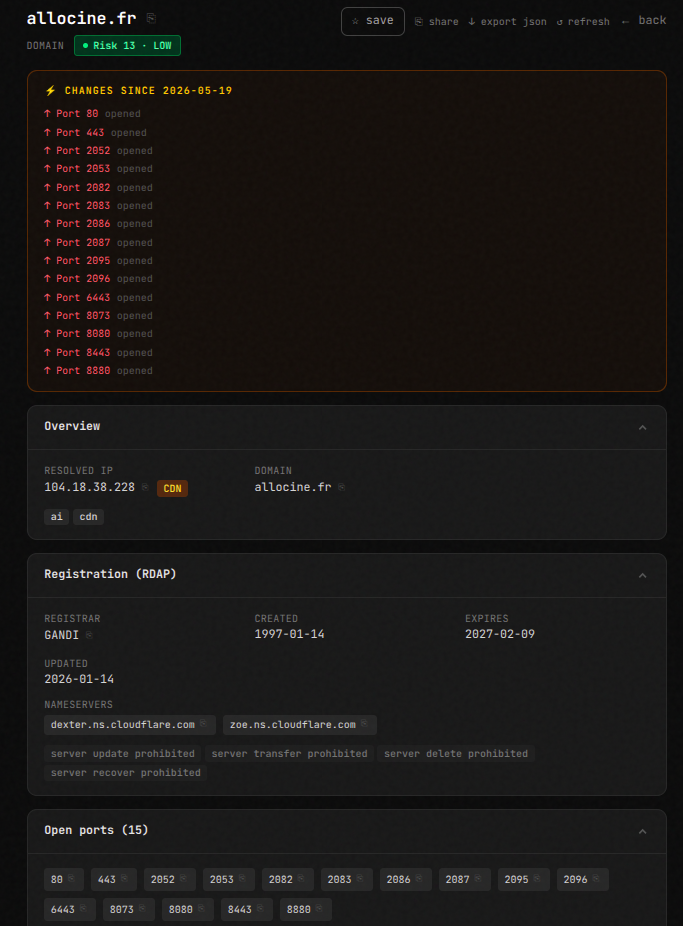 teycir/seekyou
OSINT intelligence on any IP, domain, or ASN

 functori/argos/argos
Analysis and Representation of Graphs of Suspicious Operations (Analyse et Représentation des Graphes des Opérations Suspectes)
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 watchguard-threat-lab/log4shell-iocs
A collection of IOCs for CVE-2021-44228 also known as Log4Shell
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…