
osiris
 simplifaisoul/osiris
Open Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
dns-analysisinformation-gatheringnetwork-mapping+7
11.4k
simplifaisoul/osirisOpen Source Global Intelligence Platform - Real-Time OSINT Dashboard - A Palantir Alternative - …
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 magicsword-io/lolrmm
Curated catalog of Remote Monitoring and Management tools abused by threat actors, with YAML profiles, Sigma detection rules, and API access for…
 cisagov/kev-data
Mirrors CISA's Known Exploited Vulnerabilities (KEV) catalog as CSV and JSON with a JSON schema, enabling programmatic access and commit-history…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 intelowlproject/intelowl
Scalable threat intelligence platform that enriches observables and files using 200+ analyzers, with built-in GUI, REST API, and automated workflows…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…

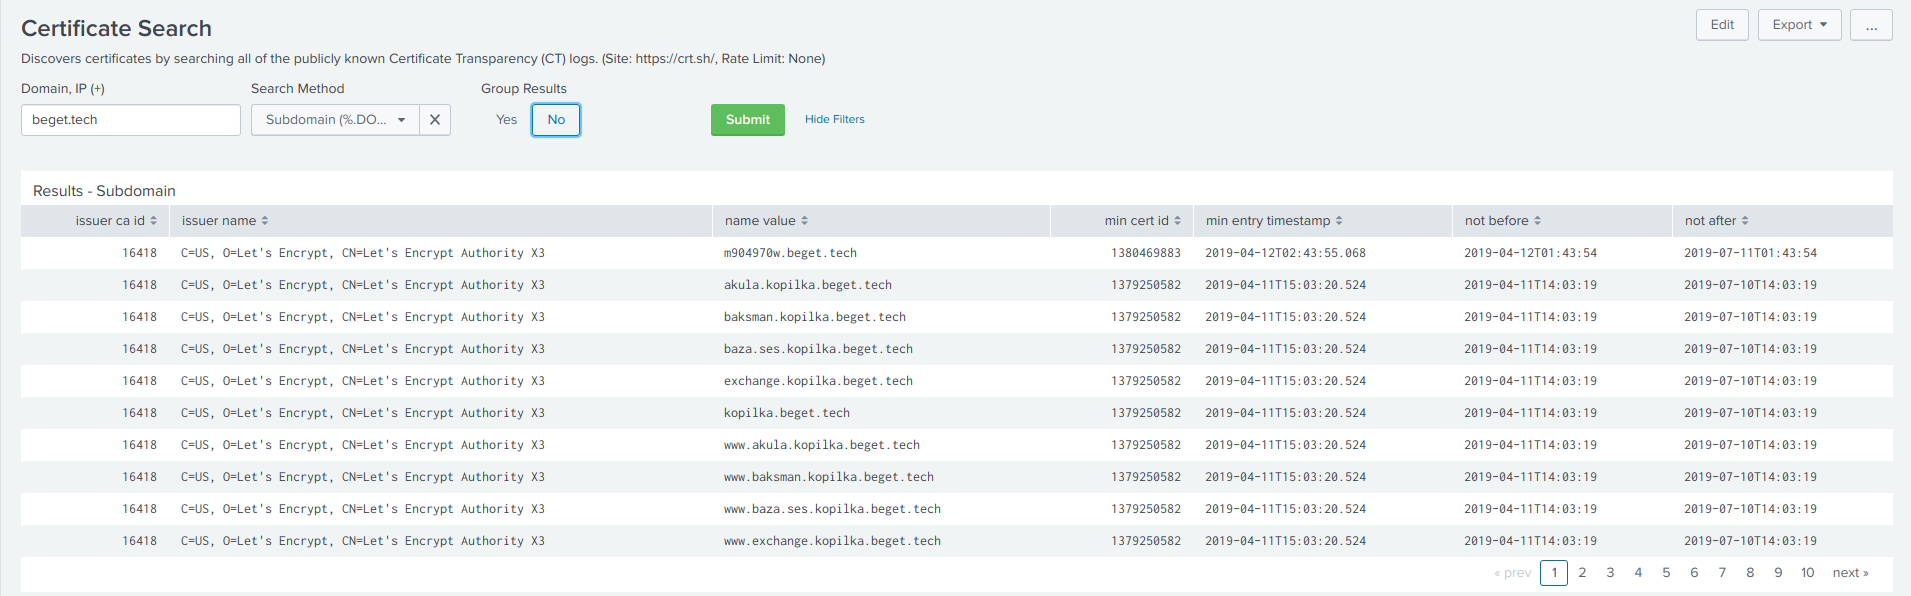 ecstatic-nobel/osweep
Don't Just Search OSINT. Sweep It.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 montysecurity/c2-tracker
Live Feed of C2 servers, tools, and botnets
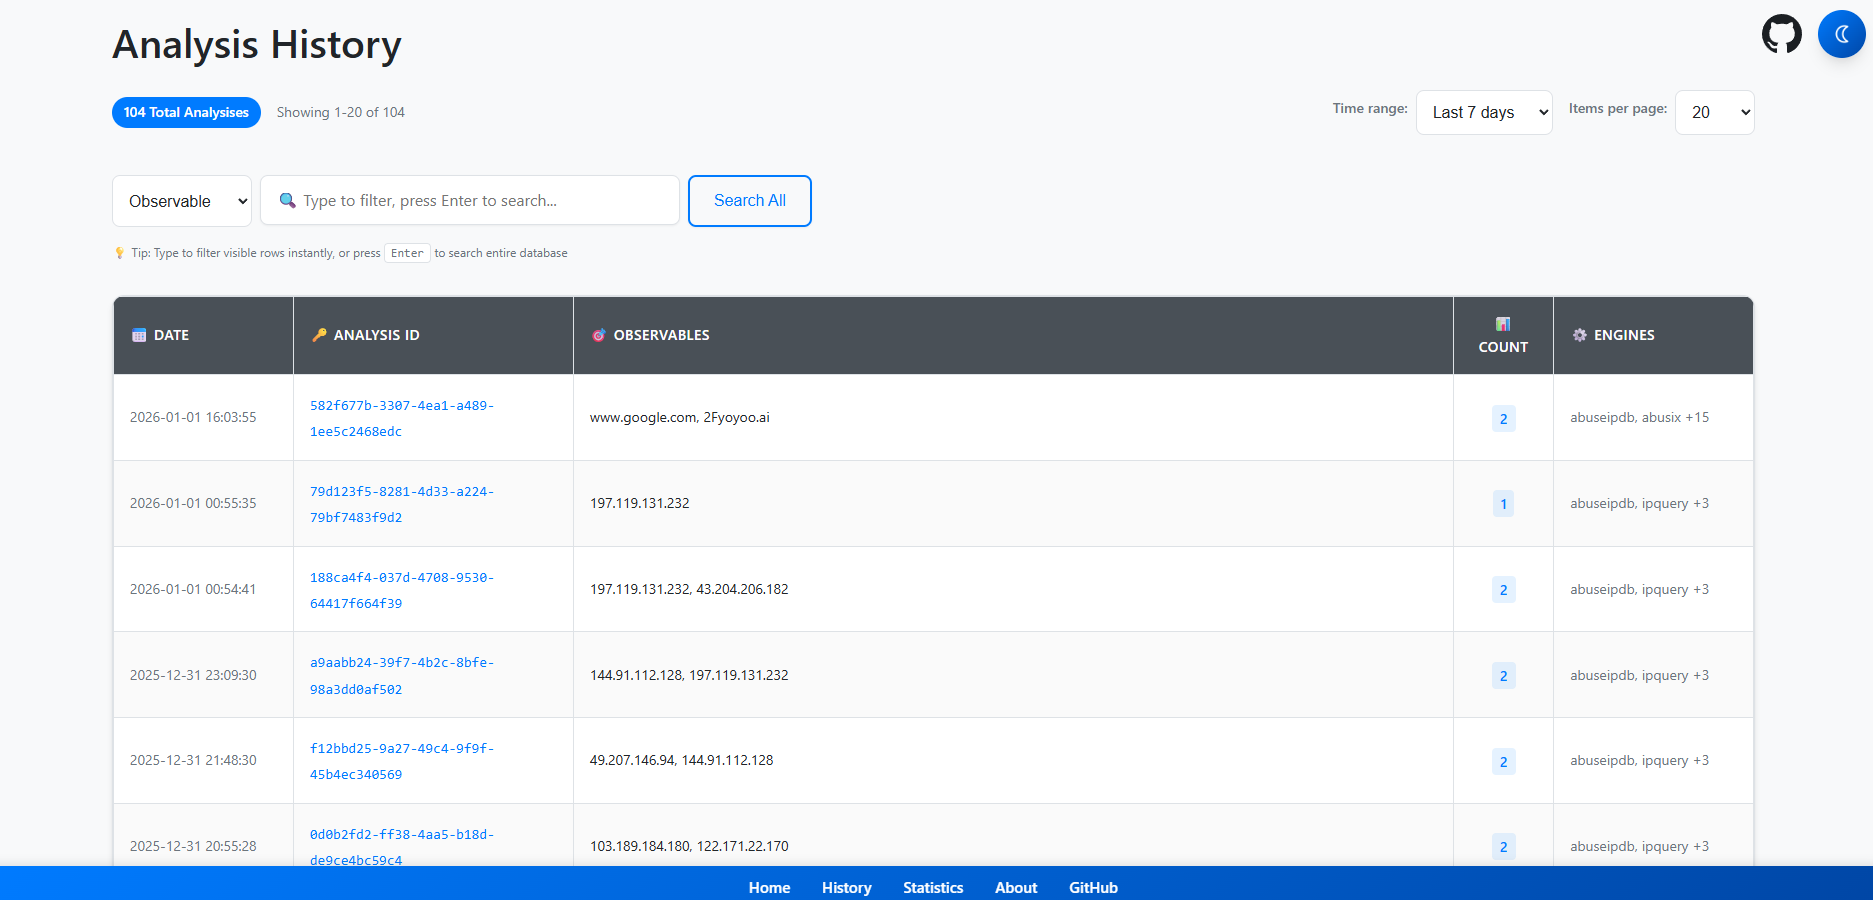 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 hurricanelabs/machinae
Automated security intelligence collector that queries public feeds and APIs for threat data on IPs, domains, URLs, hashes, and SSL fingerprints,…