

CVE-2024-3094-checker
 fabiobaroni/cve-2024-3094-checker
Quick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
educationscripting-automationsupply-chain-security+2
fabiobaroni/cve-2024-3094-checkerQuick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
 rohitberiwala/nodejs-tar-symlink-exploit-cve-2026-29786
Technical analysis and Proof-of-Concept (PoC) for a critical Path Traversal vulnerability via Symlink manipulation in the Node.js 'tar' package…
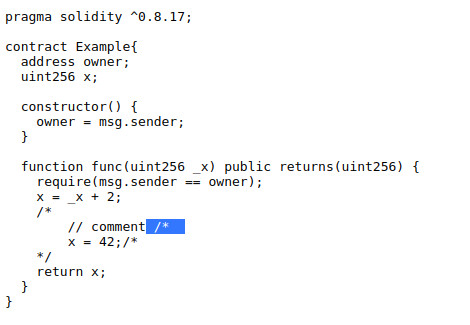 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 otakuliu/cve-2026-22807_range
Educational Python target range simulating CVE-2026-22807, an AI supply chain RCE via TOCTOU in model loading. Includes vulnerable library, PoC…
 ahmedreda38/cve-2025-47273-poc
CVE-2025-47273 is a high-severity path traversal vulnerability in the setuptools library ,specifically version 78.1.0 .
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 george0papasotiriou/cve-2026-22018-jenkins-pipeline-shared-library-code-execution-via-grab-
PoC for CVE-2026-22018, a critical Jenkins Pipeline Shared Library RCE via Groovy @Grab, demonstrating supply-chain code injection and mitigation…
 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
 gouldnicholas/cve-2026-7669-poc
PoC for CVE-2026-7669: SGLang silent trust_remote_code override -> RCE
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 amalmurali47/hook
Hook for the PoC for exploiting CVE-2024-32002
 grassplatypus/cve-2026-45033-class
CVE-2026-45033 PoC for Claude Code, not Github Copilot. Worked for Haiku 4.5.
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 hexbornestudio/atlas-tj-actions-poc
PoC for CVE-2025-54416 tj-actions/branch-names command injection
 rusakovichma/cve-2019-10172
CVE-2019-10172 PoC and Possible mitigations
 0x3a/cve-2014-4936
Repository for CVE-2014-4936 POC code.