tharindudh-Log4j-Vulnerability-in-Ghidra-tool-CVE-2021-44228

Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…

Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…

Cargo exploit from CVE-2023-38497

Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…

Protect against malicious code installed via npm, yarn, pnpm, npx, pnpx, pip, uv and poetry with Aikido Safe Chain. Free to use, no tokens required.

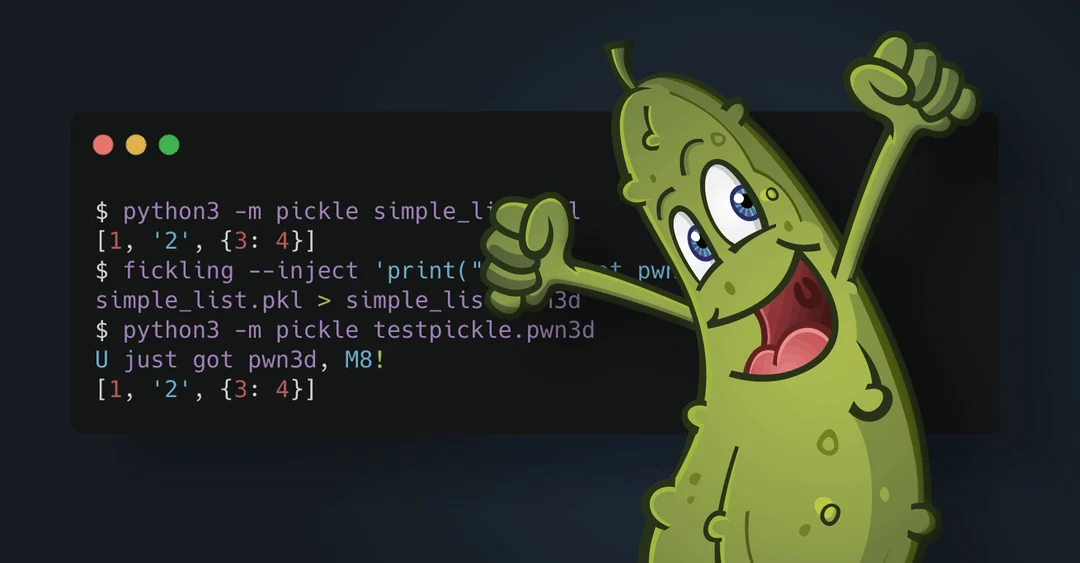
A Python pickling decompiler and static analyzer

Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…

JavaScript & Node.js open-source SAST scanner. A static analyser for detecting most common malicious patterns 🔬.

TPM Genie is an I2C bus interposer for discrete Trusted Platform Modules

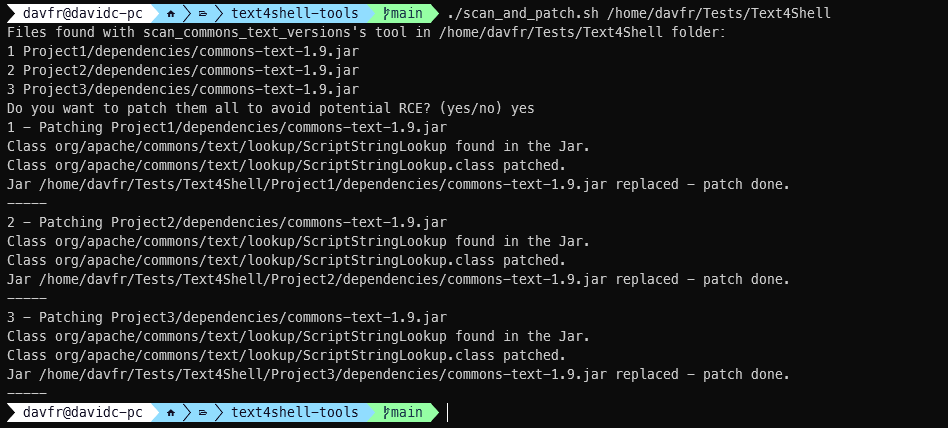
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…

Proof-of-concept code for Android APEX key reuse vulnerability

Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations

Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…

Documented security vulnerabilities in the FatFs embedded filesystem library with CVE details, fuzzing harness, exploit disk-image generator, and…

Detections for CVE-2021-44228 inside of nested binaries

GNU IFUNC is the real culprit behind CVE-2024-3094

Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)

a systems programming language prioritizing verifiable correctness, determinism, and performance

Source code for the Binaries of OWASP WrongSecrets