

DevSecOpsGuideline
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
api-securitycloud-securitycontainer-security+6
owasp/devsecopsguidelineThe OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 jeremylong/dependencycheck
The dependency-check repository has moved:
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 pathakabhi24/llm-mcp-security-field-guide
The most comprehensive LLM + MCP security guide i.e. OWASP aligned, real CVEs, actionable checklists
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
 dependencytrack/dependency-track
Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
 cdxgen/cdxgen
Creates CycloneDX Bill of Materials (BOM) for your projects from source and container images. Supports many languages and package managers. Integrate…
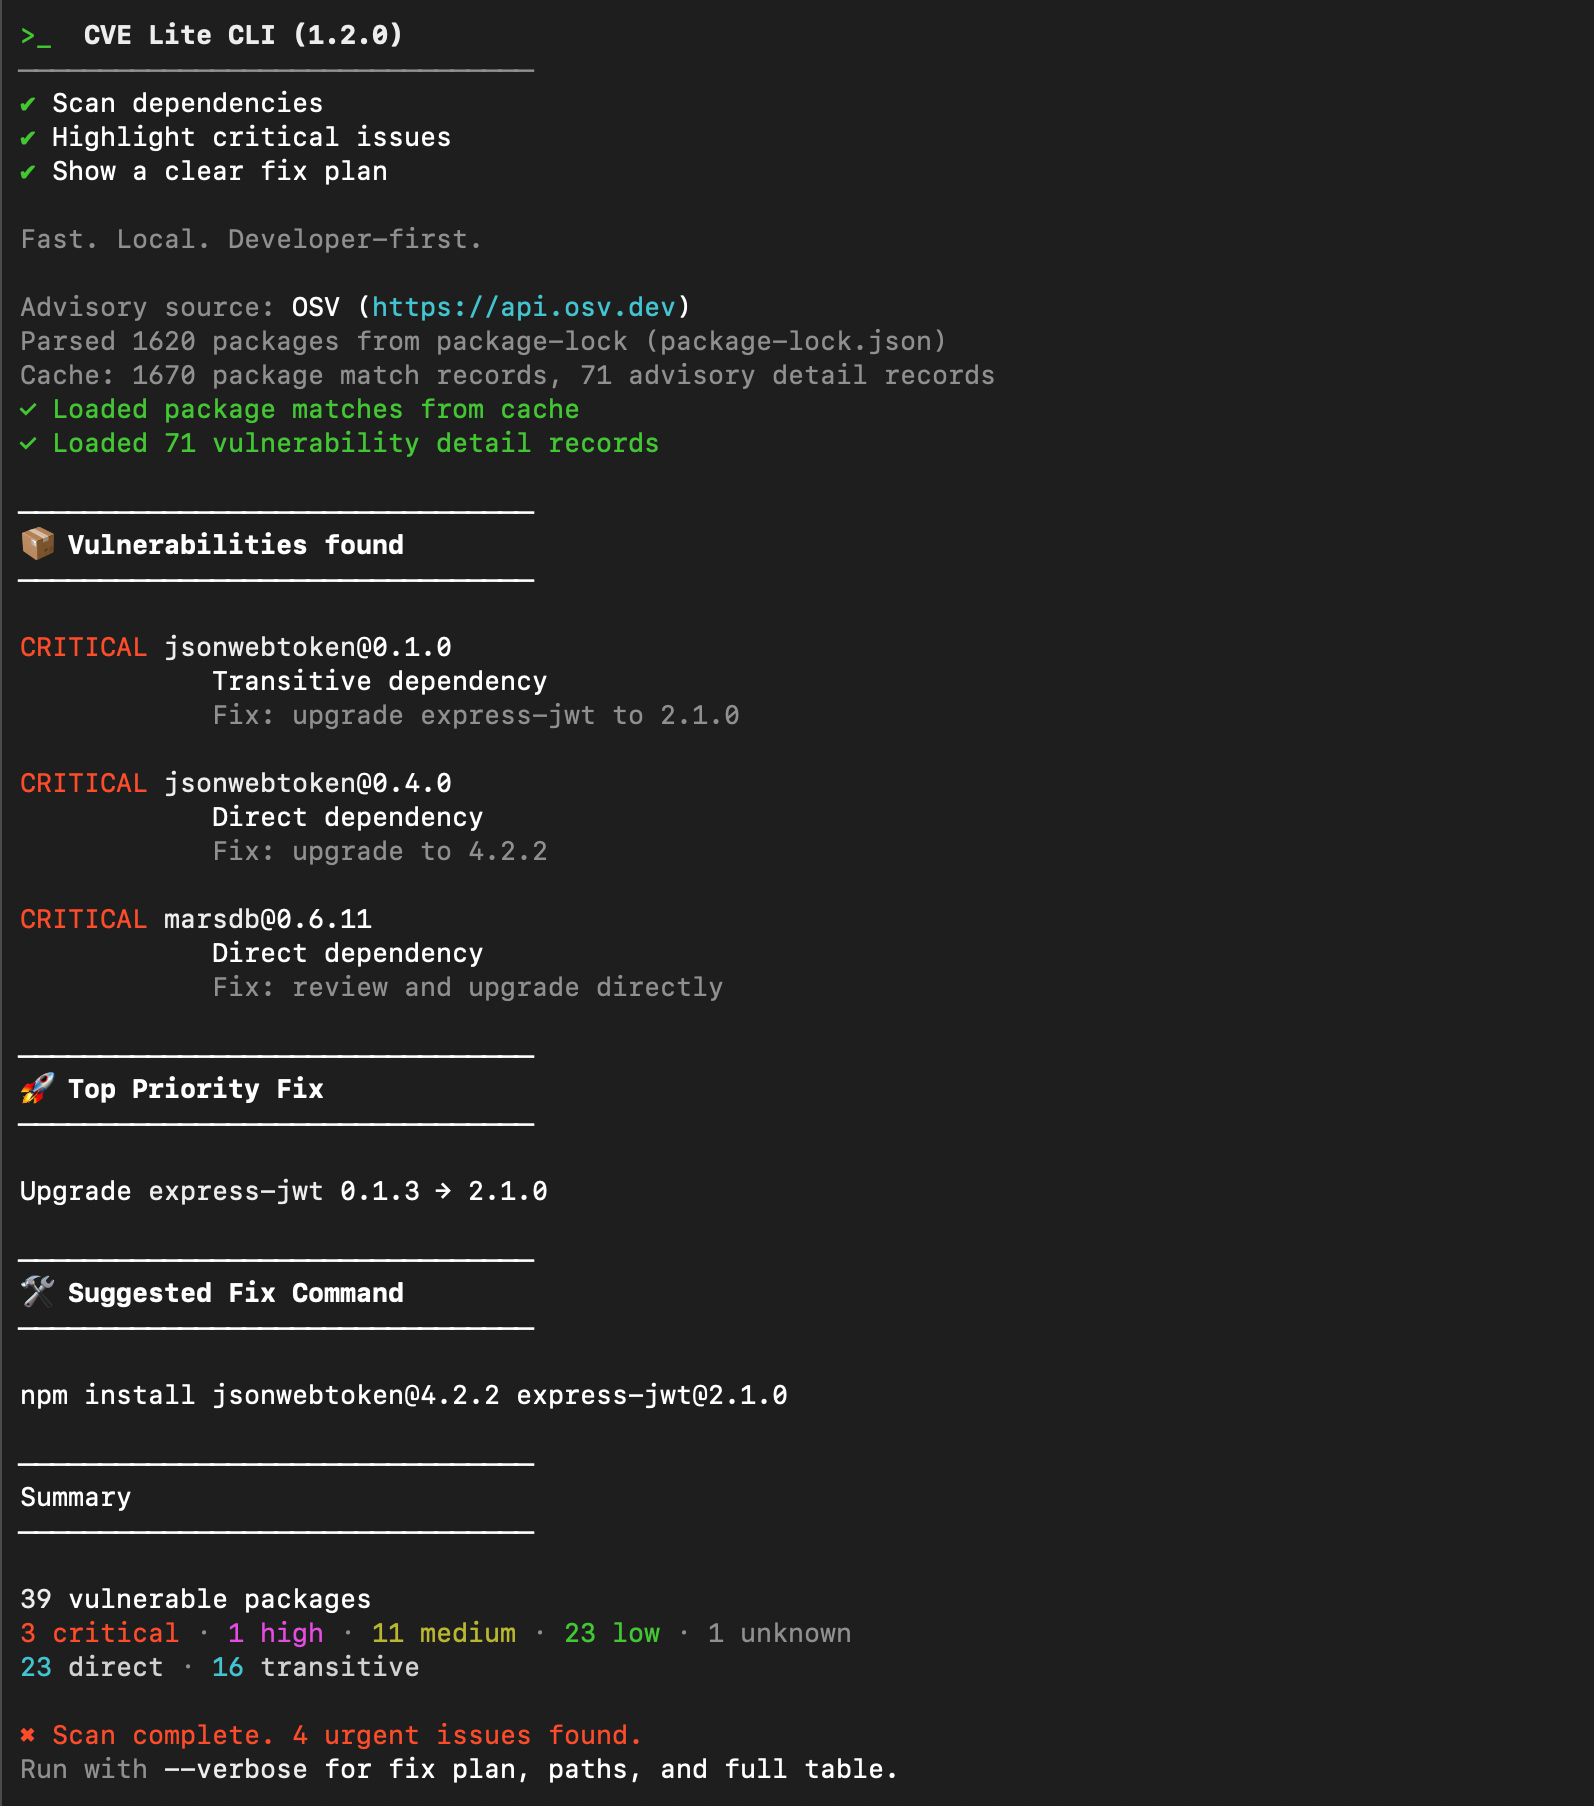 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
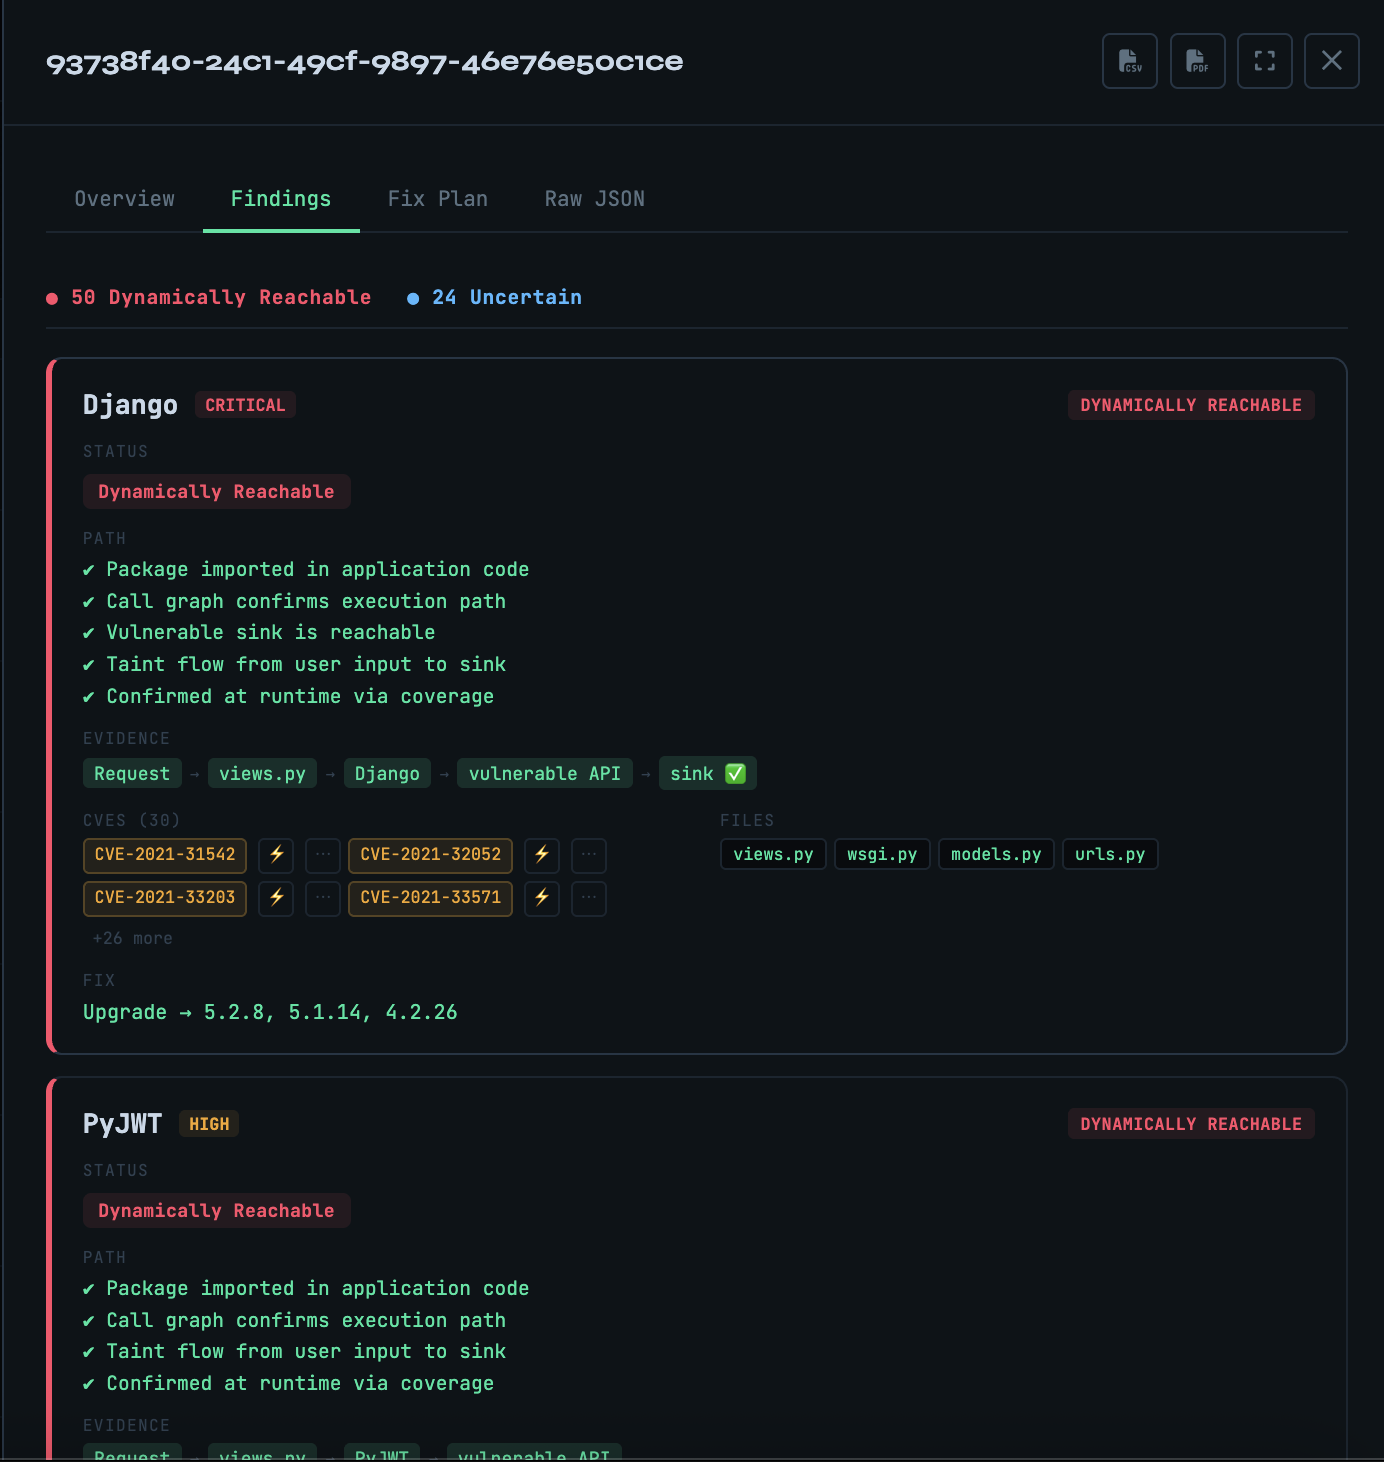 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…