
gitleaks
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
code-analysisdevsecopssecret-detection+3
29.4k
gitleaks/gitleaksFast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 jedisct1/minisign
A dead simple tool to sign files and verify digital signatures.
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
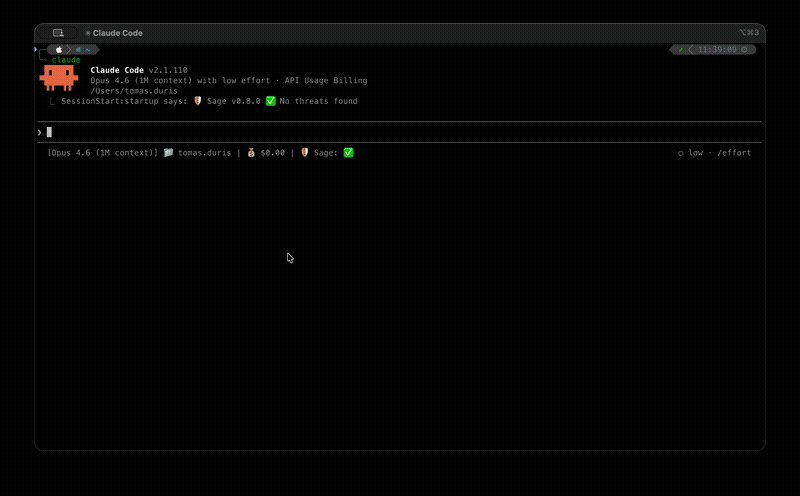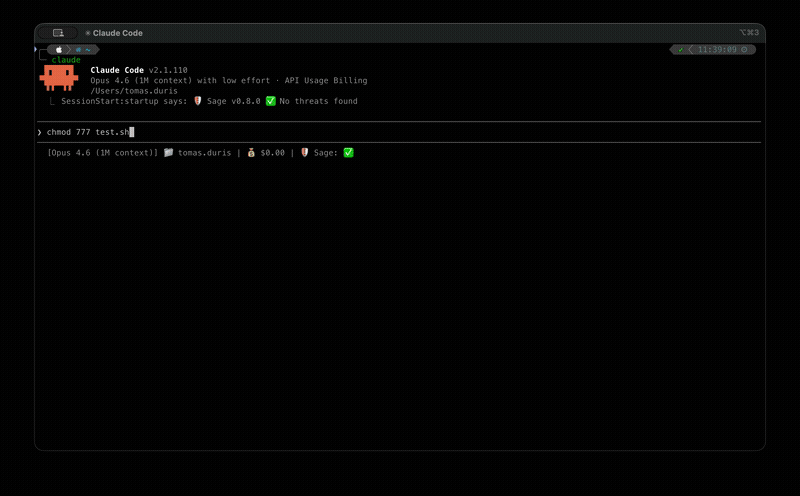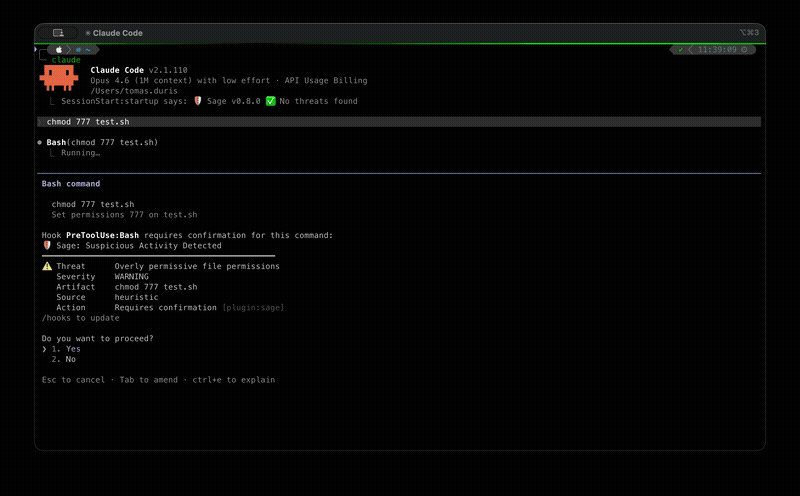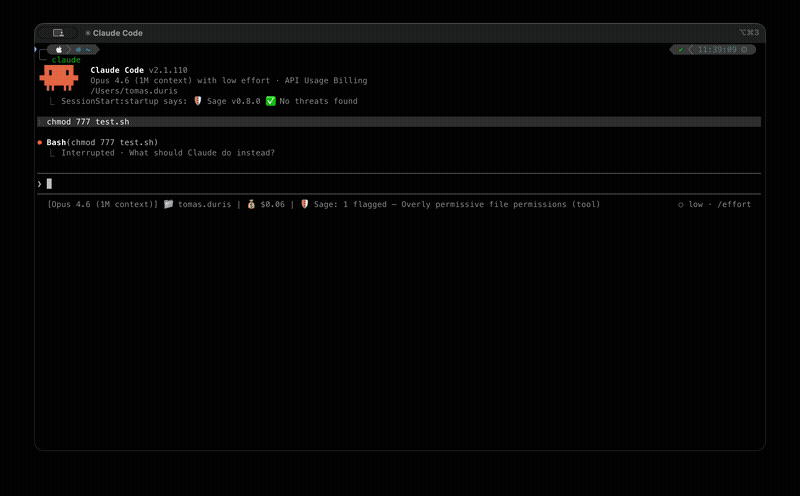 gendigitalinc/sage
Lightweight Agent Detection & Response (ADR) layer for AI agents — guards commands, files, and web requests. Part of Gen Agent Trust Hub.
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 promptfoo/modelaudit
Security scanner for AI/ML model files. Detects malicious code, backdoors, and vulnerabilities before deployment
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.
 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
 1lann/log4shelldetect
Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…
 simplylu/cve-2021-42694
Generate malicious files using recently published homoglyphic-attack (CVE-2021-42694)
 zjuicsr/deeptrap
Security benchmark for evaluating OpenClaw agents against adversarial execution contexts including poisoned files, injected skills, misleading tool…
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
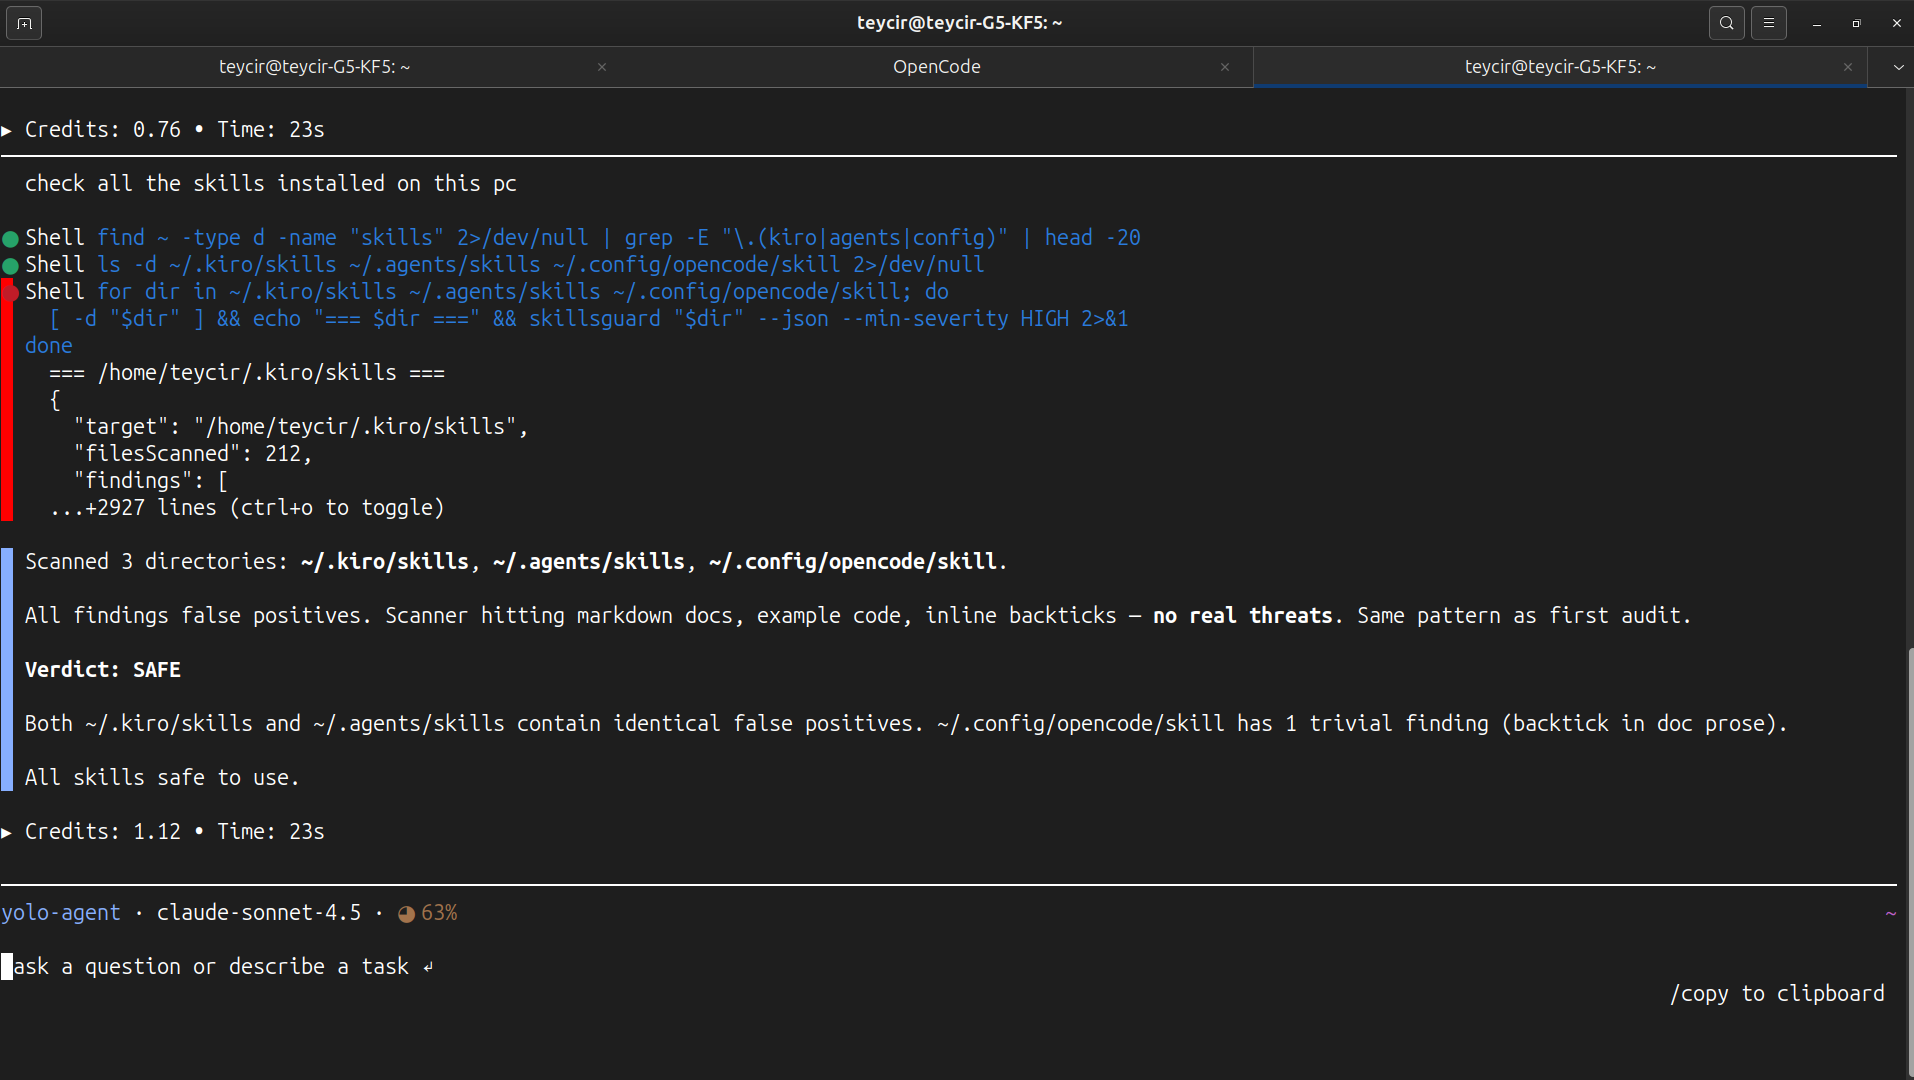 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 aquasecurity/binfinder
Find binary files not installed through package manager
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…