
openclaw-security-monitor
 adibirzu/openclaw-security-monitor
Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
defensive-toolseducationforensics+9
48
adibirzu/openclaw-security-monitorProactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 ny1024/clawguard
Modular security toolkit for autonomous agents providing static analysis, configuration auditing, runtime monitoring, and supply chain verification…
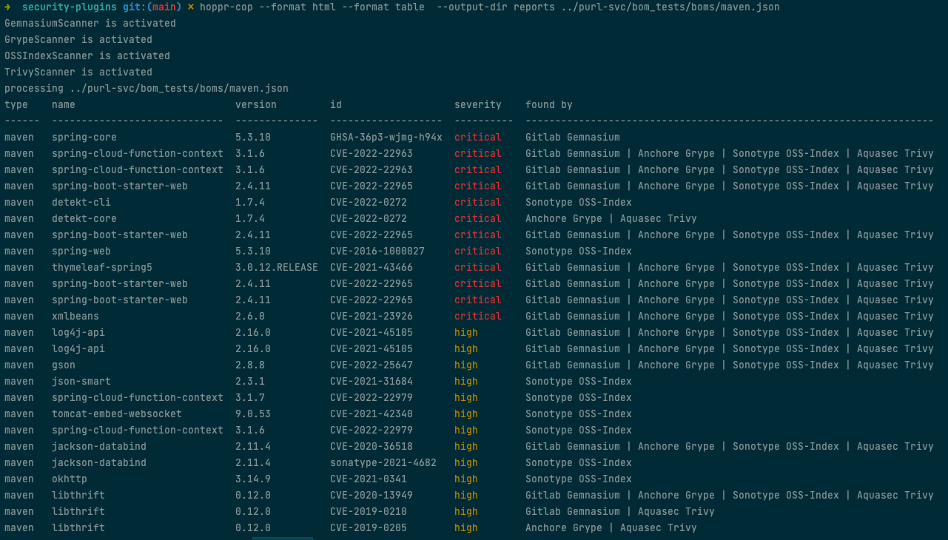
 hoppr/hoppr-cop
Aggregates vulnerability data from multiple databases into CycloneDX SBOMs, generating deduplicated VEX, HTML, and GitLab-compatible reports for…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…