
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
106 results
aura preview

aura

GitHubsourcecode-ai/aura

Python source code auditing and static analysis on a large scale
code-analysiseducationmalware-analysis+4
4933 years ago
CVE-2025-9267 preview

CVE-2025-9267

GitHubtiger3080/cve-2025-9267

Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…

binary-exploitationexploitationprivilege-escalation+2
1 year ago
cve-2018-6574-exploit preview

cve-2018-6574-exploit

GitHubzerbaliy3v/cve-2018-6574-exploit

CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…

exploitationpayload-generationsupply-chain-security+2
2 years ago
go-get-RCE preview

go-get-RCE

GitHubsaptaktdk/go-get-rce

This is the exploit of CVE-2018-6574: go get RCE
exploitationpayload-generationpenetration-testing+2
1 year ago
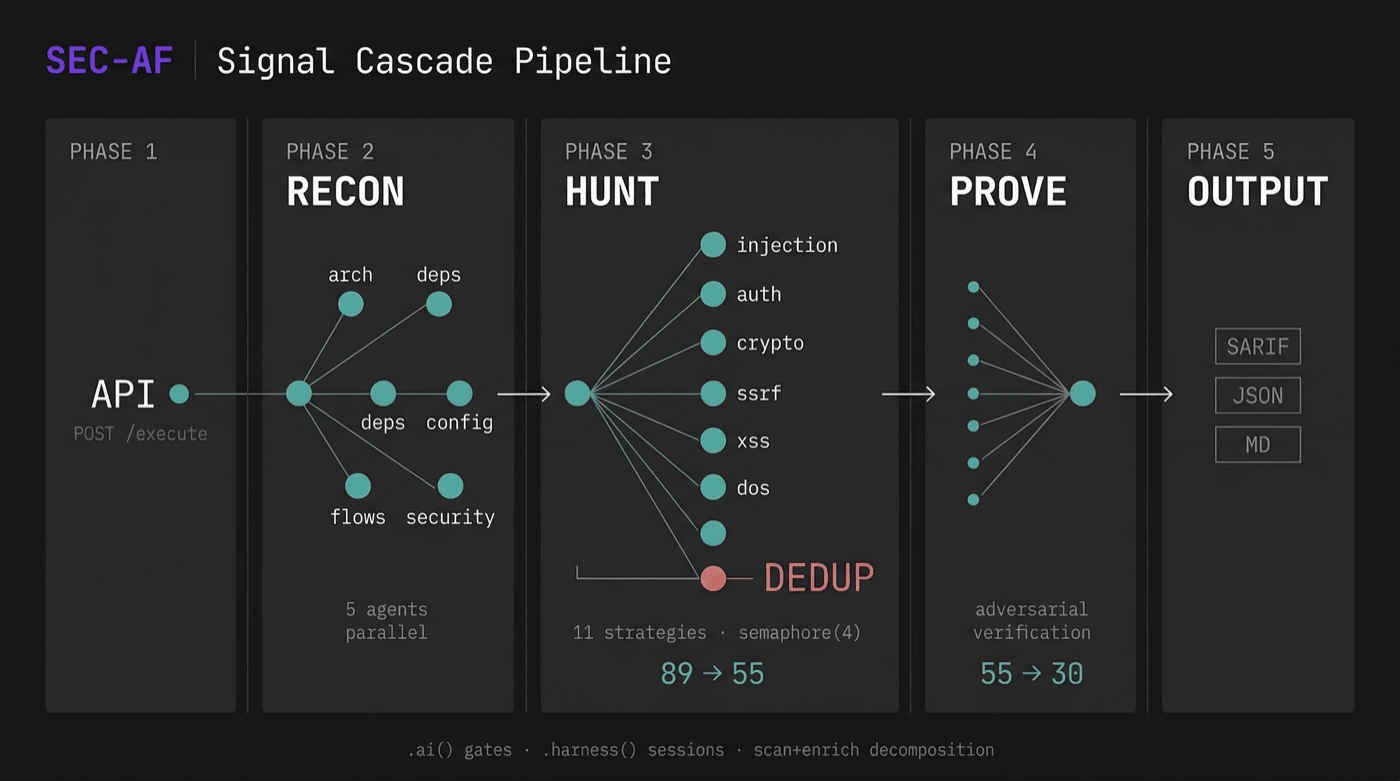
sec-af preview

sec-af

GitHubagent-field/sec-af

AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.

ai-securitycode-analysisdevsecops+7
1991 month ago
node9-proxy preview

node9-proxy

GitHubnode9-ai/node9-proxy

Access control for AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run,…
ai-securitycloud-securitycommand-and-control+7
2173 days ago
glassworm-hunter preview

glassworm-hunter

GitHubafine-com/glassworm-hunter

Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
code-analysisdevsecopseducation+9
304 months ago
CVE-2021-26700 preview

CVE-2021-26700

GitHubjackadamson/cve-2021-26700

Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
code-analysiseducationexploitation+3
205 years ago
CVE-2024-24590 preview

CVE-2024-24590

GitHubjunnythemarksman/cve-2024-24590

Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
exploitationpayload-generationpenetration-testing+3
12 years ago
CVE-2026-5817-PoC preview

CVE-2026-5817-PoC

GitHubgouldnicholas/cve-2026-5817-poc

Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
ai-securitycontainer-escapecontainer-security+4
4 months ago
deepsec preview

deepsec

GitHubvercel-labs/deepsec

Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
ai-securitycode-analysisdevsecops+5
8.1k5 days ago
log4j-detector preview

log4j-detector

GitHubmergebase/log4j-detector

File-system scanner that detects vulnerable Log4J versions (CVE-2021-44228, CVE-2021-45046) by analyzing compiled Java classes, including nested…
static-analysissupply-chain-securityvulnerability-analysis+1
6404 years ago
log4j-finder preview

log4j-finder

GitHubfox-it/log4j-finder

Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
code-analysisincident-responsestatic-analysis+3
4393 years ago
PolinRider preview

PolinRider

GitHubopensourcemalware/polinrider

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
972 months ago
async-http-client-check preview

async-http-client-check

GitHubxiaoqimikko/async-http-client-check

Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…

defensive-toolsdevsecopsstatic-analysis+4
14 days ago
prefect-cve-2026-5366 preview

prefect-cve-2026-5366

GitHubrenat0z3r0/prefect-cve-2026-5366

PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
code-analysiseducationexploitation+3
3 months ago
shai-scan preview

shai-scan

GitHubdigi4care/shai-scan

Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
code-analysisdevsecopsincident-response+6
4 months ago
CVE-2025-48384 preview

CVE-2025-48384

GitHubvignesh21-git/cve-2025-48384

GIT vulnerability | Carriage Return and RCE on cloning

code-analysiseducationexploitation+2
9 months ago
Previous123456Next