

deptrust
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
api-securitycloud-securitydevsecops+4
61
clidey/deptrustCLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 dlitz/bash-cve-2014-6271-fixes
Curated collection of verified patches for the Shellshock (CVE-2014-6271) bash vulnerability, with upstream, Debian, and custom patches plus SHA256…
 diegogarciayala/cve-2024-24590-clearml-rce-cmd-poc
CVE-2024-24590 ClearML RCE&CMD POC
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
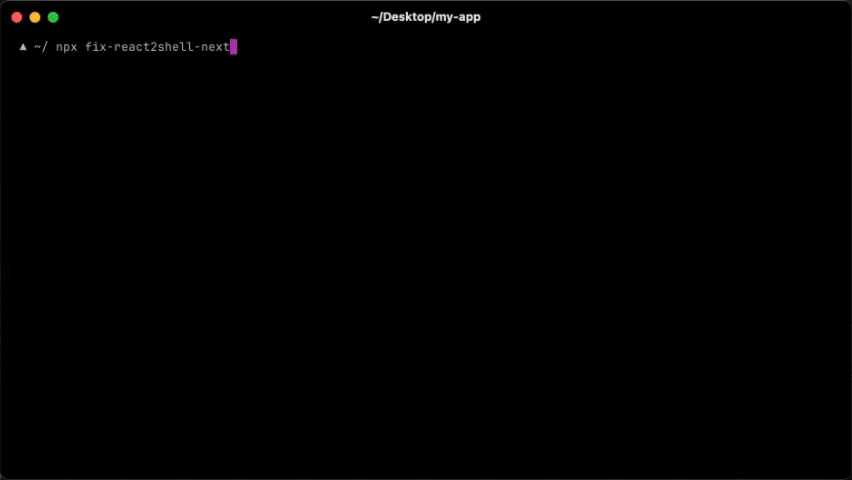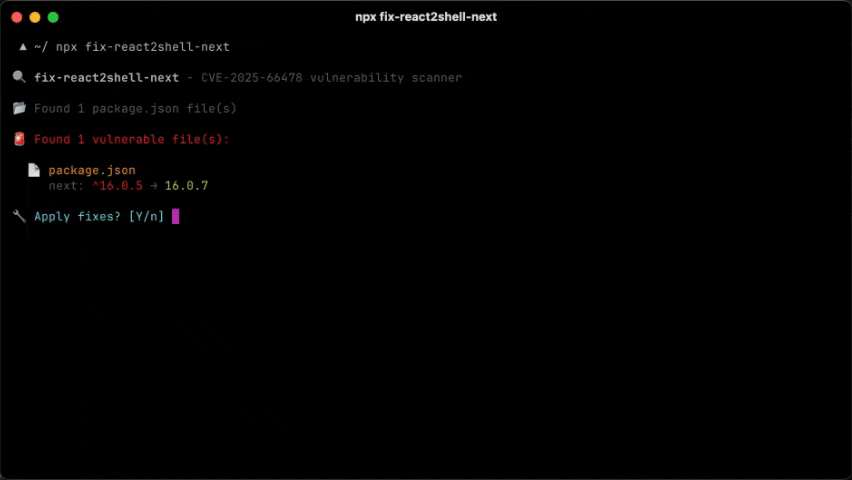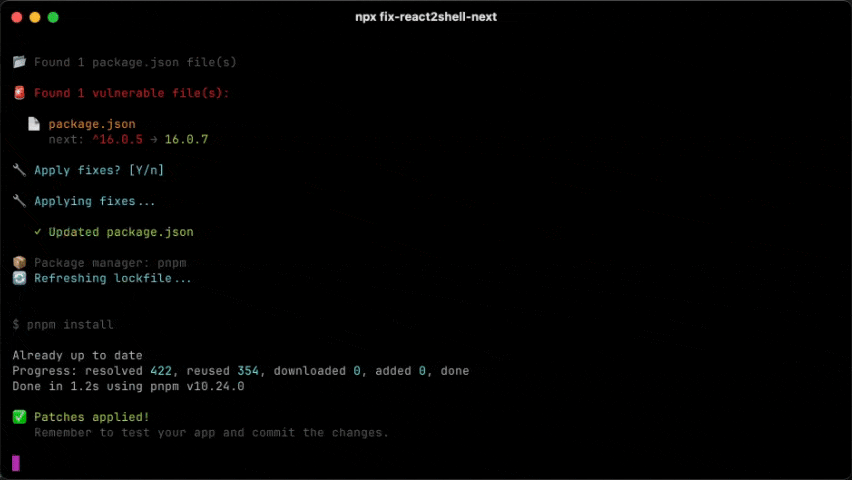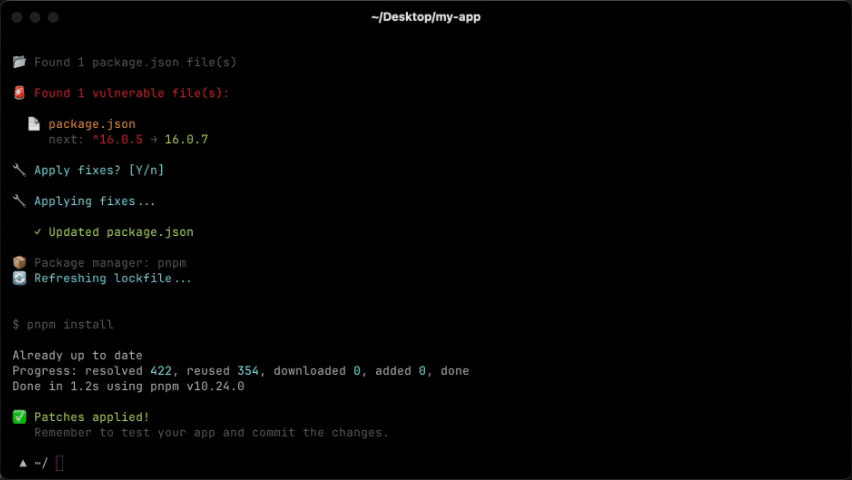 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
 asteroid-belt/skulto
Offline and security-first tool for syncing and managing agent skills
 simplylu/cve-2021-42574
Generate malicious files using recently published bidi-attack (CVE-2021-42574)
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 qainsights/cve-2022-42889-jmeter
Script to handle CVE 2022-42889
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 jbnetwork-git/cve-2024-3094-xz-utils-check
Shell script to check if your system has a vulnerable version of XZ Utils affected by CVE-2024-3094, enabling quick detection of the supply-chain…
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…