
smart-tree
 8b-is/smart-tree
Smart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
curated-resourceseducationgeneral-purpose-utilities+3
270
8b-is/smart-treeSmart Tree: not just a tree, a philosophy. A context-aware, AI-crafted replacement for 20+ tools with MEM8 quantum compression, semantic search,…
 agwa/git-crypt
Transparent file encryption in git
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
 oxsecurity/codetotal
Analyze any snippet, file, or repository to detect possible security flaws such as secret in code, open source vulnerability, code security,…
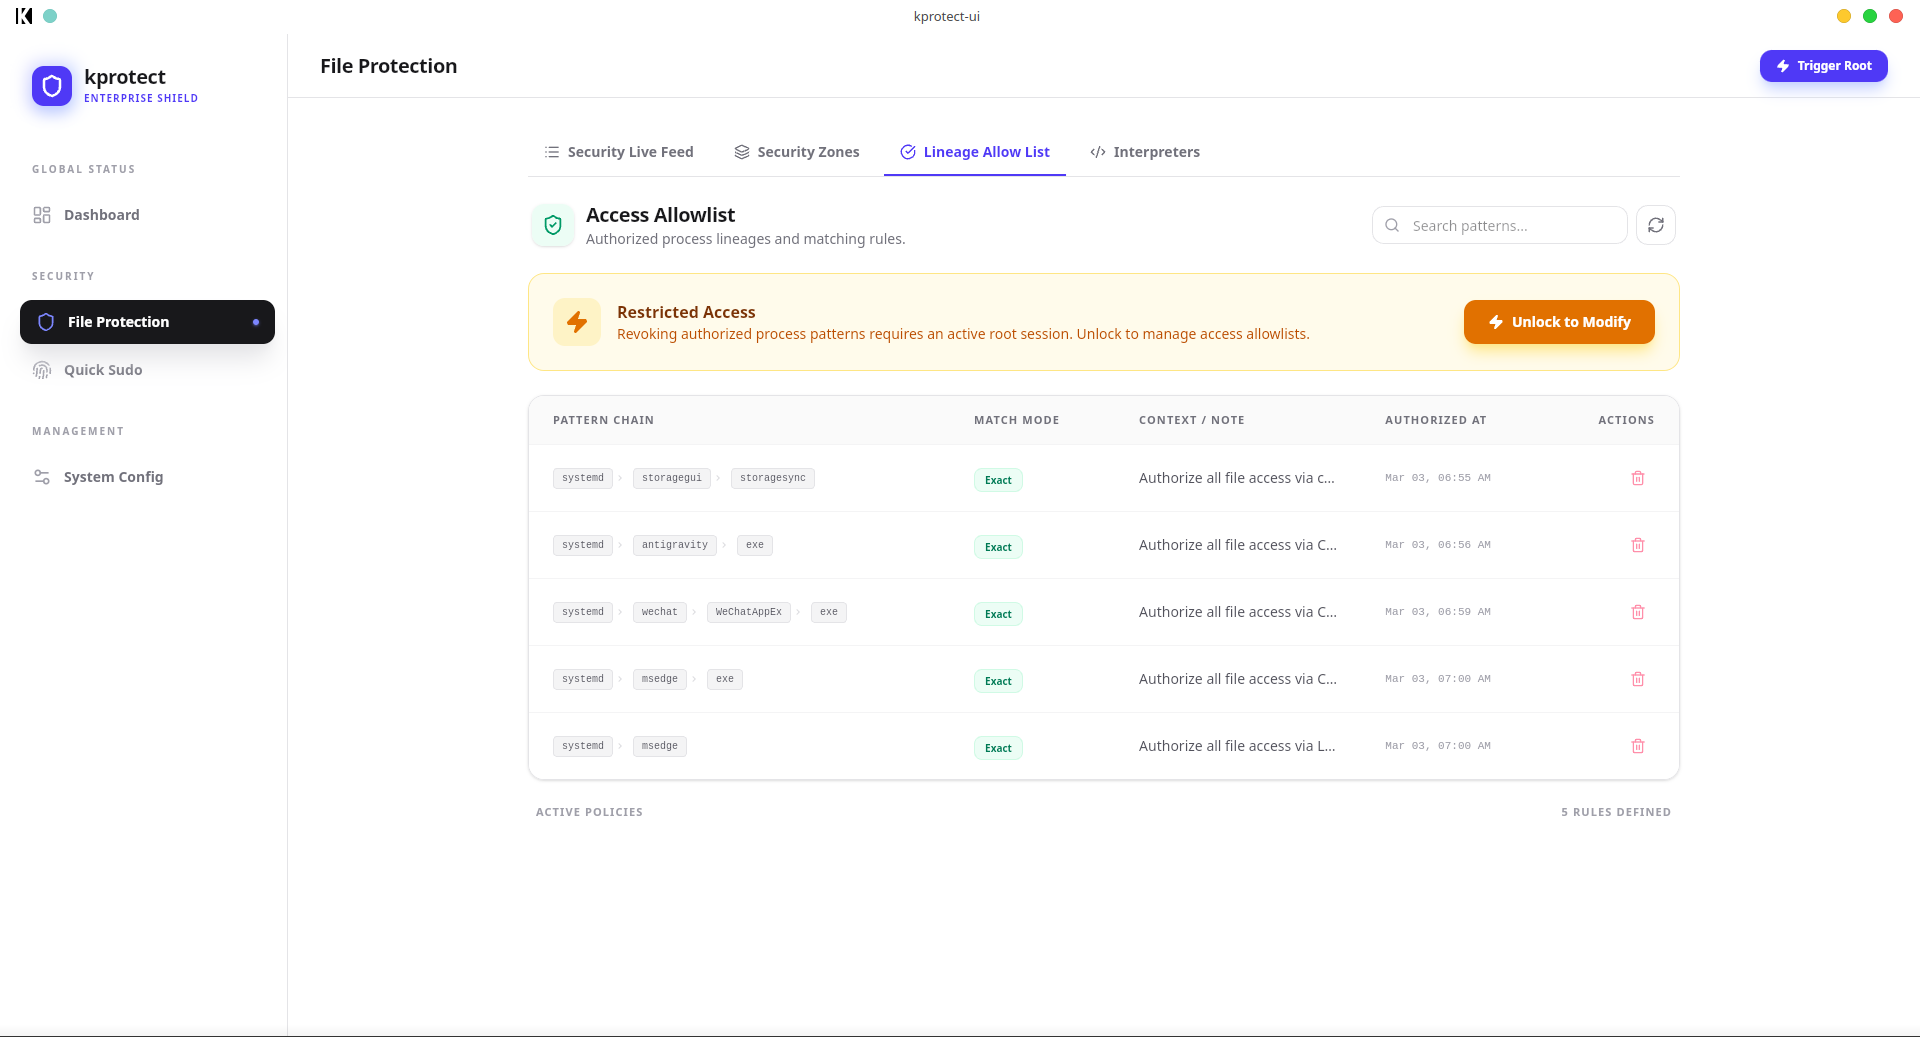 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 h3ck13r/cve-2026-35204
Proof-of-concept demonstrating a path traversal vulnerability (CVE-2026-35204) in Helm plugin installation, allowing arbitrary file write via crafted…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 ridhinva/npm-tar-path-traversal-scanner
Scanner: CVE-2026-31802 npm tar path traversal — Python checker for arbitrary file write via npm pack
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
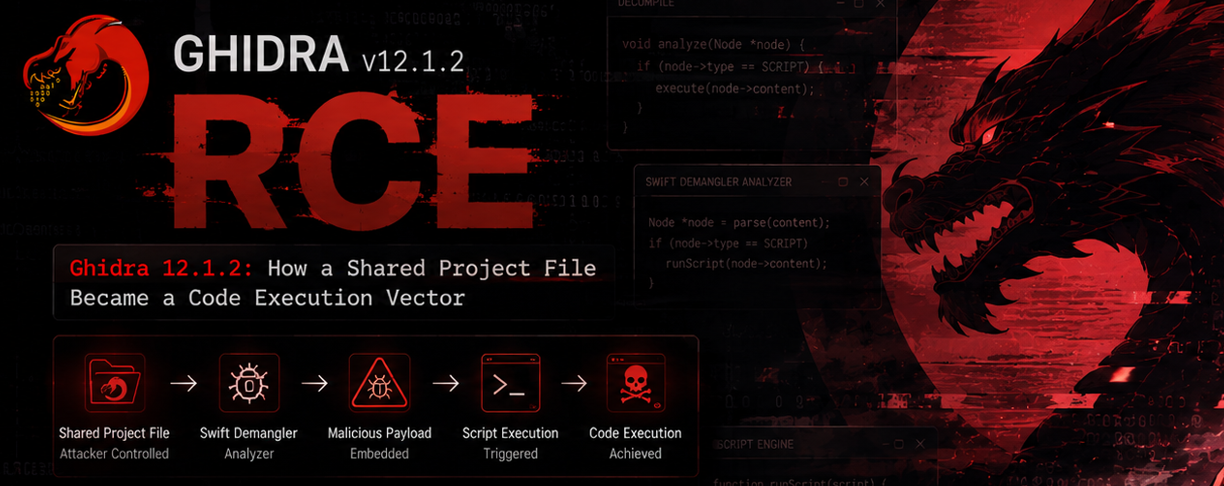 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 gcmurphy/chk_log4j
Some siimple checks to see if JAR file is vulnerable to CVE-2021-44228
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 cahyod/react2shell
Alat ini mendeteksi potensi kerentanan React2Shell (CVE-2025-55182) dalam proyek React dengan memeriksa: - File `package.json` dan file lock untuk…
 themcsam/cve-2024-12905-poc
tar-fs file write/overwrite vulnerability