

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
64 results
nono preview

nono

GitHubnolabs-ai/nono

agent runtime security - zero trust, zero setup, zero latency agent sandboxing
ai-securitycloud-securitycode-analysis+8
4.6k1 day ago
PSCF preview

PSCF

GitHubowasp/pscf

OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…

curated-resourcesdevsecopseducation+2
2914 days ago
python-tuf preview

python-tuf

GitHubtheupdateframework/python-tuf

Python reference implementation of The Update Framework (TUF)

cryptographysupply-chain-securityutilities-frameworks
1.7k9 days ago
syft preview

syft

GitHubanchore/syft

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

container-escapecontainer-securitydevsecops+3
9.7k1 day ago
DependencyCheck preview

DependencyCheck

GitHubdependency-check/dependencycheck

OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.

devsecopssupply-chain-securityvulnerability-analysis+1
7.7k10 days ago
dependency-track preview

dependency-track

GitHubdependencytrack/dependency-track

Intelligent Component Analysis platform that leverages SBOMs to identify and reduce software supply chain risk through continuous vulnerability…
devsecopssupply-chain-securityvulnerability-analysis
4.3k2h 28m ago
bumblebee preview

bumblebee

GitHubperplexityai/bumblebee

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
devsecopsincident-responseinformation-gathering+3
5.1k15 days ago
slsa preview

slsa

GitHubslsa-framework/slsa

Supply-chain Levels for Software Artifacts
curated-resourceseducationpapers-research+1
1.9k3 days ago
guac preview

guac

GitHubguacsec/guac

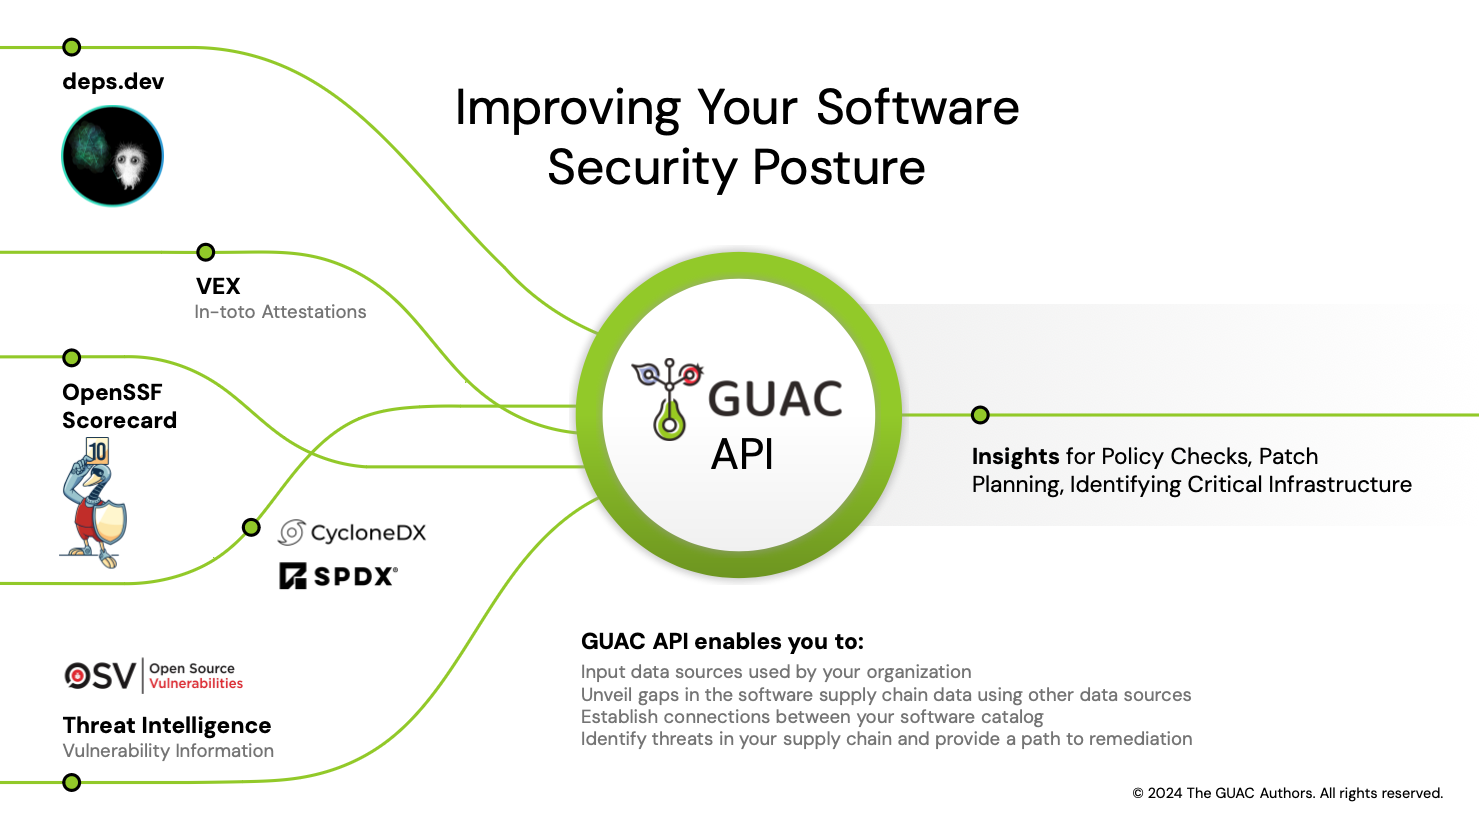
Aggregates software supply chain security metadata (SBOMs, attestations, vulnerabilities) into a queryable graph database for audit, policy, and risk…
supply-chain-securityvulnerability-analysis
1.6k3 days ago
rekor preview

rekor

GitHubsigstore/rekor

Software Supply Chain Transparency Log

cryptographydevsecopssupply-chain-security
1.2k22h 12m ago
fulcio preview

fulcio

GitHubsigstore/fulcio

Certificate authority issuing short-lived code-signing certificates tied to OpenID Connect identities, enabling verifiable software supply chain…

authentication-authorizationcryptographyidentity-access-management+1
8922 days ago
in-toto preview

in-toto

GitHubin-toto/in-toto

Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.

authentication-authorizationcryptographydefensive-tools+2
1.1k1 month ago
ship-safe preview

ship-safe

GitHubasamassekou10/ship-safe

The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
ai-securityapi-security-testingcloud-infrastructure-security+8
8616 days ago
murphysec preview

murphysec

GitHubmurphysecurity/murphysec

An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
supply-chain-securityvulnerability-scanners
1.8k6 months ago
minder preview

minder

GitHubmindersec/minder

Software Supply Chain Security Platform
cloud-securityconfiguration-auditingdevsecops+3
4239h 59m ago
chain-bench preview

chain-bench

GitHubaquasecurity/chain-bench

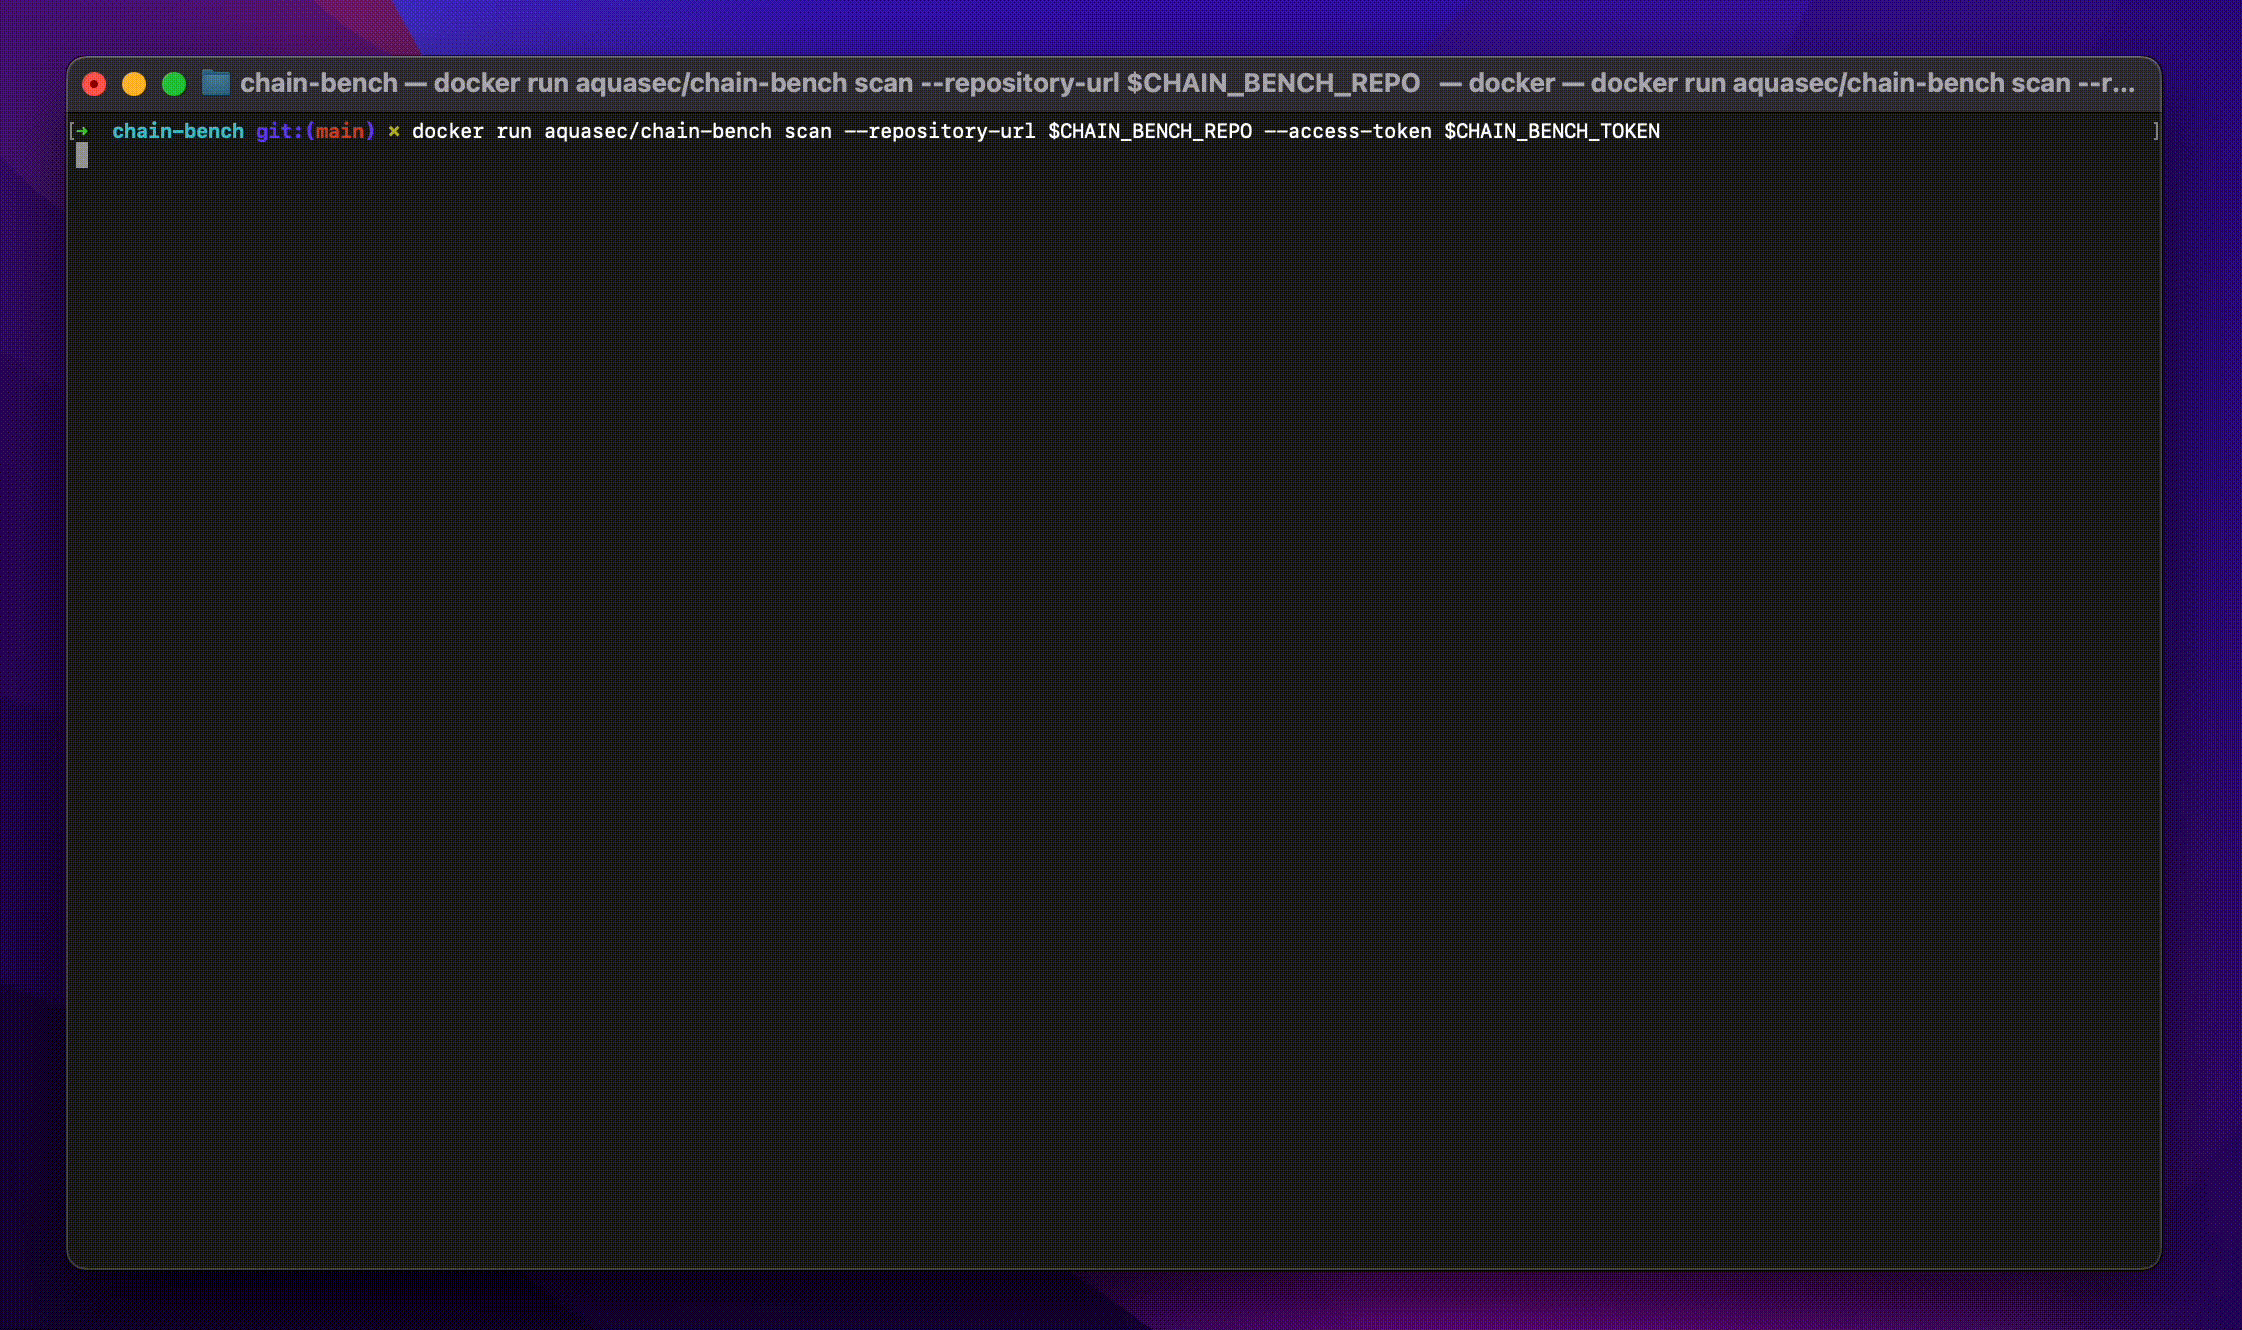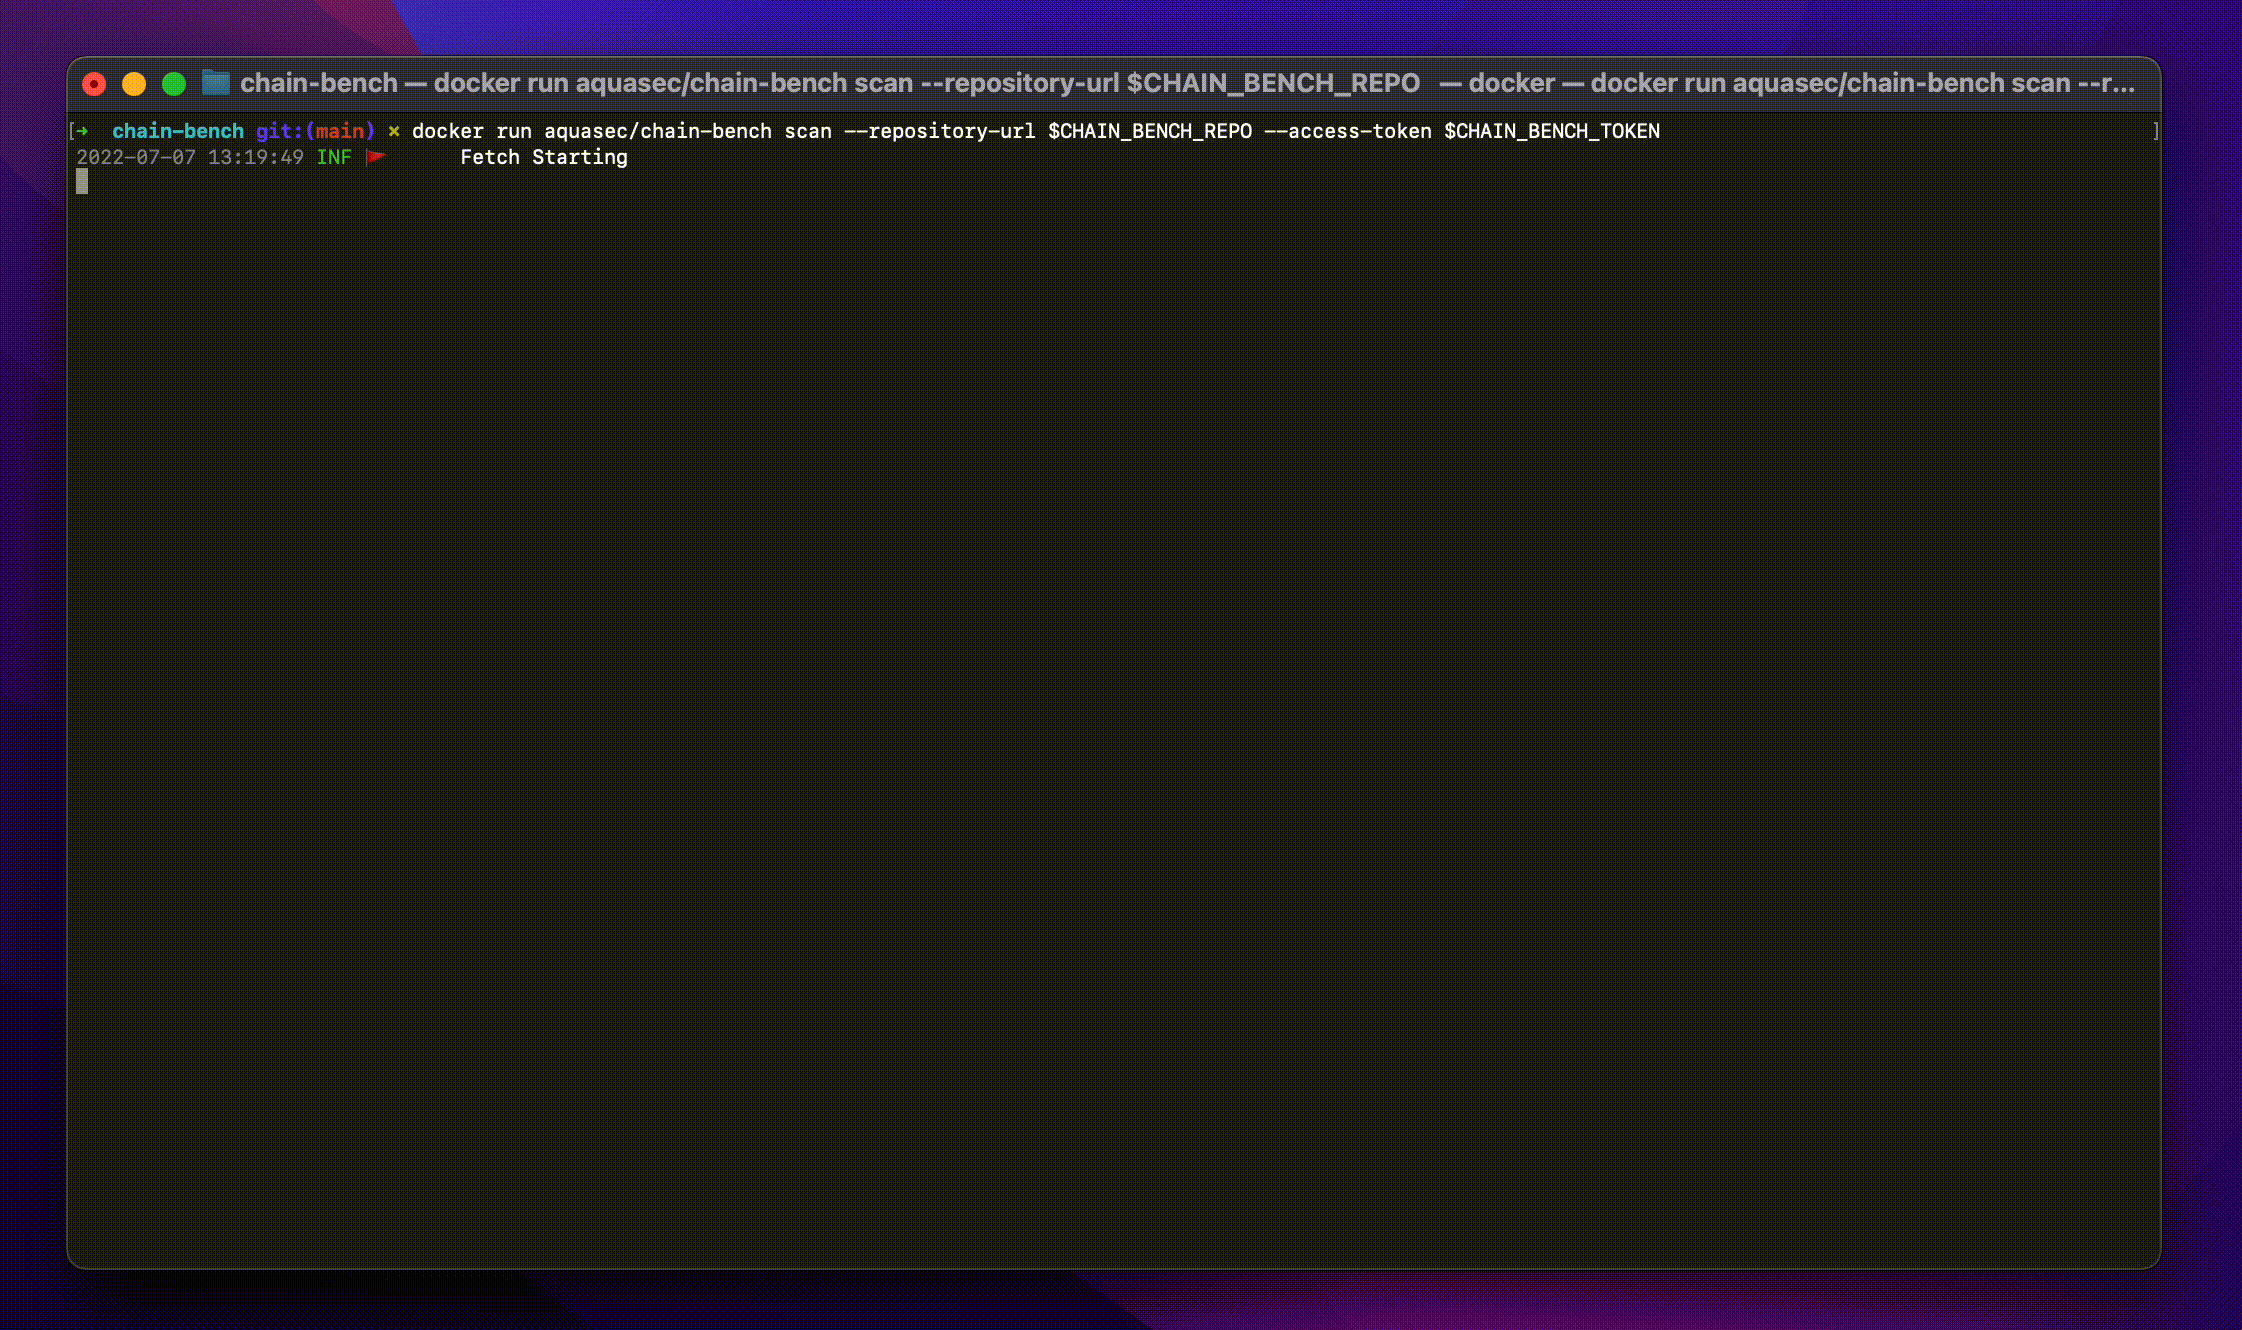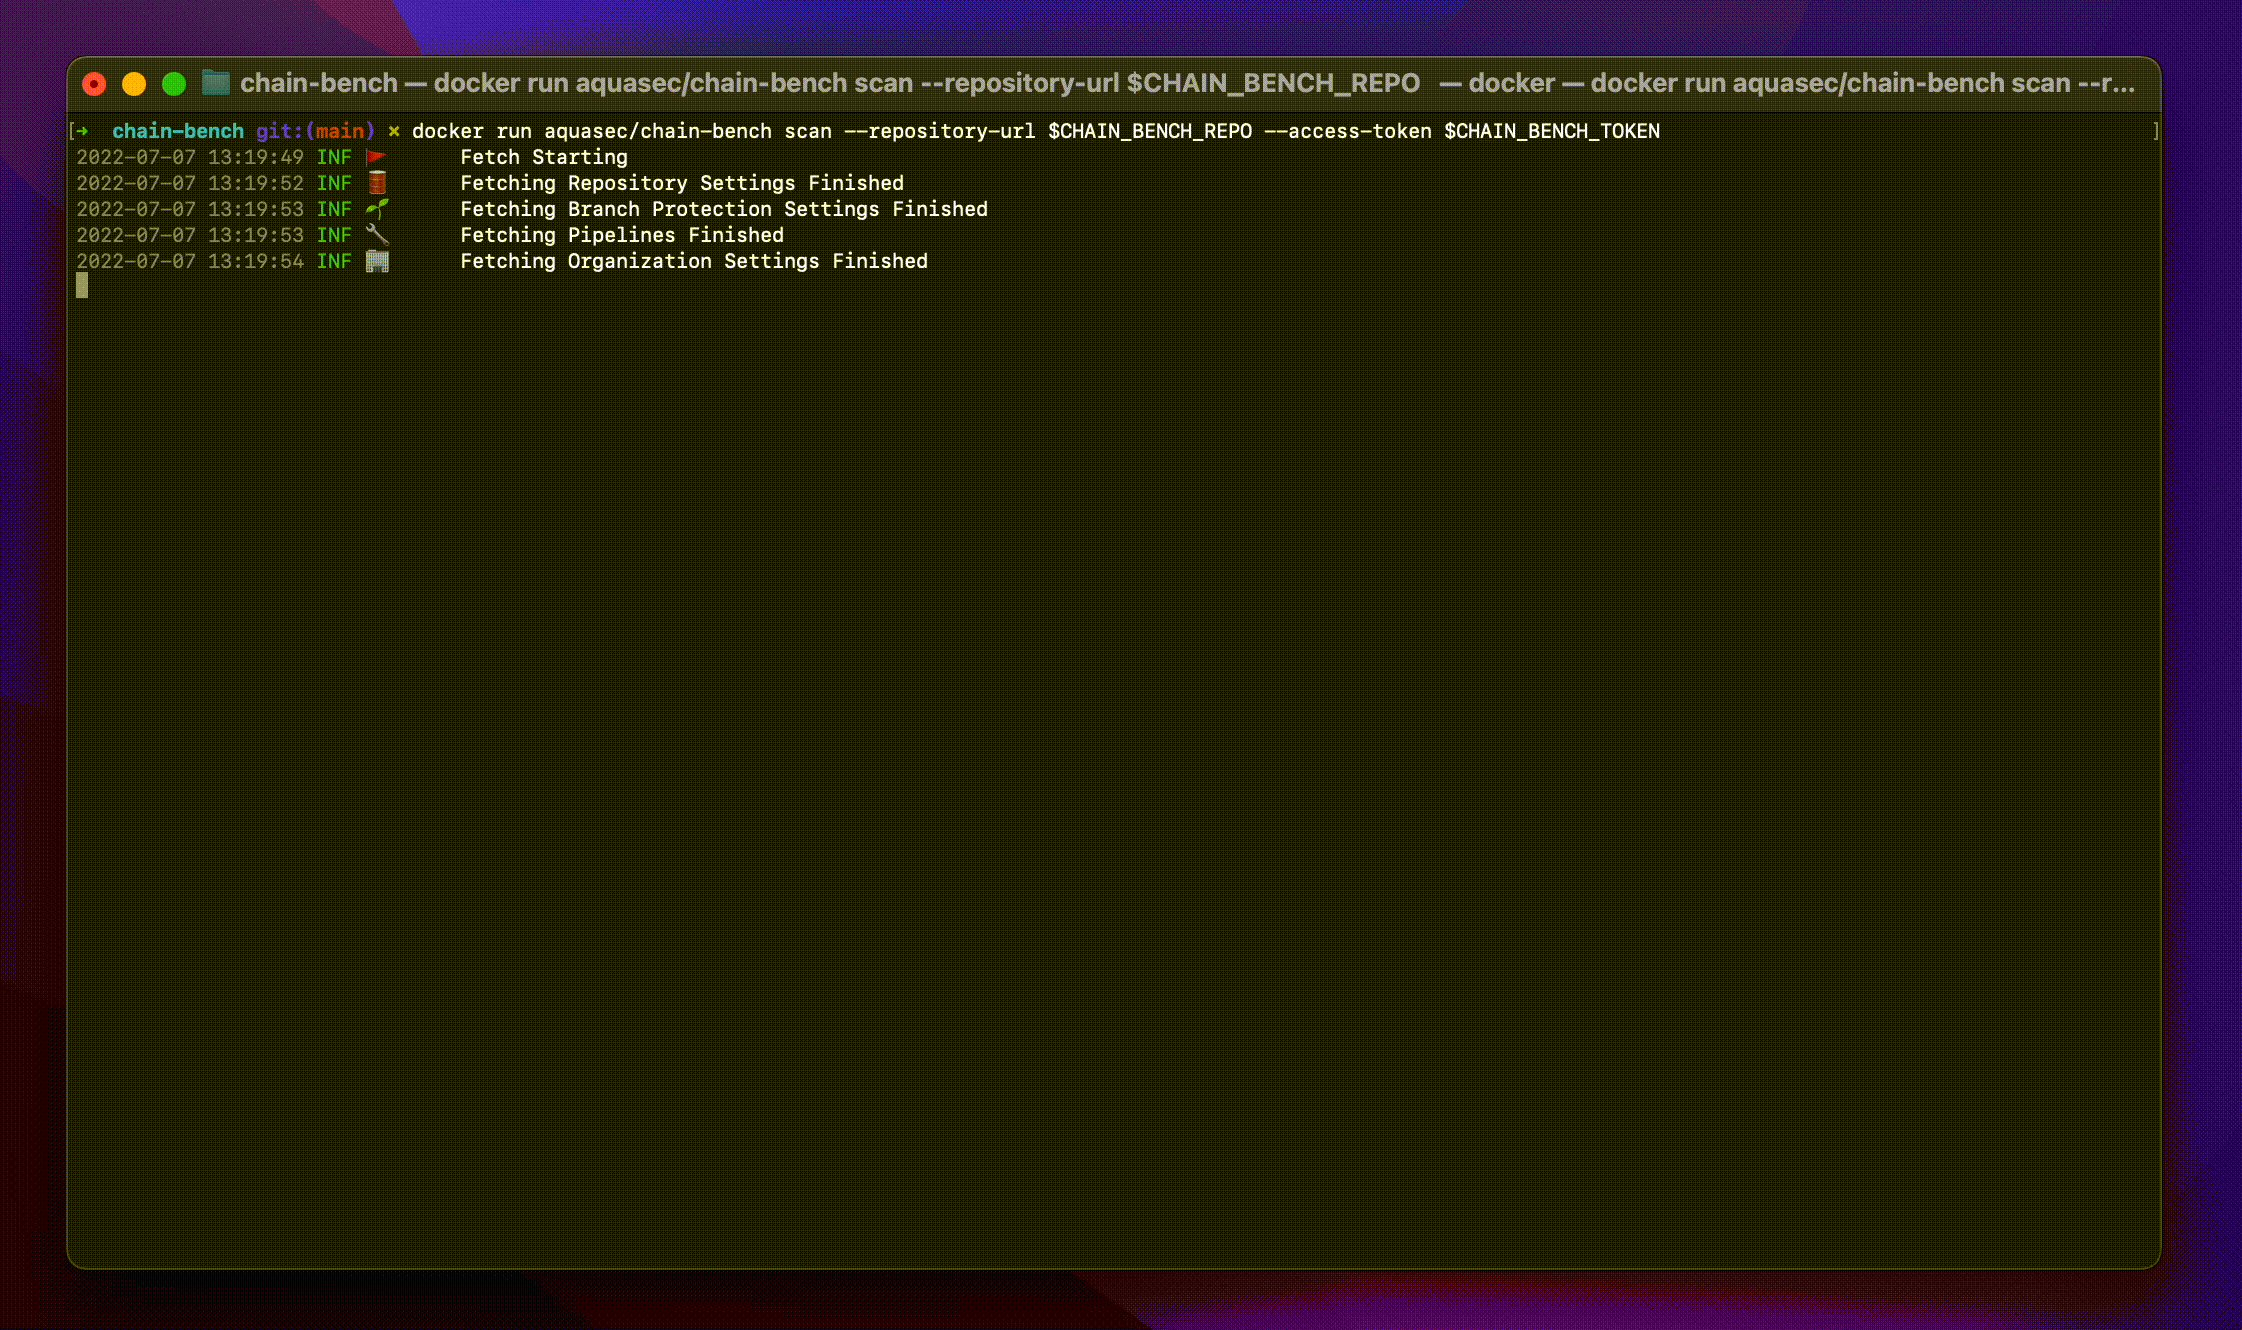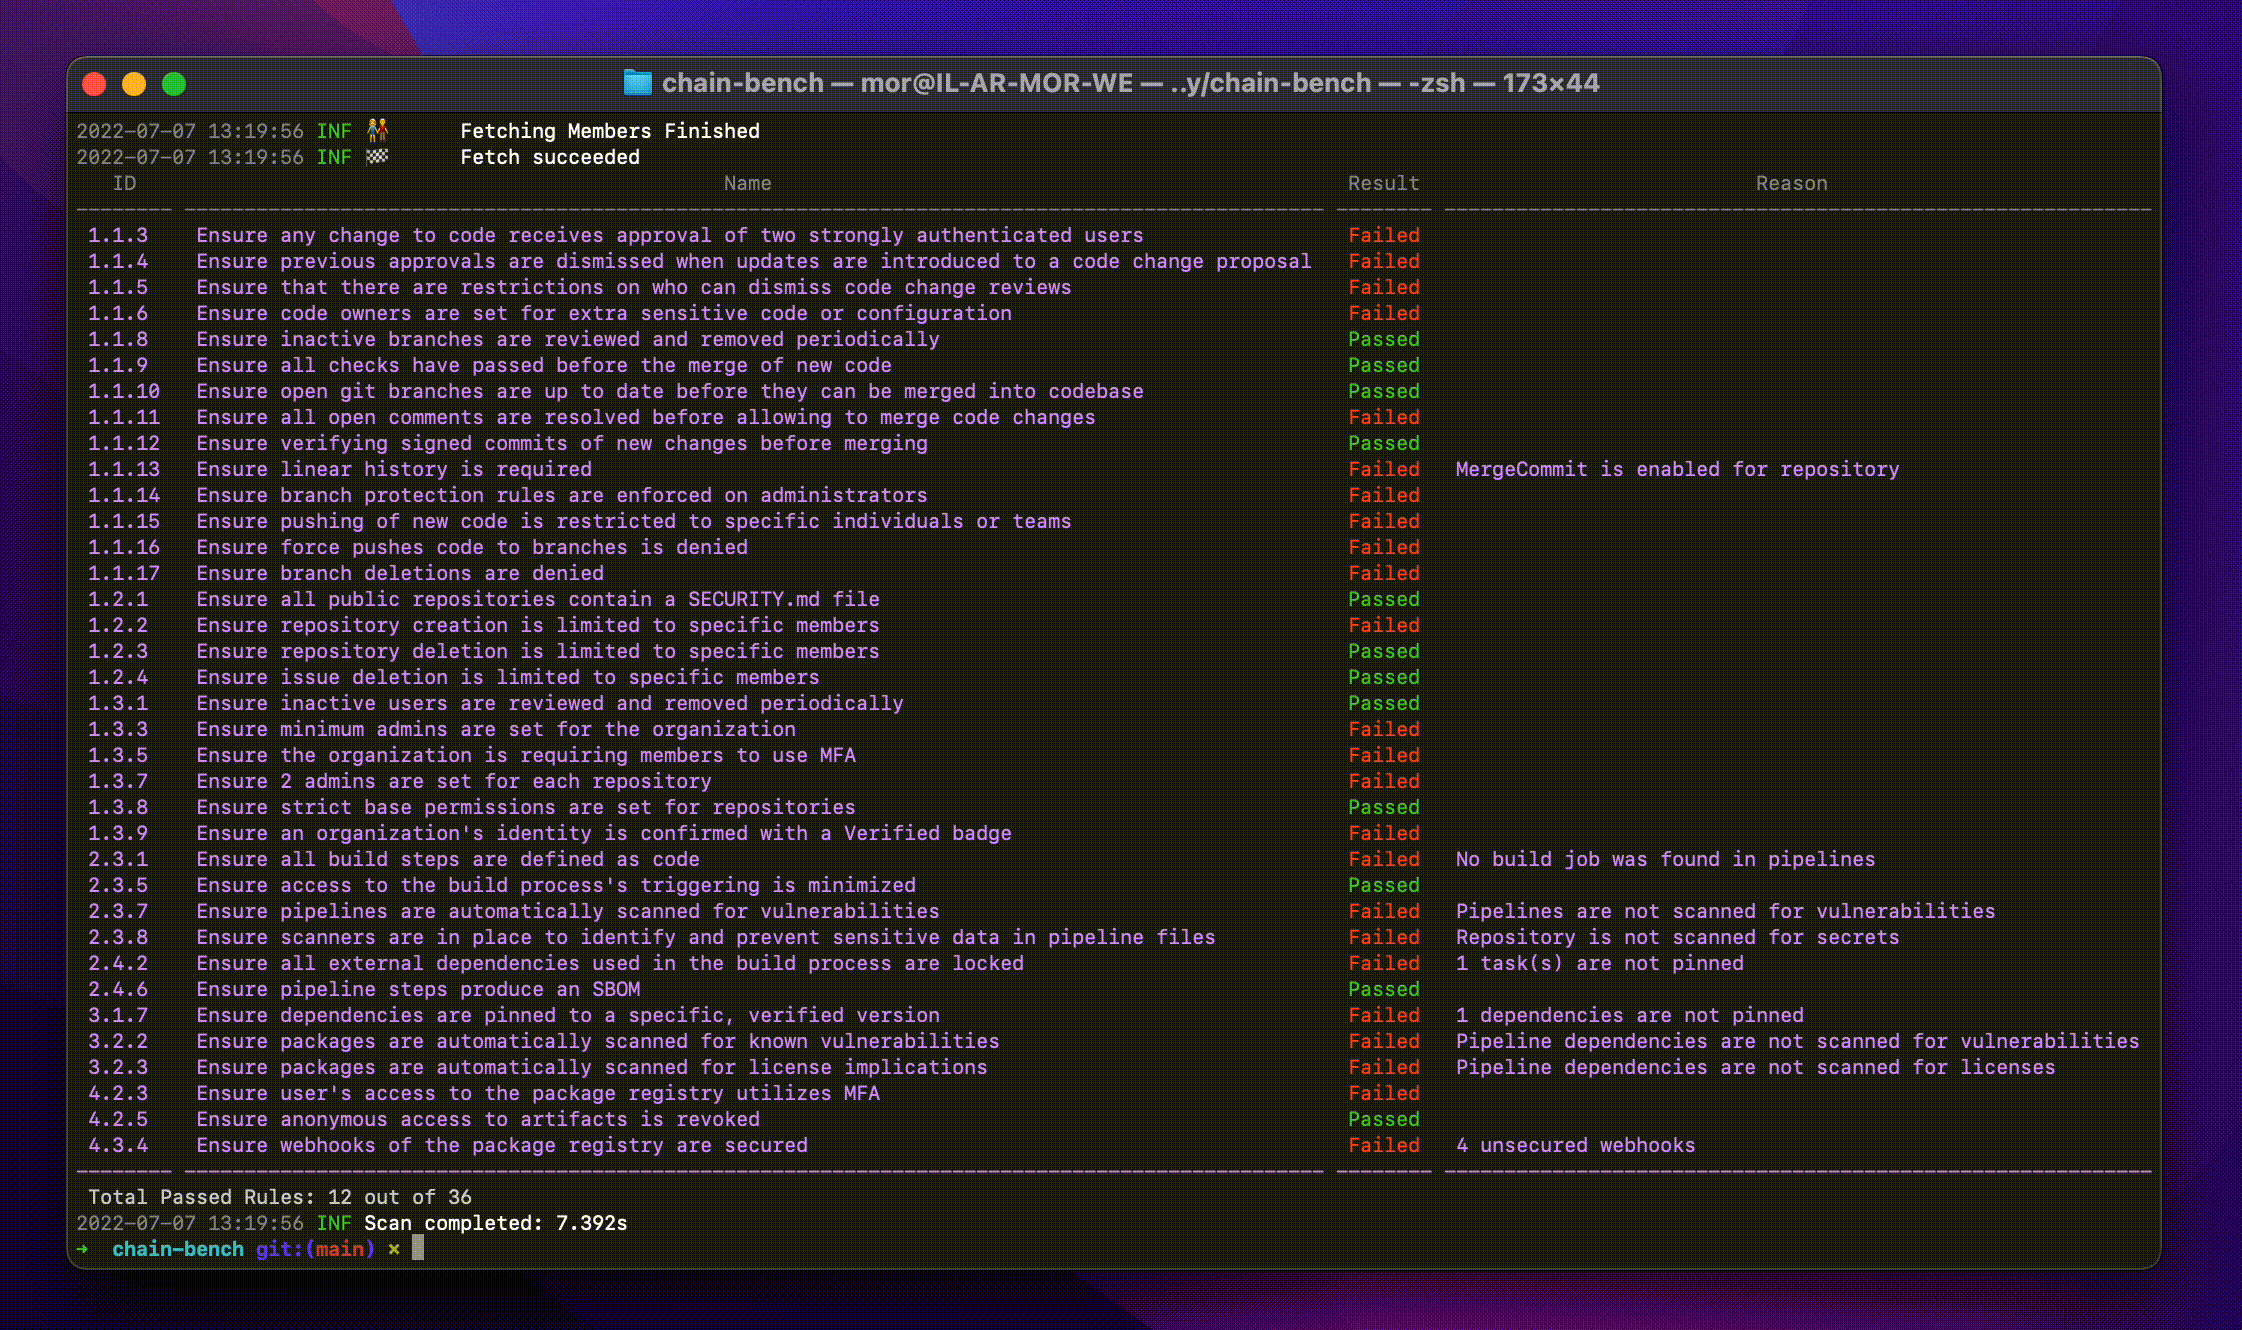
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
configuration-auditingdevsecopssupply-chain-security+1
7732 years ago
bomber preview

bomber

GitHubdevops-kung-fu/bomber

Scans Software Bill of Materials (SBOMs) for security vulnerabilities
devsecopssupply-chain-securityvulnerability-scanners
6278 months ago
advisories preview

advisories

GitHubjustinsteven/advisories

Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.

cloud-securitycurated-resourceseducation+3
2753 years ago
Previous1234Next