
InfraTest
 roy-aladin/infratest
DO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689
cloud-securityconfiguration-auditingeducation+2
roy-aladin/infratestDO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689
 aschen/log4j-patched
Provide patched version of Log4J against CVE-2021-44228 and CVE-2021-45046 as well as a script to manually patch it yourself
 owasp/devsecopsguideline
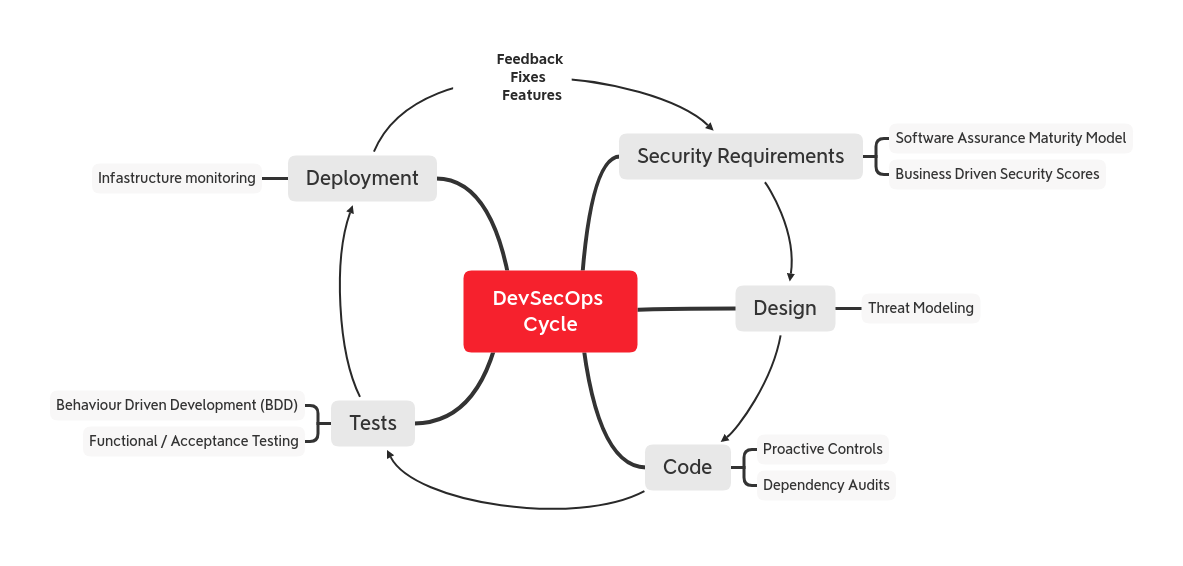
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 dhiyaneshgeek/my-presentation-slides
Collection's of Tech Talk that are presented by me :)
 dshapi/ai-spm
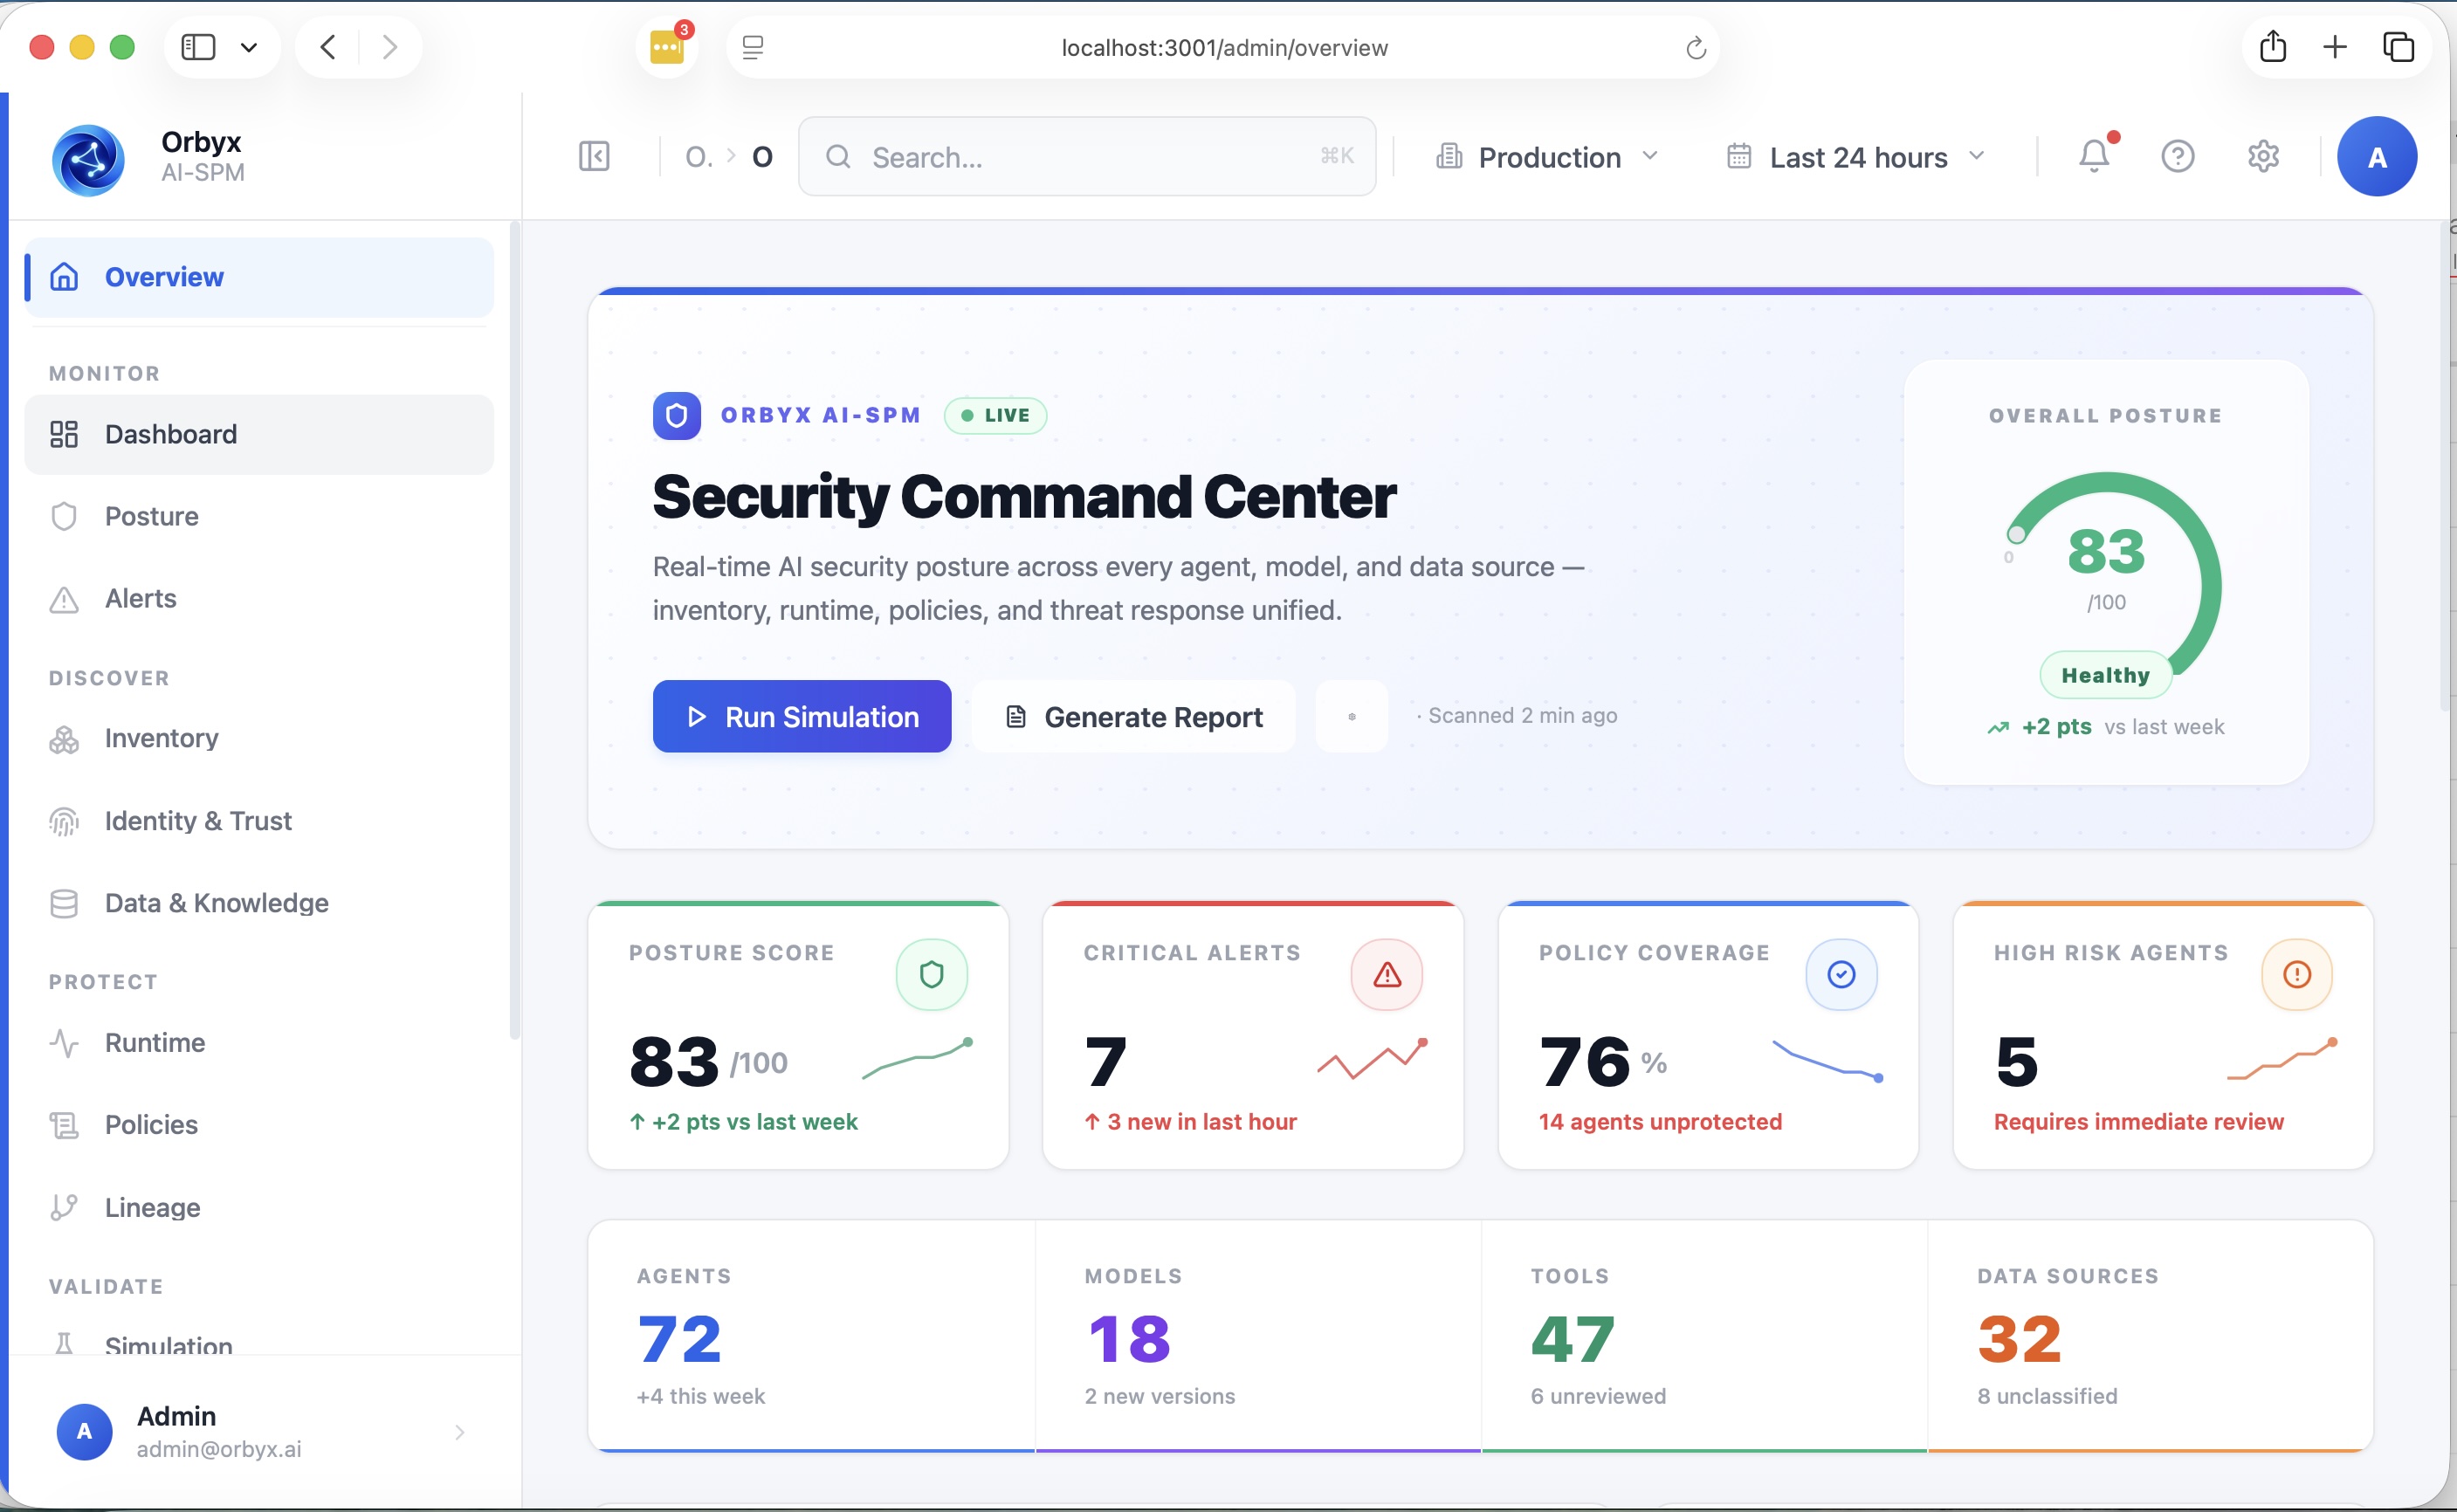
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
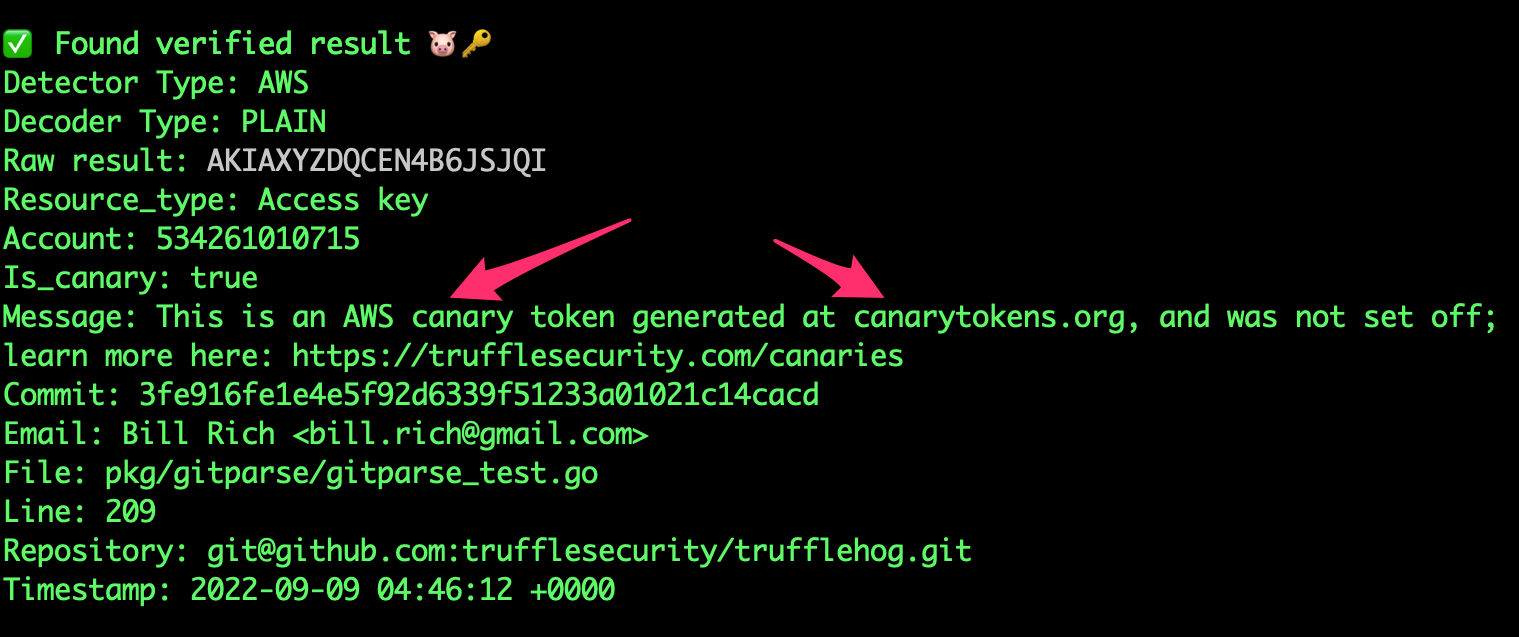 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 timwr/cve-2017-1000117
Proof of concept of CVE-2017-1000117
 google/capslock
CLI tool for analyzing Go package capabilities by tracing transitive calls to privileged standard library operations, enabling supply chain risk…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
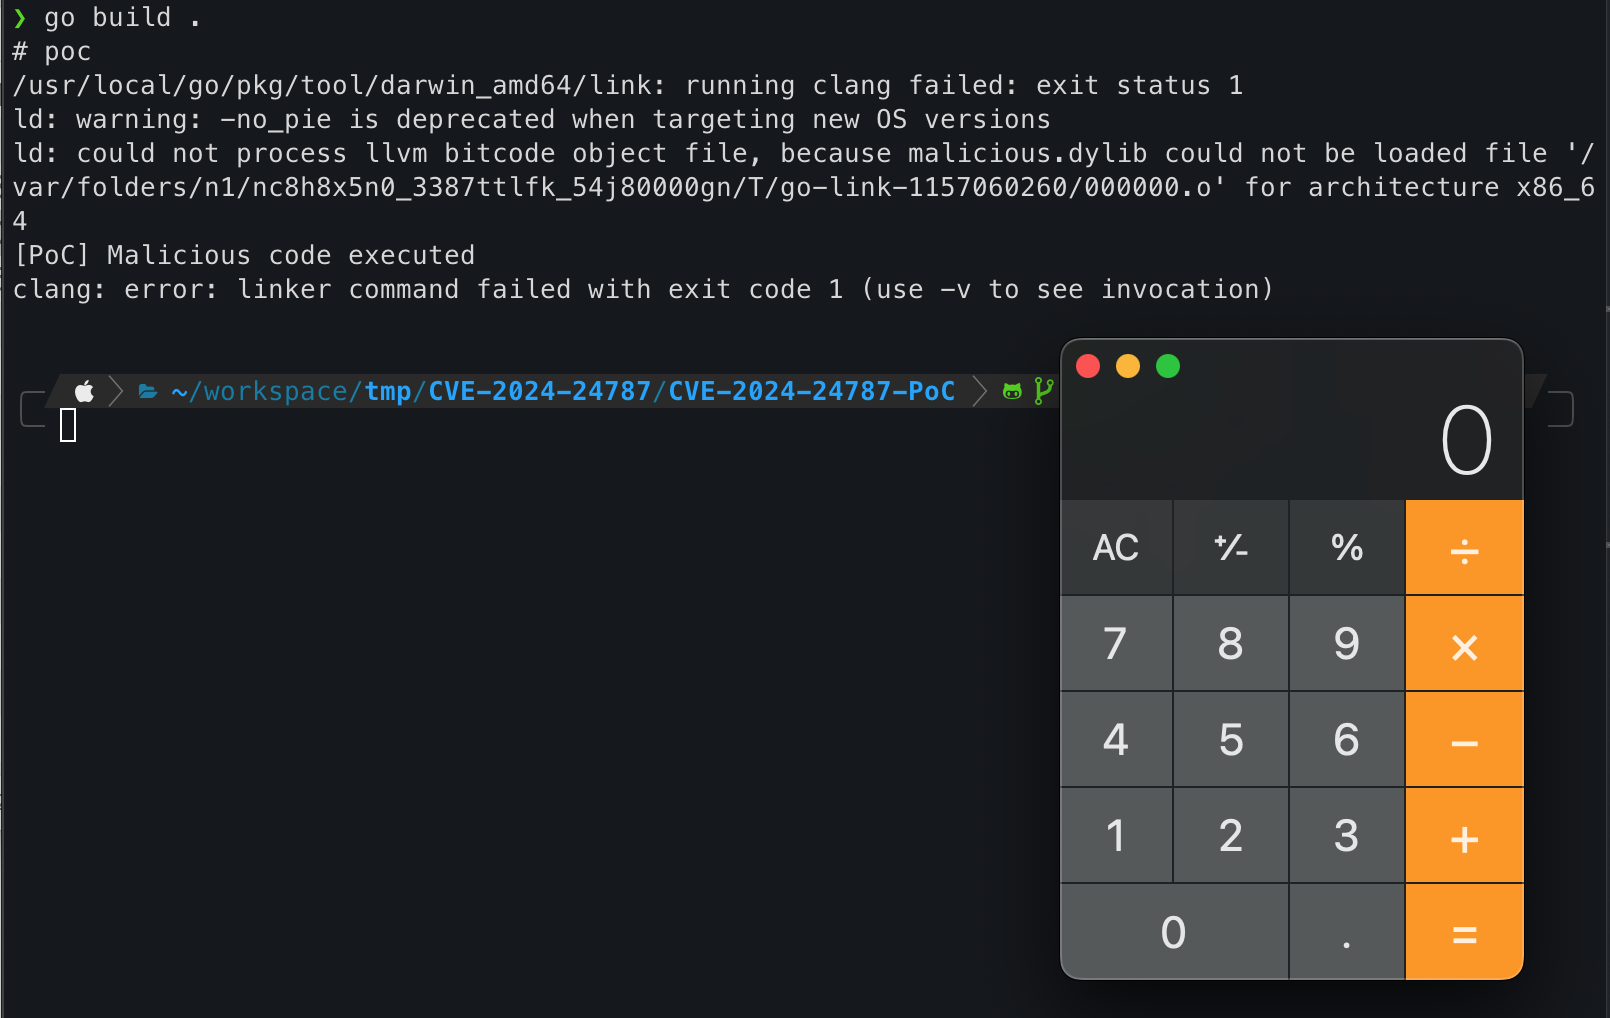 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 icatalina/cve-2021-43616
Demonstration of CVE-2021-43616: npm `ci` command ignoring package-lock.json, causing unintended dependency version installation and supply-chain…
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 u-maxx/magento-swf-patched-cve-2011-2461
Patched version of the uploader.swf and uploaderSingle.swf to fix CVE-2011-2461
 s0ld13rr/claude-code-backdoor
Backdooring Claude Code via hooks in settings.json. Authorized use only!