Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
log4shell-hotfix-side-effect preview
Archived

log4shell-hotfix-side-effect

GitHubmss/log4shell-hotfix-side-effect

Test case to check if the Log4Shell/CVE-2021-44228 hotfix will raise any unexpected exceptions
code-analysissupply-chain-securityvulnerability-analysis+1
3
4 years ago
rekor preview

rekor

GitHubsigstore/rekor

Software Supply Chain Transparency Log

cryptographydevsecopssupply-chain-security
1.2k2 days ago
trivy-action preview

trivy-action

GitHubaquasecurity/trivy-action

Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
cloud-securitycode-analysiscontainer-security+5
1.4k1 month ago
log4j-CVE-2021-44228-workaround preview

log4j-CVE-2021-44228-workaround

GitHubgrimch/log4j-cve-2021-44228-workaround

general purpose workaround for the log4j CVE-2021-44228 vulnerability

exploitationincident-responsemisconfiguration+2
4 years ago
jfrog-CVE-2022-24675 preview

jfrog-CVE-2022-24675

GitHubjfrog/jfrog-cve-2022-24675

Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
binary-analysiscode-analysisstatic-code-analysis+2
4 years ago
CS50FinalProject preview

CS50FinalProject

GitHubm1lo25/cs50finalproject

Investigation into the XZ Utils backdoor (CVE-2024-3094): chronology, attack chain, risk to SSH, and supply-chain insights. Includes slides, sources,…
curated-resourceseducationincident-response+3
111 months ago
bumblebee preview

bumblebee

GitHubperplexityai/bumblebee

Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
devsecopsincident-responseinformation-gathering+3
5.0k7 days ago
supply-chain-monitor preview

supply-chain-monitor

GitHubelastic/supply-chain-monitor

Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
code-analysisincident-responsemalware-analysis+3
5326 months ago
hotpatch-for-apache-log4j2 preview

hotpatch-for-apache-log4j2

GitHubcorretto/hotpatch-for-apache-log4j2

An agent to hotpatch the log4j RCE from CVE-2021-44228.
defensive-toolsexploitationincident-response+2
4973 years ago
cve-2024-3094-tools preview

cve-2024-3094-tools

GitHubjfrog/cve-2024-3094-tools

Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
forensicsincident-responsemalware-analysis+3
452 years ago
log4noshell preview

log4noshell

GitHubwinnpixie/log4noshell

A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
defensive-toolsexploitationincident-response+2
51 month ago
CVE-2024-3094-XZ-Backdoor-Detector preview

CVE-2024-3094-XZ-Backdoor-Detector

GitHubdevjanger/cve-2024-3094-xz-backdoor-detector

Shell script to detect the CVE-2024-3094 backdoor in XZ Utils by checking for malicious code in liblzma build artifacts and identifying affected…

forensicsincident-responsemalware-analysis+3
2 years ago
log4jjndilookupremove preview

log4jjndilookupremove

GitHublukepasek/log4jjndilookupremove

A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.

incident-responsemisconfigurationscripting-automation+2
4 years ago
CVE-2021-44228_scanner preview
Archived

CVE-2021-44228_scanner

GitHubcertcc/cve-2021-44228_scanner

Scanners for Jar files that may be vulnerable to CVE-2021-44228
code-analysisincident-responsestatic-analysis+3
3504 years ago
log4j-finder preview

log4j-finder

GitHubfox-it/log4j-finder

Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)

code-analysisincident-responsestatic-analysis+3
4393 years ago
CVE-2021-44228-Log4Shell-Hashes preview

CVE-2021-44228-Log4Shell-Hashes

GitHubmubix/cve-2021-44228-log4shell-hashes

Hashes for vulnerable LOG4J versions
forensicsincident-responseioc-management+3
1544 years ago
halo-record preview

halo-record

GitHubbkuan001/halo-record

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
ai-securityforensicsincident-response+1
8115 days ago
vercel-april2026-incident-response preview

vercel-april2026-incident-response

GitHubopensourcemalware/vercel-april2026-incident-response

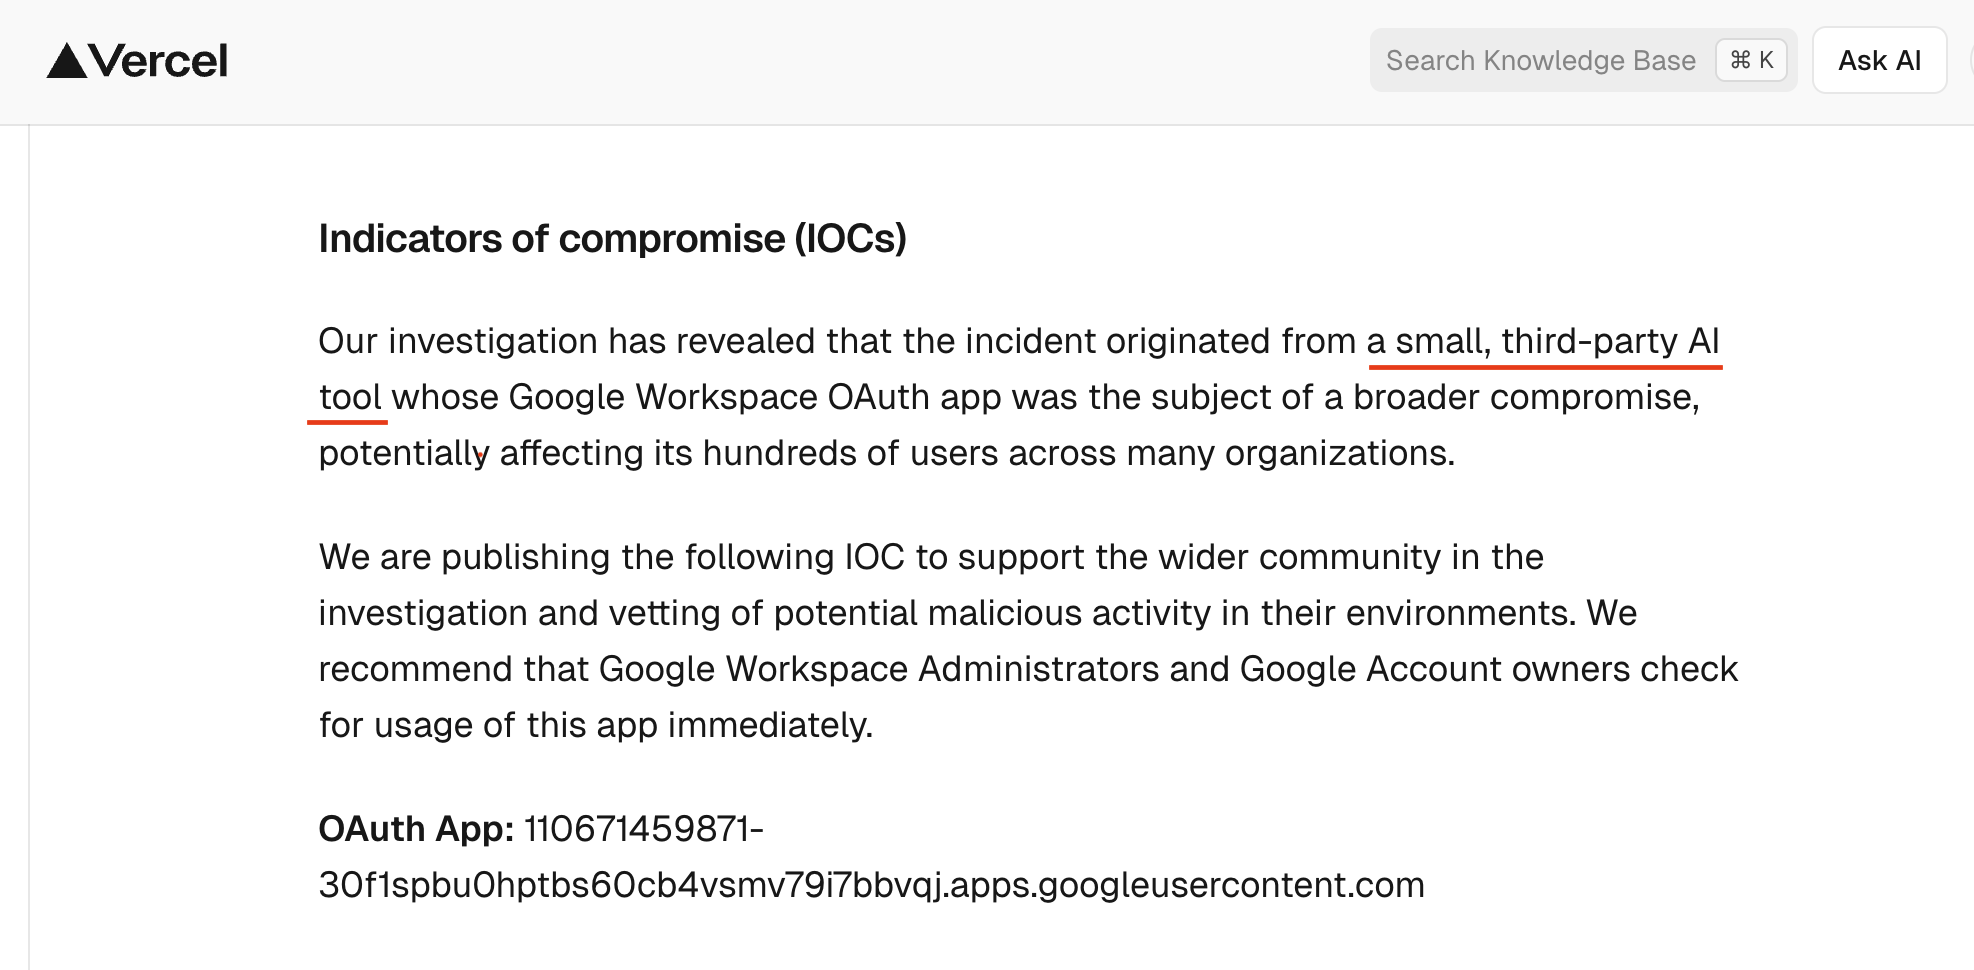
This is an incident response playbook we created for the Vercel April 2026 compromise

cloud-securitydigital-forensicsincident-response+3
325 months ago
Previous12Next
