
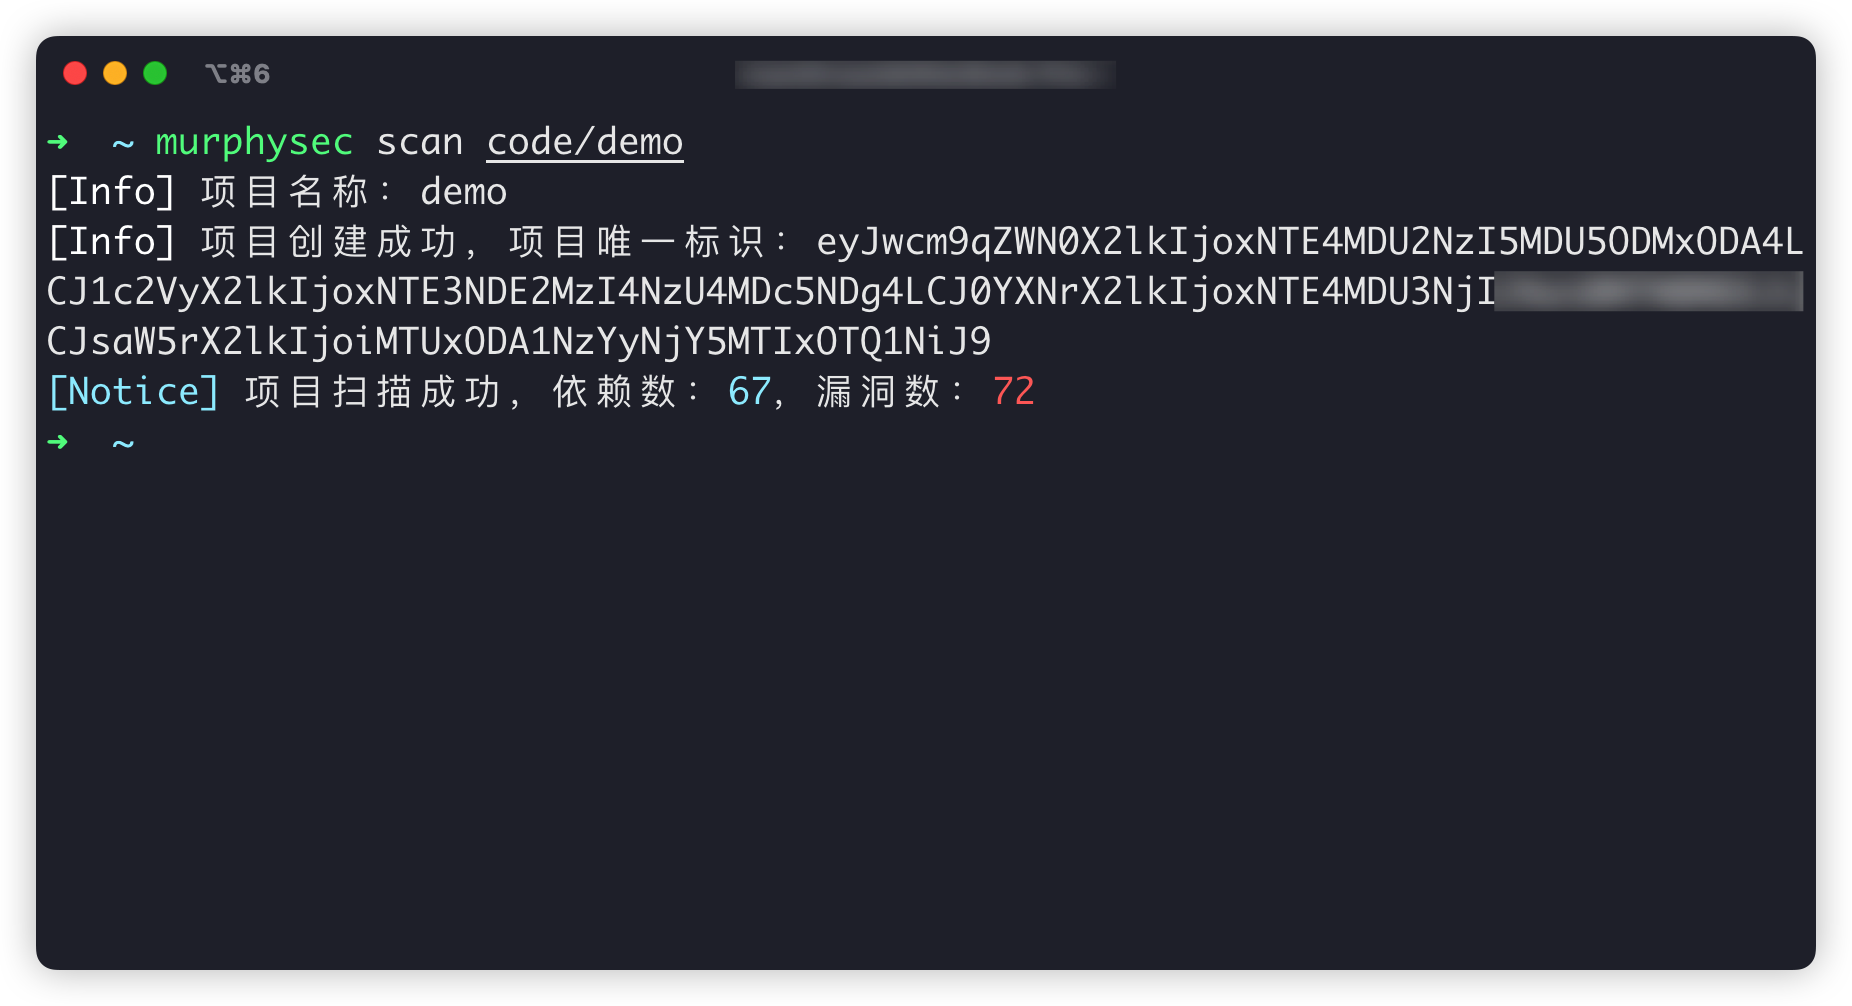
murphysec
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
supply-chain-securityvulnerability-scanners
murphysecurity/murphysecAn open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
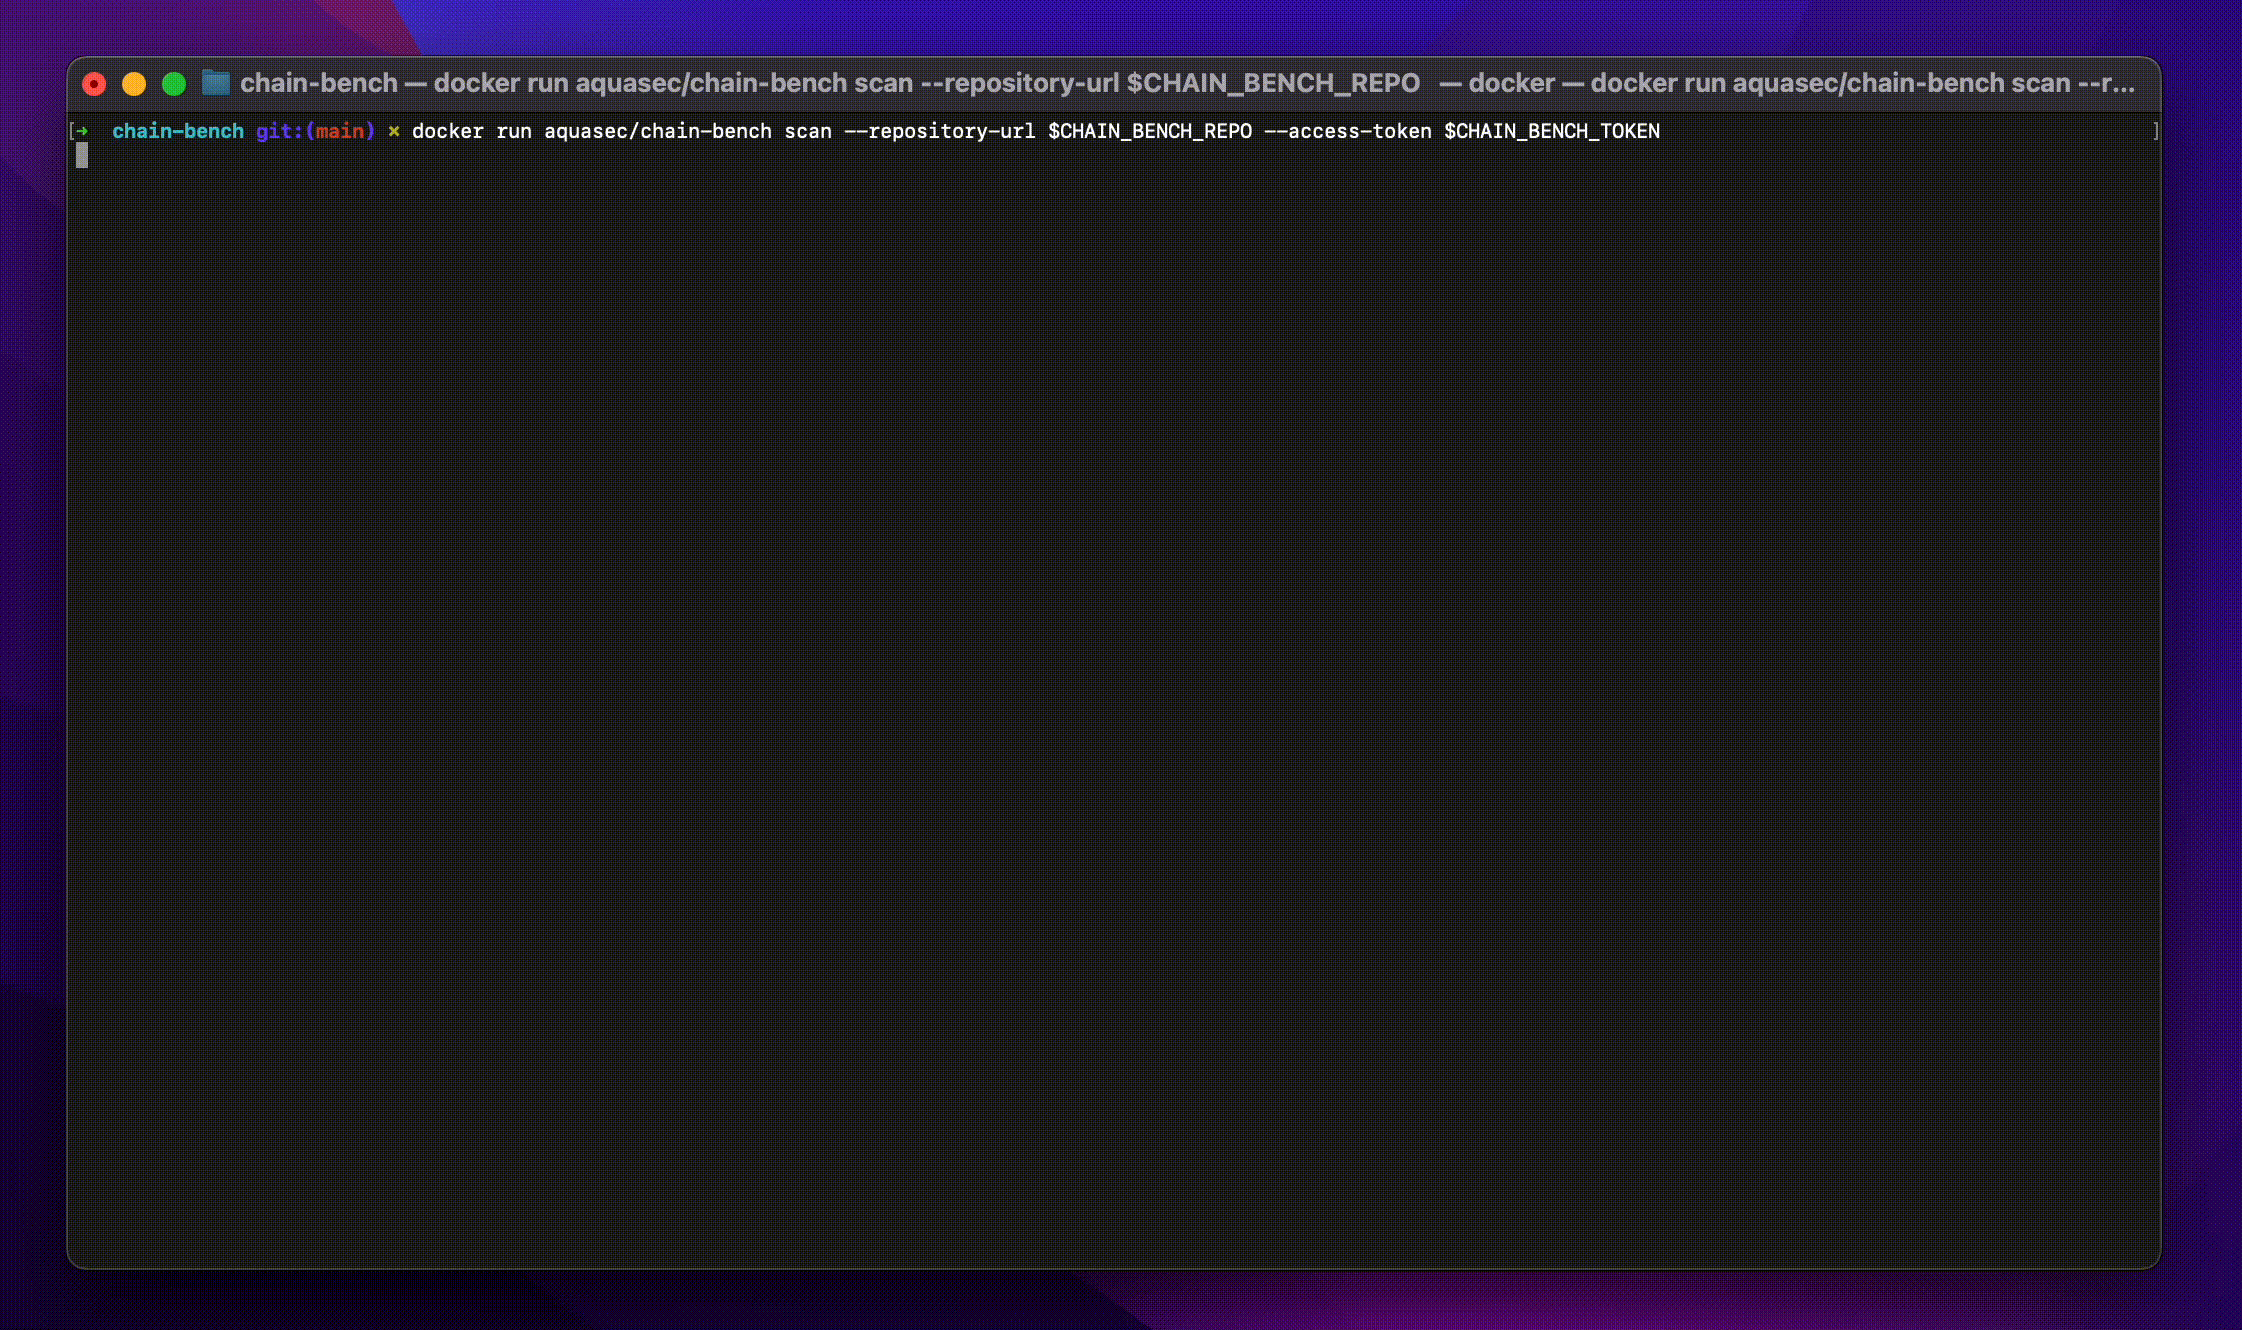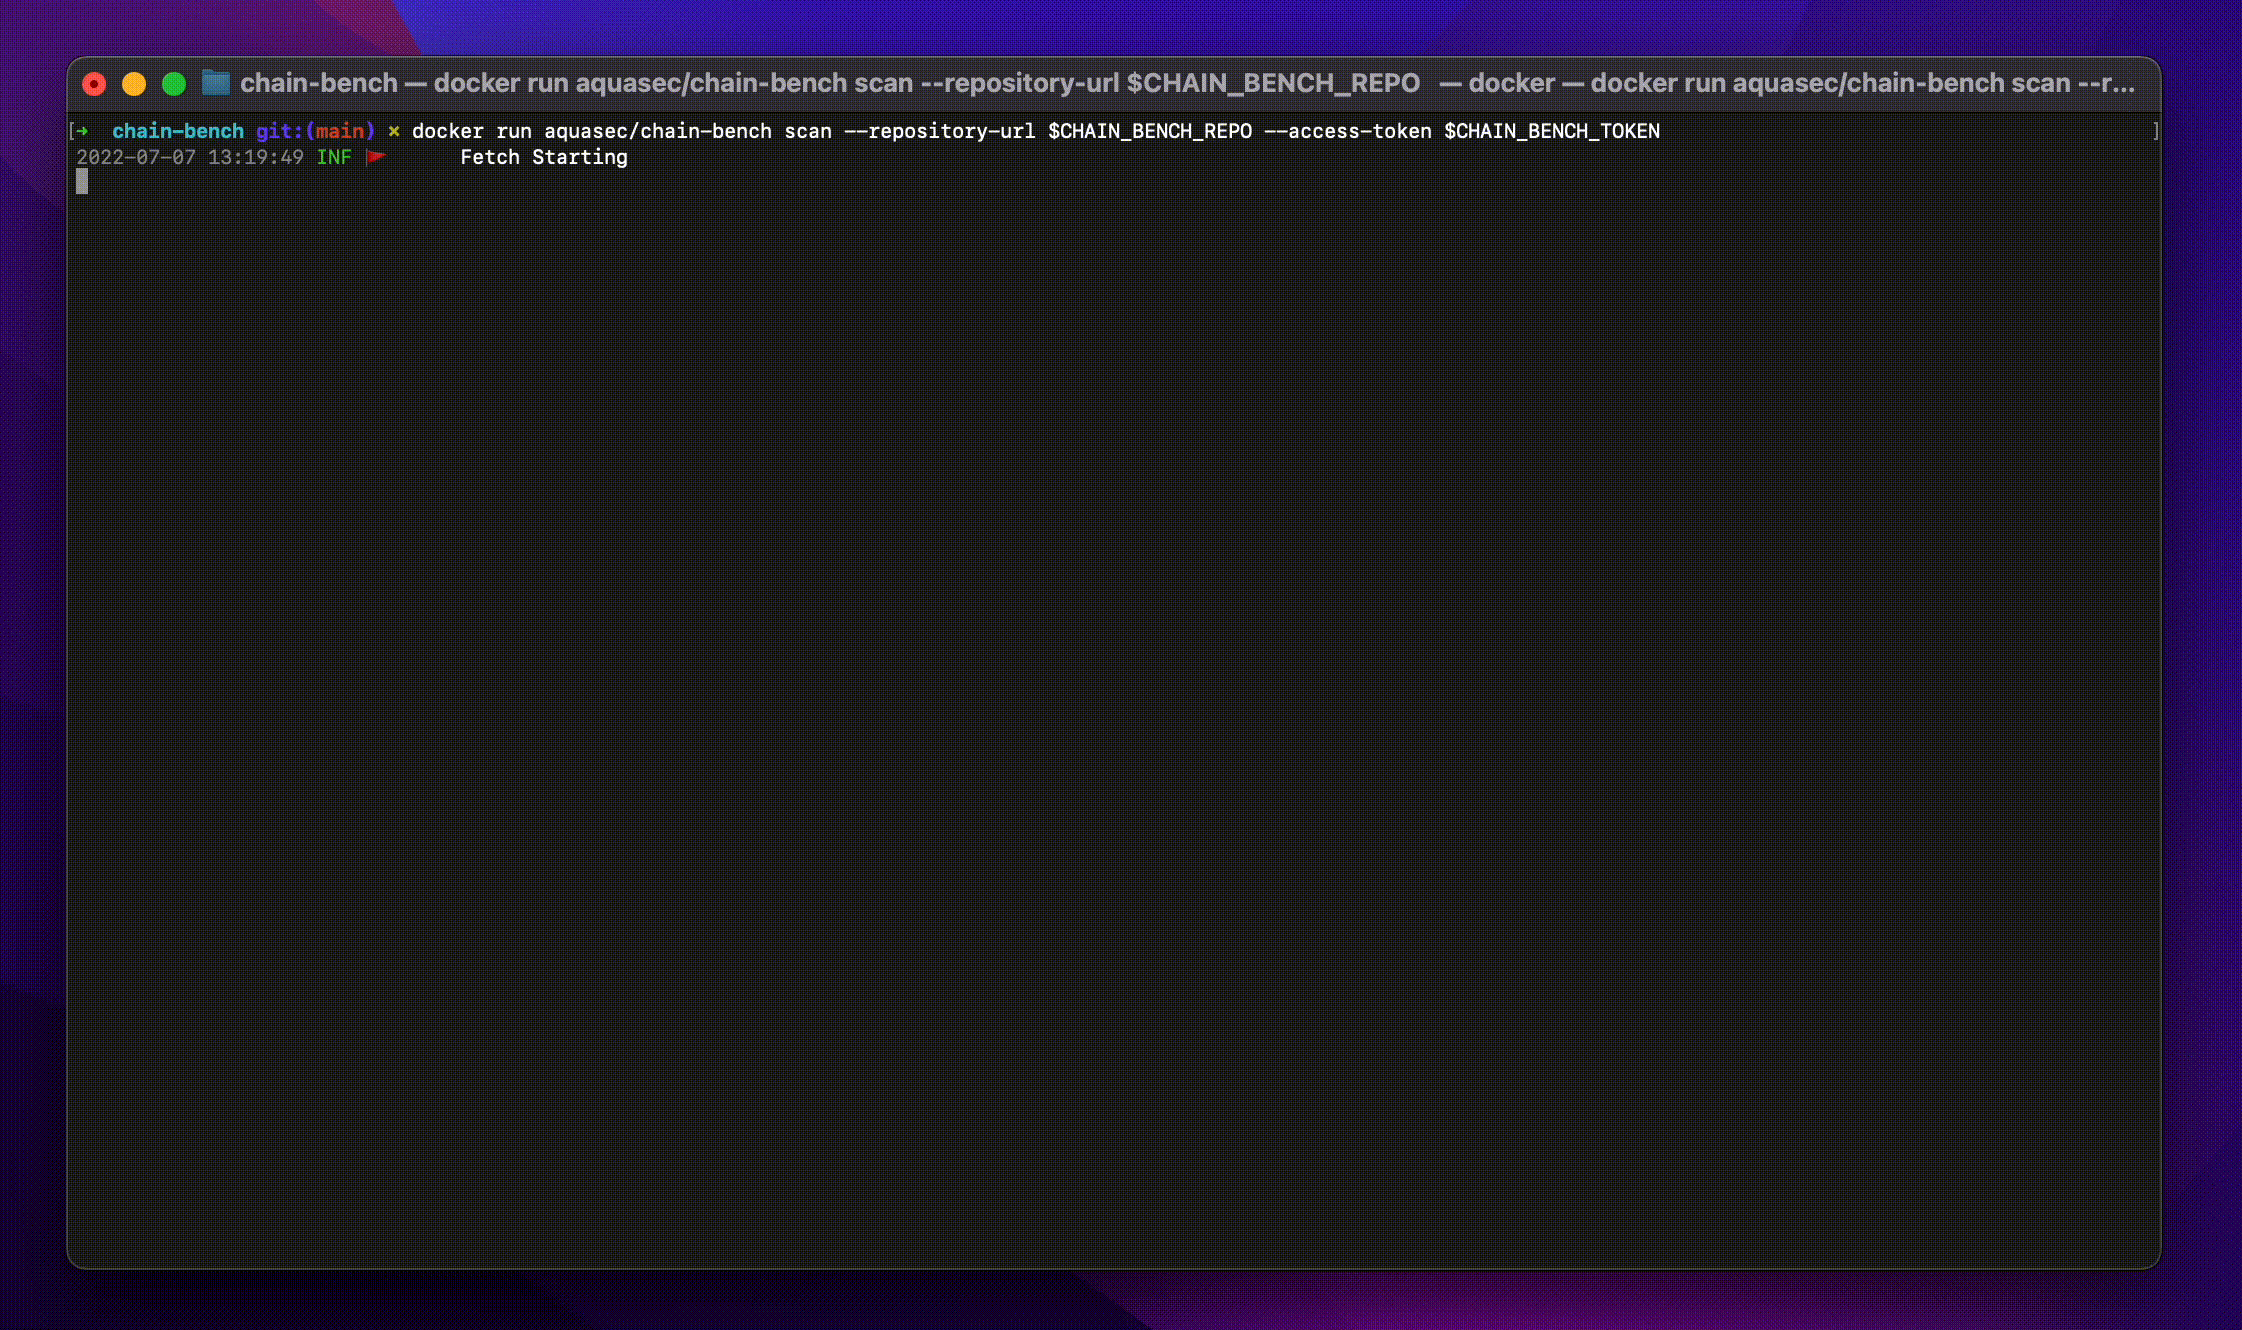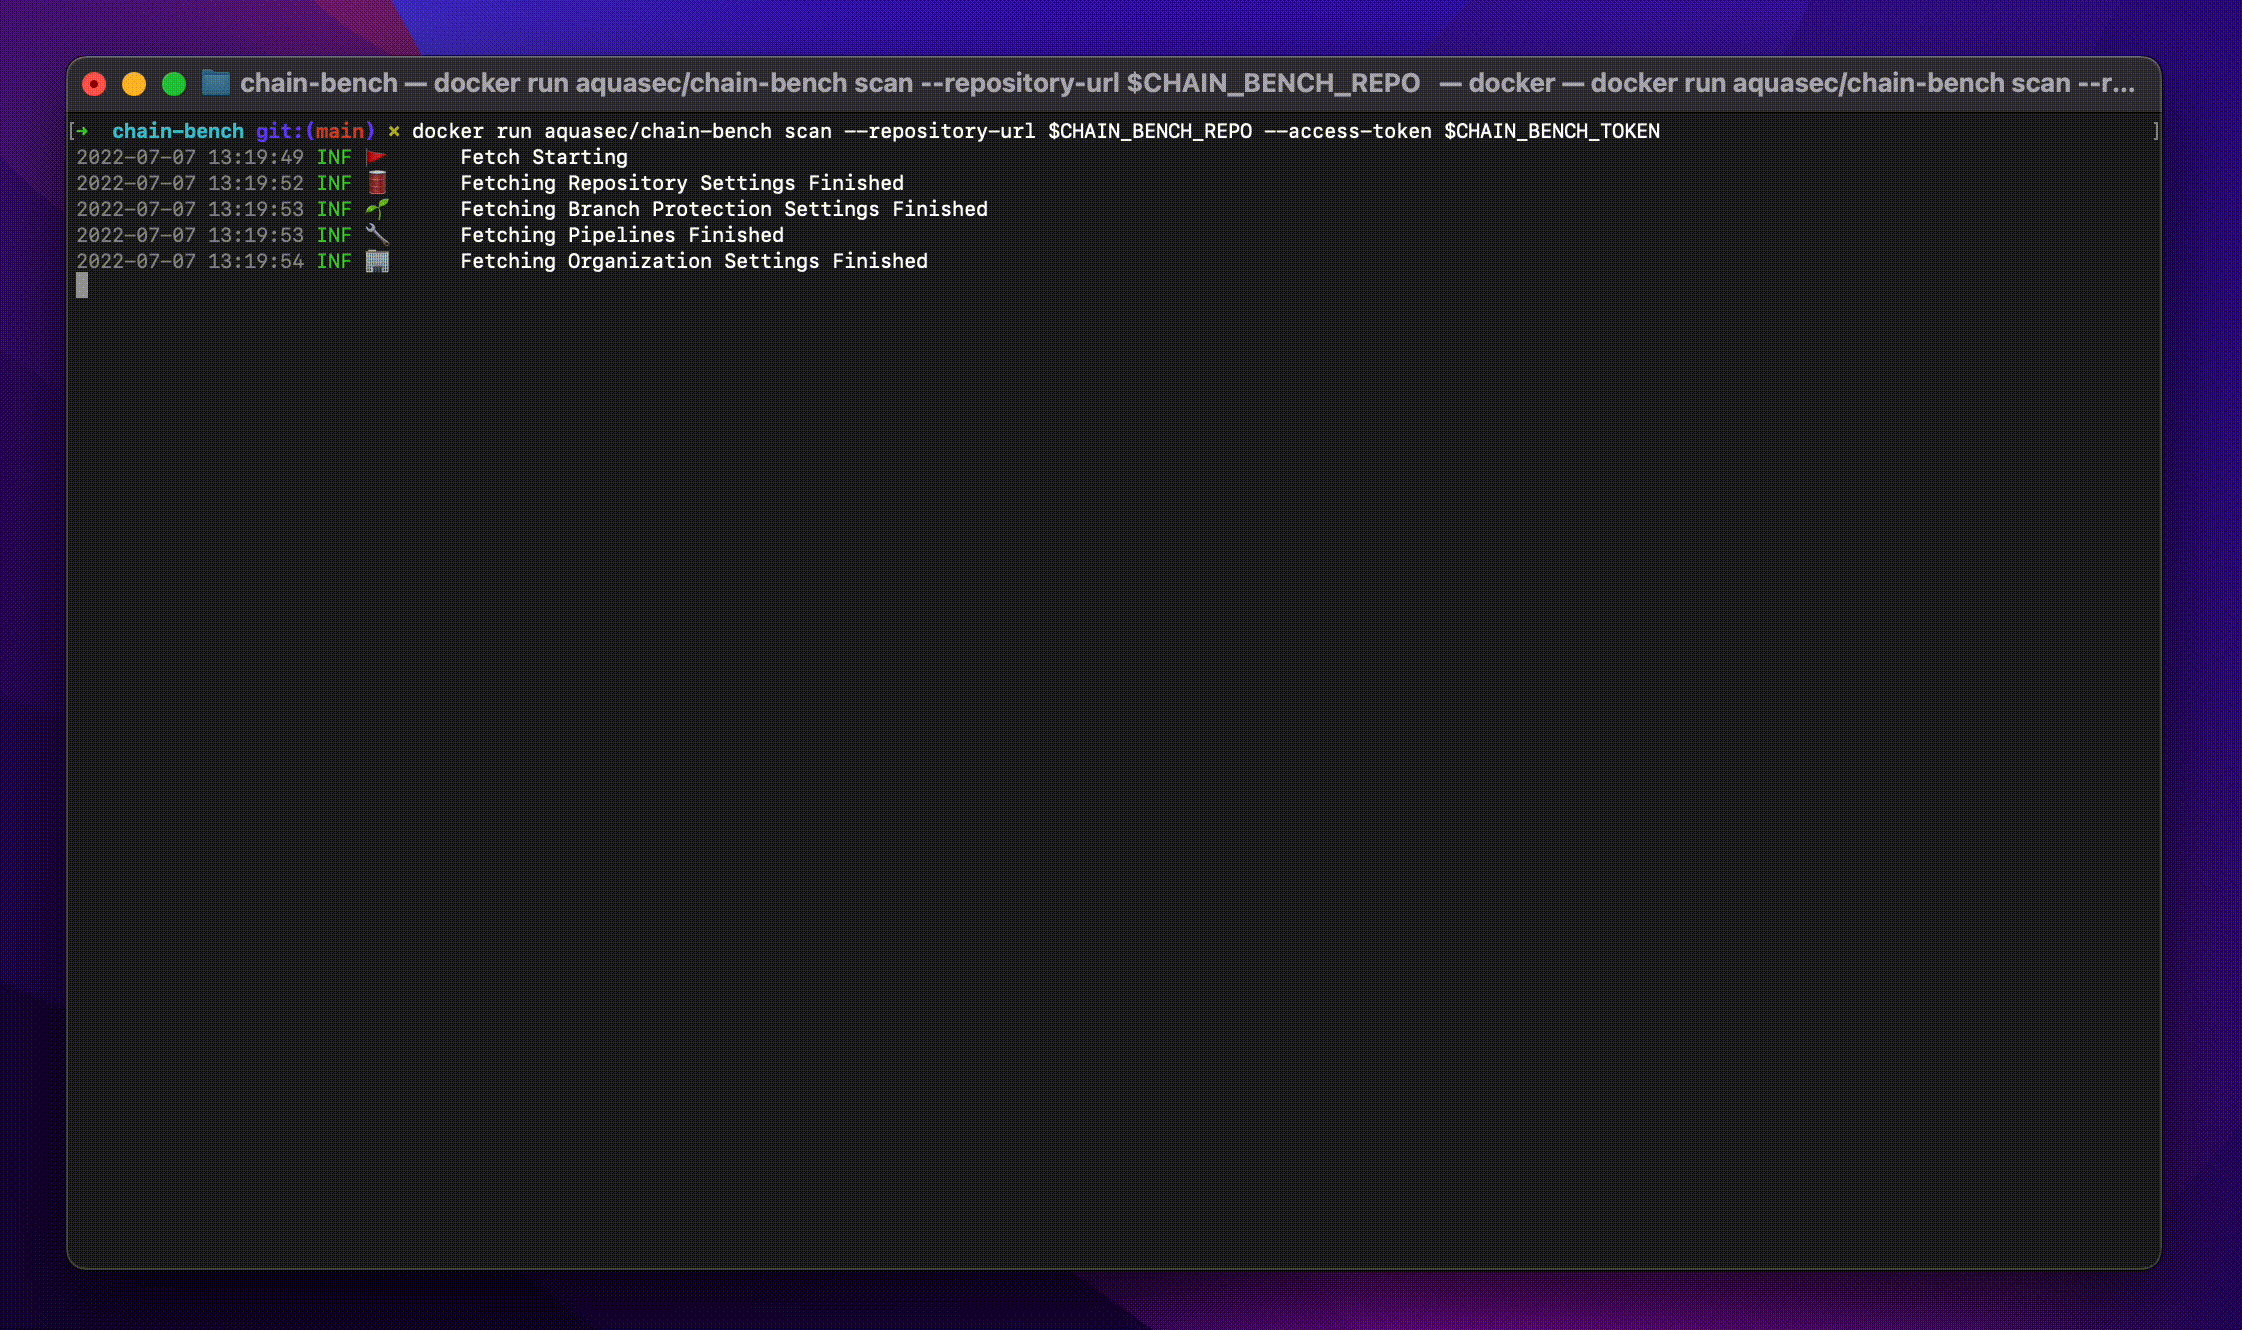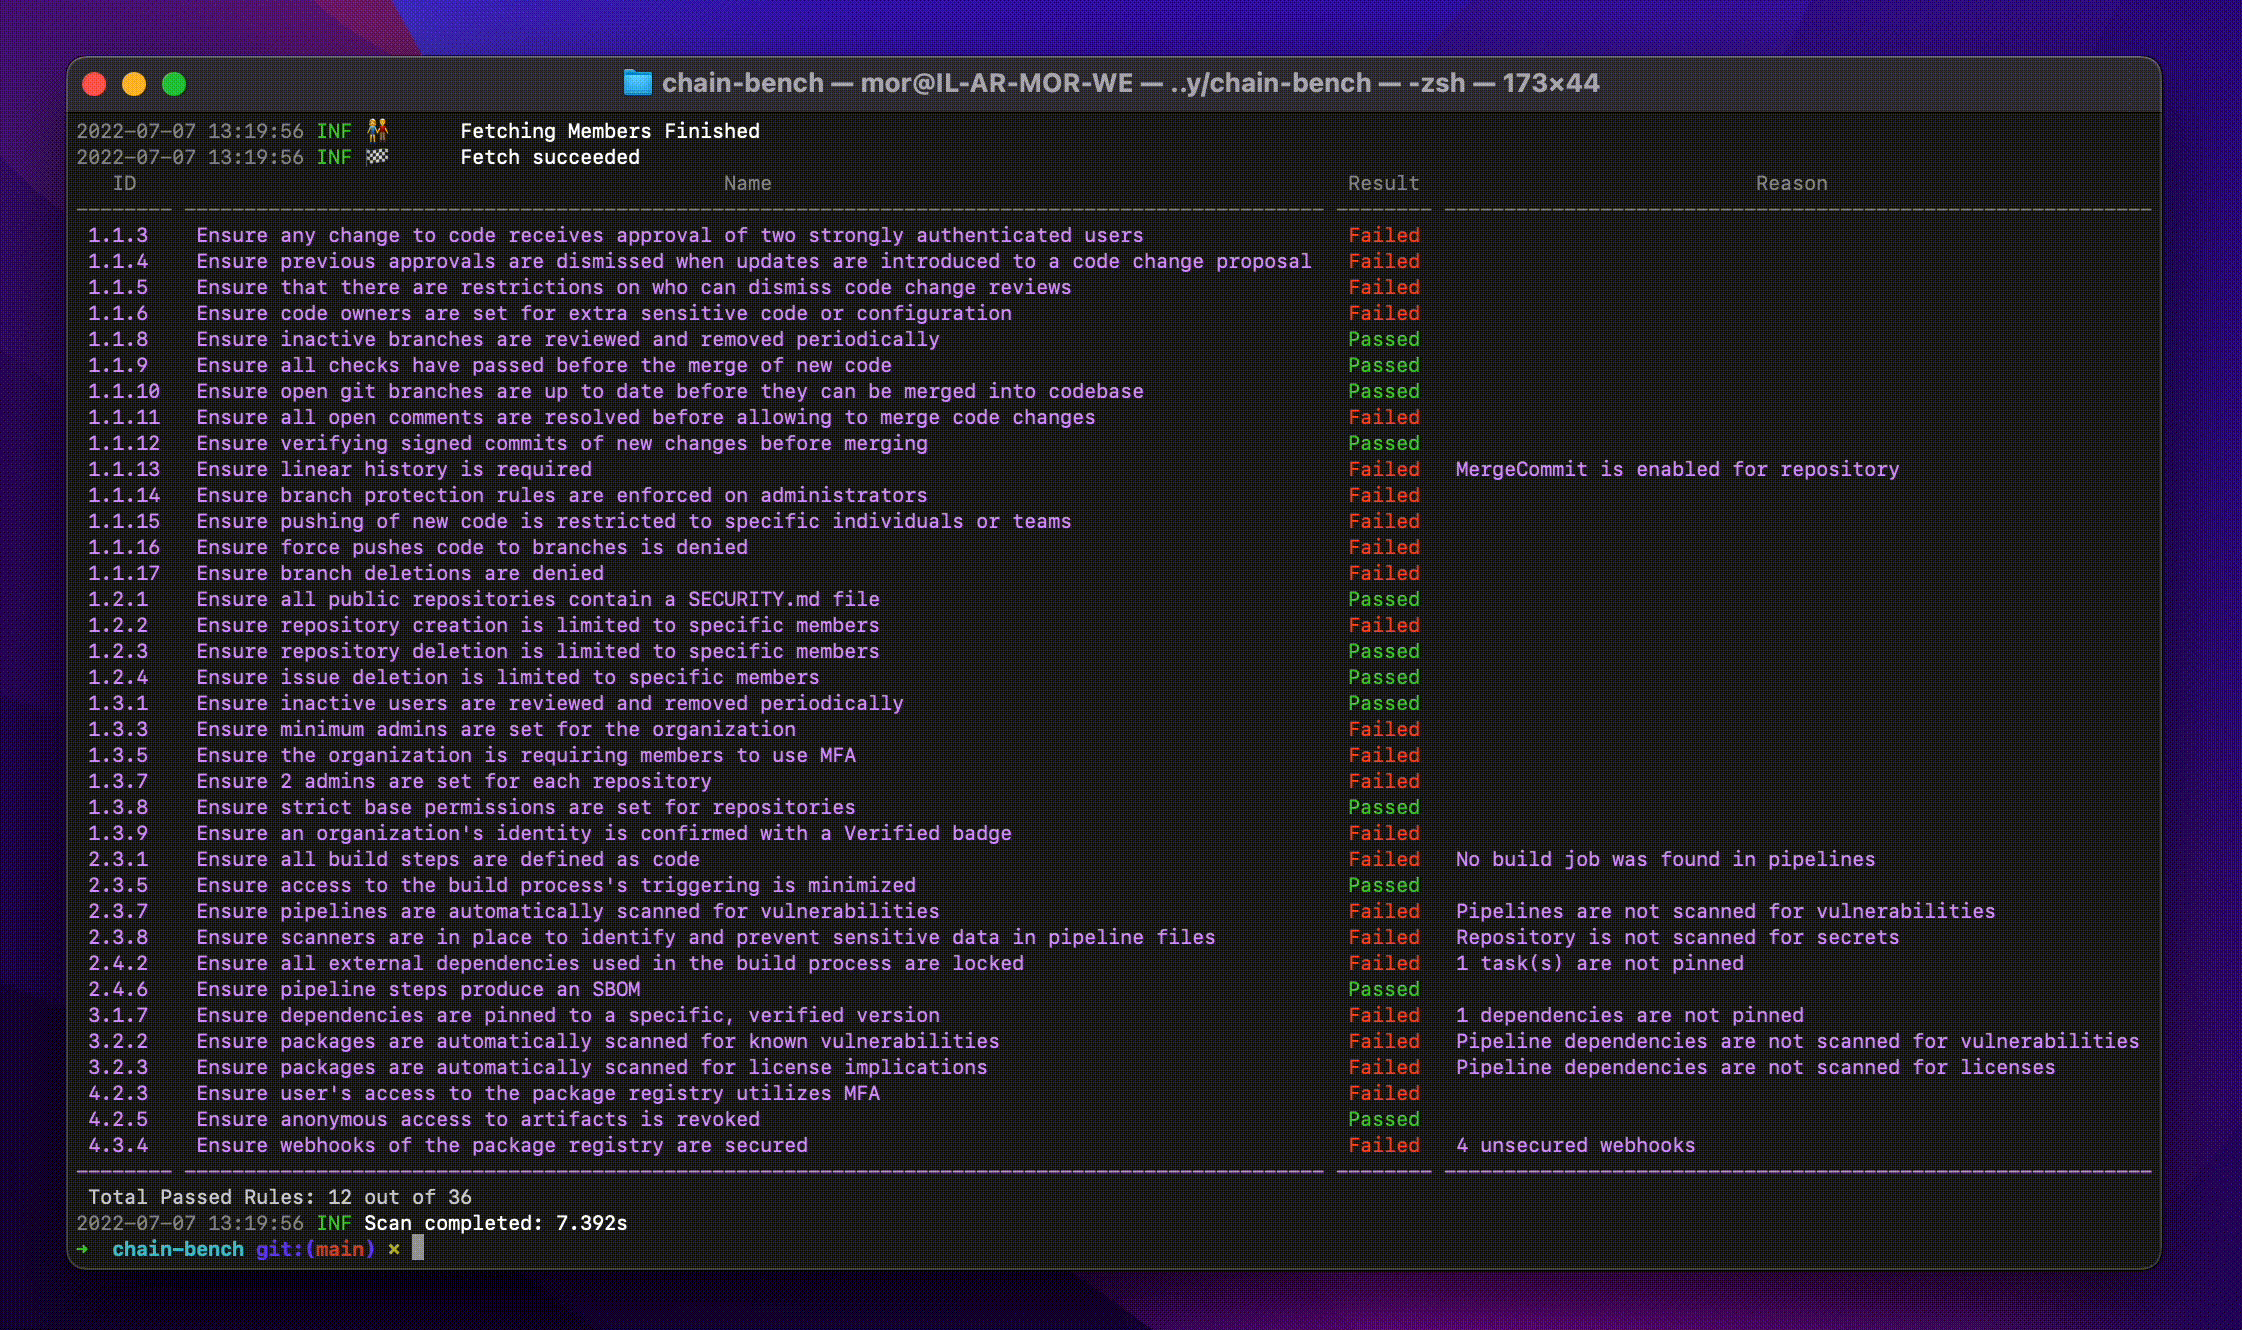 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 sastraadiwiguna-purpleeliteteaming/llamastack-rce-deterministic-supply-chain-exploitation-hardening-framework-cve-2024-50050-
LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
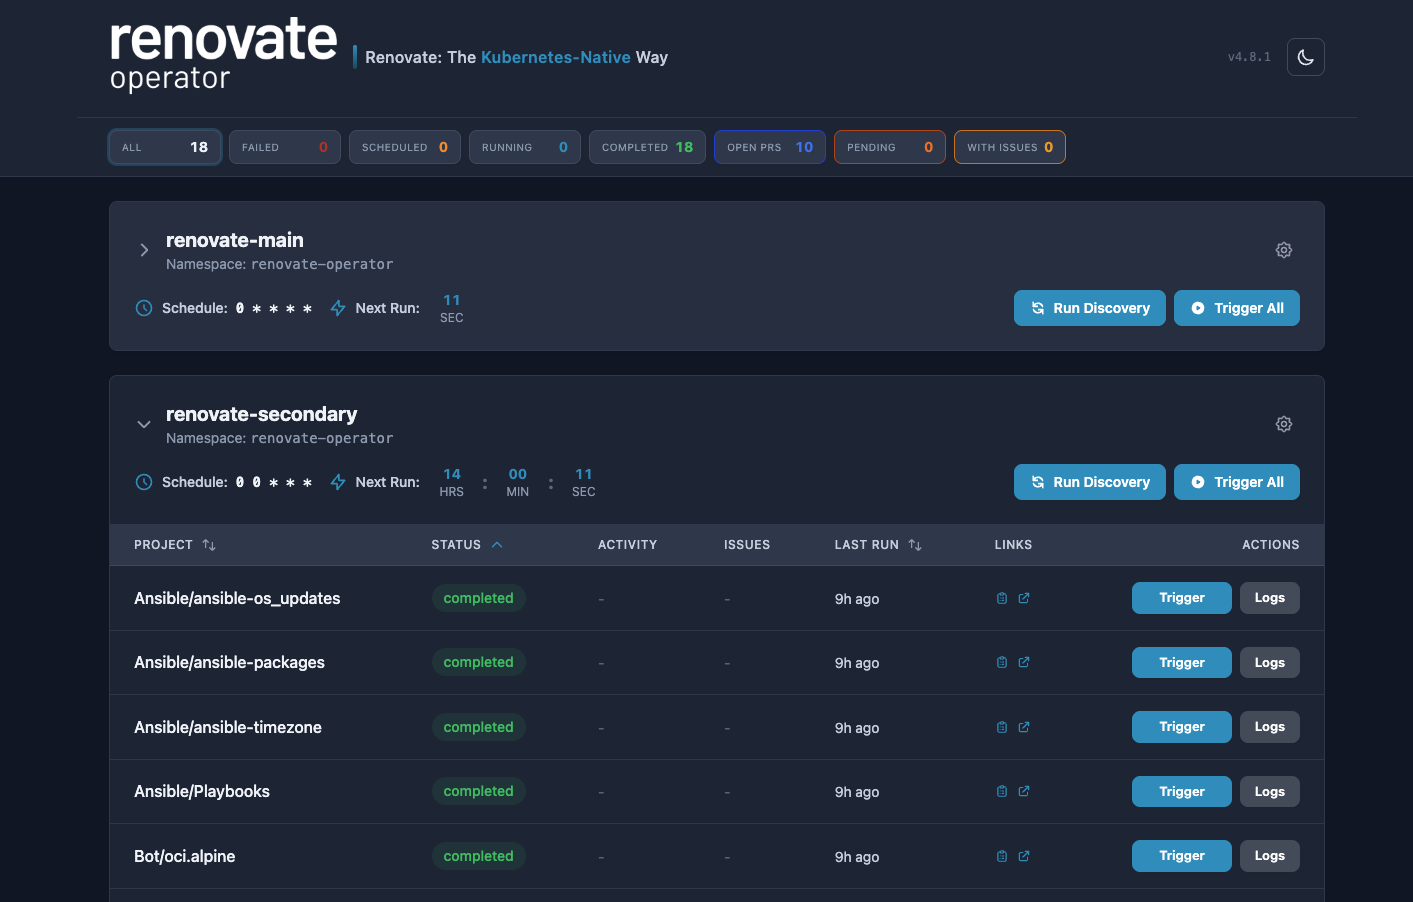 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
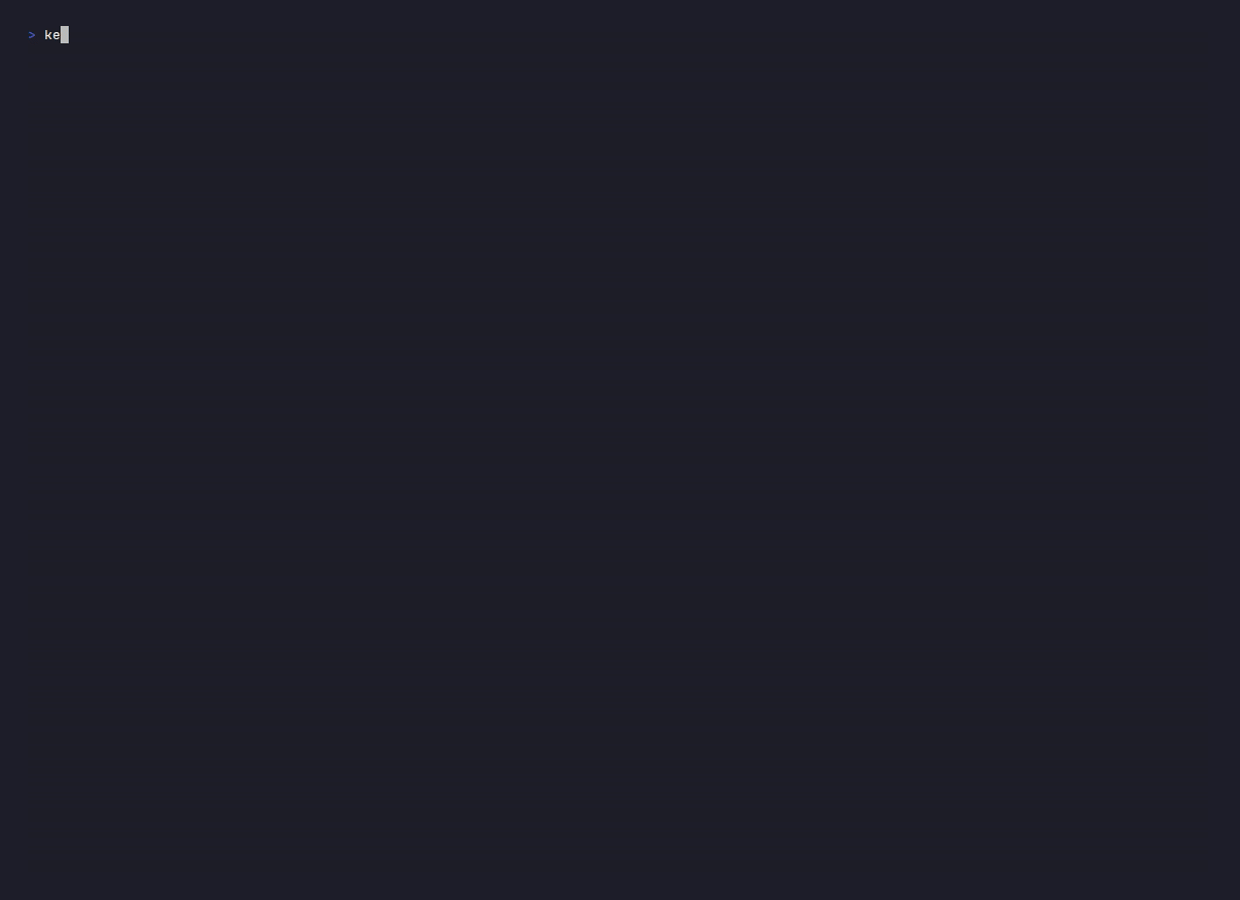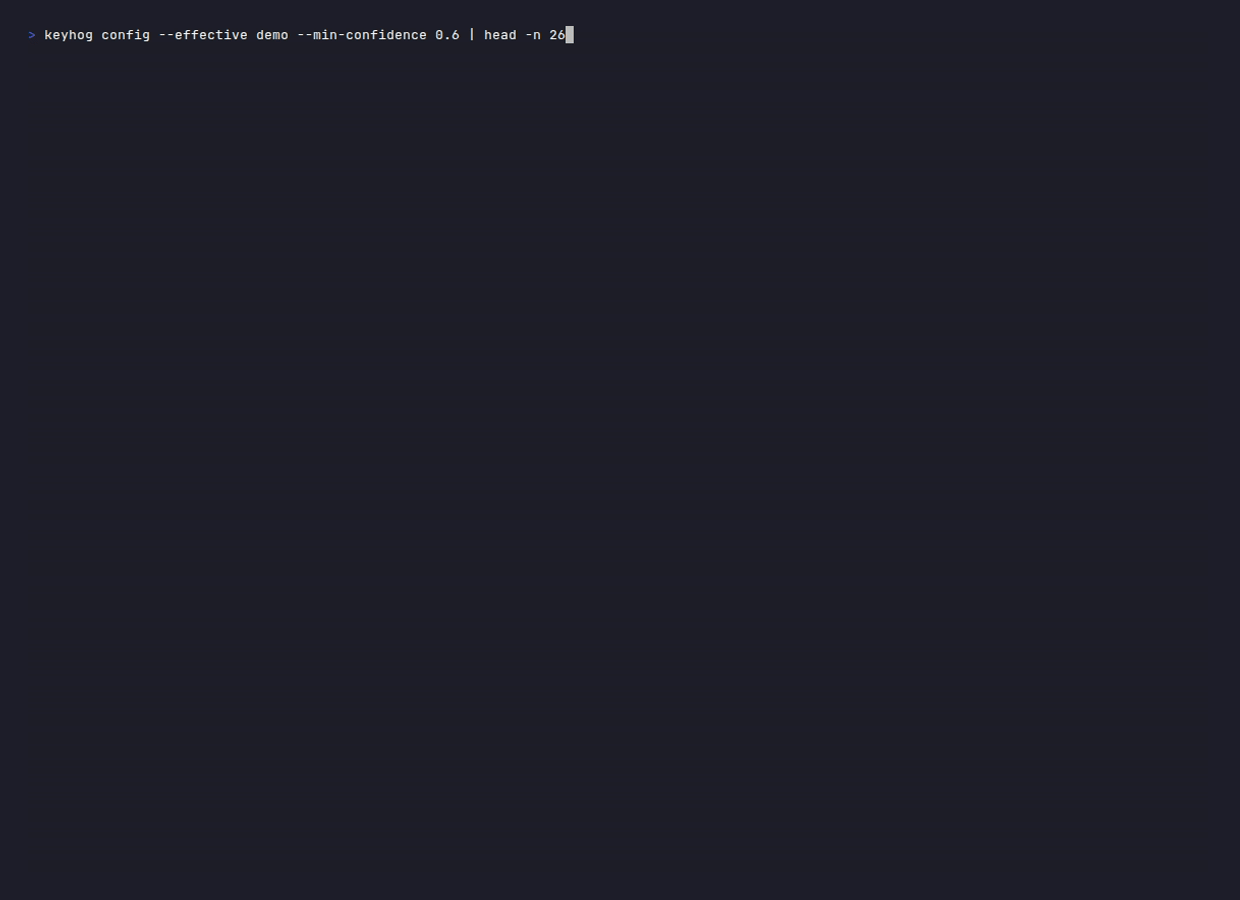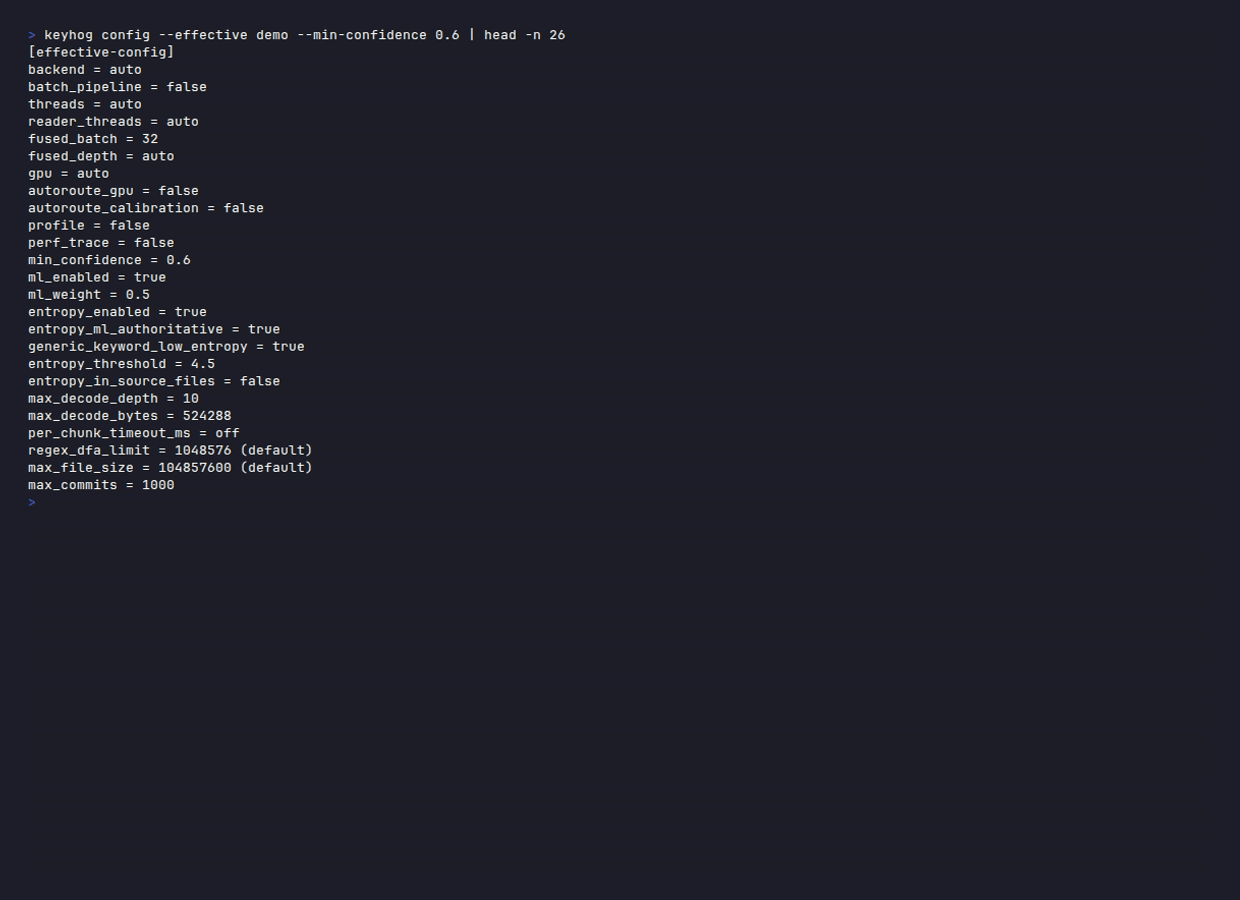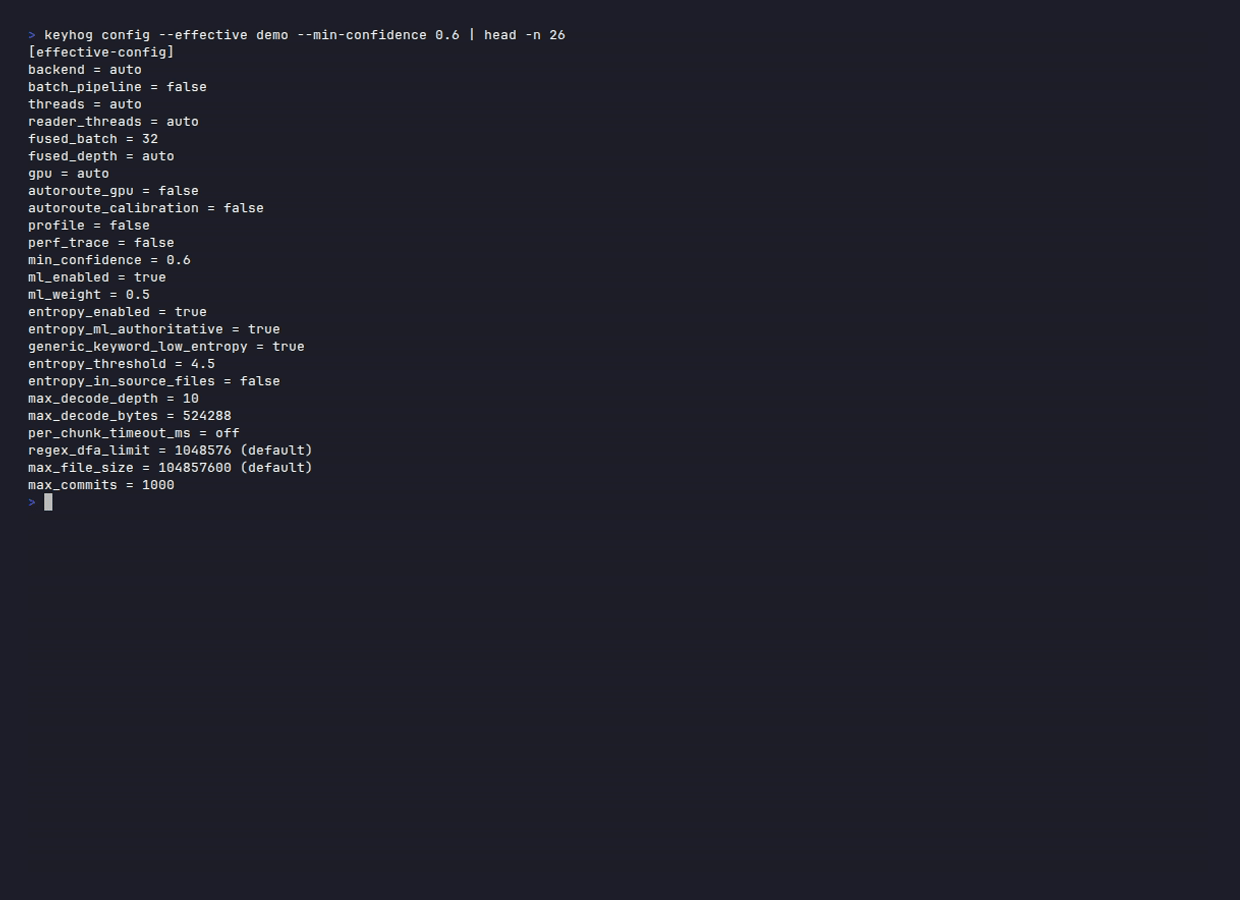 santhreal/keyhog
Open-source secret scanner in Rust
 stevehenderson/lab_xz_backdoor
Some labs looking at the xz backdoor vulnerability (CVE-2024-3094)
 izzyacademy/log4shell-mitigation
Mitigation for Log4Shell Security Vulnerability CVE-2021-44228
 owasp/docker-security
Getting a handle on container security
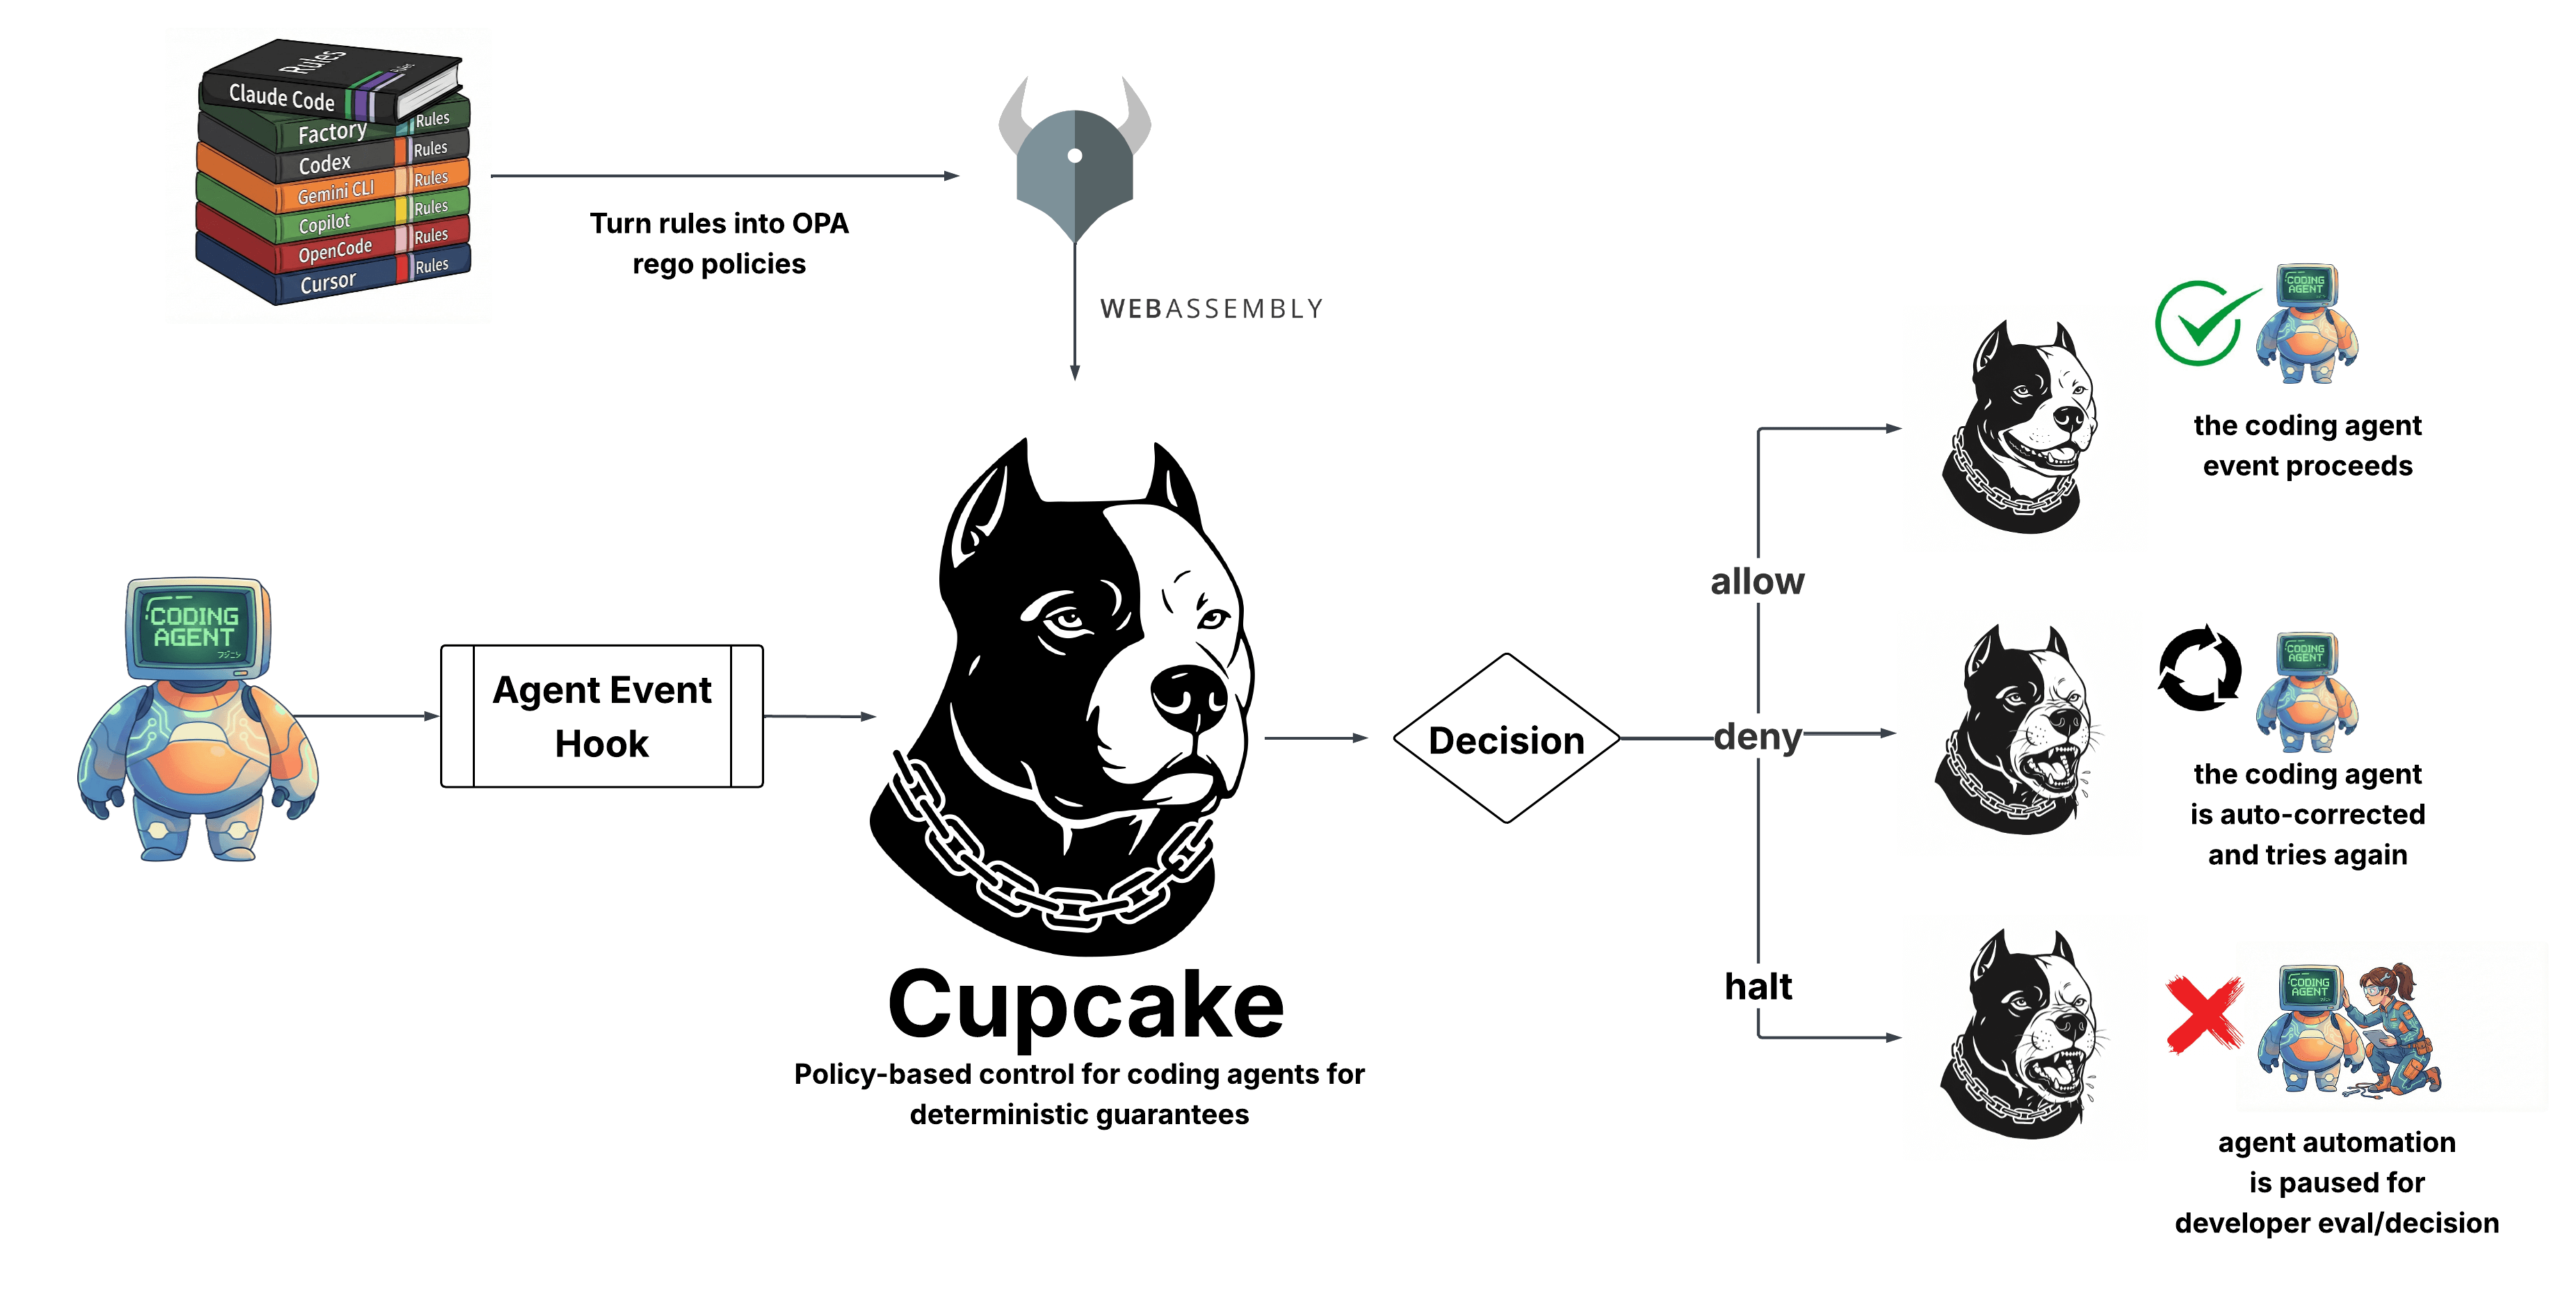 eqtylab/cupcake
A native policy enforcement layer for AI coding agents. Built on OPA/Rego.
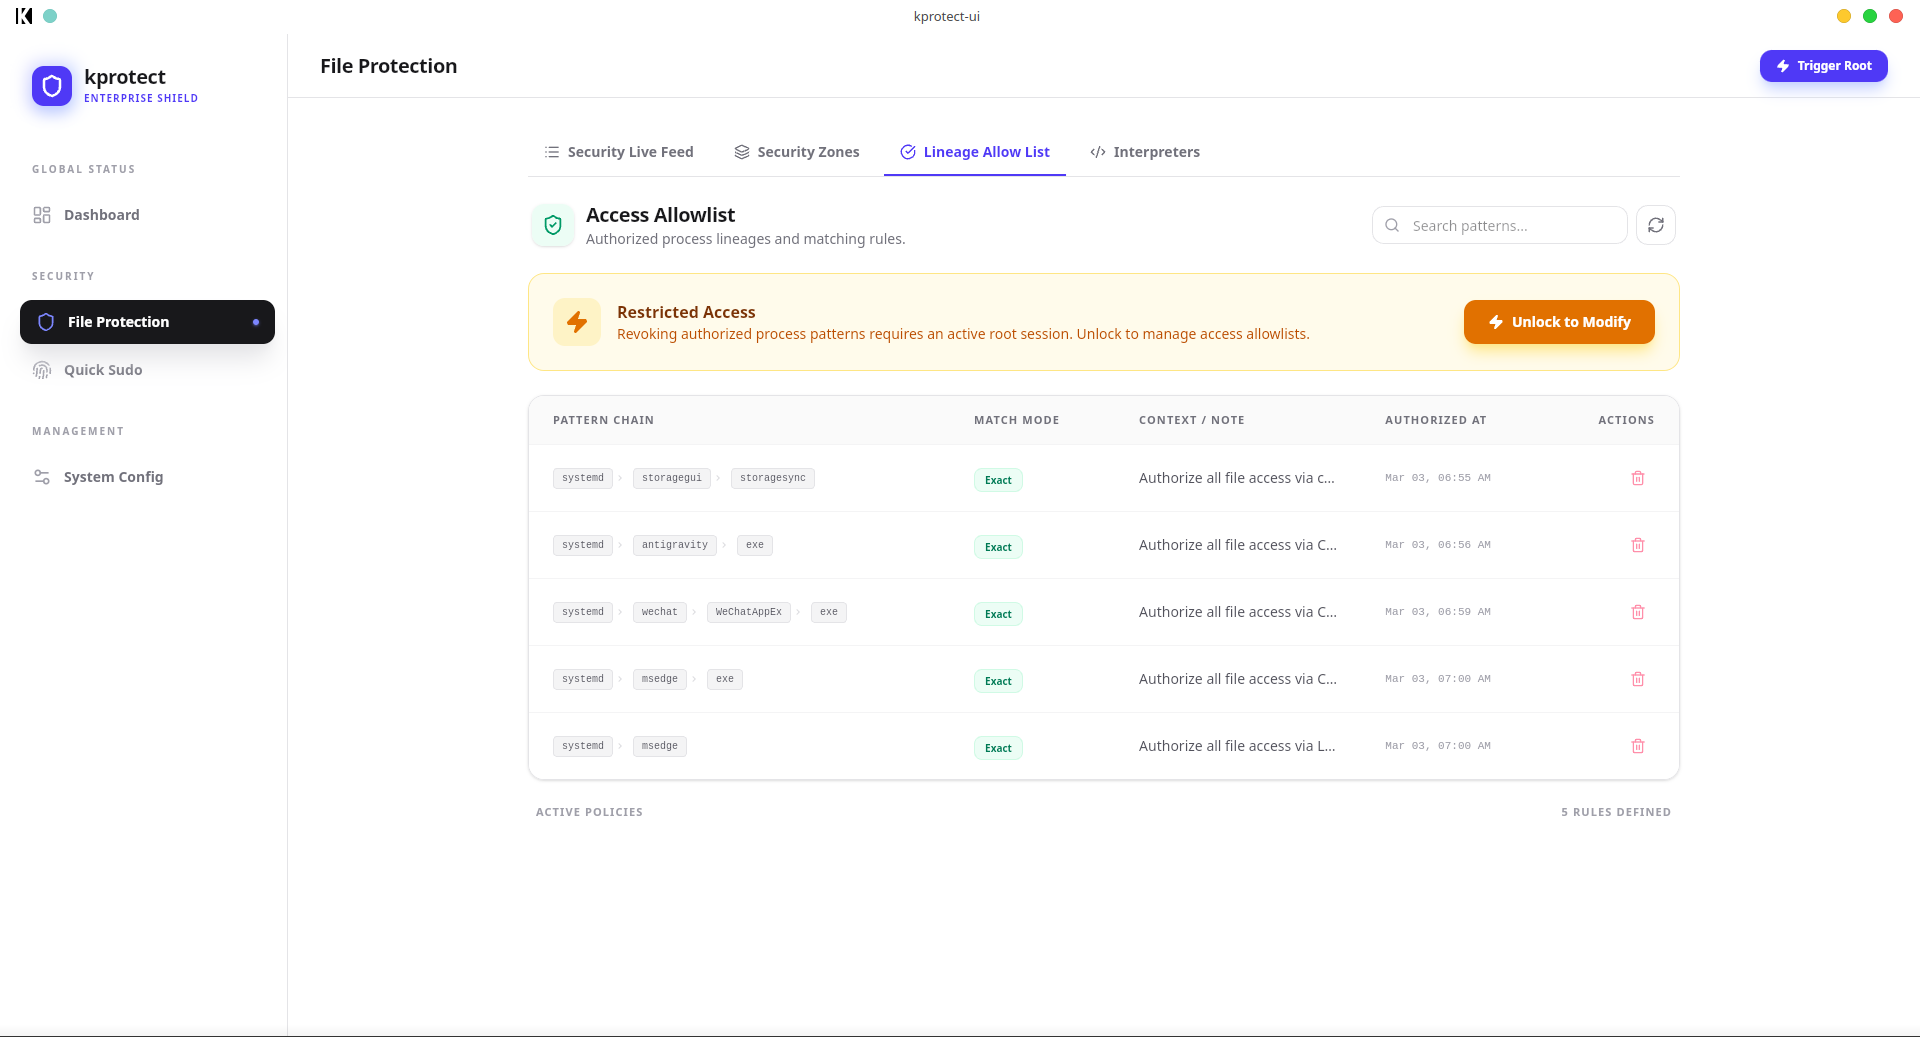 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 wiz-sec-public/githunt
Demos for Black Hat Europe 2025's The Forensic Trail On GitHub: Hunting For Supply Chain Activity
 0xlane/xz-cve-2024-3094
XZ Backdoor Extract(Test on Ubuntu 23.10)
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 renat0z3r0/prefect-cve-2026-5366
PoC for CVE-2026-5366: git argument injection in Prefect's GitRepository leading to RCE on the worker.
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box