
Archived
Cordon
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
configuration-auditingcontainer-securitydevsecops+6
2
 happyhackingspace/claude-code-backdoor-check
Read-only scanner for the backdoored Claude Code 2.1.313 extension (Cursor marketplace, Oct 2026): SSH key, persistence, reverse tunnel. macOS +…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 anteater/anteater
Anteater - CI/CD Gate Check Framework
 odomojuli/regextokens
list of regex patterns for oauth / api tokens with provided source
 disrex-group/stylesmuggler-adobe-patches-mageos
composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Mage-OS stores, via cweagans/composer-patches. Companion to…
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix
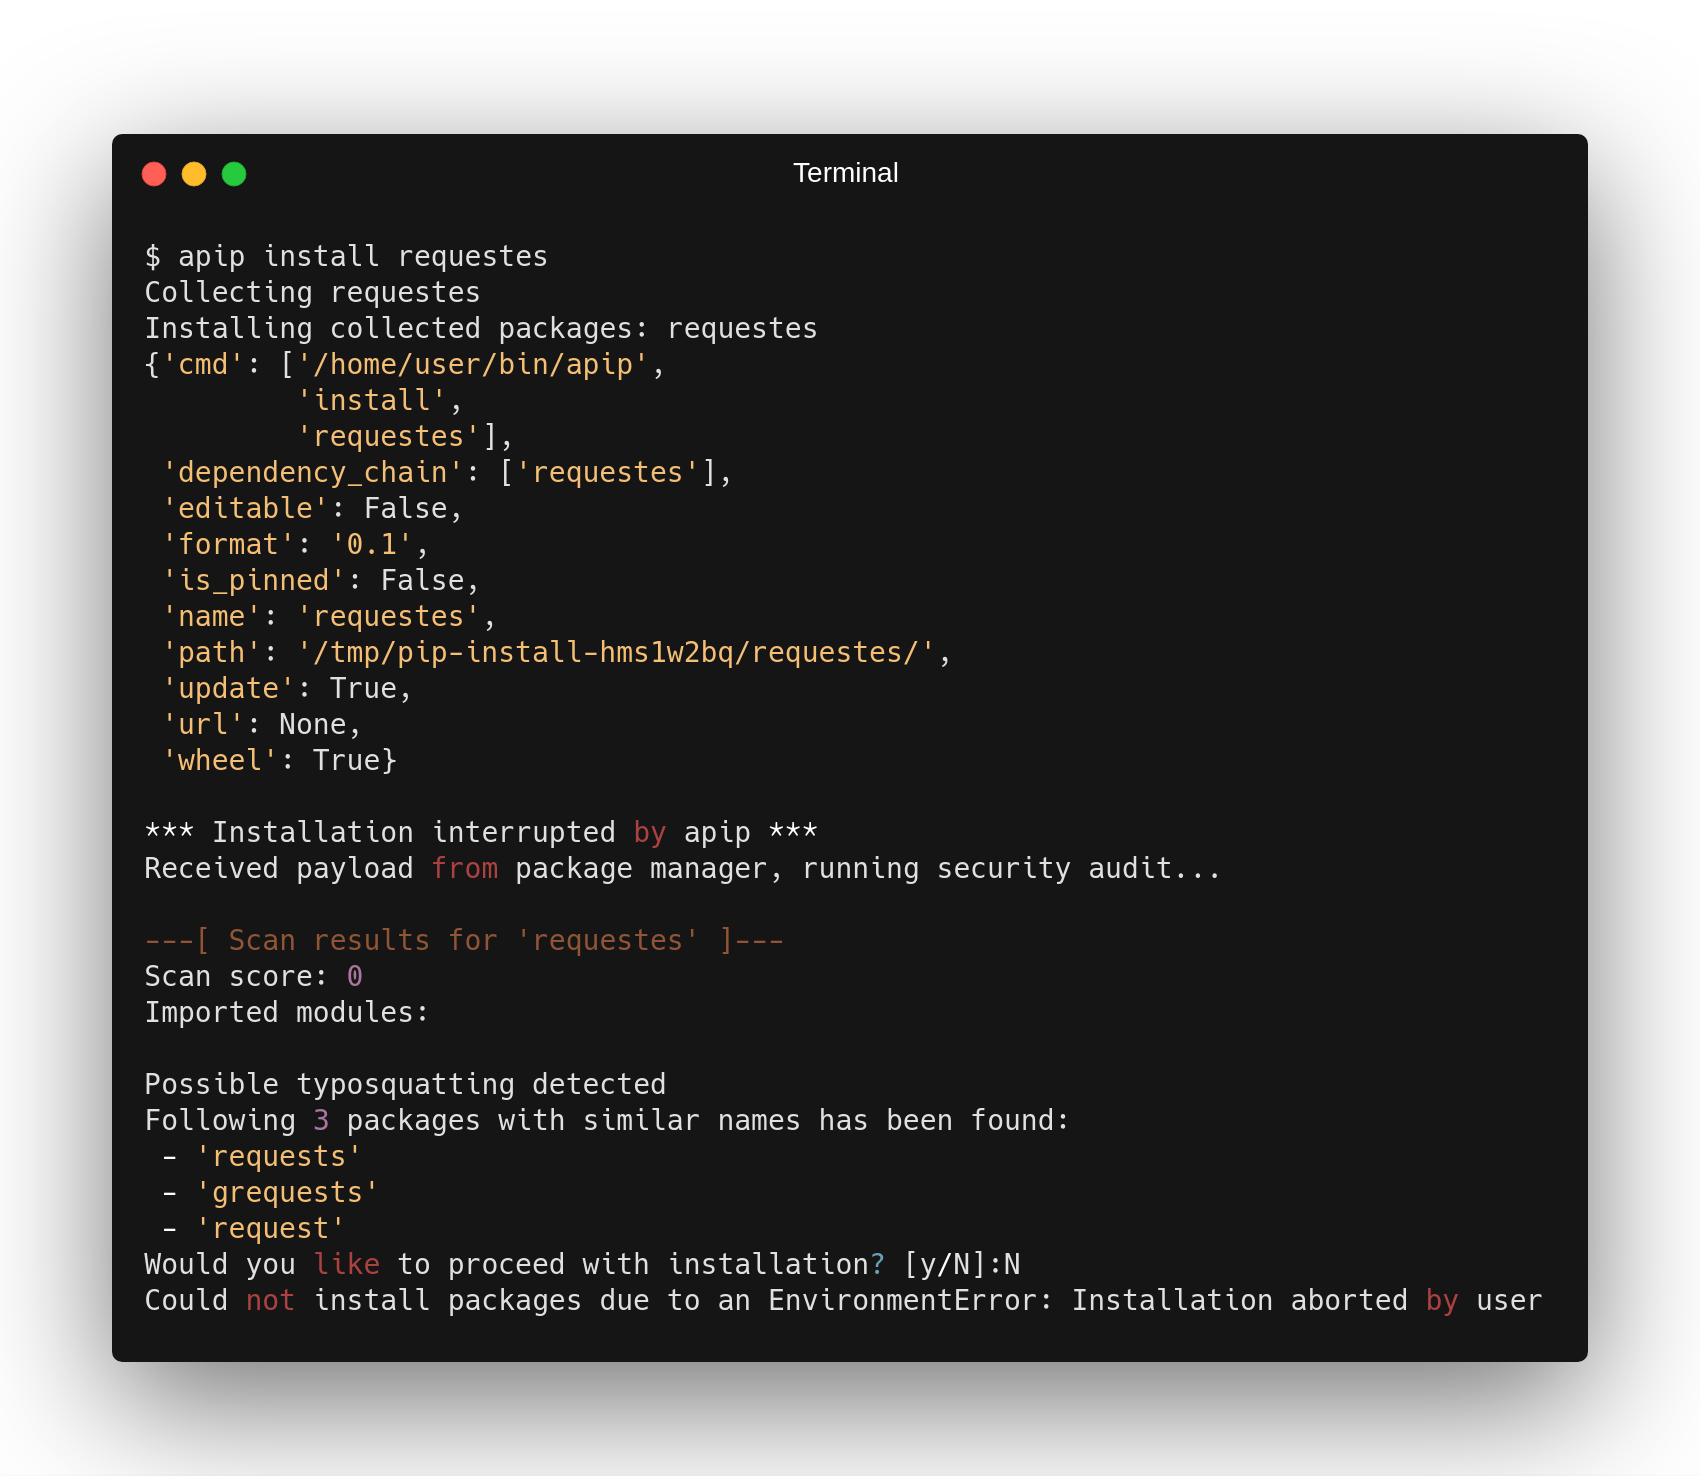 rootlug/aura
Project Aura: Security auditing and code introspection
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 dragon-lady/push-guard
Local Git pre-push hook and filesystem scanner that detects likely secret leaks, redacts matched values, and blocks pushes without telemetry or…
 giz-berlin/quasar-app-webpack-json5-vulnerability
Minimal reproduction of CVE-2022-46175 demonstrating a JSON5 prototype pollution vulnerability in Quasar webpack projects for security education and…
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428
 leetxyz/cve-2021-44228-advisories
List of company advisories log4j
 przemoc/xz-backdoor-links
apocalypxze: xz backdoor (2024) AKA CVE-2024-3094 related links
 rubenmamo/cve-2017-0248-test
Sample project to test using Microsoft.CodeDom.Providers.DotNetCompilerPlatform 2.0.1 causing CVE-2017-0248
 jeremylong/dependencycheck
The dependency-check repository has moved: