
CVE-2025-69604
 graypixel2121/cve-2025-69604
Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…
educationexploitationprivilege-escalation+2
graypixel2121/cve-2025-69604Proof-of-concept exploit for CVE-2025-69604, demonstrating privilege escalation via malicious package installation in SuperDuper backup tasks on…
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
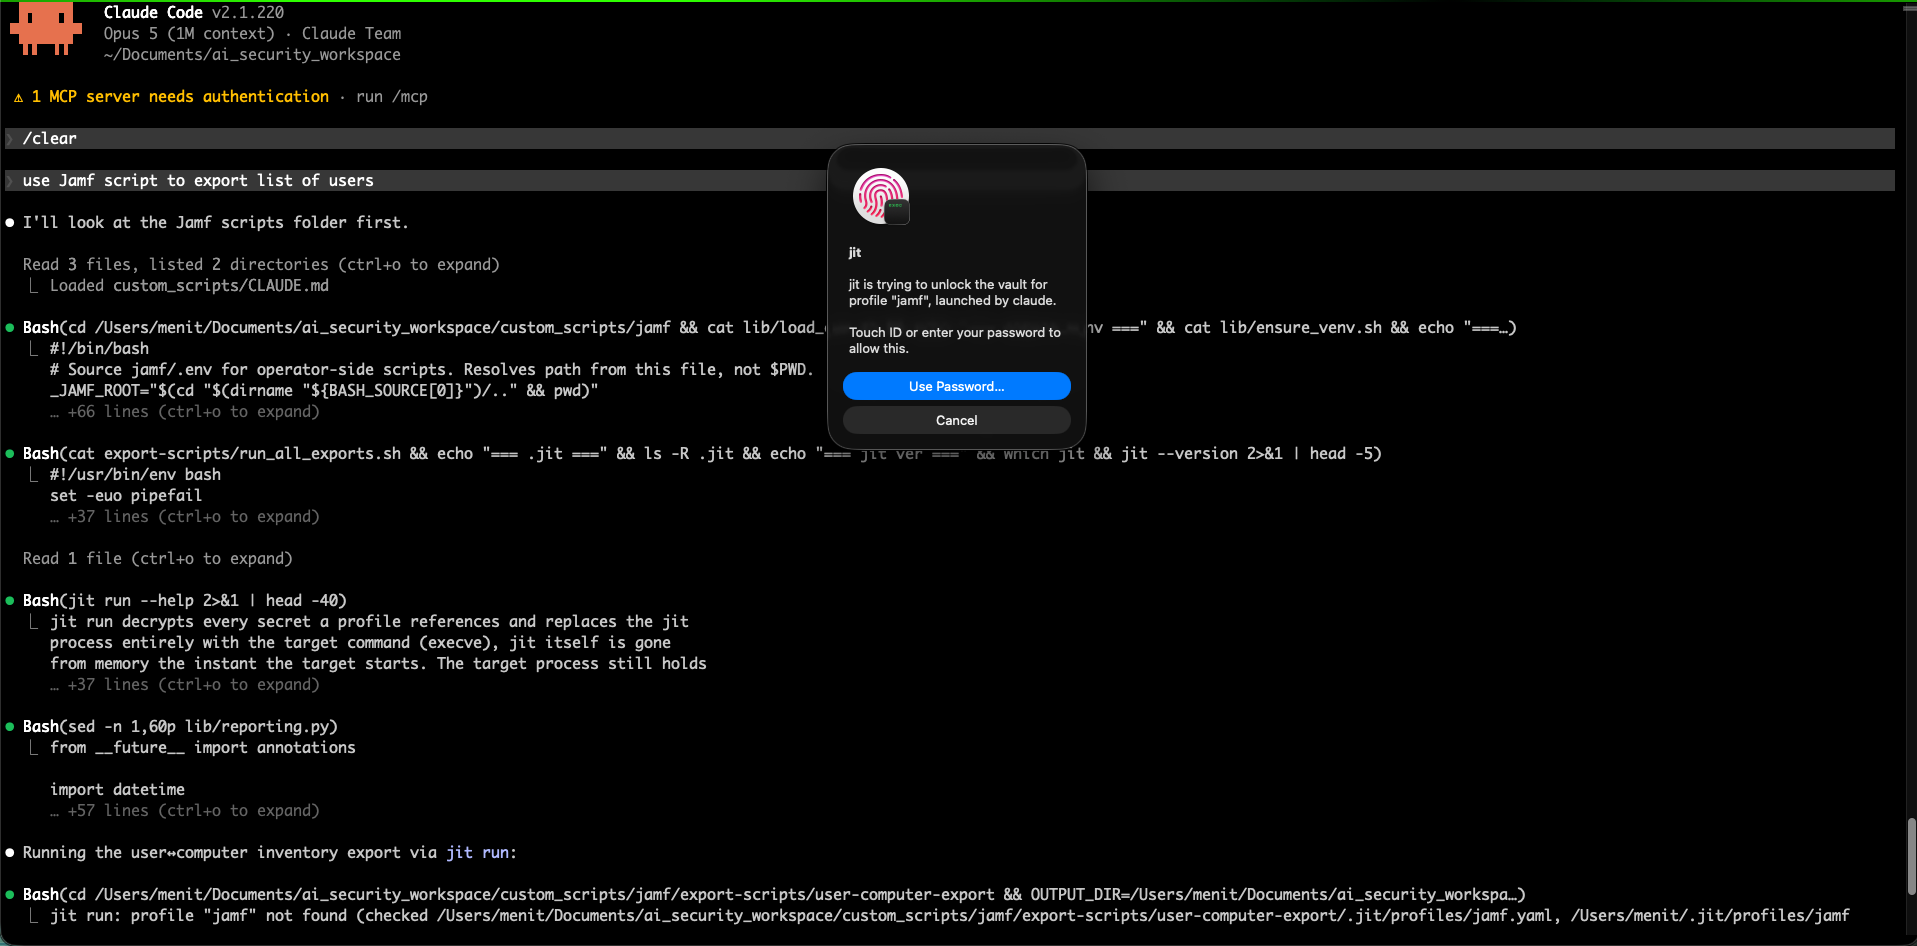 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
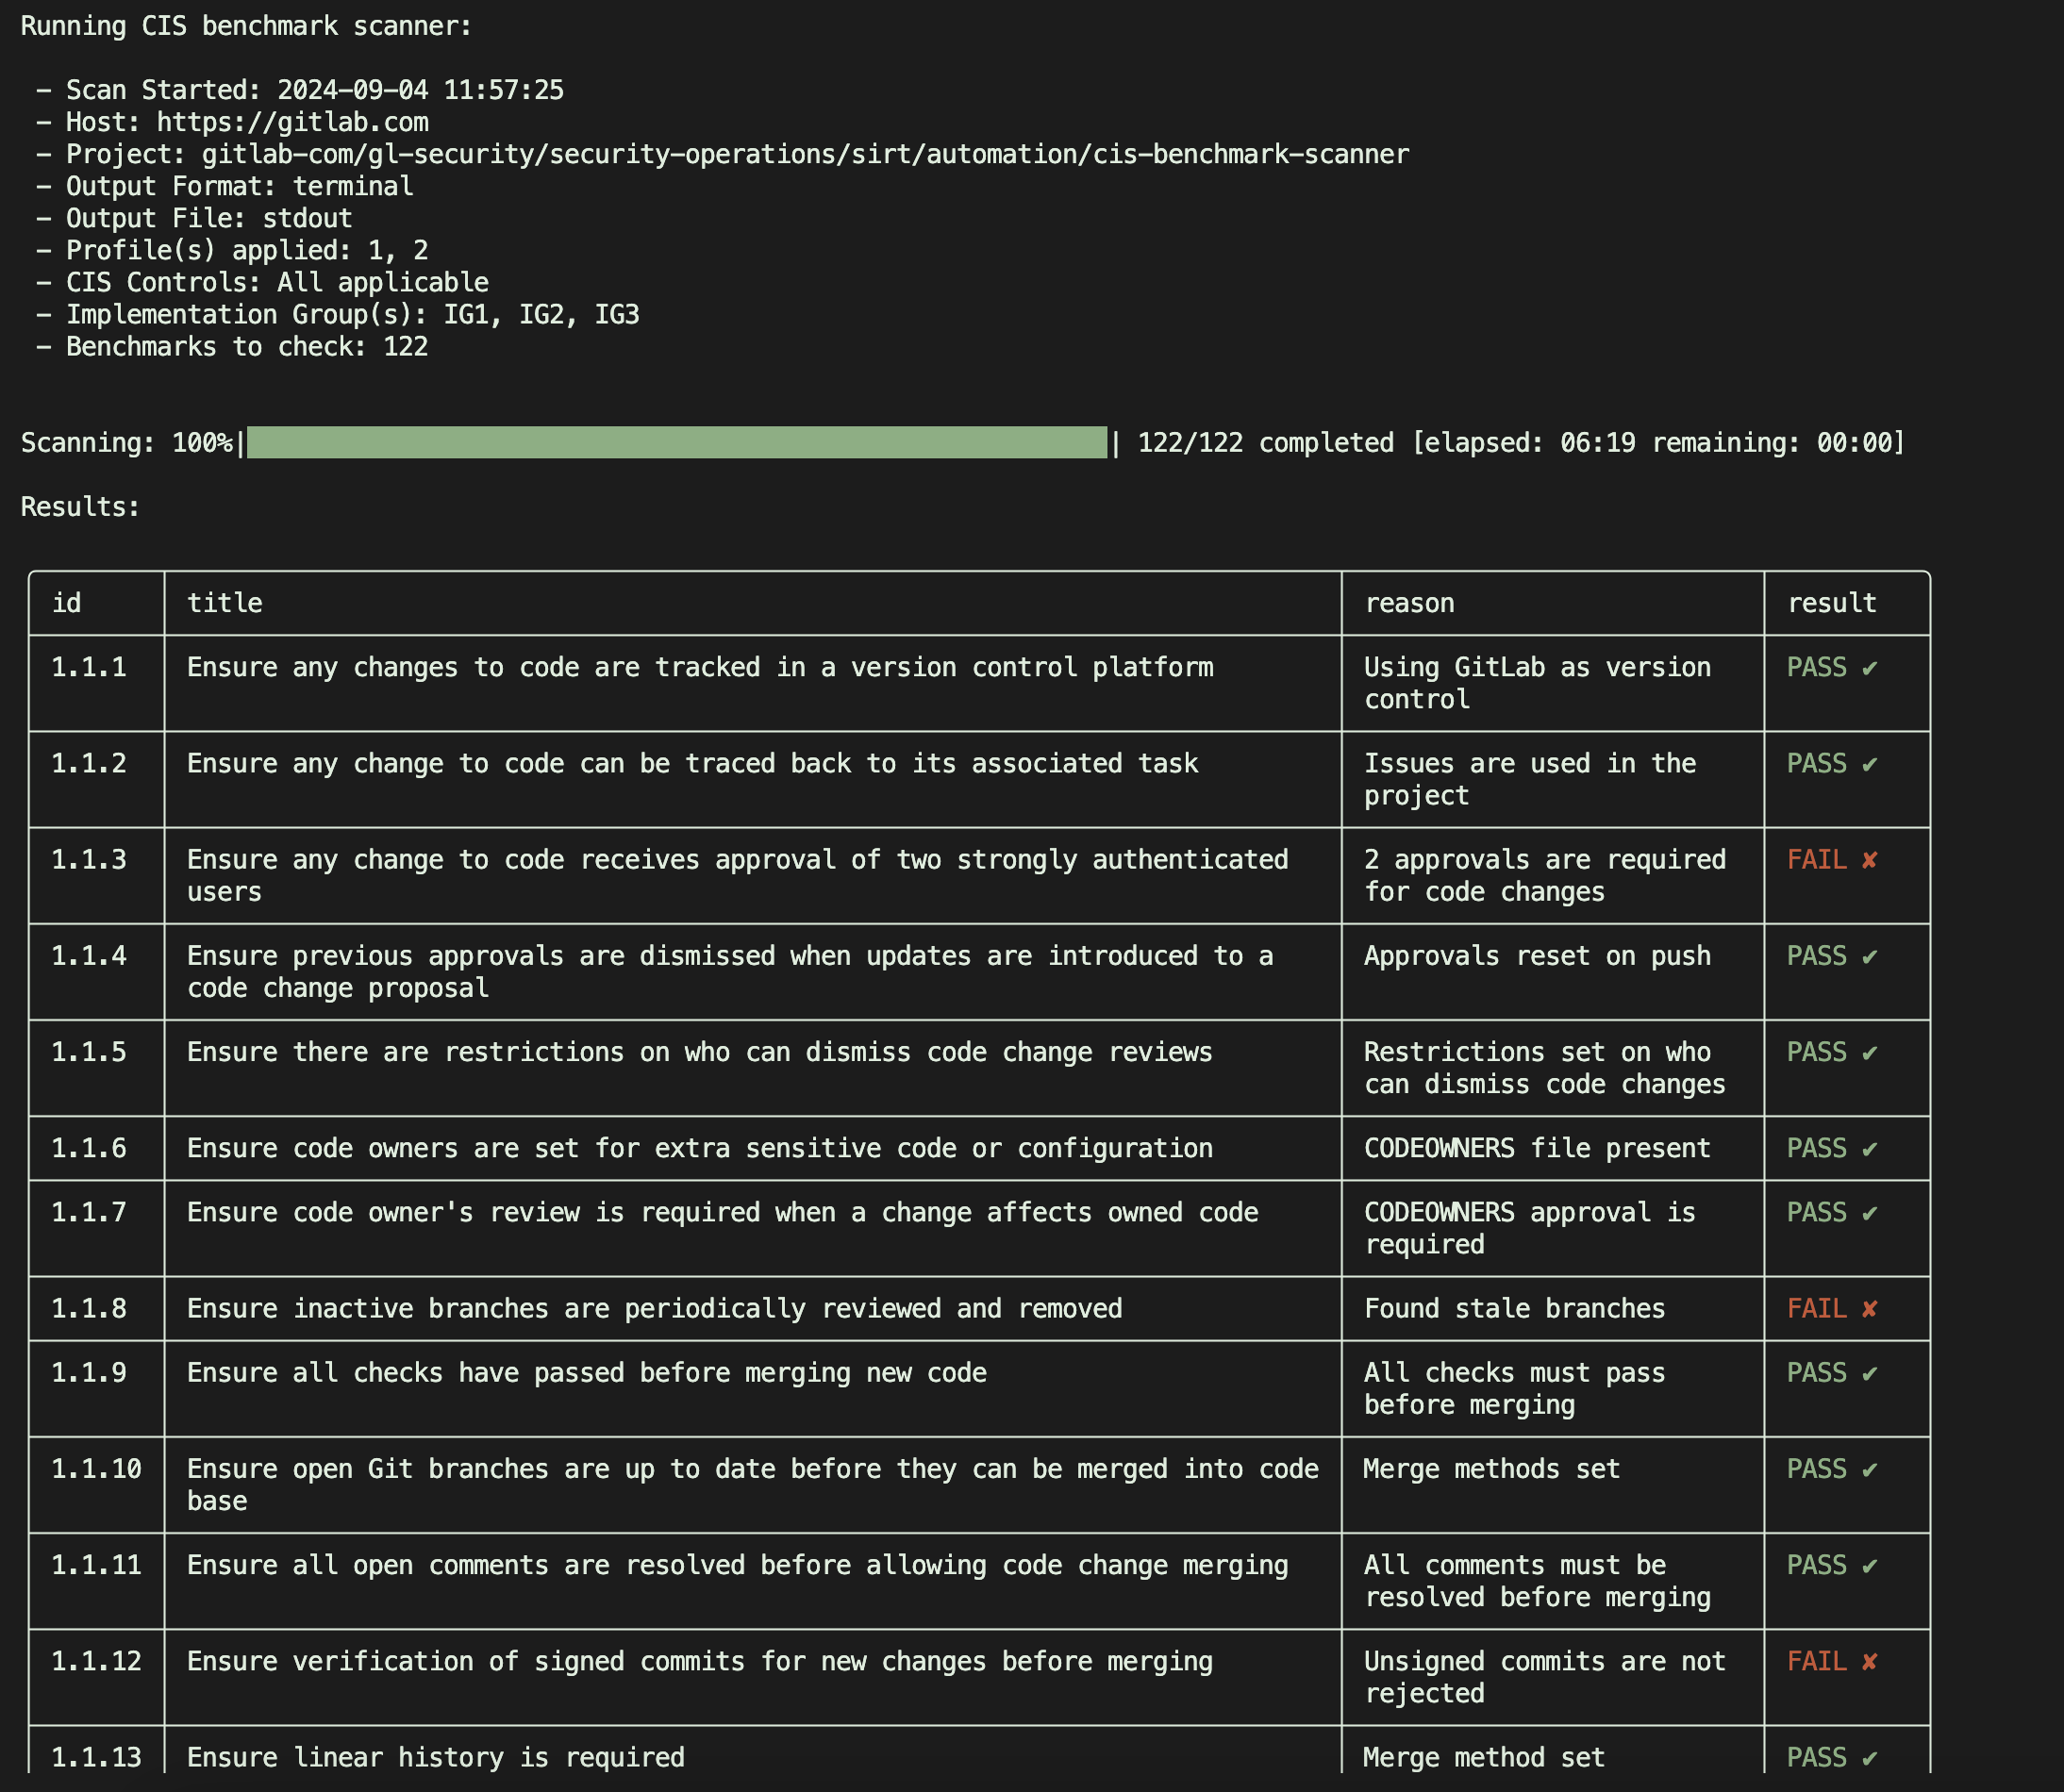
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 oopsiewoopsie/mc-log4j-patcher
CVE-2021-44228 server-side fix for minecraft servers.
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
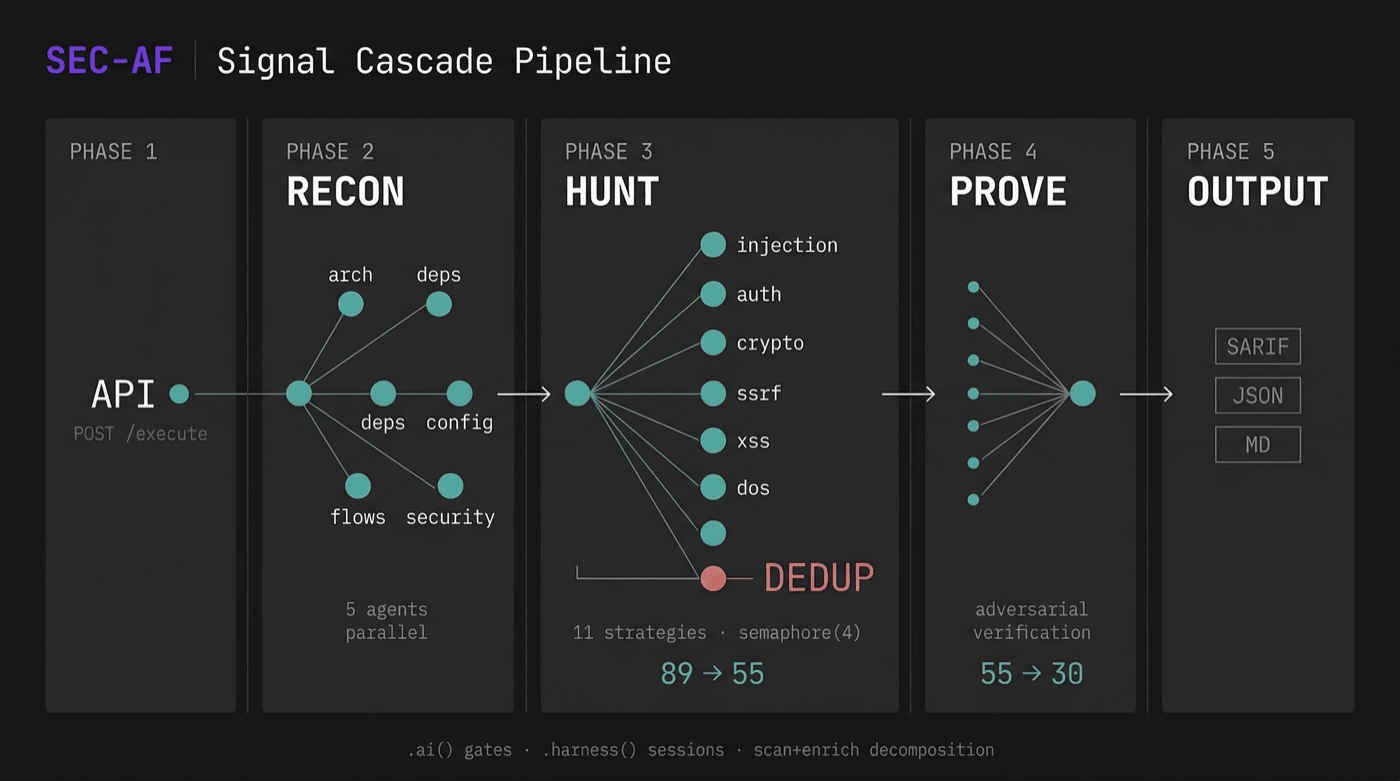 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability