
heisenberg-ssc-gha
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
devsecopssecret-detectionsupply-chain-security+1
7
appomni-labs/heisenberg-ssc-ghaGitHub Action for Heisenberg SSC

 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 git-pkgs/proxy
A lightweight caching proxy for package registries.
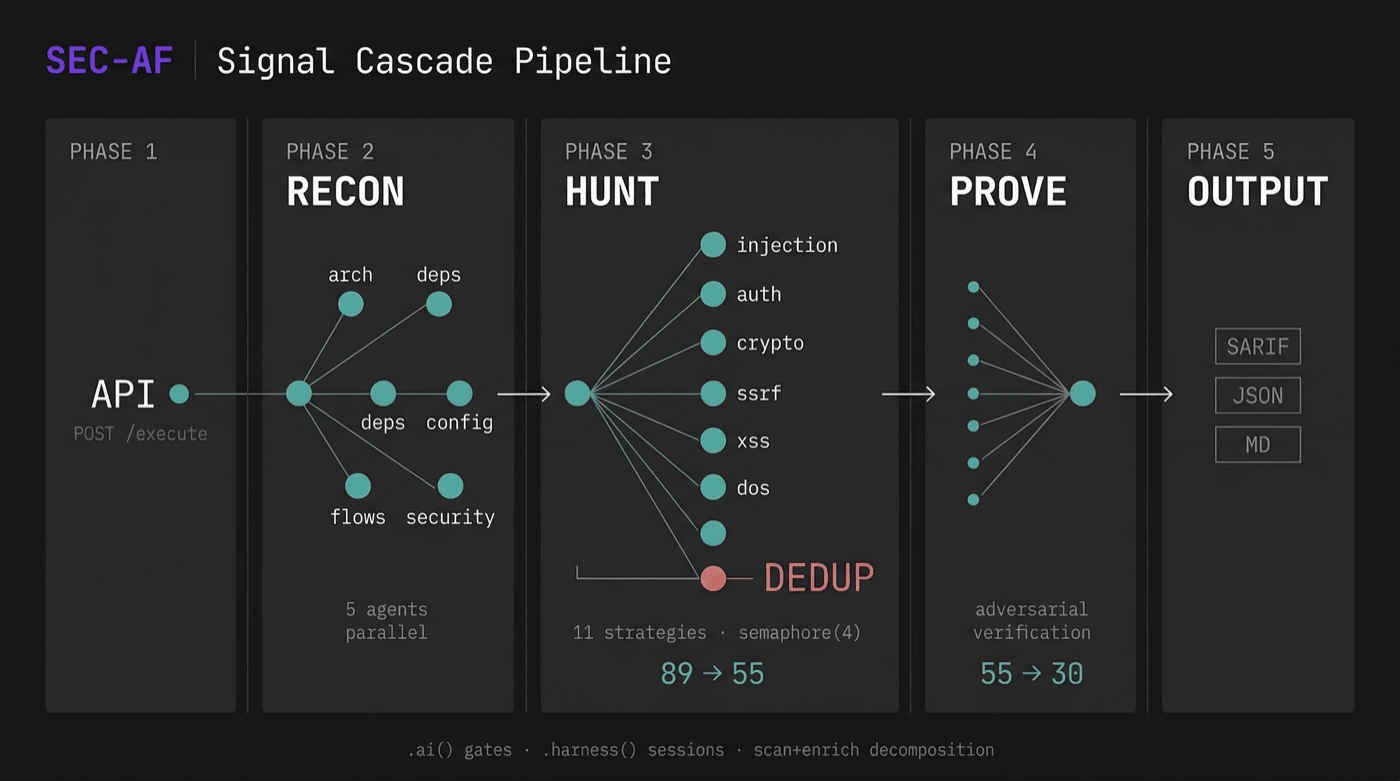 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
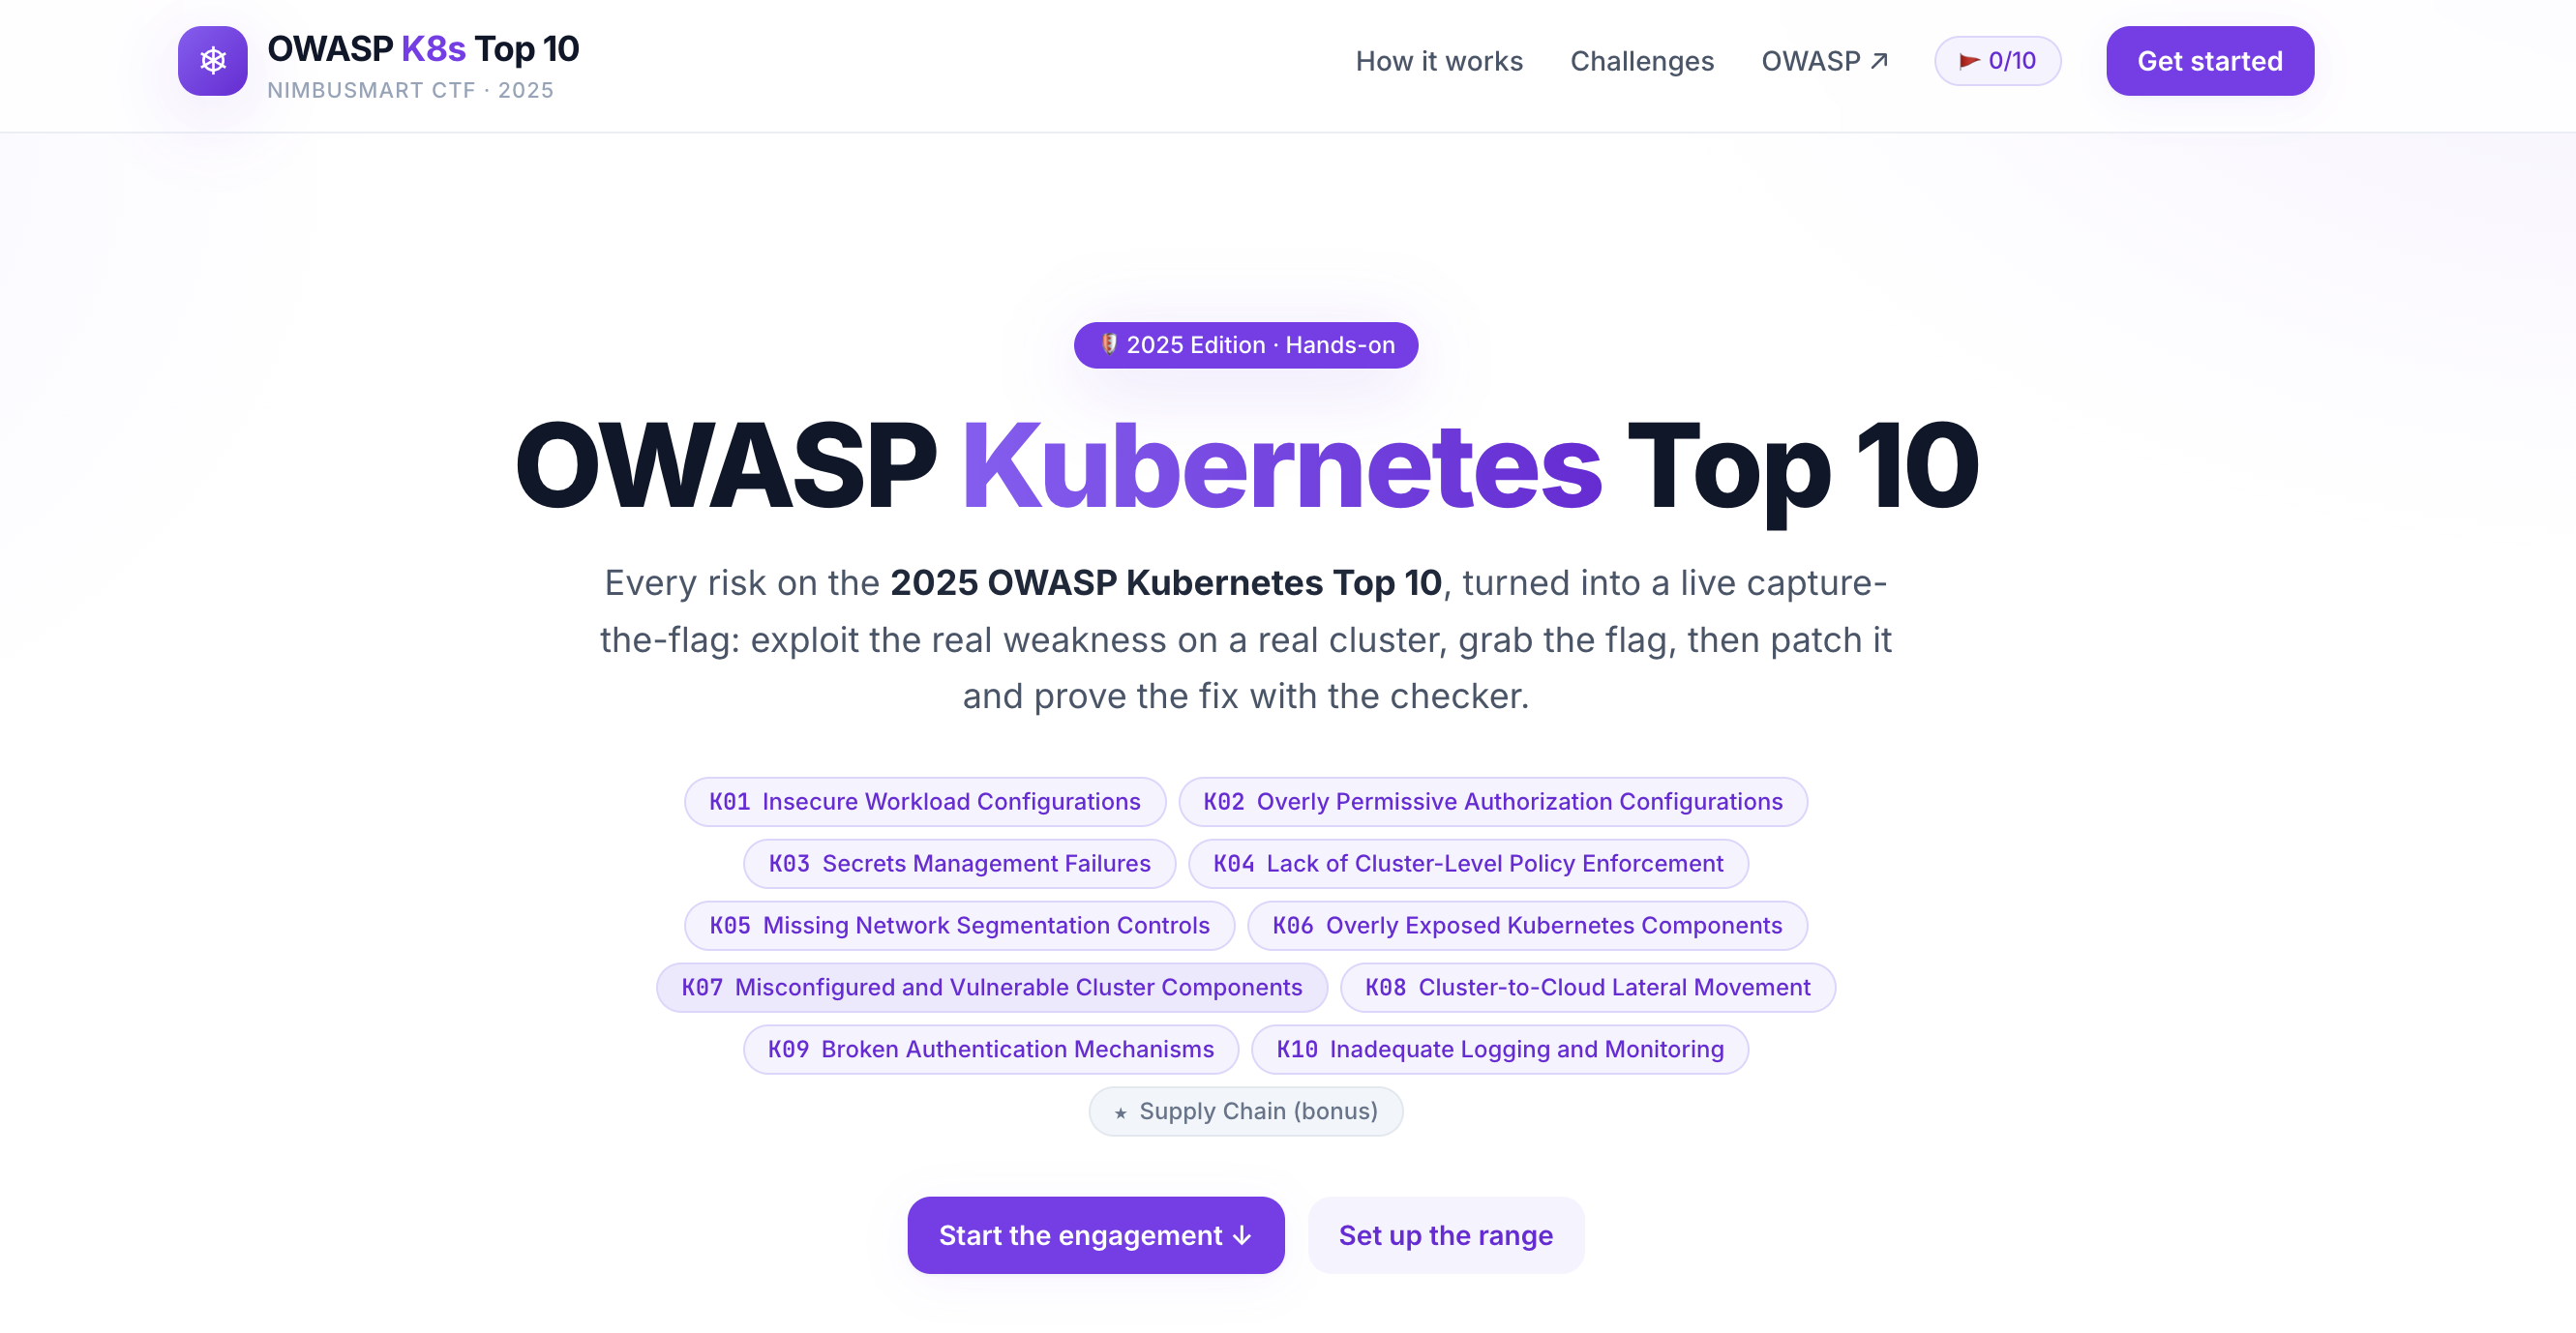 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 toxicbishop/supply-chain
A comprehensive guide to software supply chain security. This open-source manuscript provides security professionals and developers with practical…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…