

wolfssl
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
cloud-securitycryptographyembedded-systems-security+6
2.9k
wolfssl/wolfsslThe wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 aschen/log4j-patched
Provide patched version of Log4J against CVE-2021-44228 and CVE-2021-45046 as well as a script to manually patch it yourself
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
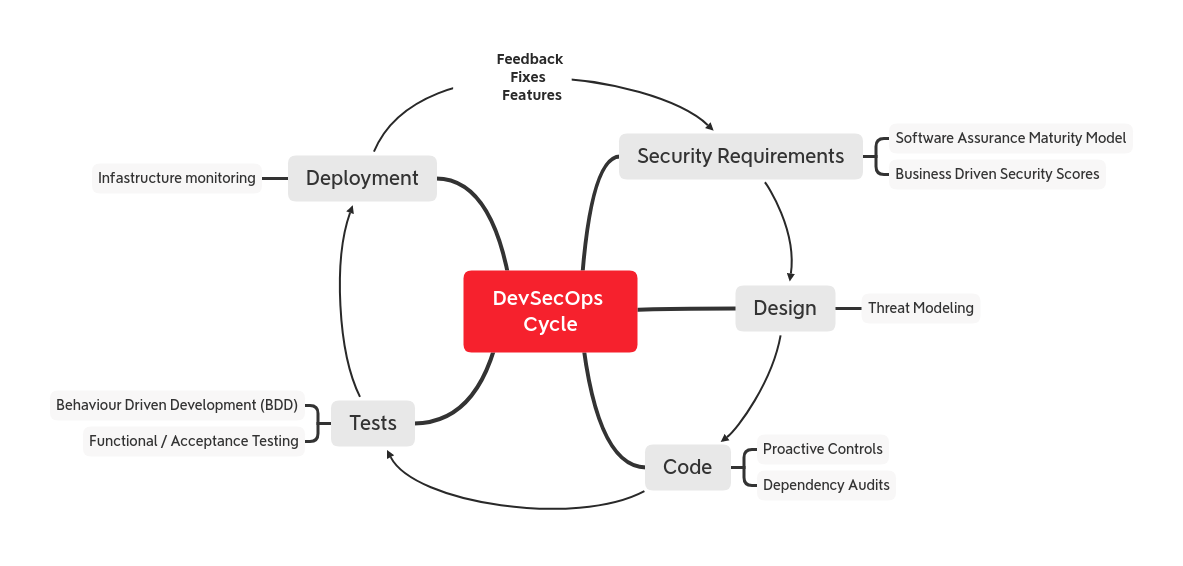 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack

 mubix/cve-2021-44228-log4shell-hashes
Hashes for vulnerable LOG4J versions
 authomize/log4j-log4shell-affected
Lists of affected components and affected apps/vendors by CVE-2021-44228 (aka Log4shell or Log4j RCE). This list is meant as a resource for security…
 knqyf263/go-mal-pkgs
A security tool to detect malicious Go packages by verifying checksums in go.sum against the original source code
 yomisana/are-you-get-tanstack-attack
Are you get Tanstack Supply chain attack attack of 5/11? CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]
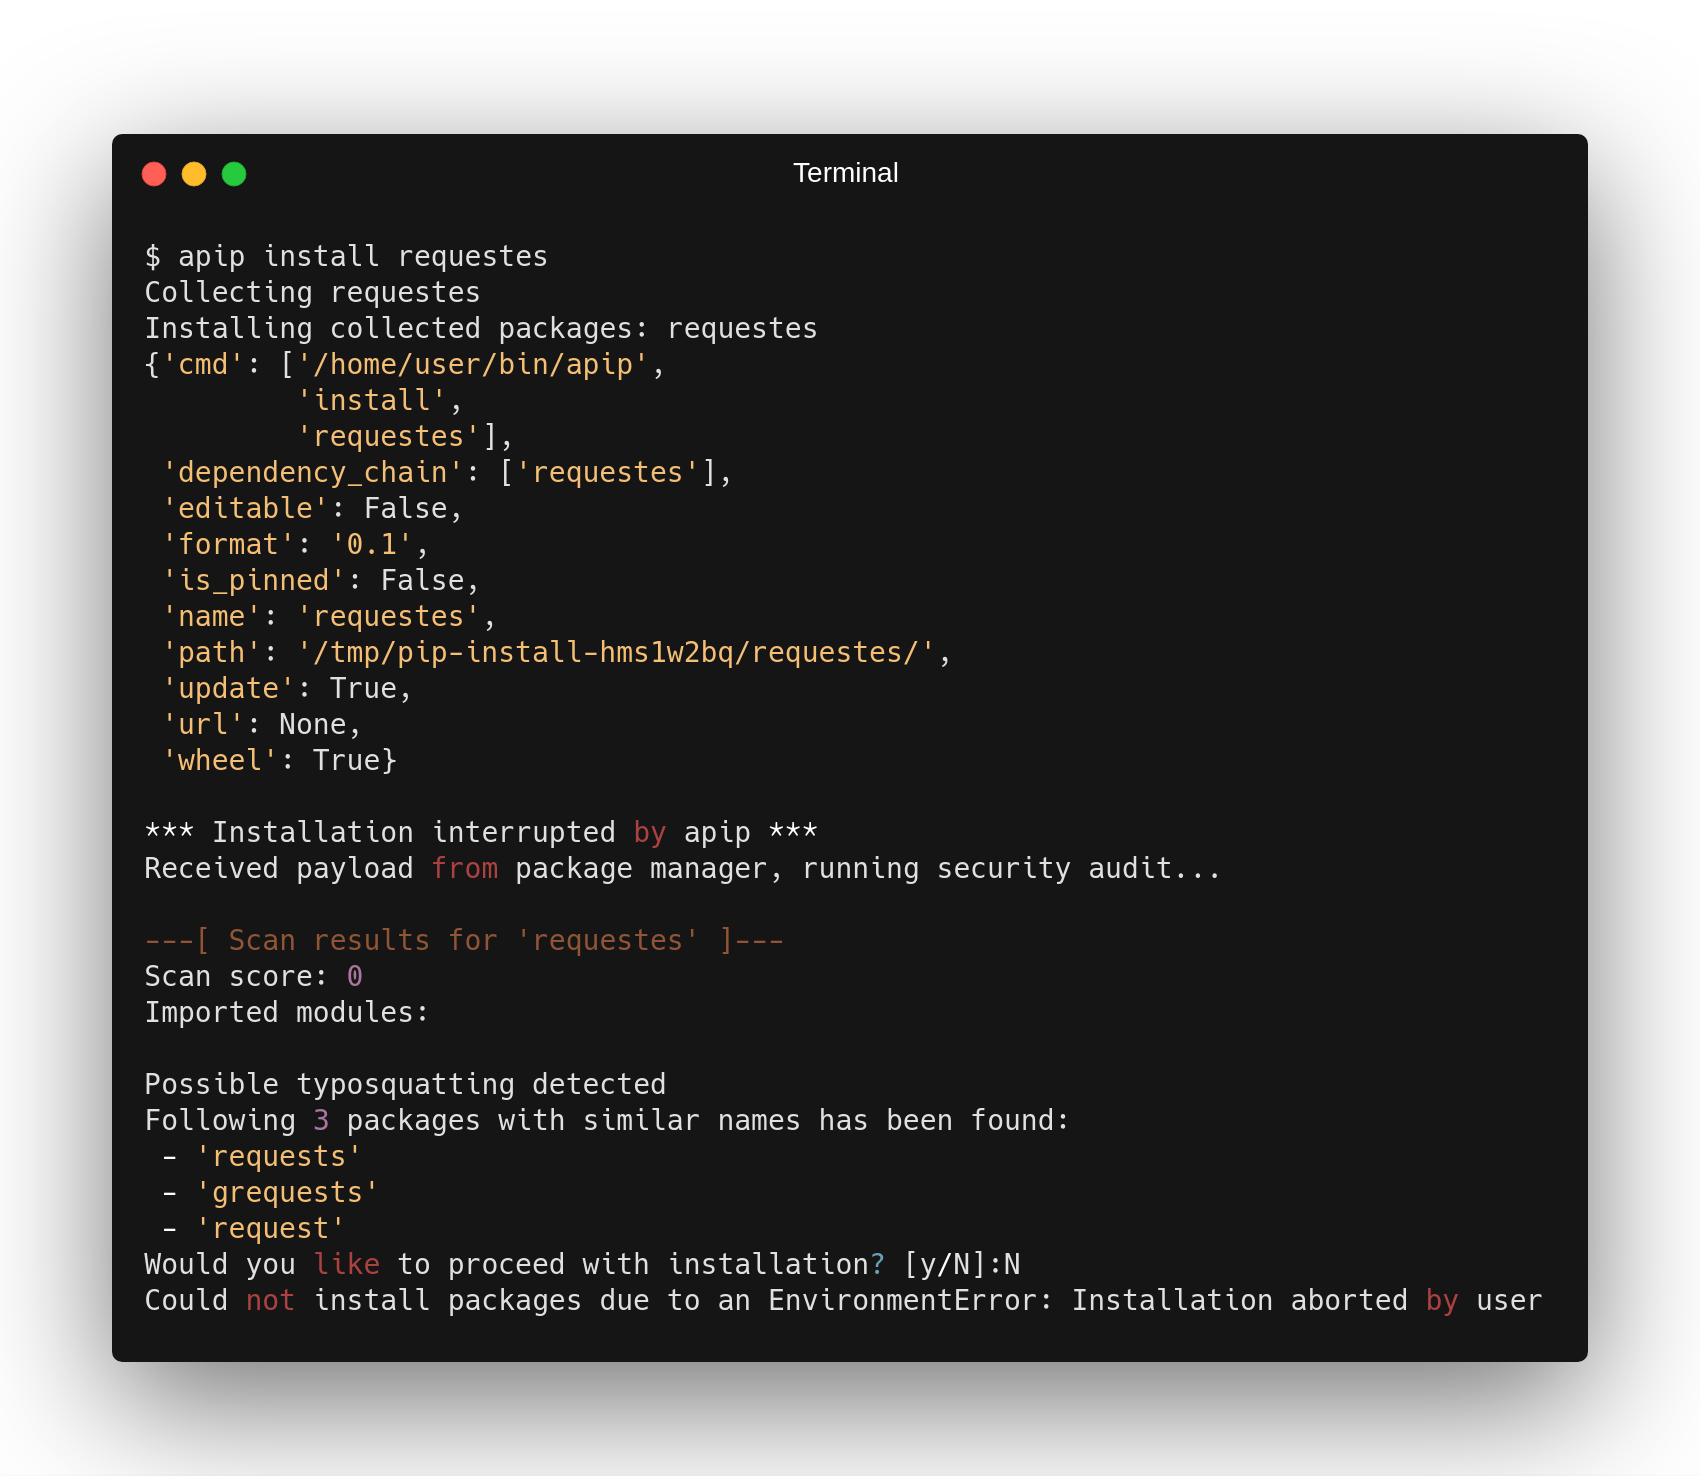 rootlug/aura
Project Aura: Security auditing and code introspection
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 morrisel/cve-2023-26136
This repository contains a solution for the CVE-2023-26136 vulnerability.
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source