
inspec_cve_2019_15224
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
configuration-auditingincident-responsemalware-analysis+2
1
chef-cft/inspec_cve_2019_15224Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box
 soliantconsulting/cve-2025-46295-fix-fms
Automated script suite to detect and remediate CVE-2025-46295 by replacing vulnerable Apache Commons JARs in FileMaker Server installations with…
 dpomnean/log4j_scanner_wrapper
log4j vulnerability wrapper scanner for CVE-2021-44228
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 staxis-platform/gitlab-profile
Modular Node.js runtime orchestrator with HMAC integrity verification, import guards, and sandboxed execution for secure, layered application…
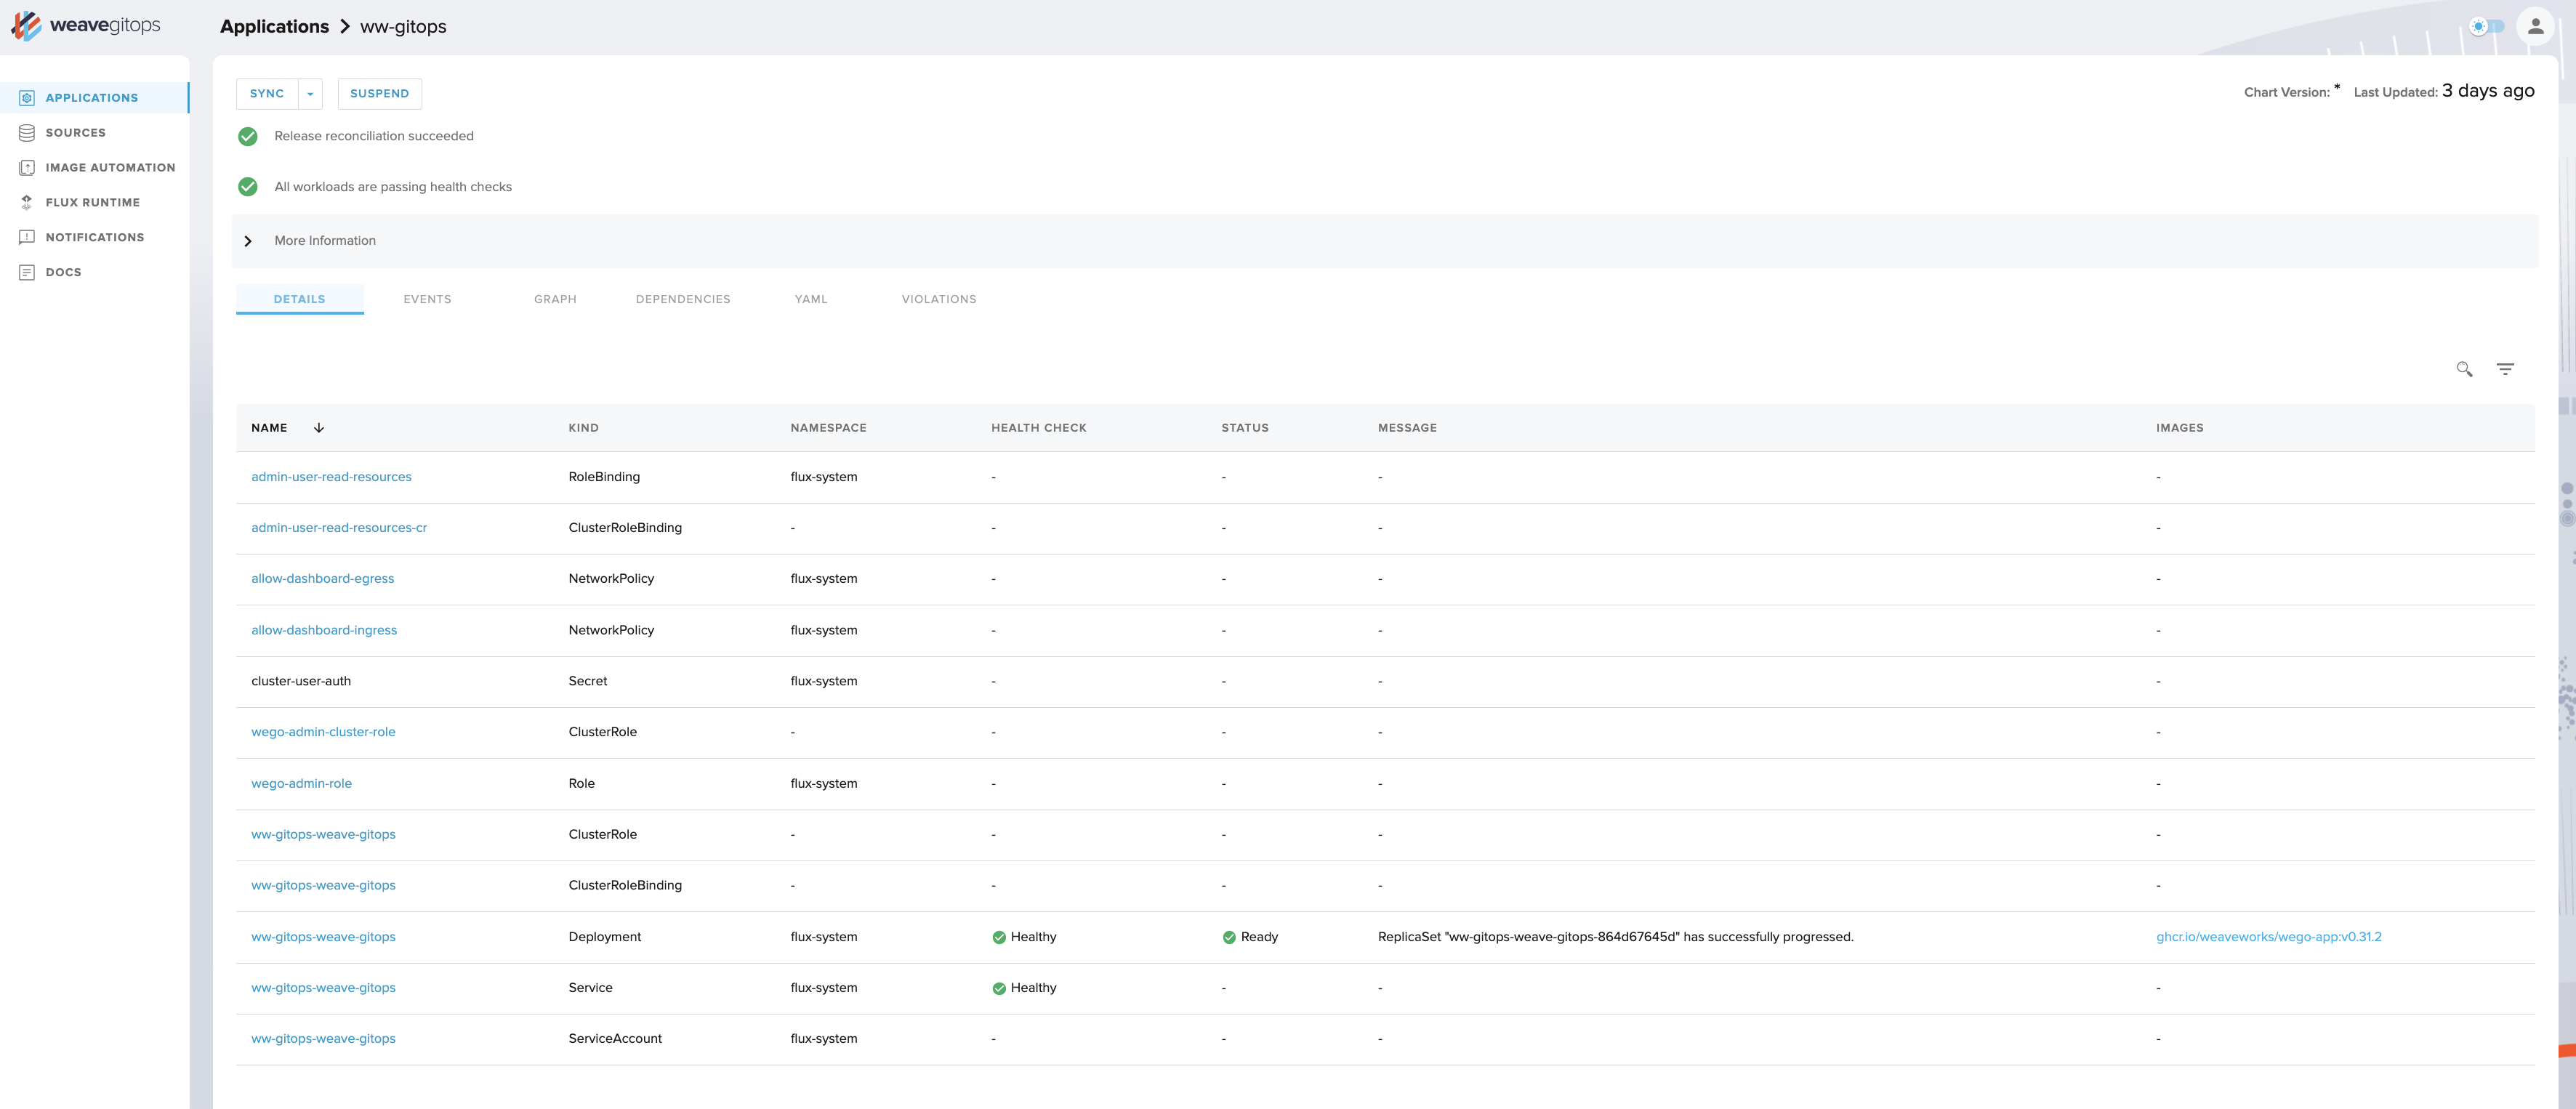 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 knqyf263/remic
Vulnerability Scanner for Detecting Publicly Disclosed Vulnerabilities in Application Dependencies
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.