

scan-cve-2018-8115
 aquasecurity/scan-cve-2018-8115
CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
container-securitymisconfigurationstatic-analysis+2
7
aquasecurity/scan-cve-2018-8115CLI tool that verifies Docker images for CVE-2018-8115 by checking layers for malicious files, helping ensure safe pulls from Docker Hub.
 microsoft/azurelinux
Hardened, Azure-optimized Linux distribution built from Fedora sources with RPM packaging, supply chain security, and declarative configuration for…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 santhreal/keyhog
Open-source secret scanner in Rust
 anchore/grype
A vulnerability scanner for container images and filesystems
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
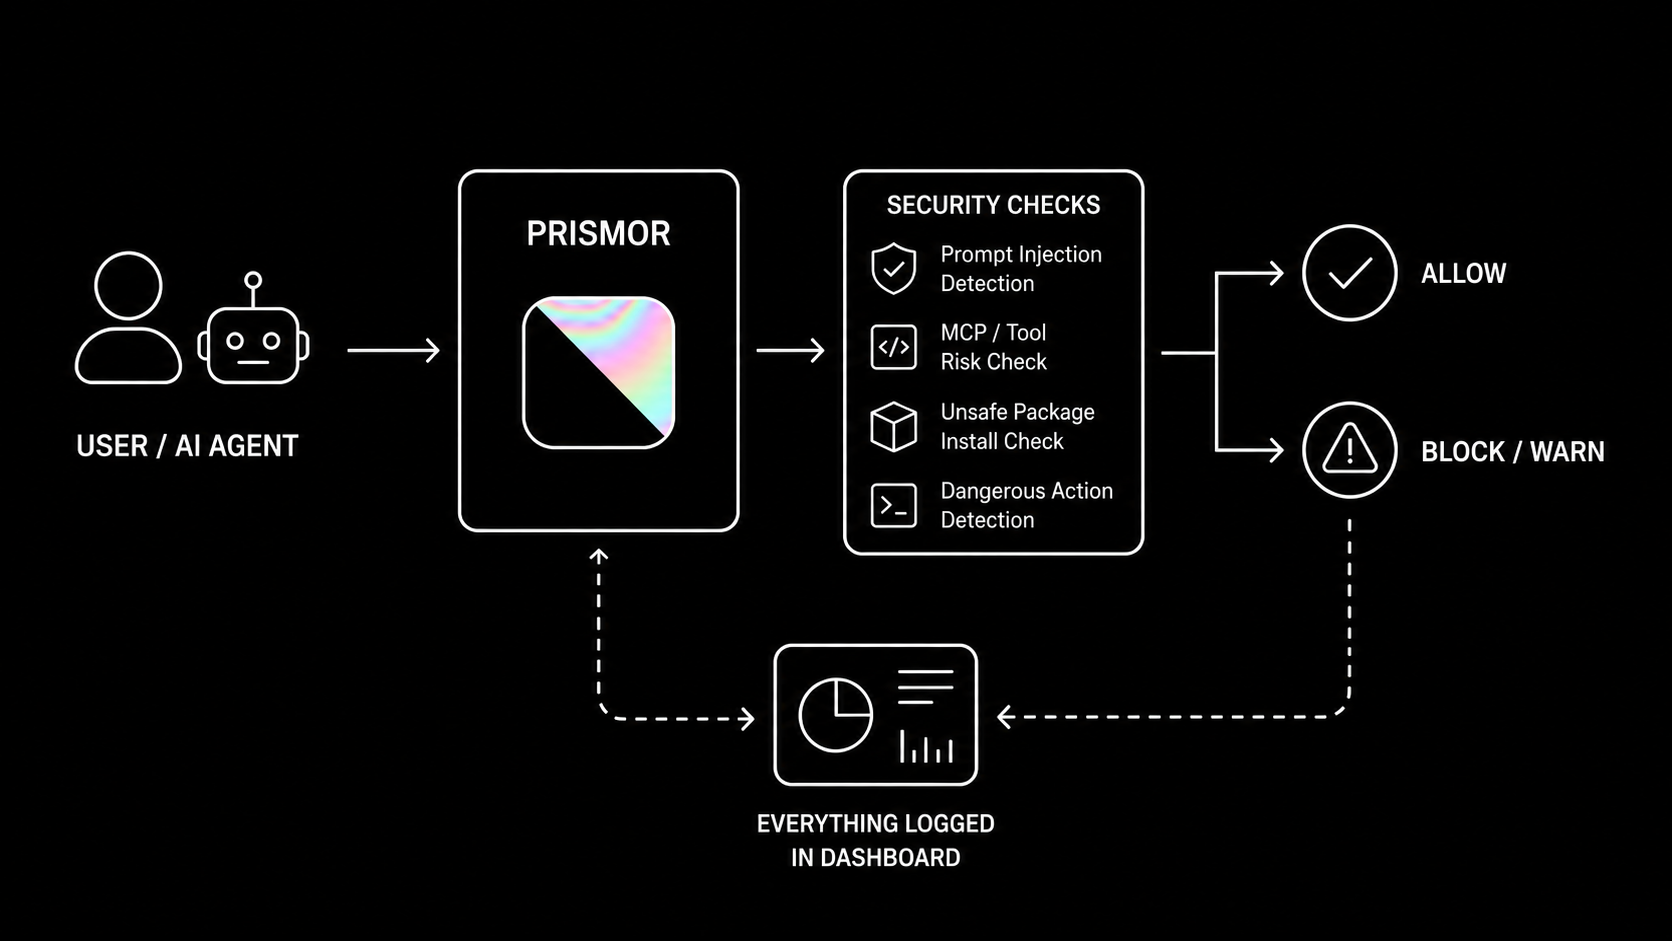 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 aquasecurity/trivy-repo
deb/rpm repository for Trivy
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
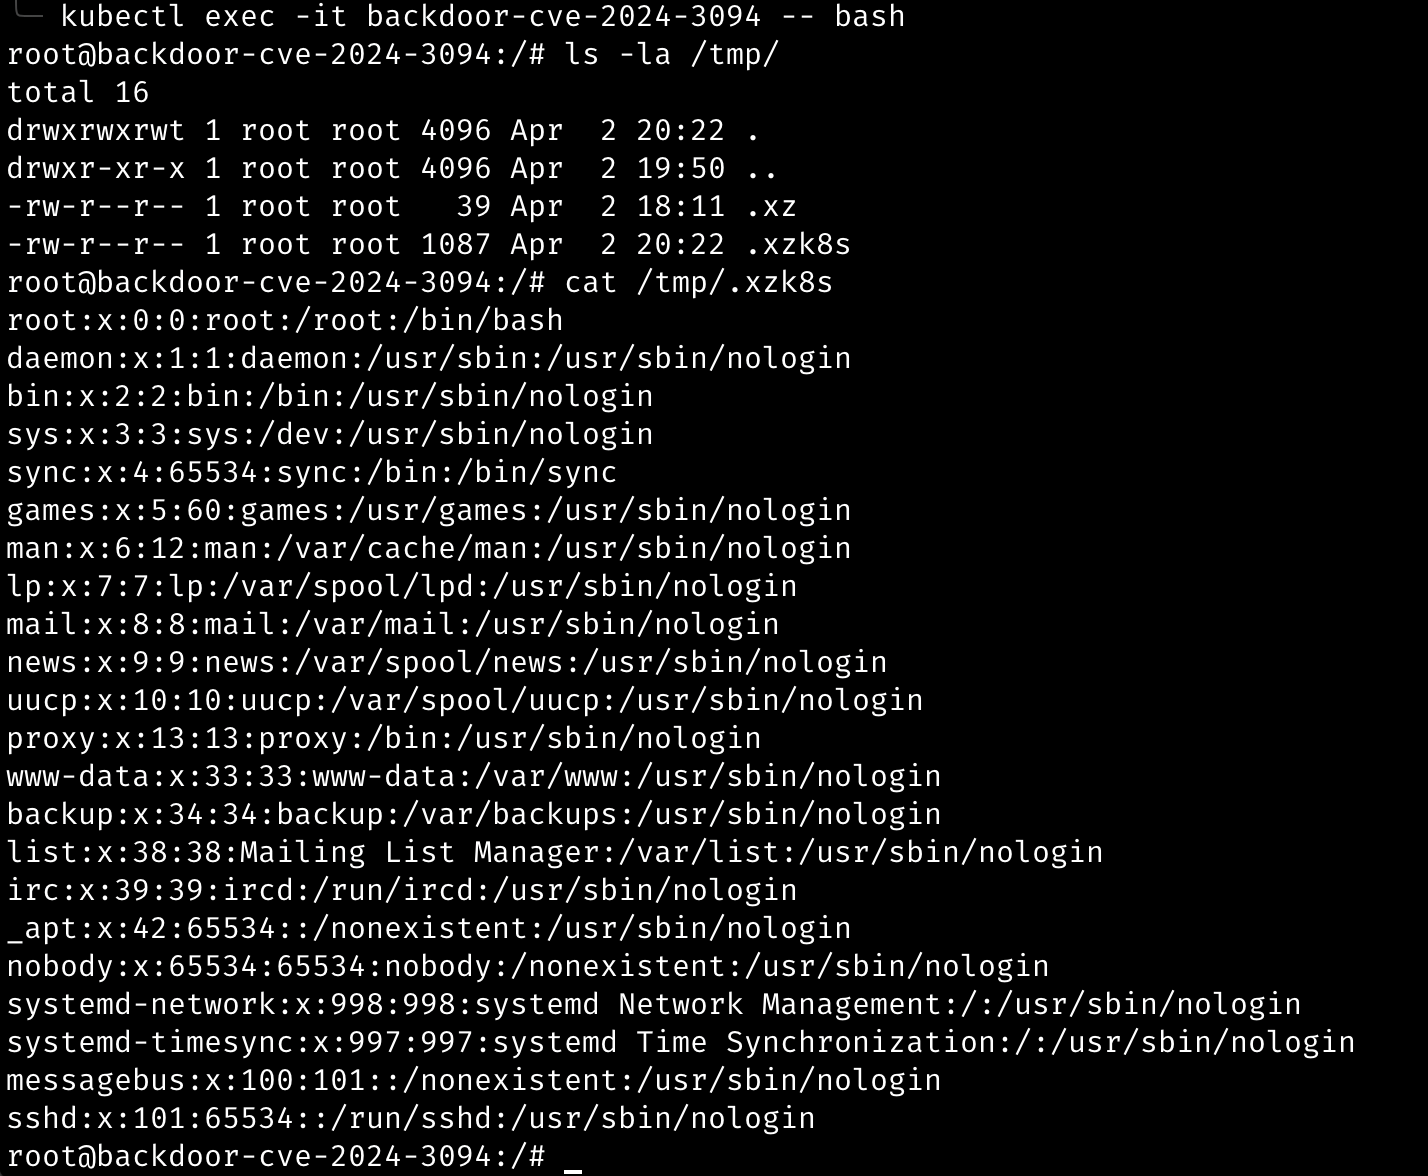 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094
 mhaggis/package-inferno
A Public Package Scanner for The Community