
Log4j_CVE-2021-44228
 vorburger/log4j_cve-2021-44228
Curated resource hub for Log4j CVE-2021-44228, covering detection, mitigation, exploitation, and dependency management strategies for the critical…
curated-resourceseducationexploitation+3
3
vorburger/log4j_cve-2021-44228Curated resource hub for Log4j CVE-2021-44228, covering detection, mitigation, exploitation, and dependency management strategies for the critical…
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
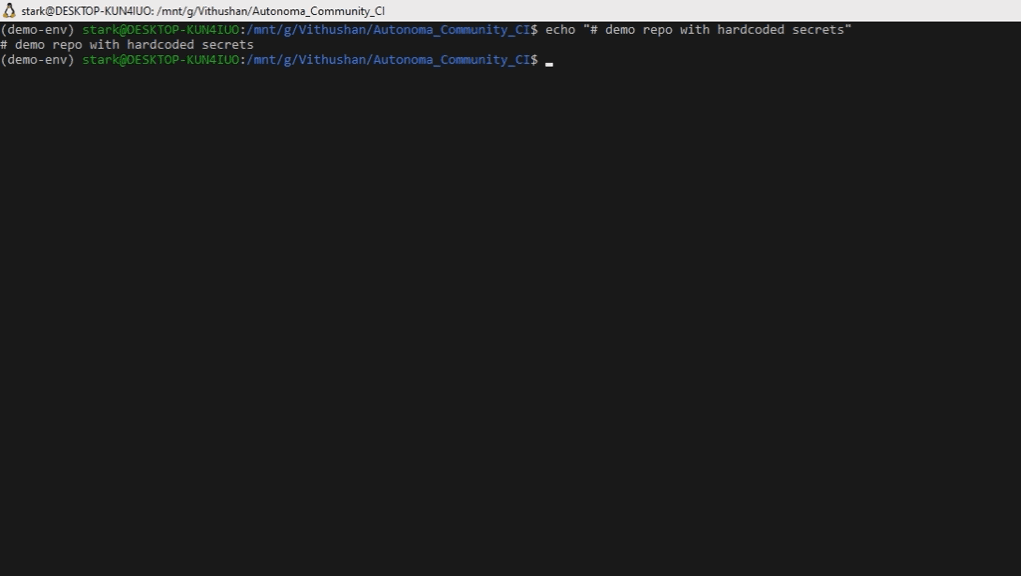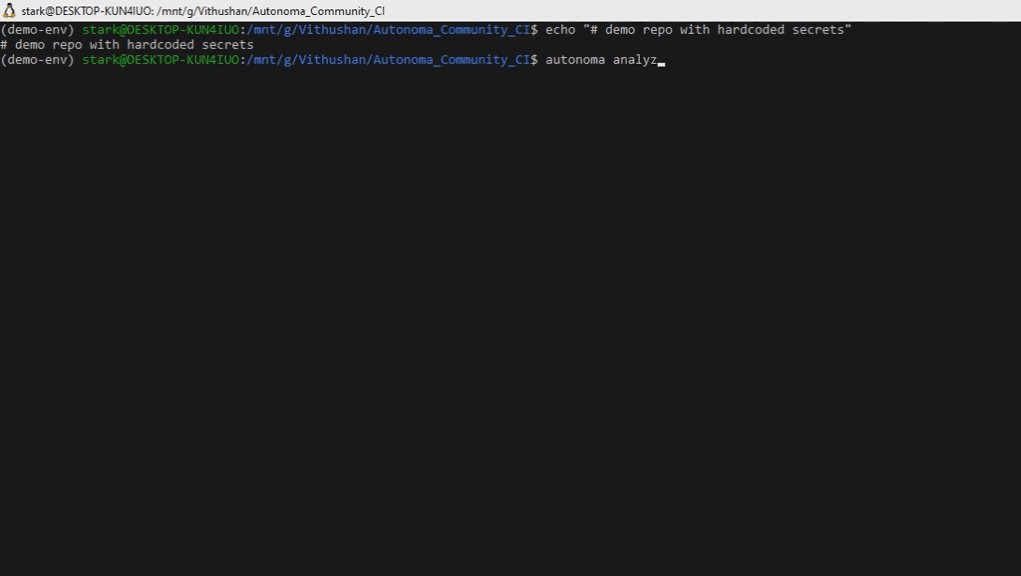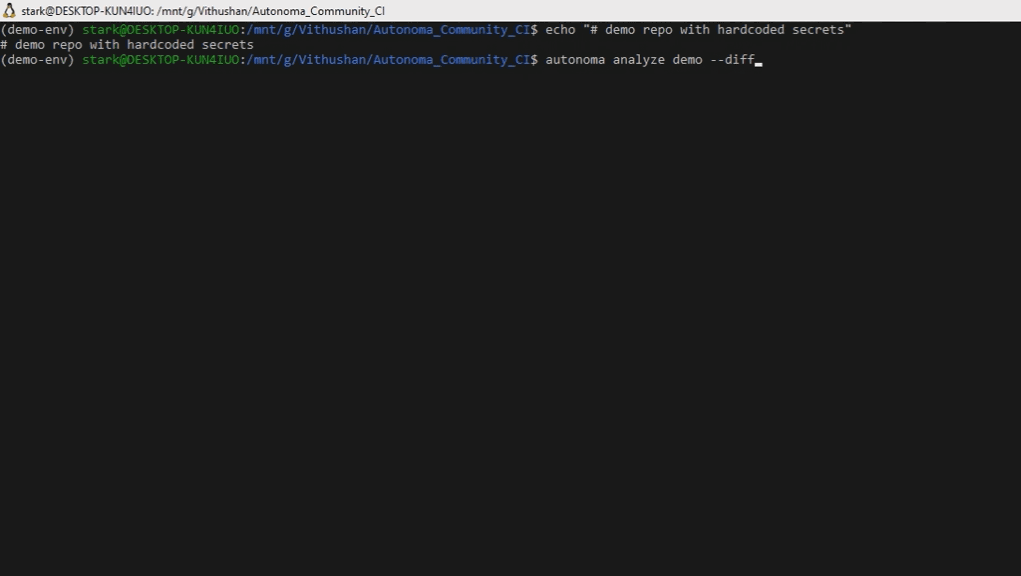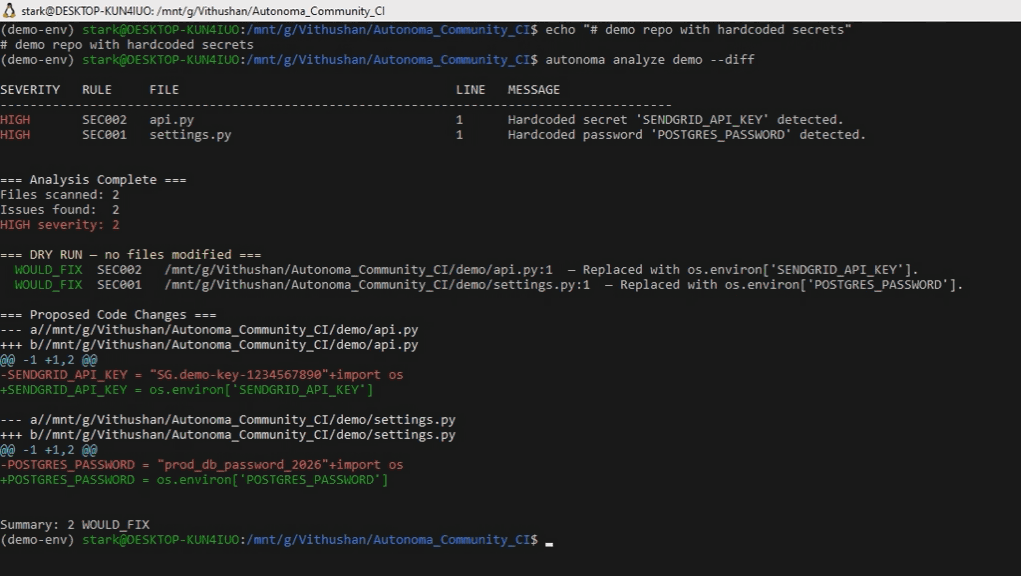 vihaaninnovations/autonoma
Detects and auto-fixes hardcoded secrets in Python repos — refuses when the fix could break your code
 prashanthnataraj/mini-shai-hulud-detector
One-command scanner for the Mini Shai-Hulud npm supply-chain worm (CVE-2026-45321). Detect before rotating tokens.
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 gonsarrabia/minimus-junior-backend-exercise
Junior Backend Candidate Exercise: Packaging the dasel CLI (v3.3.1) with Melange, fixing CVE-2026-33320, and building a minimal container image using…
 mrk336/cve-2024-3094
CVE-2024-3094 exposed a backdoor in the XZ compression library, allowing remote SSH access by bypassing authentication. It’s a major supply chain…
 randomrobbiebf/chart-down
Extracts all the chart lists from ChartMuseum
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 danielruf/snyk-js-jquery-565129
patches for SNYK-JS-JQUERY-565129, SNYK-JS-JQUERY-567880, CVE-2020-1102, CVE-2020-11023, includes the patches for SNYK-JS-JQUERY-174006,…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 rahulreddykarne/cve-2026-43637-cornac
Path traversal (Tar Slip) in Cornac via _extract_archive (CVE-2026-43637)
 atorralba/cve-2021-30005-poc
Proof-of-concept demonstrating arbitrary command execution via malicious virtual environment activation scripts in PyCharm before 2020.3.4,…
 zebberncve/cve-2026-26830
Advisory for pdf-image ⌯⌲ 10 000 weekly downloads
 snailsploit/cve-2026-32794
CVE-2026-32794: TLS Certificate Verification Bypass in Apache Airflow Databricks Provider
 neilc1964techned/craready-test-java-vulns
CRAReady SBOM test fixture — Java/Maven app with Log4Shell (CVE-2021-44228), Spring4Shell, Text4Shell, and other critical CVEs
 s41r4j/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning