

jfrog-CVE-2022-21449
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
code-analysisstatic-analysissupply-chain-security+1
37
jfrog/jfrog-cve-2022-21449Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
 simplylu/cve-2021-42694
Generate malicious files using recently published homoglyphic-attack (CVE-2021-42694)
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
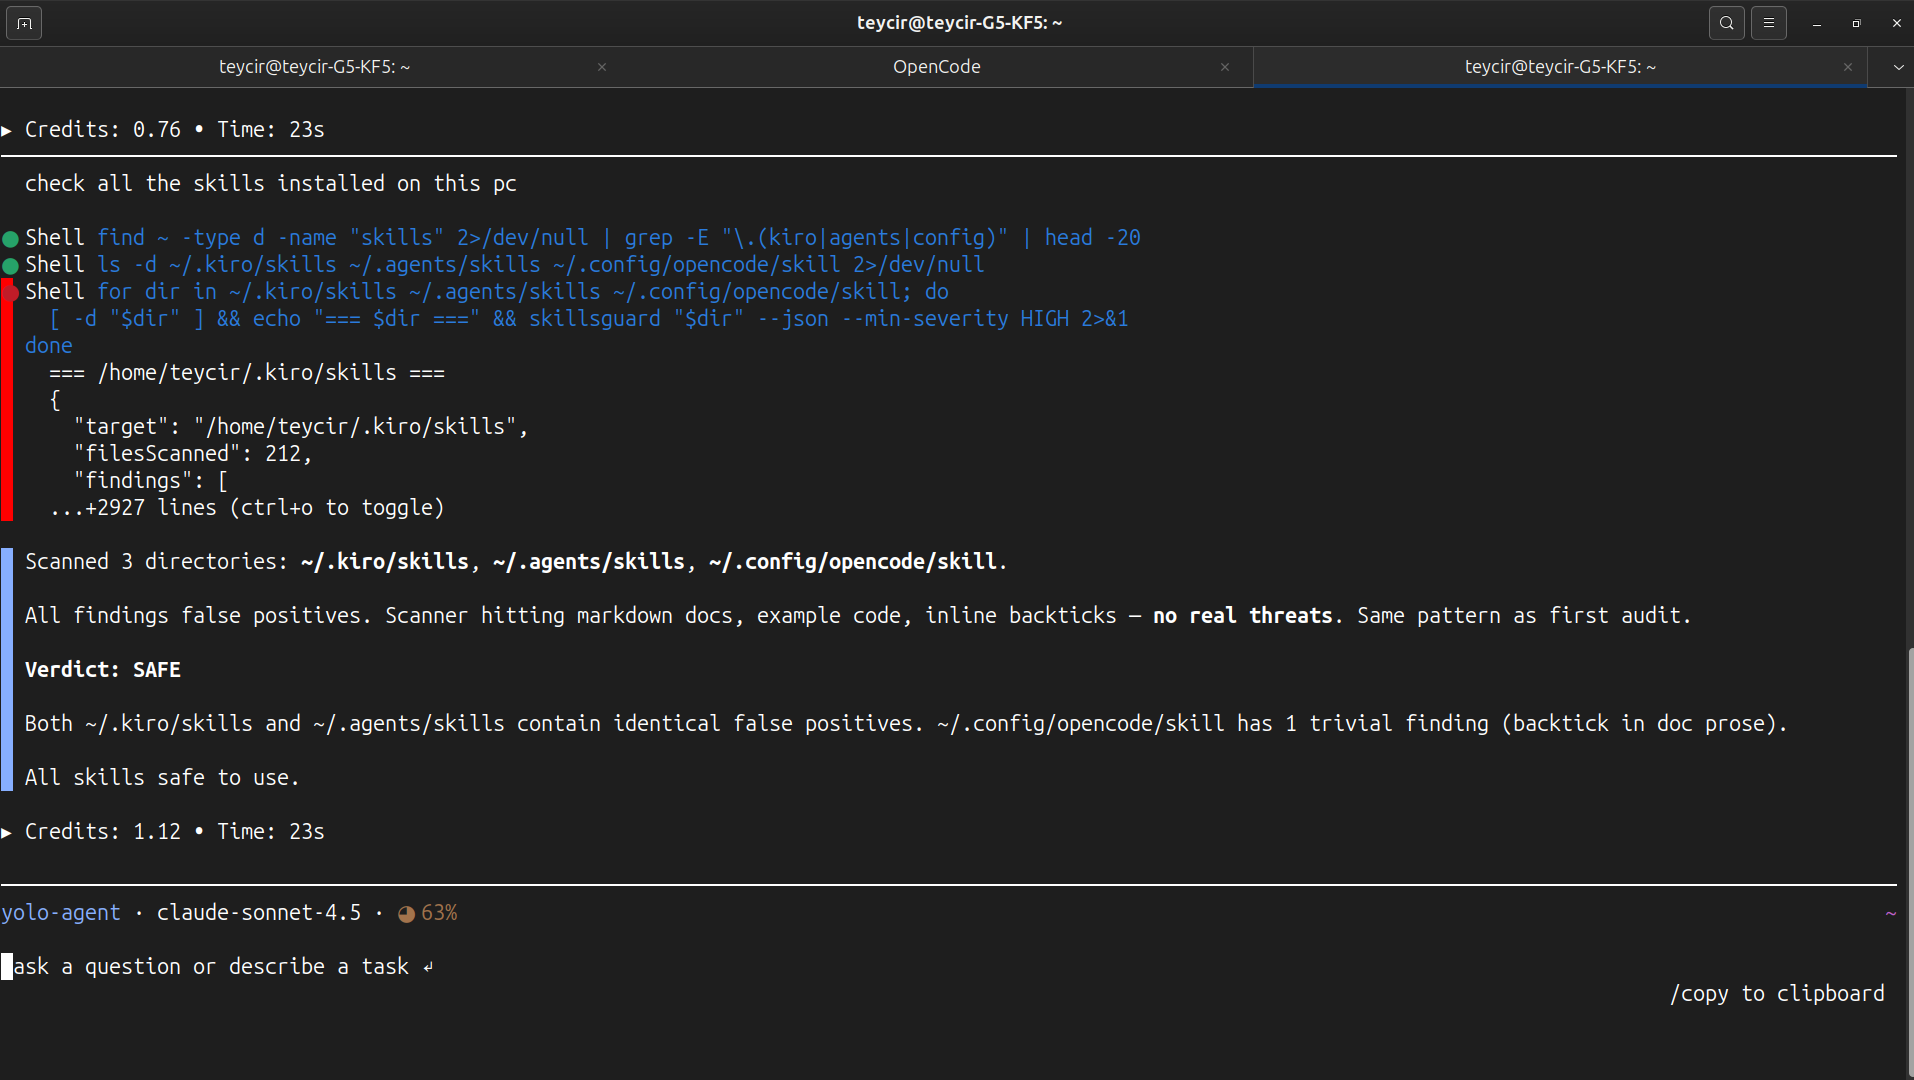 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 aquasecurity/trivy-java-db
Builds a SQLite database of Maven artifacts (ArtifactID, GroupID, Version, SHA1) for Trivy's Java component vulnerability detection, enabling scans…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]