cloud-middleware-dataset

Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…

Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…

Software Component Verification Standard (SCVS)

Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…

A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)

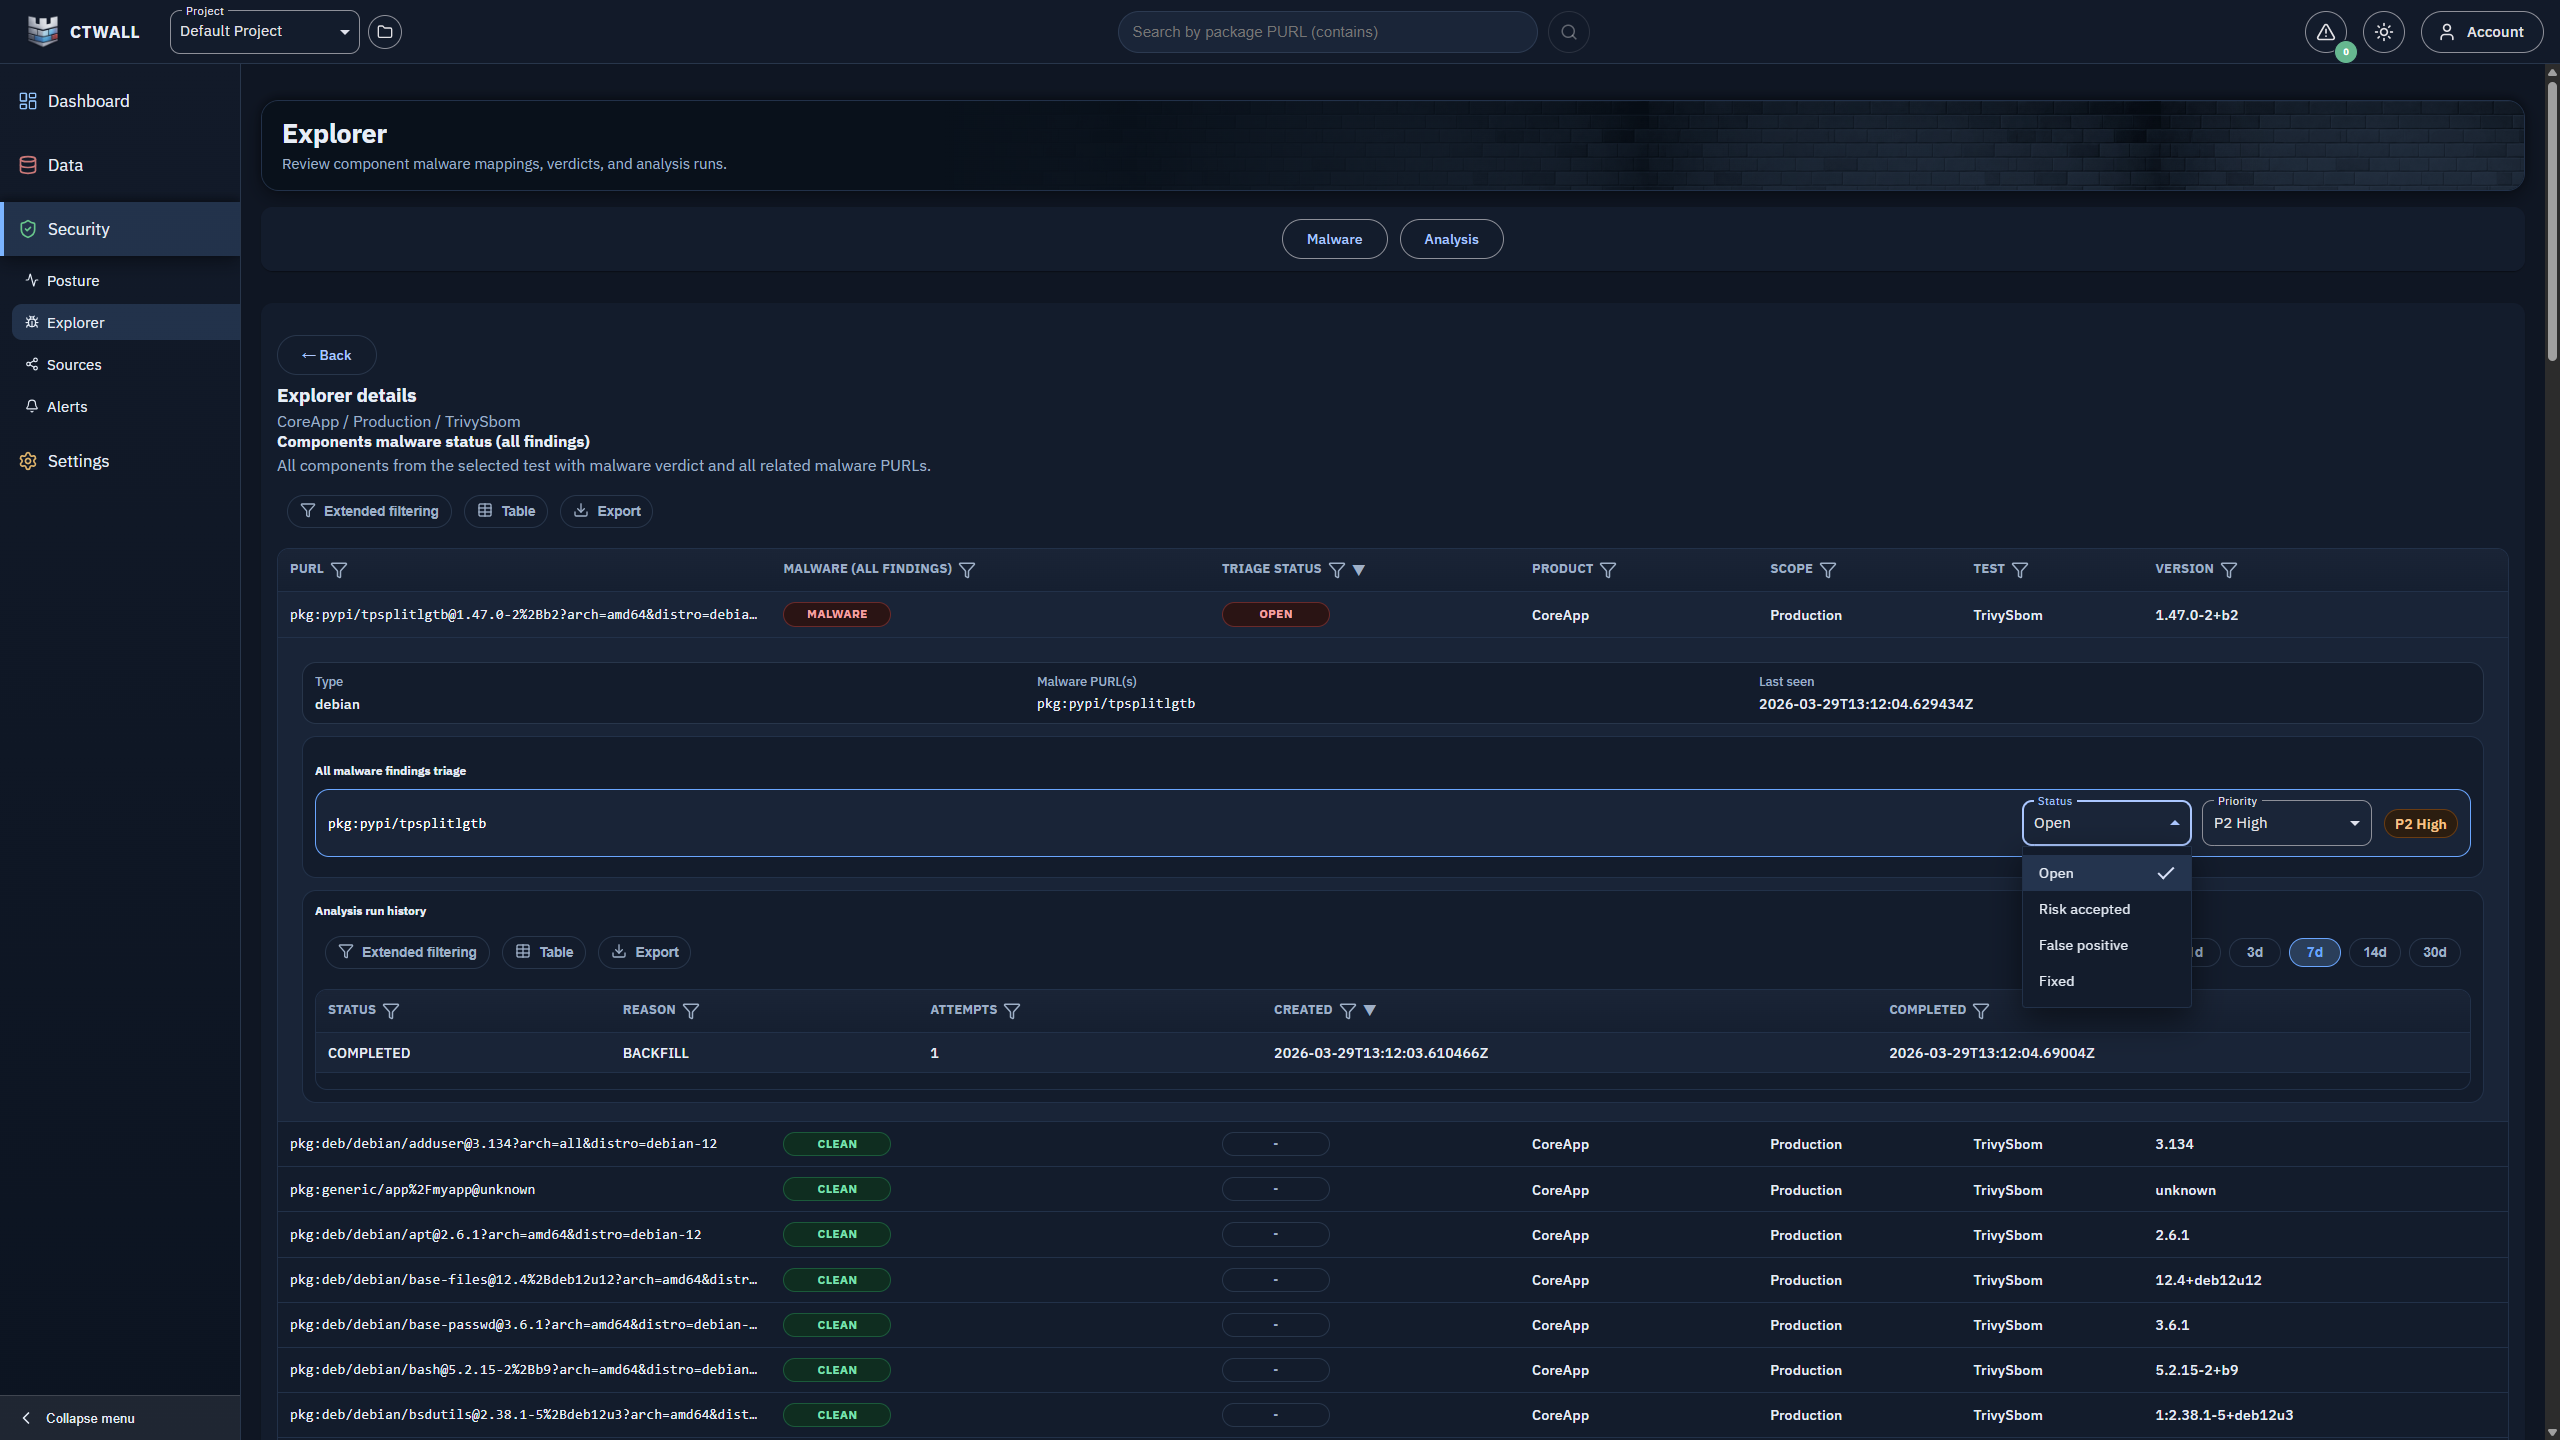
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…

Curated vulnerability writeup collection with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for…

A comprehensive guide to software supply chain security. This open-source manuscript provides security professionals and developers with practical…

Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…

KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems

A software supply chain framework powered by Nix.

Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…

Safety checks Python dependencies for known security vulnerabilities and suggests the proper remediations for vulnerabilities detected.

Static and dynamic analysis tool that audits open-source packages for malicious, vulnerable, and risky attributes, with sandboxed installation to…

A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.

Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…

Aggregates Vulnerability Exploitability eXchange (VEX) documents from open-source projects. Organizes by PURL for automated security tool integration.