

cve-2022-32223
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
binary-exploitationexploitationpayload-development+2
3
ianyong/cve-2022-32223Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 zerbaliy3v/cve-2018-6574-exploit
CVE-2018-6574 this vulnerability impacts Golang go get command and allows an attacker to gain code execution on a system by installing a malicious…
 in-toto/in-toto
Protects software supply chain integrity by verifying each step is performed by authorized functionaries, using signed layout and link metadata.
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 pypa/advisory-database
Community-owned database of security advisories for Python packages on PyPI, providing structured vulnerability data in OSV format for integration…
 murphysecurity/murphysec
An open source tool focused on software supply chain security. 墨菲安全专注于软件供应链安全,具备专业的软件成分分析(SCA)、漏洞检测、专业漏洞库。
 owasp/docker-security
Getting a handle on container security
 mergebase/log4j-detector
File-system scanner that detects vulnerable Log4J versions (CVE-2021-44228, CVE-2021-45046) by analyzing compiled Java classes, including nested…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
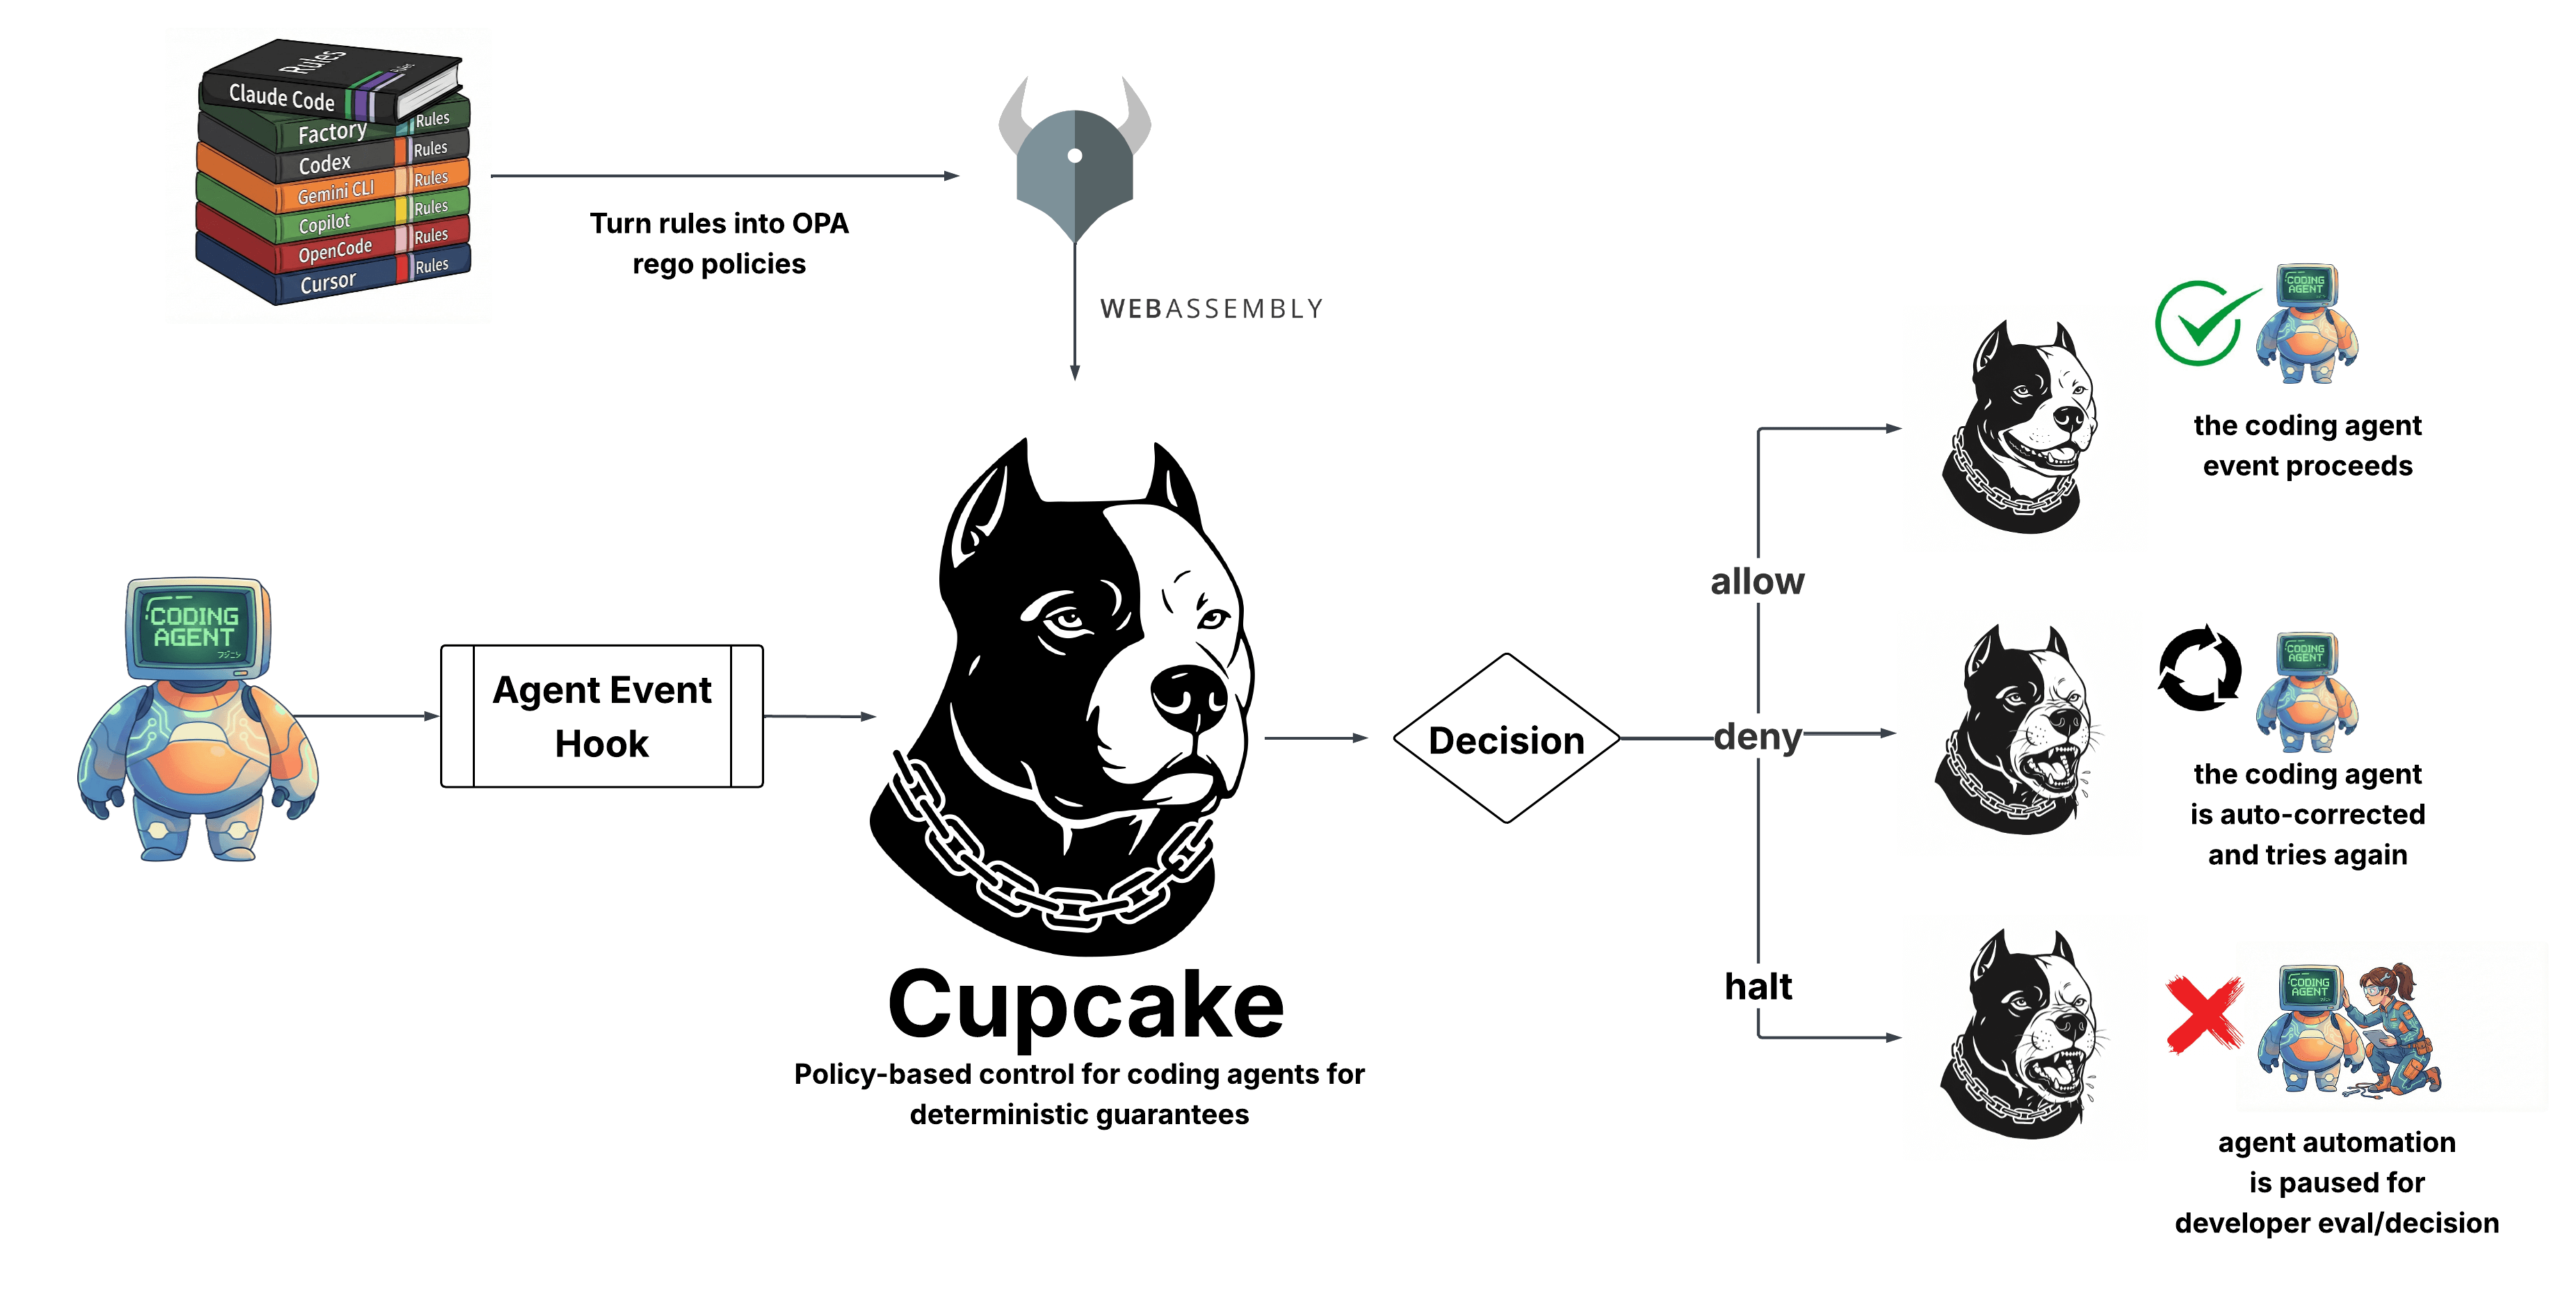 eqtylab/cupcake
A native policy enforcement layer for AI coding agents. Built on OPA/Rego.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
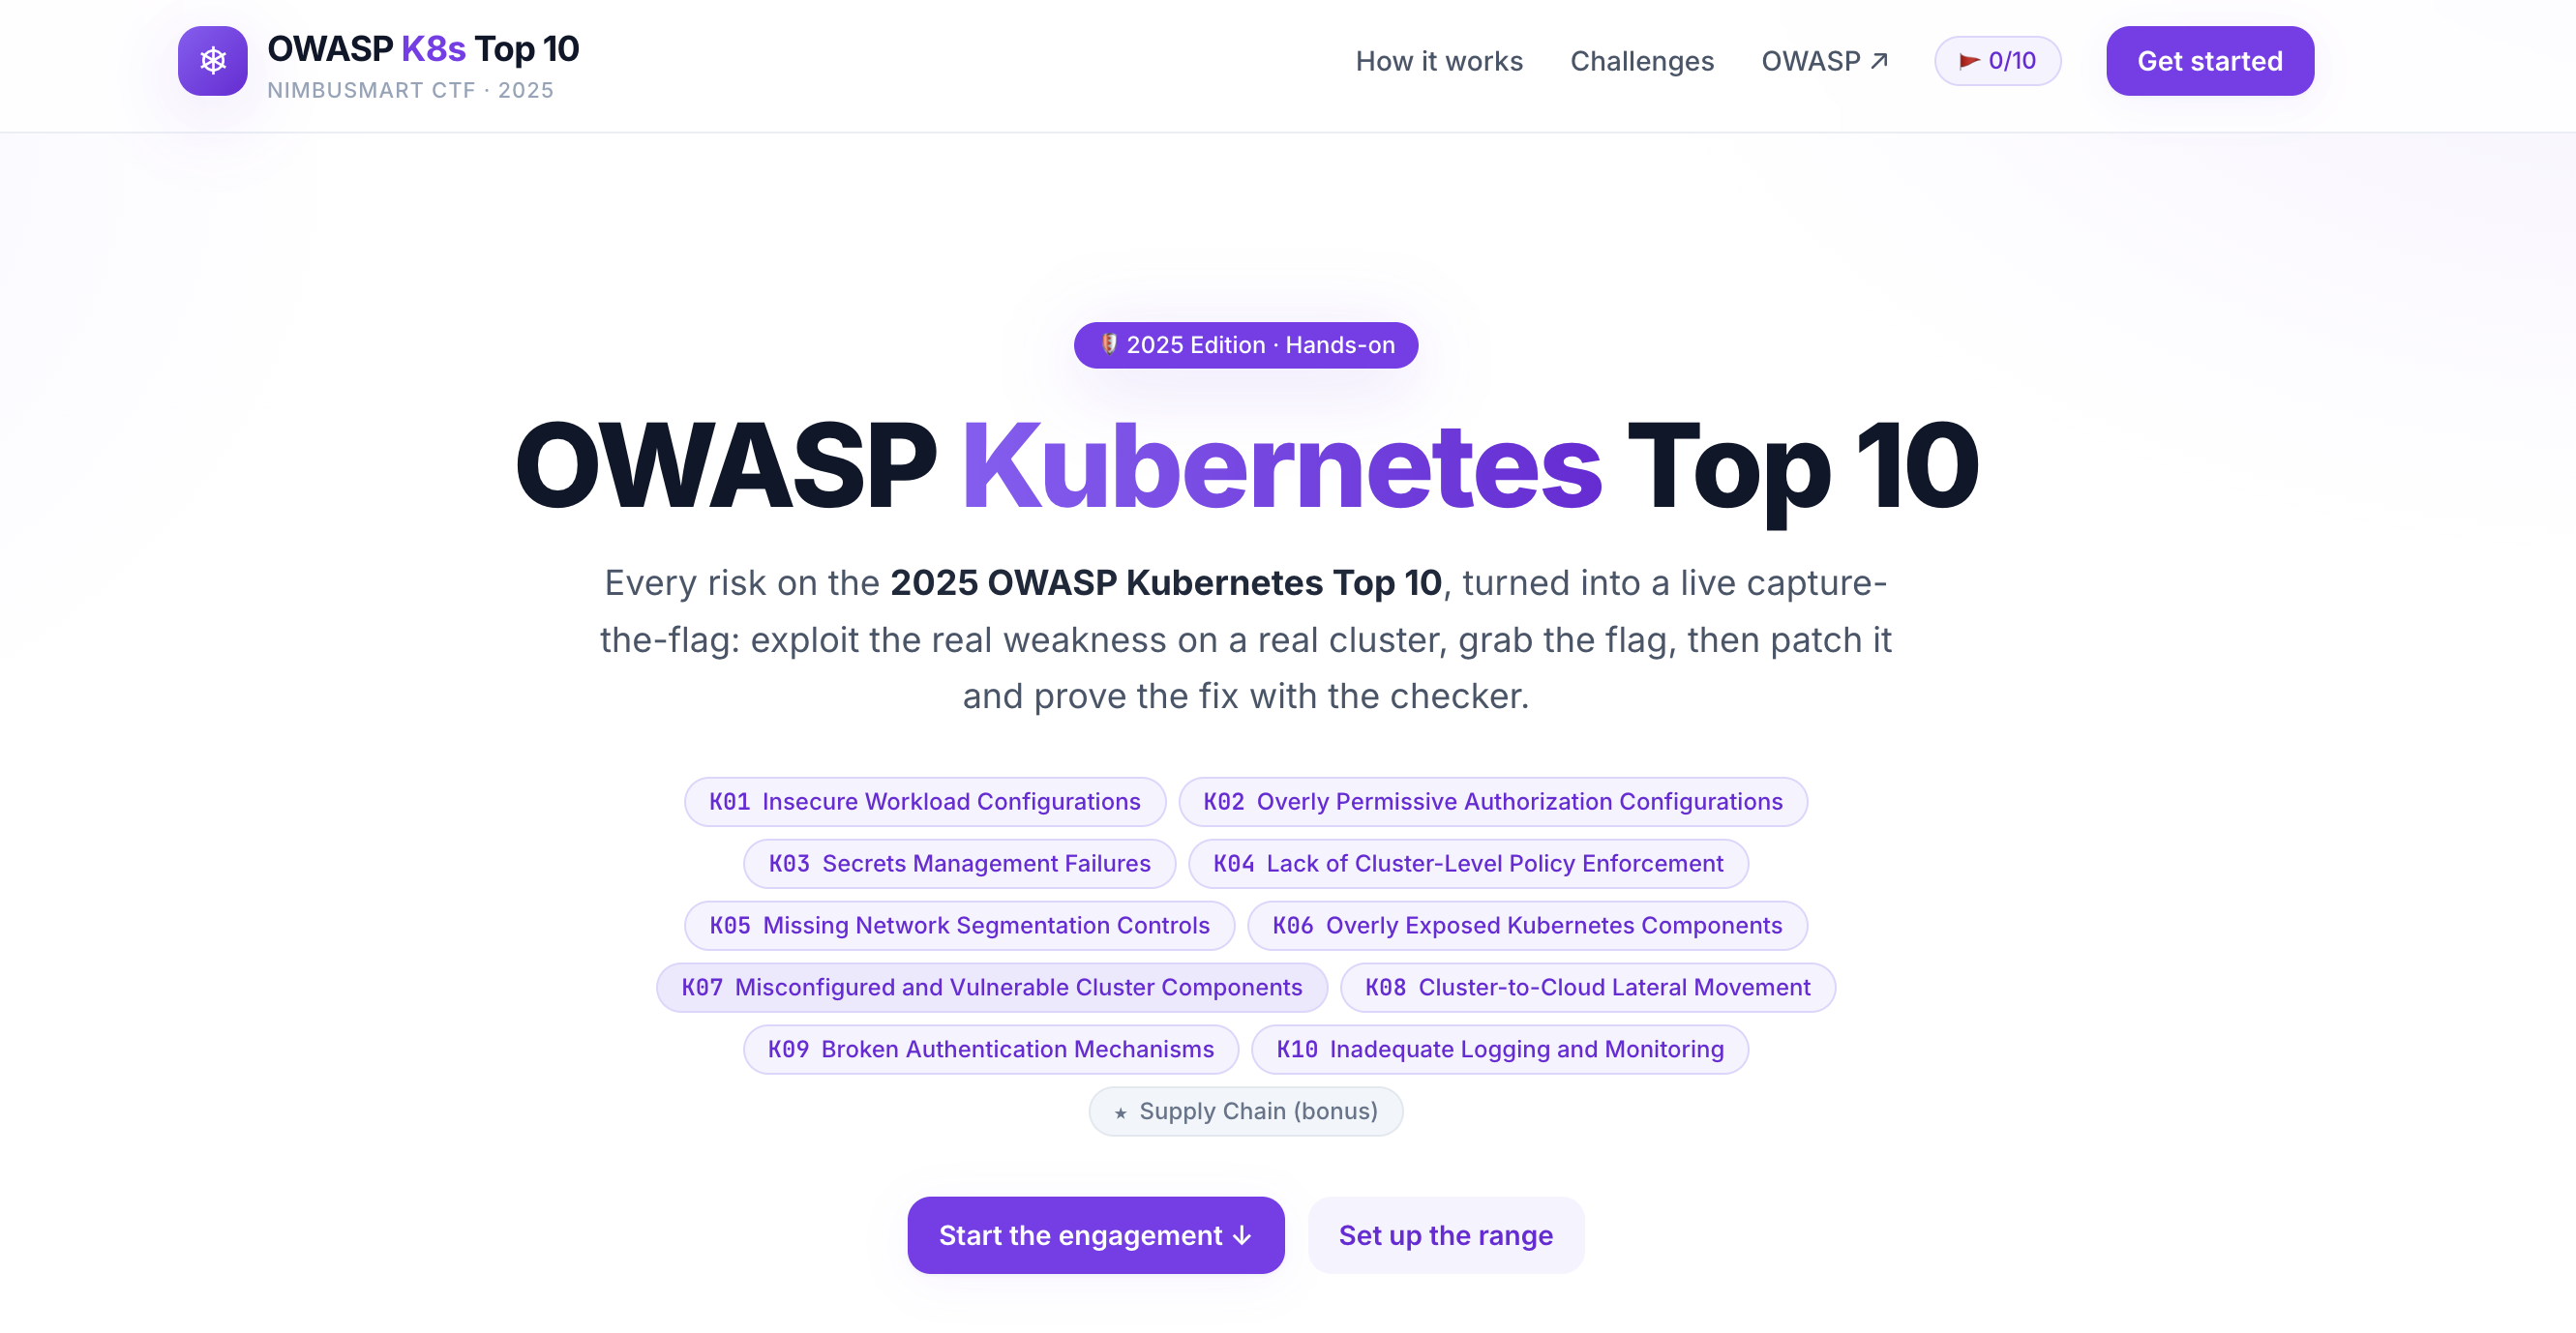 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…