
OpenAnt
 knostic/openant
OpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
ai-securitydevsecopsdynamic-analysis-sandboxing+4
knostic/openantOpenAnt from Knostic is the leading open source LLM-based vulnerability discovery product, helping defenders proactively find verified security flaws…
 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 nccgroup/log4j-jndi-be-gone
A Byte Buddy Java agent-based fix for CVE-2021-44228, the log4j 2.x "JNDI LDAP" vulnerability.
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 edera-dev/cve-tarmageddon
Demonstration of CVE-2025-62518: a critical PAX extended header size override bug in tokio-tar and async Rust tar libraries, with reproduction tools…
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
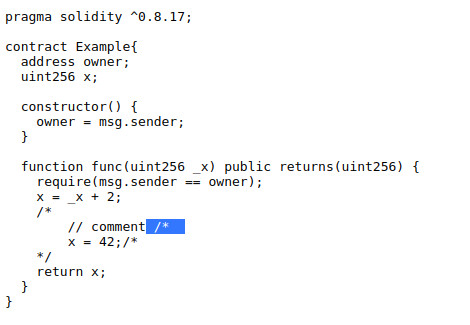 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 10cks/cve-2024-32002-exp
Bash PoC for CVE-2024-32002 that exploits Git clone with malicious submodules and symlinks to execute arbitrary commands on Windows and macOS.
 wise-security/cve-2026-38945
Proof-of-concept exploit for CVE-2026-38945, demonstrating path traversal in RayVentory Scan Engine's Java detection to execute arbitrary binaries.
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 simoesctt/sovereign-echo-33017
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow 1.8.1 via the build_public_tmp endpoint, enabling Python code injection through…
 nkopylov/tanscript-exploit-check
IOC checker for the TanStack/Mini Shai-Hulud npm supply chain attack (CVE-2026-45321)
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 dannyendortest/node-prompt-here
Deliberately vulnerable Node.js demo target for CVE-2020-7602, used to showcase automated dependency vulnerability detection and one-click PR-based…
 rohitberiwala/nodejs-tar-symlink-exploit-cve-2026-29786
Technical analysis and Proof-of-Concept (PoC) for a critical Path Traversal vulnerability via Symlink manipulation in the Node.js 'tar' package…