

opengrep
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
code-analysisdefensive-toolsdevsecops+7
opengrep/opengrep🔎 Static code analysis engine to find security issues in code.
 msaad00/agent-bom
AI supply-chain BOM: every agent, MCP server and AI package, and what each one can reach. Open-source scanner and self-hosted control plane for code,…
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 hashgraph-online/hol-guard
Open-source antivirus and firewall for AI agents: block risky tools, secret access, prompt injection, malicious packages, MCP servers, plugins, and…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 canonical/ubuntu-security-notices
Ubuntu vulnerability dataset publishing USN/LSN security notices in OSV and OpenVEX JSON formats for automated vulnerability and VEX-aware dependency…
 safedep/vet
Protect against malicious open source packages 🤖
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
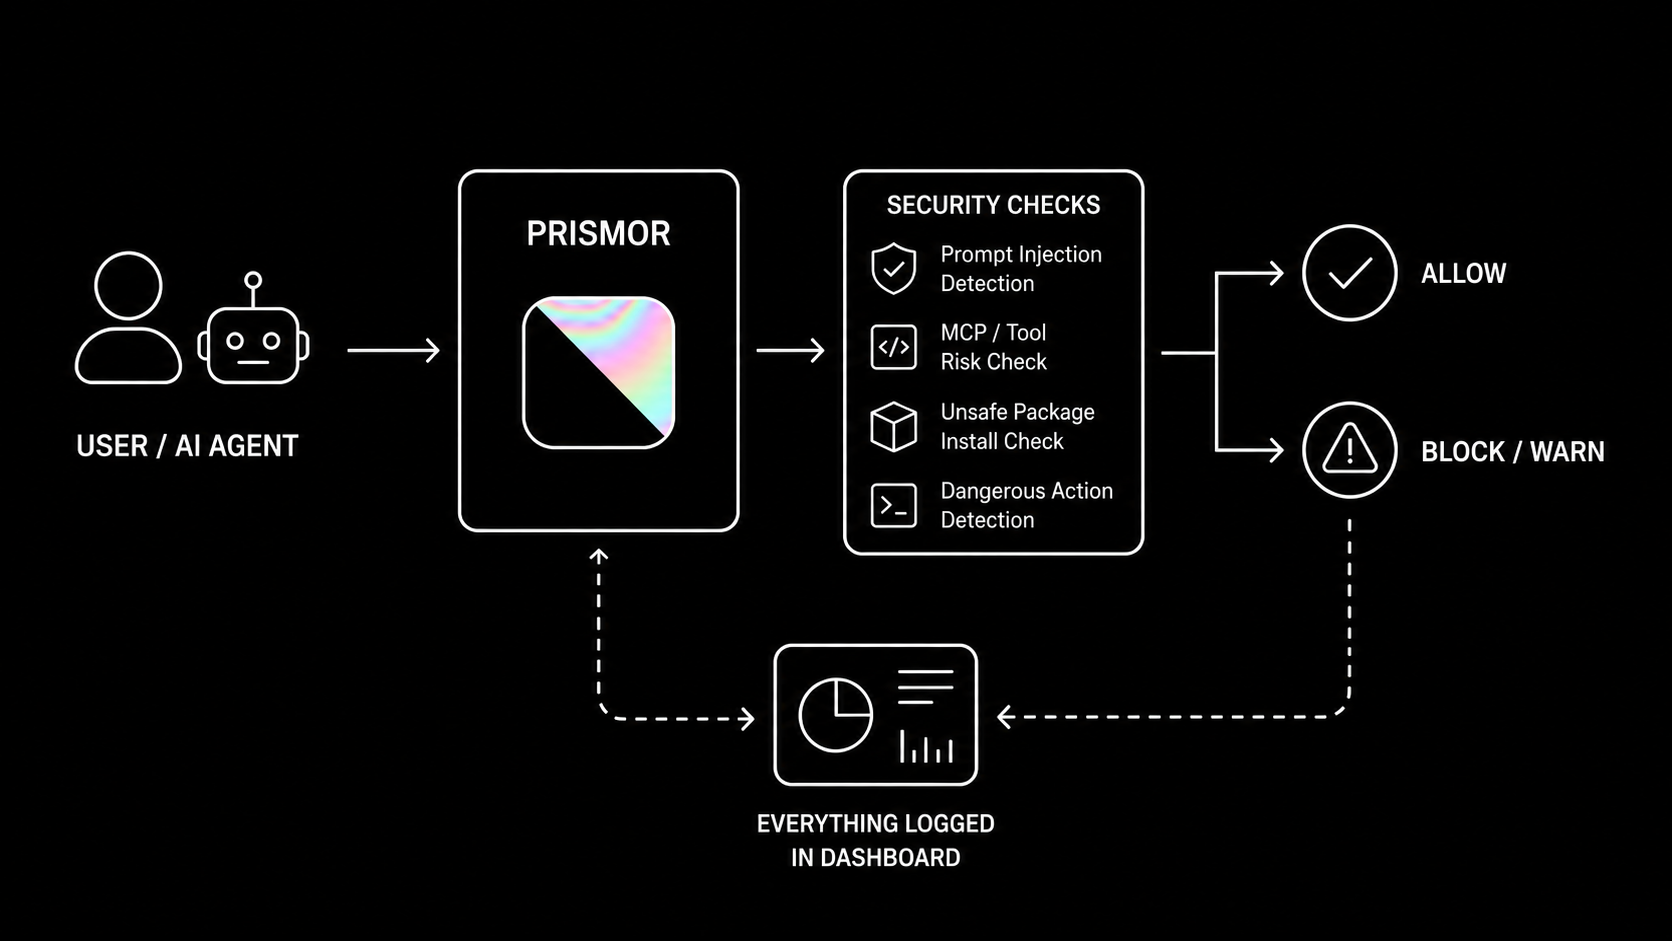 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 theupdateframework/python-tuf
Python reference implementation of The Update Framework (TUF)
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 sigstore/root-signing
Maintains the TUF repository that securely delivers the Sigstore trust root (trusted_root.json) to clients, using keyholder threshold signing, KMS…